
Seqrite Details Operation CamelClone Espionage Campaign Using HOPPINGANT and Rclone
Summary
Seqrite Labs links campaigns targeting government, defense, diplomatic, and energy entities in four countries through a shared HOPPINGANT loader and Rclone configuration. The researchers say the activity is likely coordinated but do not attribute it to a known actor.
Key points
- ZIP spear-phishing archives contain malicious LNK files that run PowerShell and download the HOPPINGANT JavaScript loader from filebulldogs[.]com.
- HOPPINGANT downloads an archive containing Rclone v1.70.3 and reconstructs MEGA account credentials using XOR key 56.
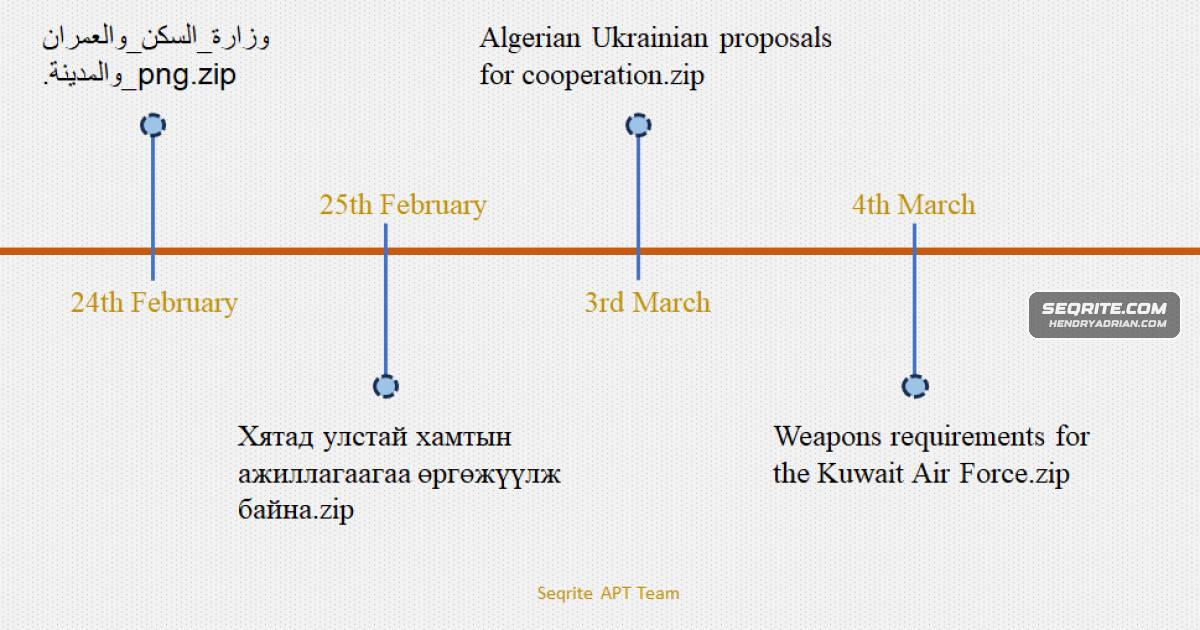
- The operation targets government, defense, diplomatic, and energy-related entities in Algeria, Mongolia, Ukraine, and Kuwait with region-themed lures.
- The scripts target Desktop documents and Telegram session data for possible upload to MEGA; Seqrite reports that one account contained only small files with gibberish data.
- Shared loader, XOR key, and Rclone settings across the samples support Seqrite’s assessment that the campaigns are coordinated; the researchers do not attribute them to a known threat actor.
Article Details
- Attack Vectors
- Spear-phishing ZIP archives contained malicious LNK shortcuts and decoy images; opening a shortcut initiated the infection chain.
- The LNK executed PowerShell to download and run a WSH JavaScript loader. The loader used Base64-encoded PowerShell commands to retrieve and extract an additional archive.
- The extracted Rclone executable collected documents from the victim's Desktop and attempted to collect Telegram session data.
- Collected files were uploaded to MEGA accounts registered with attacker-used email addresses.
- Defensive Notes
- The report says the same XOR key (56) and Rclone settings (12 threads, 12 transfers, and a 100M bandwidth limit) were reused across observed samples, which may help correlate related activity.
- The operation used public file hosting for payload delivery and cloud storage for exfiltration rather than dedicated C2 infrastructure; the article notes that this complicates network-based detection.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
coreyroberson@onionmail[.]org | Email address used to register a MEGA account for campaign data exfiltration. | |
keatonwalls@onionmail[.]org | Email address used to register a MEGA account for campaign data exfiltration. | |
oliwiagibbons@onionmail[.]org | Email address used to register a MEGA account for campaign data exfiltration. | |
theresaunderwood@onionmail[.]org | Email address used to register a MEGA account for campaign data exfiltration. | |
| SHA256 | 1d0ea66d347325902e20a12e1f2f084be45d3d6045264e513dcc420b9928013c | SHA-256 hash of the malicious Kuwait Air Force-themed LNK shortcut. |
| SHA256 | 230a22a1f1800f11718b43a7ce9390d2ef0fa9dc212d954c8fafbfbe997bbbef | SHA-256 hash of a JavaScript loader used in the campaign. |
| SHA256 | 2671e1f43b2e5911310c5b3f124c076055eec5dee4e596854332ffcf791fd740 | SHA-256 hash of a malicious LNK shortcut delivered in a campaign archive. |
| SHA256 | 27d7a398a58c12093bc49f7144dac2f079232768096d0558c226ea5c53782e29 | SHA-256 hash of a malicious ZIP archive used in the campaign. |
| SHA256 | 2902cdee050a60c3129b4bb84e74ddda7b129c3473556f689d83609d9a5981a7 | SHA-256 hash of a malicious Mongolia-themed LNK shortcut. |
| SHA256 | 2dcaaedfad798dad87f27aef39885d2879825c4c8bed1dcd9e863aba0d463103 | SHA-256 hash of a JavaScript loader used in the campaign. |
| SHA256 | 31f1a97c72f596162f0946df74838d3bef89289ce630adba8791c0f3220980ee | SHA-256 hash of a malicious ZIP archive used in the campaign. |
| SHA256 | 3e36b396c4cb71b8eaae2300c21bec26700b27ce5f6be83ef6b86d214e294c8b | SHA-256 hash of the Rclone executable deployed for data exfiltration. |
| SHA256 | 4a0e2649f89e11121ffe55546ee081ac07472db650d094314414ebf26fcb7a8e | SHA-256 hash of a malicious Mongolia-themed ZIP archive. |
| SHA256 | 51af876b0f7fde362c69219f7dec39f7fb667fb53dc5fe2cbdf841d6c5951460 | SHA-256 hash of the malicious Kuwait Air Force-themed ZIP archive. |
| SHA256 | 62c477c0827752ffeb8ea243497eef1c666fc41025d287909d021bceb5b8e699 | SHA-256 hash of a JavaScript loader used in the campaign. |
| SHA256 | 630ac67d8db777ae0b93e066bd13b21908e79f23a41a64448f0a4ea38c063a44 | SHA-256 hash of a JavaScript loader used in the campaign. |
| SHA256 | 92962bfa6df48ec0f13713c437af021f4138dc5a419bc92bc8a376d625a6519a | SHA-256 hash of a malicious LNK shortcut delivered in a campaign archive. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/82WX5GP8CI/a.zip | Malicious payload archive download URL; the archive contained the executable used for exfiltration. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/82WX5GP8CI/f.js | Malicious JavaScript loader download URL used in the campaign. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/AVQB61TVOX/a.zip | Malicious payload archive download URL; the archive contained the executable used for exfiltration. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/AVQB61TVOX/f.js | Malicious JavaScript loader download URL used in the campaign. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/F1OQY9GU84/a.zip | Malicious payload archive download URL; the archive contained the executable used for exfiltration. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/F1OQY9GU84/f.js | Malicious JavaScript loader download URL used in the campaign. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/OKW5RN48ZJ/a.zip | Malicious payload archive download URL; the archive contained the executable used for exfiltration. |
| URL | hxxps[:]//filebulldogs[.]com/uploads/OKW5RN48ZJ/f.js | Malicious JavaScript loader download URL used in the campaign. |
MITRE ATT&CK
T1005 · Data from Local SystemThe operation collected documents from the victim's Desktop and attempted to collect Telegram session data from a local directory.T1027 · Obfuscated Files or InformationThe loader used Base64-encoded PowerShell commands and XOR-encoded credentials.T1059.001 · PowerShellThe LNK and JavaScript loader executed PowerShell commands to download and run additional payloads.T1059.007 · JavaScriptThe HOPPINGANT loader was a WSH JavaScript file that ran encoded PowerShell commands.T1105 · Ingress Tool TransferThe scripts downloaded the JavaScript loader and a ZIP archive containing the Rclone executable.T1204.002 · Malicious FileA victim had to open the LNK shortcut inside the archive to trigger the infection chain.T1566.001 · Spearphishing AttachmentSpear-phishing ZIP attachments delivered archives containing malicious LNK shortcuts and decoy images.T1567.002 · Exfiltration to Cloud StorageRclone uploaded collected files to MEGA accounts registered for the operation.
Malware
Tools
Countries
AlgeriaTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti ArmedKuwaitTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti ArmedMongoliaTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti ArmedUkraineTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti Armed
Industries
DefenseTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti ArmedEnergyTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti ArmedGovernmentTargets span government, defense, diplomatic, and energy sectors in Algeria, Mongolia, Ukraine, and Kuwait, with decoys impersonating entities such as the Algerian Ministry of Housing, MonAtom LLC, and the Kuwaiti Armed