
Malicious React Native npm Releases Used a Solana-Based C2 for Malware Delivery
Summary
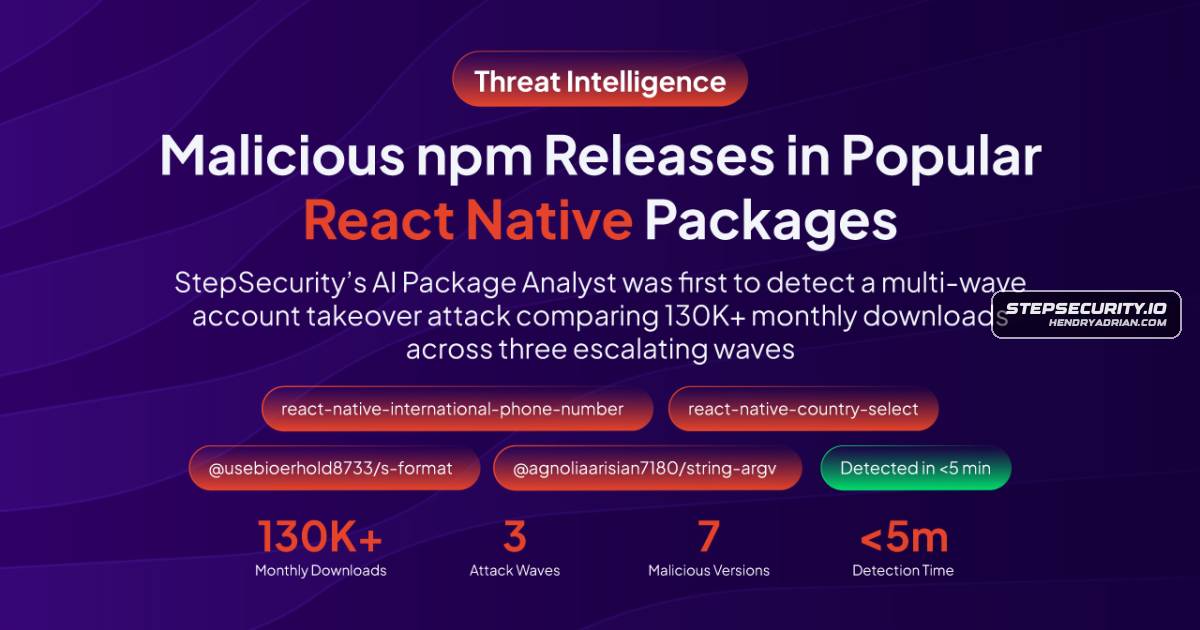
StepSecurity traced three waves of malicious React Native npm releases to a maintainer account takeover and a dependency-chain loader for obfuscated malware using Solana for C2. It said technical overlaps suggest a link to GlassWorm.
Key points
- StepSecurity reported malicious releases of react-native-international-phone-number and react-native-country-select, along with malicious scoped dependency packages.
- The maintainer confirmed their npm account had been taken over. StepSecurity said the releases lacked matching GitHub release, tag, or Actions workflow activity.
- The first wave used a direct preinstall hook; later releases hid the payload in a multi-layer dependency chain whose loader ran it as a detached process and suppressed errors.
- The malware delayed execution, checked locale and timezone signals to avoid Russia and CIS systems, and used Solana transaction data to resolve a payload URL.
- The malware fetched an AES-256-encrypted second-stage payload, with the decryption key and IV delivered in HTTP response headers; it executed the payload in memory and wrote ~/init.json as a 48-hour execution lock.
- StepSecurity said the campaign shared technical indicators with ForceMemo and assessed that it was likely linked to GlassWorm; the article presents this as an assessment, not a confirmed attribution.
- As of the article's March 18, 2026 update, StepSecurity said the malicious packages remained on npm and had been reported for removal. It advised checking for the malware's file artifact and rotating secrets present during installation.
Article Details
- Attack Vectors
- An attacker took over the npm maintainer account and published compromised package versions outside the maintainer's GitHub release and Actions workflow process.
- The first wave added a package preinstall hook that ran an obfuscated JavaScript payload automatically during npm install.
- Later releases delivered the payload through a three-layer dependency chain, using scoped relay and payload-host packages with postinstall hooks.
- A 10-second execution delay and checks of locale, username, timezone, and UTC offset were used to evade analysis and skip Russian/CIS environments.
- The malware queried the Solana blockchain for a payload URL, then fetched an AES-encrypted second-stage payload from 45.32.150.251 over HTTP.
- The second-stage payload was decrypted and executed in memory; a timestamp in ~/init.json limited re-execution to once per 48 hours.
- Defensive Notes
- Pin react-native-international-phone-number to the last known safe version 0.11.7 and react-native-country-select to 0.4.0; do not use @latest for either package.
- Check for ~/init.json and audit node_modules for @agnoliaarisian7180/string-argv and @usebioerhold8733/s-format.
- Review outbound network logs for connections to 45.32.150.251 and Solana RPC endpoints from developer machines.
- Rotate API keys, wallet private keys, tokens, and other secrets present on affected machines at installation time.
- Use lockfiles, review dependency updates, enable npm 2FA for publishing accounts, and use CI network restrictions such as Harden-Runner.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
agnoliaarisian7180@proton[.]me | Email identified by the article as an attacker-controlled maintainer address for a malicious relay package. | |
usebioerhold8733@proton[.]me | Email identified by the article as an attacker-controlled maintainer address for a malicious payload-host package. | |
voughoeveryc05de@proton[.]me | Attacker-controlled maintainer email added to a compromised package during the account takeover. | |
| IPV4 | 45[.]32[.]150[.]251 | Payload server used by the malware to deliver the encrypted second-stage payload. |
| URL | hxxp[:]//45[.]32[.]150[.]251 | Malicious payload-server URL identified in the article as the malware's second-stage delivery infrastructure. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe JavaScript payload was heavily obfuscated using RC4-based string encryption and array rotation.T1059.007 · JavaScriptPackage lifecycle hooks ran Node.js scripts that launched the malware, including install.js, init.js, and child.js.T1071.001 · Web ProtocolsThe malware used HTTP to contact the payload server and retrieve the second-stage payload.T1078 · Valid AccountsThe attacker used the taken-over npm maintainer account to publish malicious package versions.T1102.001 · Dead Drop ResolverThe malware queried Solana transaction memos as a dead-drop resolver to retrieve a changeable payload URL.T1105 · Ingress Tool TransferThe malware fetched an encrypted second-stage payload from its server after resolving the URL through Solana.T1140 · Deobfuscate/Decode Files or InformationThe malware base64-decoded and AES-256-decrypted the fetched payload before execution.T1195.002 · Compromise Software Supply ChainThe attacker compromised npm packages and used their releases and dependencies to deliver malware to developers.T1497.003 · Time Based ChecksThe malware waited 10 seconds before activity as a time-based sandbox-evasion measure.T1614.001 · System Language DiscoveryThe malware checked Russian language and locale settings, including LANG, LANGUAGE, and LC_ALL, to identify and skip some environments.T1620 · Reflective Code LoadingThe decrypted payload was executed in memory using eval(atob(payload)) on macOS/Linux or Node.js vm.Script on Windows.
People
Threat Actors
Vendors
npmThreat Intel was the first to detect and report malicious releases in two popular React Native npm packages — react-native-international-phone-number and react-native-country-select. StepSecurity's AIStepSecurityOn March 16, 2026, StepSecurity Threat Intel was the first to detect and report malicious releases in two popular React Native npm packages — react-native-international-phone-number and react-native-country-select.
Products
react-native-country-selectconfirmed full account takeover. Do not use react-native-international-phone-number@latest or react-native-country-select@latest — both resolve to compromised versions.react-native-international-phone-number16, the attacker did not stop. Over March 17–18, three additional malicious versions of react-native-international-phone-number were published (0.12.1, 0.12.2, 0.12.3) along with a new three-layer dependency chain