
eSentire Analyzes MuddyWater-Attributed Tsundere Botnet Deployment
Summary
eSentire’s analysis of an open directory attributed to MuddyWater found a PowerShell stager deploying Tsundere, which retrieves C2 addresses from Ethereum smart contracts, uses AES-encrypted WebSockets, fingerprints hosts and persists via a Windows Run key.
Key points
- eSentire’s Threat Response Unit investigated an open directory it attributed to MuddyWater and found a PowerShell stager that decrypts and runs Tsundere and a persistence module.
- Tsundere retrieves C2 addresses from an Ethereum smart contract through multiple RPC providers, selecting the address returned most frequently.
- The researchers identified two C2 IP addresses: 193.17.183.126 and 185.236.25.119.
- Tsundere uses AES-256-CBC-encrypted WebSocket communications, collects machine details to generate a host fingerprint, and executes JavaScript commands supplied by its C2.
- Its persistence module installs Node.js dependencies and adds a Windows Run registry entry; the payloads were likely obfuscated with Obfuscator.io.
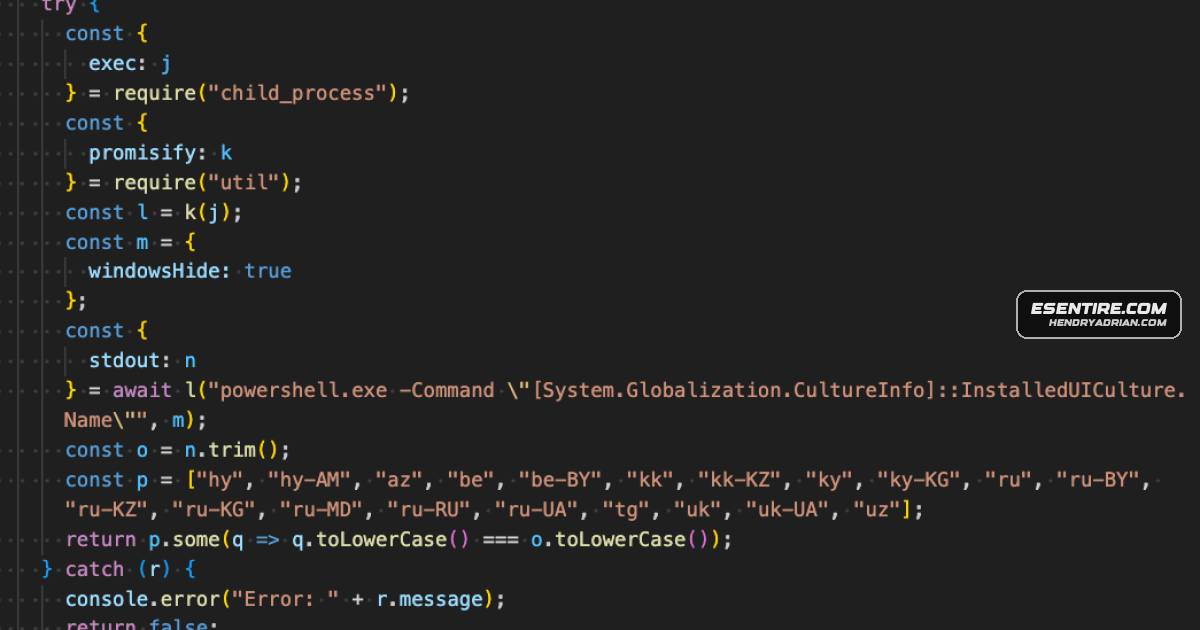
- Language checks for several CIS countries, including Ukraine, cause the malware to exit when a match is found; eSentire says this supports a suspected Russian origin for the MaaS offering.
- eSentire reports that its analysts isolated an affected host and assisted the customer with remediation.
Article Details
- Attack Vectors
- A PowerShell stager, reset.ps1, decodes, decrypts, and executes the Tsundere botnet payload and a persistence module.
- Tsundere retrieves C2 addresses from an Ethereum smart contract by querying RPC providers and selecting the most frequently returned address.
- Tsundere communicates with C2 servers over WebSockets using AES-256-CBC encryption and executes JavaScript commands received from C2.
- A persistence module uses PowerShell to create a Windows Run registry entry for automatic execution.
- The malware fingerprints victim systems and sends the fingerprint and a derived hardware ID to C2.
- Defensive Notes
- The article recommends blocking crypto-network RPC providers used by threat actors for payload staging.
- eSentire’s SOC Cyber Analysts isolated the affected host and assisted the customer with remediation.
- The article recommends 24/7 managed detection and response, threat hunting, and rapid threat response.
- The article refers readers to eSentire’s security advisory, “Iranian APT MuddyWater Exposed,” for further recommendations.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 185[.]236[.]25[.]119 | Additional Tsundere botnet C2 address revealed by a transaction to the smart contract. |
| IPV4 | 193[.]17[.]183[.]126 | Tsundere botnet C2 address stored in the Ethereum smart contract. |
| SHA256 | 6a19953b6bb1b4eedb8beba5f9e1f4d1eb64a283a5f90f0deeba89593a3ca9f4 | Hash of the obfuscated Tsundere botnet payload, sysuu2etiprun.js. |
| SHA256 | 7ab597ff0b1a5e6916cad1662b49f58231867a1d4fa91a4edf7ecb73c3ec7fe6 | Hash of reset.ps1, the stager that deploys Tsundere and its persistence module. |
| SHA256 | dd87dfb302501e3cbe2e59fca9e14bfd53e65ed313c1b70e4d7daf68d86386ff | Hash of the deobfuscated Tsundere botnet payload, sysuu2etiprun.js. |
| SHA256 | df8b94f7b3399b005cb64e879cfe04bfc3ba1499cf98608c10e532dbb493fa8d | Hash of the deobfuscated persistence module, VfZUSQi6oerKau.js. |
| SHA256 | e3c0ffeb5fcaab75bb2cf32c930e32b3f219325cb72ba813a033531aa2ff0305 | Hash of the obfuscated persistence module, VfZUSQi6oerKau.js. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article reports that the Node.js payloads were obfuscated, likely with Obfuscator.io.T1059.001 · PowerShellThe reset.ps1 stager and persistence module use PowerShell to run commands, perform environment checks, and establish persistence.T1059.007 · JavaScriptTsundere creates and invokes a JavaScript Function from code received in a C2 message.T1071.001 · Web ProtocolsTsundere communicates with its C2 servers over WebSockets.T1082 · System Information DiscoveryTsundere collects system and hardware details, including GPU, Windows version, volume serial, BIOS, and Machine GUID, to create a victim fingerprint and HWID.T1547.001 · Registry Run Keys / Startup FolderThe persistence module uses PowerShell to add a value to the Windows Run registry key.T1573 · Encrypted ChannelTsundere encrypts C2 communications with AES-256-CBC and retrieves an AES key and IV from C2.
Threat Actors
Malware
Vendors
Products
Ethereumstager that deploys a persistence module and the Tsundere botnet, which retrieves C2 addresses from the Ethereum blockchain using an “EtherHiding” technique and communicates via AES-encrypted WebSockets.Node.jsAnalysis shows Tsundere uses Node.js obfuscation (likely Obfuscator.io), includes CIS/Ukraine language checks that terminate execution, and relies on Run-key persistence and MaaS-style tradecraft.
Tools
Countries
ArmeniaAnalysis reveals CIS-country language checks (Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Ukraine) that cause termination if matched, and two C2 IPs identified: 193.17.183.126 and 185.236.25.119.BelarusAnalysis reveals CIS-country language checks (Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Ukraine) that cause termination if matched, and two C2 IPs identified: 193.17.183.126 and 185.236.25.119.KazakhstanAnalysis reveals CIS-country language checks (Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Ukraine) that cause termination if matched, and two C2 IPs identified: 193.17.183.126 and 185.236.25.119.KyrgyzstanAnalysis reveals CIS-country language checks (Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Ukraine) that cause termination if matched, and two C2 IPs identified: 193.17.183.126 and 185.236.25.119.MoldovaAnalysis reveals CIS-country language checks (Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Ukraine) that cause termination if matched, and two C2 IPs identified: 193.17.183.126 and 185.236.25.119.RussiaAnalysis reveals CIS-country language checks (Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Ukraine) that cause termination if matched, and two C2 IPs identified: 193.17.183.126 and 185.236.25.119.UkraineAnalysis shows Tsundere uses Node.js obfuscation (likely Obfuscator.io), includes CIS/Ukraine language checks that terminate execution, and relies on Run-key persistence and MaaS-style tradecraft.