
Fake Claude Installer Uses G DATA DLL Sideloading to Deploy PlugX
Summary
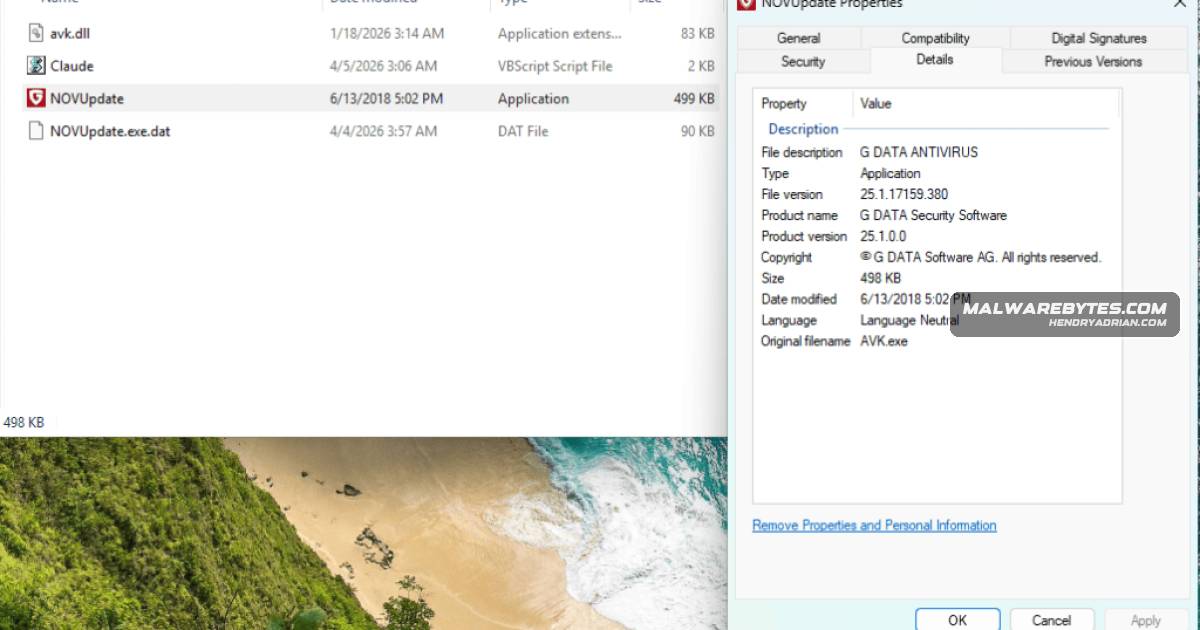
A fake Claude installer delivered a working app alongside a PlugX sideloading chain using signed G DATA updater NOVUpdate.exe and malicious avk.dll. Sandbox telemetry recorded an outbound connection to 8.217.190.58:443.
Key points
- A fake Claude download page offered Claude-Pro-windows-x64.zip, whose installer launched a working Claude app while deploying malware.
- The MSI used a misspelled installation path, and a VBScript dropper ran claude.exe while setting up the hidden payload.
- The dropper copied NOVUpdate.exe, avk.dll, and NOVUpdate.exe.dat into the Windows Startup folder; the signed G DATA updater loaded the malicious DLL through sideloading.
- Sandbox telemetry observed NOVUpdate.exe connect to 8.217.190.58:443 about 22 seconds after execution and modify a TCP/IP-related registry key.
- The dropper attempted to delete itself and suppress errors, leaving the Startup-folder components and running updater as persistent artifacts.
- The sideloading setup resembles a PlugX triad documented by Lab52 in February 2026; the article cautions that tooling alone does not establish attribution.
- The article advises checking for the named Startup-folder files and misspelled directory, scanning the system, and reviewing network logs for the observed IP.
Article Details
- Attack Vectors
- A fake website impersonating Claude offered a trojanized installer archive that installed a working Claude application alongside a PlugX sideloading chain.
- A VBScript dropper copied NOVUpdate.exe, malicious avk.dll, and encrypted NOVUpdate.exe.dat into the Windows Startup folder, then launched the signed updater to sideload the DLL.
- The running sideloading host connected to 8.217.190.58 on port 443; sandbox telemetry observed the first connection 22 seconds after execution.
- The dropper modified a TCP/IP-related registry key and used a batch file to delete itself and the original VBScript.
- Defensive Notes
- Check the Windows Startup folder for NOVUpdate.exe, avk.dll, and NOVUpdate.exe.dat, and check for the misspelled installation directory C:Program Files (x86)AnthropicClaudeCluade.
- Check firewall or proxy logs for outbound connections to 8.217.190.58.
- If the listed Startup-folder files are present, disconnect from the internet, run a full system scan, and change passwords for accounts accessed from the affected machine.
- Download Claude only from its official site and avoid links in emails, ads, or unofficial “Pro” versions.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | hendryadrian[.]com | Domain of the fake website identified as impersonating Claude to distribute the trojanized installer. |
| IPV4 | 8[.]217[.]190[.]58 | C2 destination contacted by NOVUpdate.exe during sandbox analysis. |
| SHA256 | 35feef0e6806c14f4ccdb4fceff8a5757956c50fb5ec9644dedae665304f9f96 | Hash of the trojanized Claude-Pro-windows-x64.zip archive distributed by the fake site. |
| SHA256 | 8ac88aeecd19d842729f000c6ab732261cb11dd15cdcbb2dd137dc768b2f12bc | Hash of the encrypted payload file NOVUpdate.exe.dat used in the sideloading chain. |
| SHA256 | be153ac4db95db7520049a4c1e5182be07d27d2c11088a2d768e931b9a981c7f | Hash of NOVUpdate.exe, the signed G DATA updater used as the sideloading host in the malicious chain. |
| SHA256 | d5590802bf0926ac30d8e31c0911439c35aead82bf17771cfd1f9a785a7bf143 | Hash of the malicious avk.dll identified as the PlugX loader. |
MITRE ATT&CK
T1059.005 · Visual BasicA VBScript dropper launches the legitimate application, copies the sideloading components, and starts NOVUpdate.exe.T1112 · Modify RegistrySandbox analysis observed NOVUpdate.exe modifying HKLMSystemCurrentControlSetServicesTcpipParameters.T1204.002 · Malicious FileThe dropper runs after the victim clicks the desktop shortcut installed by the trojanized package.T1547.001 · Registry Run Keys / Startup FolderThe dropper copies NOVUpdate.exe, avk.dll, and NOVUpdate.exe.dat into the Windows Startup folder for persistence.T1574.002 · DLL Side-LoadingNOVUpdate.exe loads the substituted malicious avk.dll from its own directory to run the PlugX payload.
Malware
Vendors
AnthropicA fake website impersonating Anthropic’s Claude distributed a trojanized installer (Claude-Pro-windows-x64.zip) that installs a working Claude application while secretly deploying a PlugX sideloading chain.G DATAThe dropper uses a signed G DATA updater (NOVUpdate.exe), a malicious avk.dll, and an encrypted payload (NOVUpdate.exe.dat) to perform DLL sideloading and rapidly call back to 8.217.190.58, exploiting the popularity of