
UAT-10362 Uses LucidRook Malware in Spear-Phishing Campaigns Targeting Taiwanese NGOs
Summary
Cisco Talos attributes campaigns targeting Taiwanese NGOs and suspected universities to UAT-10362. The group uses archive lures and DLL side-loading to deploy LucidRook, a Lua-based stager, with geofencing and compromised infrastructure.
Key points
- Cisco Talos says it discovered the activity in October 2025 and attributes it to the previously undocumented cluster UAT-10362.
- RAR or 7-Zip archive lures deliver LucidPawn, which uses DLL side-loading to launch LucidRook.
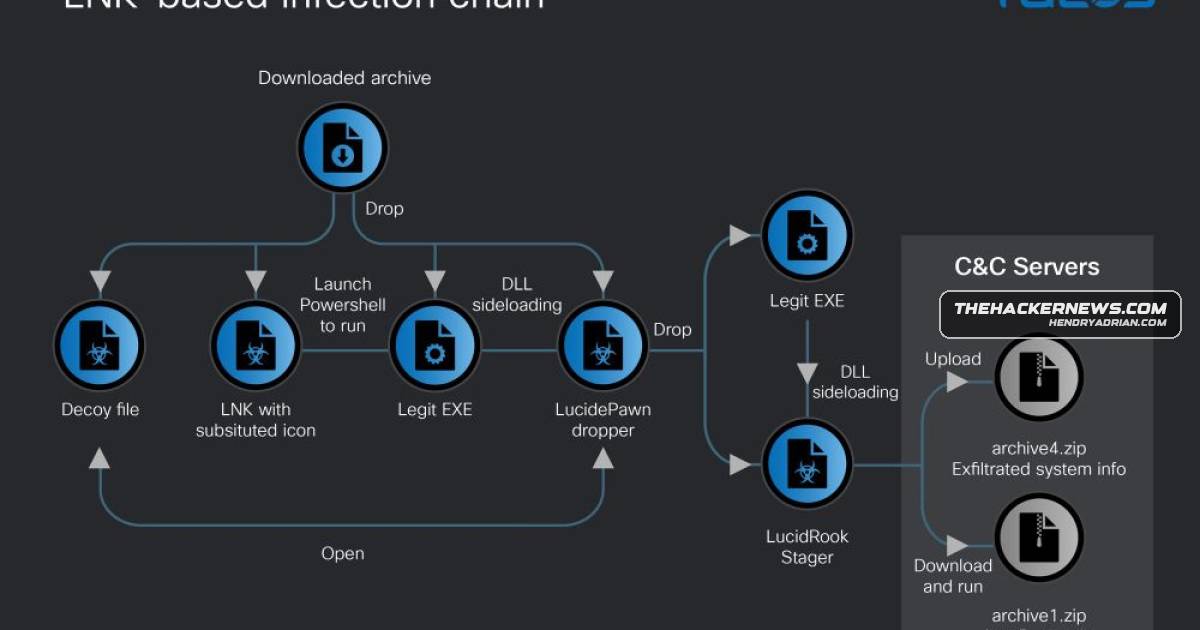
- One infection chain uses a PDF-icon LNK file and PowerShell; another uses a purported Trend Micro executable that acts as a .NET dropper.
- LucidRook is an obfuscated 64-bit DLL with an embedded Lua 5.4.8 interpreter; Talos says it collects and exfiltrates system information, then decrypts and runs Lua bytecode.
- LucidPawn checks for the Traditional Chinese system language (zh-TW) and continues only when it matches.
- The operators reportedly use OAST services and compromised FTP servers for command and control. A LucidKnight variant can exfiltrate system information through Gmail.
Article Details
- Attack Vectors
- Spear-phishing archives in RAR or 7-Zip format targeted Taiwanese NGOs and suspected universities.
- An LNK file disguised with a PDF icon launches a PowerShell script, which runs index.exe and uses DLL side-loading to execute LucidPawn; LucidPawn then side-loads LucidRook.
- A purported Trend Micro executable, Cleanup.exe, acts as a .NET dropper and uses DLL side-loading to execute LucidRook.
- LucidRook collects system information, exfiltrates it to an external server, and receives encrypted Lua bytecode for decryption and execution.
- LucidPawn checks the system UI language and continues only when it matches zh-TW.
- Talos reports that the actors used an OAST service and compromised FTP servers for command and control; a LucidKnight variant exfiltrates system information via Gmail to a temporary email address.
- Defensive Notes
- The article does not provide specific mitigation, patching, or remediation guidance.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationLucidRook is described as heavily obfuscated to deter analysis and detection.T1041 · Exfiltration Over C2 ChannelLucidRook exfiltrates collected system information to an external server.T1059.001 · PowerShellIn the LNK chain, a PowerShell script runs index.exe.T1082 · System Information DiscoveryLucidRook and LucidKnight collect system information.T1105 · Ingress Tool TransferLucidRook receives encrypted Lua bytecode from an external server for subsequent execution.T1204.002 · Malicious FileThe infection chains rely on a user opening a disguised LNK file or a purported Trend Micro executable from an archive.T1566.001 · Spearphishing AttachmentThe campaigns used spear-phishing with RAR or 7-Zip archive lures to deliver the malware.T1574.002 · DLL Side-LoadingThe LNK and EXE chains use DLL side-loading to execute LucidPawn and LucidRook.T1614.001 · System Language DiscoveryLucidPawn checks the system UI language and proceeds only when it matches zh-TW.
People
Threat Actors
Malware
LucidKnightActors use geofencing for zh-TW systems, abuse OAST services and compromised FTP for C2, and deploy LucidKnight for reconnaissance, indicating a mature, targeted toolkit.LucidPawnThe attackers use RAR/7âZip lures to deliver a LucidPawn dropper that leverages DLL sideâloading in LNK- and EXE-based chains to launch a heavily obfuscated 64-bit LucidRook DLL that embeds a Lua interpreter,LucidRookCisco Talos attributed a previously undocumented threat cluster, UAT-10362, to spear-phishing campaigns targeting Taiwanese NGOs and suspected universities to deploy a new Lua-based stager called LucidRook.
Products
GmailFurthermore, at least one variant of the dropper has been found to deploy a 64-bit Windows DLL named LucidKnight that’s capable of exfiltrating system information via Gmail to a temporary email address.Microsoft WindowsThere are two distinct infection chains that lead to LucidRook, one using a Windows Shortcut (LNK) file with a PDF icon and another involving an executable that masquerades as an antivirus program from Trend Micro.PowerShellTwo infection chains exist: an LNK file that triggers PowerShell and index.exe sideloading, and a fake Trend Micro EXE that acts as a .NET dropper.