
AI-Automated Device Code Phishing Targets Italian Public Administration
Summary
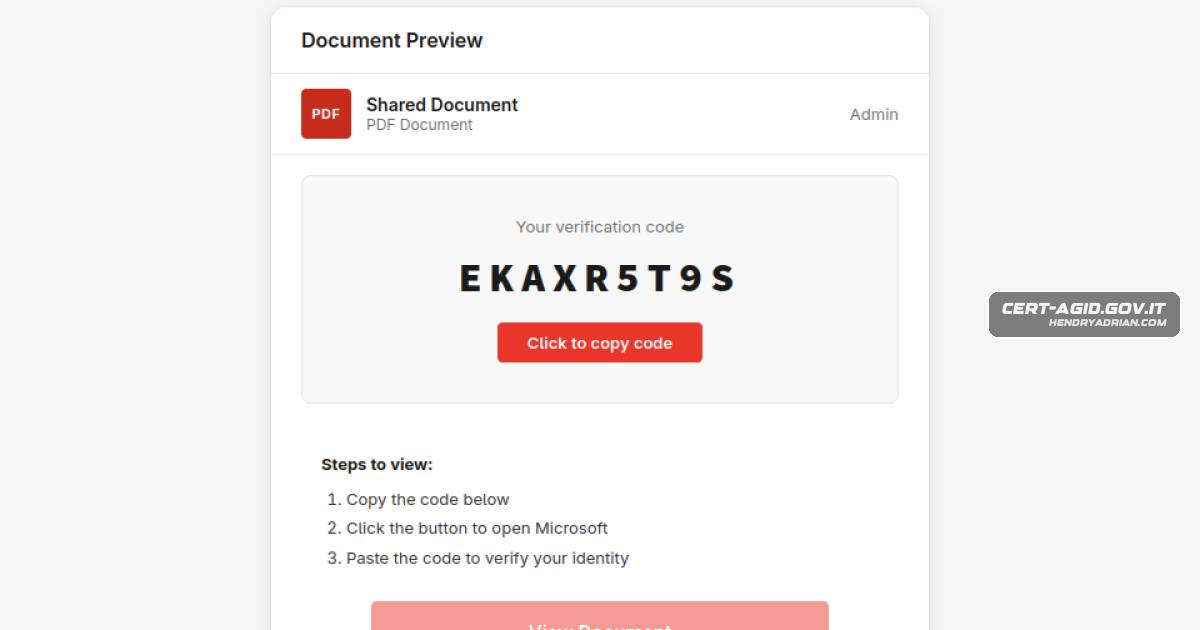
CERT-AgID says it has evidence that an automated device-code phishing campaign targets Italian public administration. Dynamic codes and redirect chains help attackers obtain Microsoft access tokens, bypass MFA and take over accounts.
Key points
- Attackers abuse the legitimate OAuth device code flow: victims enter a code in the official Microsoft login process, authorizing an attacker-initiated session without directly giving attackers their credentials.
- Deceptive emails use lures such as document sharing, electronic signatures and voicemail notifications, with links in messages or PDF and HTML attachments.
- In-page JavaScript interacts with Microsoft authentication endpoints to generate device codes dynamically; in some cases, the code is copied to the victim’s clipboard.
- Redirect chains through compromised legitimate domains and serverless platforms such as AWS, Cloudflare and Vercel are used to evade URL scanners and sandboxes.
- Successful attacks give actors access tokens that can enable account takeover and bypass MFA. Reported post-compromise actions include registering devices, taking mailbox data and creating inbox rules.
- CERT-AgID says it has evidence of targeting against Italian public administration and distributed indicators of compromise to accredited entities.
- CERT-AgID recommends enabling device code flow only when necessary, alongside user awareness and caution around unusual login requests and permissions.
Article Details
- Attack Vectors
- Deceptive emails used document-sharing, electronic-signature, and voicemail lures, with links in the message body or in PDF and HTML attachments.
- Phishing pages used JavaScript to request device codes through Microsoft authentication endpoints and sometimes copied the codes to victims’ clipboards.
- Victims were induced to enter attacker-initiated device codes on the legitimate Microsoft sign-in portal, authorizing attacker sessions and exposing access tokens.
- The campaign used redirect chains through compromised legitimate domains and serverless or cloud platforms, including AWS, Cloudflare, and Vercel.
- Defensive Notes
- Administrators were advised to enable device code flow only when strictly necessary.
- The article recommends user awareness, caution with unusual sign-in requests and permissions, and contacting IT promptly when in doubt.
- CERT-AgID reported distributing indicators of compromise to accredited public administrations.
MITRE ATT&CK
T1059.007 · JavaScriptIn-page JavaScript interacted with Microsoft authentication endpoints to generate device codes and check whether the victim completed sign-in.T1098.005 · Device RegistrationIn some cases, attackers registered new devices for long-term persistence.T1114 · Email CollectionThe reported post-compromise activity included stealing data from victims’ email.T1528 · Steal Application Access TokenAfter the victim authorized the attacker-initiated device-code session, the attacker-controlled server obtained an access token.T1550.001 · Application Access TokenThe campaign used access tokens obtained through the device-code flow to access victim accounts.T1566.002 · Spearphishing LinkPhishing emails contained links in their body or in PDF and HTML attachments that redirected victims to the phishing interface.
Vendors
Amazon Web ServicesAttackers use chains of redirects through compromised legitimate domains and serverless/cloud platforms (AWS, Cloudflare, Vercel) to evade URL scanners and sandboxes.CloudflareAttackers use chains of redirects through compromised legitimate domains and serverless/cloud platforms (AWS, Cloudflare, Vercel) to evade URL scanners and sandboxes.MicrosoftMicrosoft warned of a large-scale phishing campaign that abuses the OAuth device code flow to obtain access tokens and bypass multi-factor authentication.VercelAttackers use chains of redirects through compromised legitimate domains and serverless/cloud platforms (AWS, Cloudflare, Vercel) to evade URL scanners and sandboxes.