
LevelBlue Details Malicious Axios npm Versions and RAT Deployment
Summary
LevelBlue reports malicious Axios versions 1.14.1 and 0.30.4 used a hidden postinstall dependency to fetch a payload and deploy a RAT on customer systems. It observed suspicious npm/node process chains; large-scale data exfiltration remains unconfirmed.
Key points
- LevelBlue says malicious [email protected] and [email protected] versions appeared after an attacker compromised a developer's npm account.
- A hidden dependency ran through an npm postinstall script, downloaded a secondary payload, and was associated with RAT deployment on multiple customer machines.
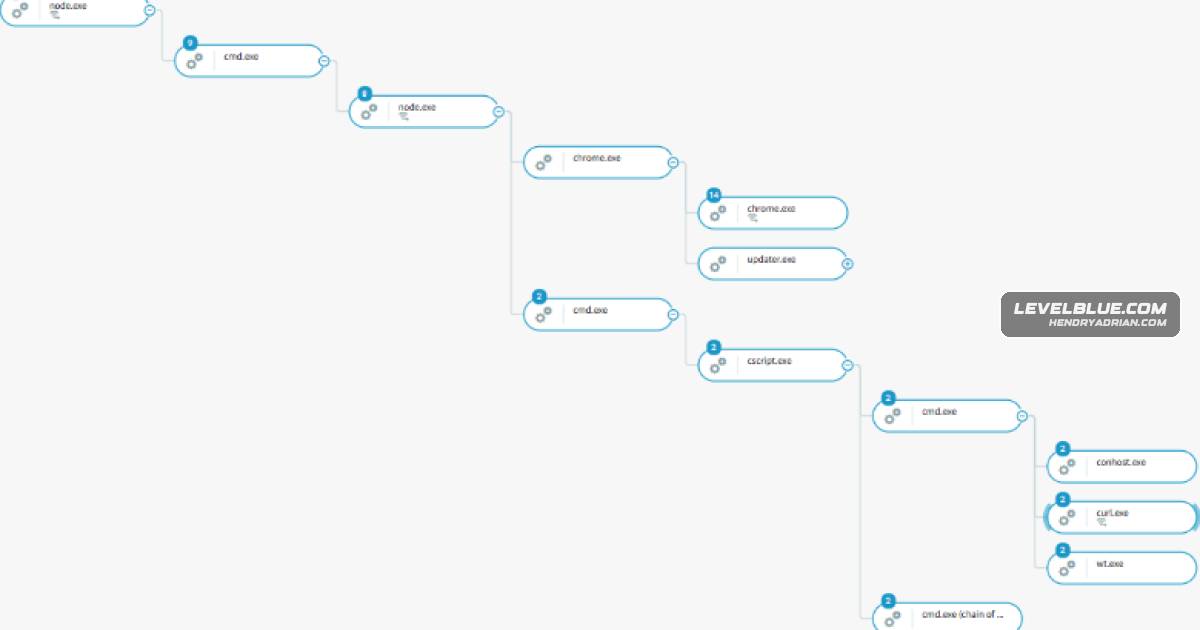
- Observed process chains included npm or node spawning cmd.exe or PowerShell, followed by network utilities such as curl or wget.
- LevelBlue reports Cybereason EDR detections for postinstall execution, unusual process spawning, and outbound communications to sfrclak[.]com.
- The article says large-scale data exfiltration was not conclusively confirmed, while warning that credentials and development or CI/CD environments may be at risk.
- Recommended steps include isolating and rebuilding affected systems, rotating potentially exposed credentials, auditing pipelines, and reviewing dependencies and npm scripts.
Article Details
- Attack Vectors
- Malicious Axios versions 1.14.1 and 0.30.4 were published to npm after the article reports that a developer's npm account was compromised.
- A hidden dependency, identified as plain-crypto-js, ran automatically through an npm postinstall script and downloaded a secondary payload that deployed a RAT.
- On affected systems, npm or node spawned cmd.exe and powershell.exe, followed by network utilities such as curl or wget.
- Defensive Notes
- Isolate affected systems and reimage or rebuild them; rotate potentially exposed API keys, SSH keys, access tokens, and npm credentials.
- Audit CI/CD pipelines and recent builds, review outbound connections, and hunt for the reported filenames, hashes, C2 indicators, and suspicious npm/node process chains.
- Disable npm lifecycle scripts where feasible, pin dependency versions, verify package integrity and sources, and enable MFA for developer and package-repository accounts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | sfrclak[.]com | C2 domain reported as used for payload hosting and control. |
| IPV4 | 142[.]11[.]206[.]73 | C2 IP address reported communicating with infected hosts. |
| SHA256 | 617b67a8e1210e4fc87c92d1d1da45a2f311c08d26e89b12307cf583c900d101 | Hash reported for 6202033.ps1, associated with the secondary payload. |
| SHA256 | e10b1fa84f1d6481625f741b69892780140d4e0e7769e7491e5f4d894c2e0e09 | Hash reported for package/setup.js, associated with the malicious postinstall activity. |
| URL | hxxp[:]//sfrclak[.]com:8000/6202033 | URL reported as the C2 and payload-delivery endpoint for the secondary payload. |
MITRE ATT&CK
T1059.001 · PowerShellAffected systems showed npm or node spawning powershell.exe, and the article reports the 6202033.ps1 script.T1059.003 · Windows Command ShellAffected systems showed npm or node spawning cmd.exe to execute commands.T1059.007 · JavaScriptA hidden dependency ran automatically through an npm postinstall script; the article identifies package/setup.js among the associated artifacts.T1071.001 · Web ProtocolsThe article reports outbound C2 communications and payload retrieval over HTTP, including the reported URL on sfrclak[.]com.T1105 · Ingress Tool TransferThe postinstall activity downloaded a secondary payload from external infrastructure.T1195.002 · Compromise Software Supply ChainMalicious Axios package versions were published to npm after compromise of a developer's npm account.
Vendors
CybereasonLevelBlue’s Cybereason EDR generated detections for post-install script execution, renamed PowerShell spawning, and suspicious outbound network communications tied to C2 infrastructure.LevelBlueLevelBlue detected abnormal npm/node-spawned command interpreters, outbound C2 traffic to sfrclak[.]com (142.11.206[.]73), and provided containment, remediation, and hunting guidance.
Products
AxiosA supply chain compromise delivered malicious versions of the Axios npm package that executed a hidden postinstall dependency to download and deploy a remote access trojan on developer and CI/CD systems.Cybereason Defense PlatformPost-exploitation activities detected by LevelBlue: LevelBlue’s Cybereason Defense Platform generated detections associated with post-install script execution, abnormal process (renamed PowerShell) spawning, andnpmA supply chain compromise delivered malicious versions of the Axios npm package that executed a hidden postinstall dependency to download and deploy a remote access trojan on developer and CI/CD systems.