Analysis Links Ashab al-Yamin’s Claims to a Broader Iranian-Aligned Telegram Network
Summary
An analysis of Telegram activity finds Ashab al-Yamin’s attack claims and media circulate across Iranian-aligned channels, complicating attribution and leaving its status as a distinct operational group uncertain.
Key points
- Ashab al-Yamin’s primary Telegram channel appears to have been removed; related claims continue to circulate through secondary and supporter channels.
- The article identifies shared content and messaging across Ashab al-Yamin, Sabereen News, and other channels, but says these links do not prove a single point of origin or centralized coordination.
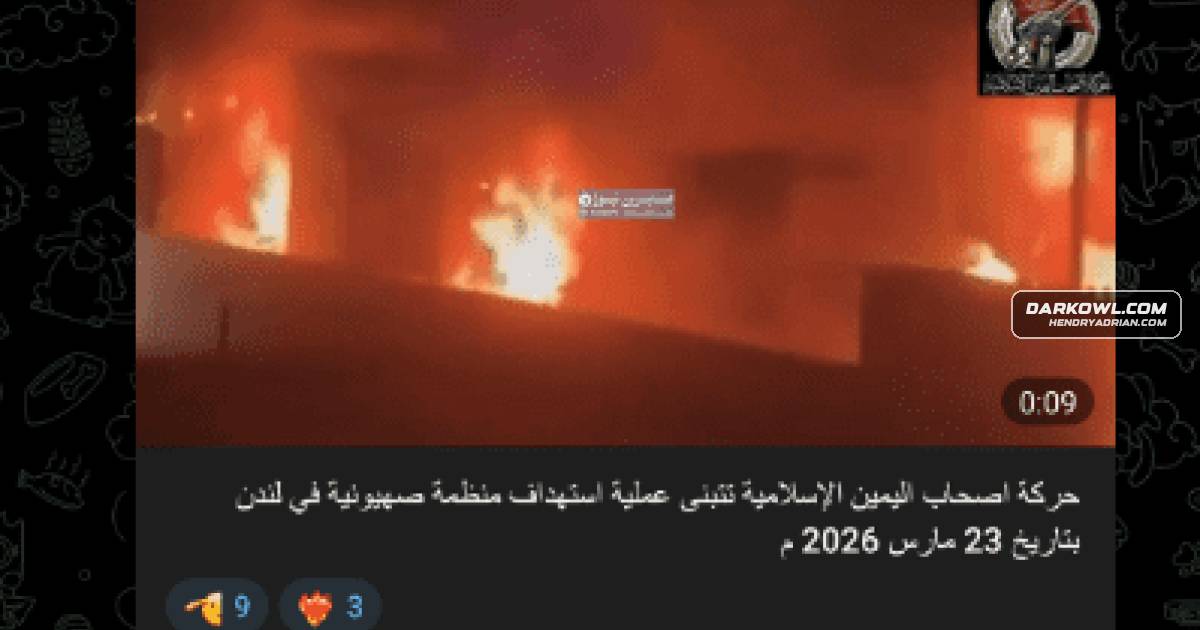
- Videos claiming attacks in London, Amsterdam, and the Netherlands are discussed; the article presents them as claims, not independently confirmed outcomes.
- The group’s limited organizational structure and inconsistent media output leave its operational status uncertain; analysts cited suggest it may be a front identity used by loosely connected actors.
- The article describes other unverified cyber claims in the wider ecosystem, including alleged Lockheed Martin data theft and an intrusion targeting Los Angeles Metro.
- The analysis emphasizes that content redistribution and amplified claims can create perceived reach without establishing sustained operational capability.
Article Details
- Attack Vectors
- Telegram channels were used to publish and redistribute attack claims, propaganda, and geopolitical messaging.
- The article reports claims of cyber intrusion, data exfiltration, and system disruption targeting Los Angeles Metro infrastructure, but says evidence was limited and attribution unclear.
- APT Iran allegedly advertised stolen Lockheed Martin data on Telegram and a darknet marketplace; the claims and valuation remain unverified.
Threat Actors
Ababil of MinabGroup claiming a cyber incident targeting Los Angeles Metro infrastructure; attribution and the claimed impact remain unclear or unverified.Ajnad Bayt al-MaqdisSunni jihadist group whose material was reportedly reshared by Sabereen News; the article says it pledged allegiance to al-Qaeda in February 2026.APT IRANPro-Iranian hacktivist group that claimed to possess stolen Lockheed Martin data; the claims remain unverified.Ashab al-KahfIraqi militia group aligned with the Islamic Resistance in Iraq, reported to claim attacks against U.S. military and allied targets.Ashab al-YaminShort form used in the article for Harakat Ashab al-Yamin al-Islamia, whose attack claims circulated across Telegram channels.Harakat Ashab al-Yamin al-IslamiaA group claiming responsibility for attacks in Europe; the article says its status as a distinct operational organization is uncertain.Jaysh al-GhadabGroup described as operating within the Islamic Resistance ecosystem and publishing attack claims and related messaging.
Products
Tools
Countries
BahrainFor example, content includes battlefield or intelligence-style analysis, such as satellite imagery purportedly showing damage to U.S.-linked air facilities in Bahrain and Kuwait following Iranian strikes.Iranoutlet widely associated with Iranian-aligned networks, with multiple analyses pointing to links with Iran’s Islamic Revolutionary Guard Corps–Qods Force (IRGC-QF) and Iran-backed militia groups.IsraelThe most recent identifiable content, dated April 4, included a video claiming responsibility for an attack targeting a building associated with Christians for Israel in Nijkerk, Netherlands.Jordanone statement claims responsibility for a drone attack targeting Israeli-affiliated infrastructure in Jordan, while emphasizing civilian evacuation warnings and framing the operation within a broader resistanceKuwaitFor example, content includes battlefield or intelligence-style analysis, such as satellite imagery purportedly showing damage to U.S.-linked air facilities in Bahrain and Kuwait following Iranian strikes.NetherlandsThe most recent identifiable content, dated April 4, included a video claiming responsibility for an attack targeting a building associated with Christians for Israel in Nijkerk, Netherlands.
Industries
DefenseNews publishes a list of Western companies, including technology firms, financial institutions, and defense-related entities, framing them as potential targets linked to broader geopolitical events.TechnologyIn this example, Sabereen News publishes a list of Western companies, including technology firms, financial institutions, and defense-related entities, framing them as potential targets linked to broader geopolitical