
Dragon Boss PUP Disabled Antivirus and Exposed 23,565 Endpoints to Update Hijacking
Summary
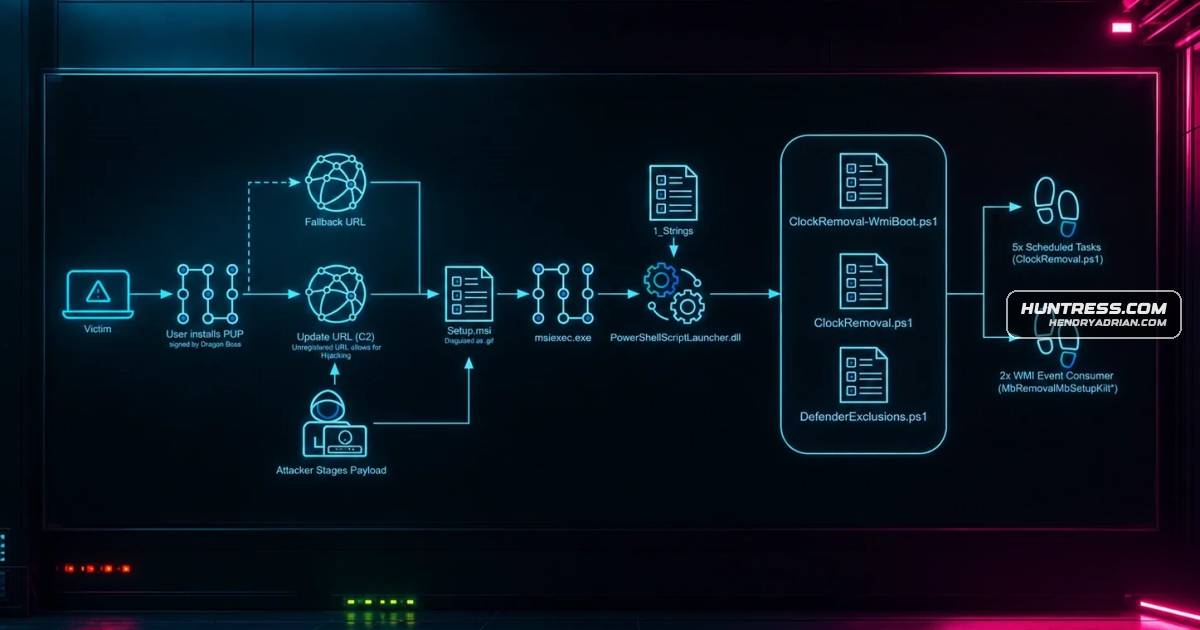
Huntress analyzed Dragon Boss Solutions software that silently disabled antivirus and persisted on Windows systems. It found an unregistered update domain could let an attacker deliver arbitrary payloads; sinkholed requests came from 23,565 unique IPs in 24 hours.
Key points
- The software’s PowerShell payload ran with SYSTEM privileges, killed or removed security products, blocked antivirus update domains, and added Windows Defender exclusions.
- WMI event subscriptions and scheduled tasks maintained persistence and repeatedly attempted to disable or remove security tools.
- An unregistered primary update domain, chromsterabrowser[.]com, could have allowed anyone who registered it to deliver arbitrary payloads to systems running that software.
- Huntress registered and sinkholed the domain; 23,565 unique IP addresses connected during a 24-hour period, representing systems attempting to contact the update infrastructure.
- The observed infections spanned 124 countries. Huntress identified 324 infections in high-value networks, including educational, operational technology, government, and healthcare organizations.
- Huntress advises checking for Dragon Boss Solutions-signed processes, MbRemoval or MbSetup WMI artifacts, ClockRemoval tasks, suspicious Defender exclusions, and antivirus-domain blocks in Windows hosts files.
Article Details
- Attack Vectors
- Dragon Boss Solutions-signed PUP/updater software used its update mechanism to download and silently install MSI payloads, running with SYSTEM privileges.
- The updater configuration included update domains, including an unregistered primary domain that infected hosts contacted; Huntress reported that registering it could allow arbitrary payload delivery to those hosts.
- The MSI used PowerShell scripts to disable or remove antivirus products, block their update domains through hosts-file changes, and add Windows Defender exclusions.
- The scripts established persistence through WMI event subscriptions and scheduled tasks, including boot, logon, and recurring tasks.
- The installer checked for administrator privileges, virtual machines, internet connectivity, and installed security products before deploying its payload.
- Defensive Notes
- Hunt for WMI event subscriptions with consumer names containing “MbRemoval” or “MbSetup,” and scheduled tasks referencing WMILoad directories or ClockRemoval.
- Alert on processes signed by Dragon Boss Solutions LLC.
- Review Windows hosts files for entries blocking antivirus vendor domains.
- Check Windows Defender exclusions for suspicious paths such as DGoogle, EMicrosoft, and DDapps.
- Investigate endpoints running Dragon Boss Solutions software for the listed updater, payload, and persistence artifacts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | artificialupdates[.]com | Listed as a network indicator associated with the Dragon Boss Solutions operation; its specific role is not stated. |
| DOMAIN | chromsterabrowser[.]com | Unregistered primary update domain in an updater configuration; infected hosts contacted it, and Huntress registered and sinkholed it. |
| DOMAIN | chromsteraupdates[.]com | Listed as a network indicator associated with the Dragon Boss Solutions operation; its specific role is not stated. |
| DOMAIN | dragonstraffic[.]com | Listed as a network indicator associated with the Dragon Boss Solutions operation; its specific role is not stated. |
| DOMAIN | updaterituals[.]com | Listed as a network indicator associated with the Dragon Boss Solutions operation; its specific role is not stated. |
| DOMAIN | worldwidewebframework2[.]com | Listed as a network indicator associated with the Dragon Boss Solutions operation; its specific role is not stated. |
| DOMAIN | worldwidewebframework3[.]com | Domain identified as C2 and sinkholed by Huntress. |
| DOMAIN | worldwidewebuniverse3[.]com | Domain identified as the active C2/update domain for the updater. |
| SHA256 | 26ddd0712a101b27b018658b4072ad56bb4083026c797b0345b2cce43862fc83 | SHA-256 of the MSI’s !_StringData payload containing installer instructions. |
| SHA256 | 40ac30ce1e88c47f317700cc4b5aa0a510f98c89e11c32265971564930418372 | SHA-256 of the Setup.msi payload. |
| SHA256 | 909539d3ef8dedc3be56381256713fa5545cc7fd3d3d0e0428f7efb94a7e71cb | SHA-256 of RaceCarTwo.exe, identified as the initial loader/updater. |
| SHA256 | da6aba50f9908f5f29d877dfaaca1ef6e03d597bb7b52bd294b4ec644fe7e6c0 | SHA-256 of the ClockRemoval-WmiBoot.ps1 persistence script. |
| SHA256 | feb13087c43406da7f2cea26b003a9b93db0e6b544b10bd57342d5dbbb18ba02 | SHA-256 of the manually reconstructed ClockRemoval.ps1 AV-killer script. |
| URL | hxxps[:]//dl[.]isready26[.]online/image/ldk4945jfds.gif | URL from which the updater obtained a Setup.msi payload disguised with a .gif filename. |
MITRE ATT&CK
T1036.008 · Masquerade File TypeA Setup.msi payload was delivered under the filename ldk4945jfds.gif.T1053.005 · Scheduled TaskThe payload created scheduled tasks for boot, startup, logon, and recurring execution.T1059.001 · PowerShellThe installer launched ClockRemoval scripts through PowerShell.T1105 · Ingress Tool TransferThe updater contacted configured remote domains and downloaded MSI update payloads.T1112 · Modify RegistryThe script manipulated registry entries to disable antivirus services and remove antivirus-related Run keys.T1218.007 · MsiexecThe update mechanism silently installed the downloaded MSI package through the Windows Installer Service.T1497.001 · System ChecksThe installer checked whether it was running in a virtual machine before deploying the main payload.T1518.001 · Security Software DiscoveryThe installer checked registry data for installed security products, including Malwarebytes, Kaspersky, McAfee, and ESET.T1546.003 · Windows Management Instrumentation Event SubscriptionThe script established WMI event subscriptions and recreated them at boot to maintain persistence and monitor process starts.T1562.001 · Disable or Modify ToolsClockRemoval killed, disabled, and removed antivirus products and added Windows Defender exclusions.T1562.006 · Indicator BlockingThe script redirected antivirus update domains to 0.0.0.0 in the hosts file, blocking access to those indicators and updates.