
Likely Former Black Basta Affiliates Target Executives With Automated Teams Help-Desk Scams
Summary
ReliaQuest says a likely former Black Basta affiliate campaign pairs email bombing with Teams help-desk impersonation and RMM tools to target executives, reporting rapid access and recommending verification, tool controls, and targeted training.
Key points
- ReliaQuest assesses that former Black Basta affiliates are highly likely involved, while noting that collaboration with other groups or imitation remain possible.
- The reported sequence combines email bombing with impersonation of IT support through Microsoft Teams to pressure targets into remote-access sessions.
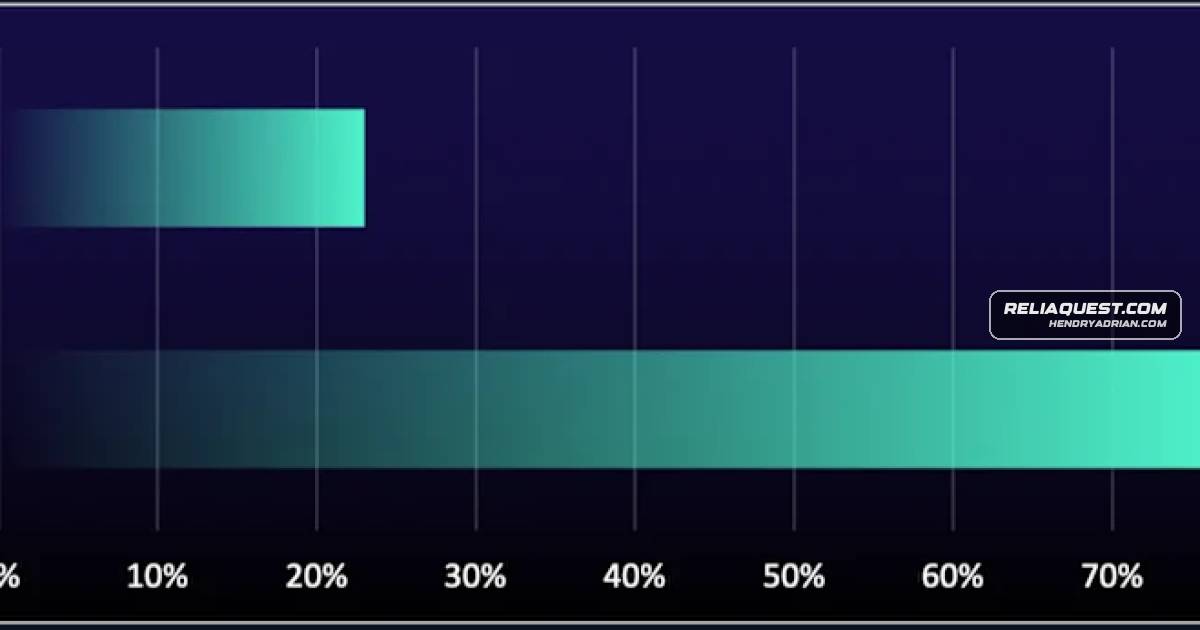
- From March 1 to April 1, 2026, 77% of observed incidents targeted senior-level employees, up from 59% in January and February.
- Some observed activity moved from initial chat engagement to script execution in as little as 12 minutes; attackers used Supremo and Quick Assist for remote access.
- ReliaQuest says it has not observed ransomware deployment in the incidents described, though the activity is consistent with pre-ransomware staging.
- Recommended defenses include out-of-band verification for remote-access requests, strict controls on RMM tools, and targeted simulations for senior staff.
Article Details
- Attack Vectors
- Mass email bombing followed by help-desk impersonation through Microsoft Teams or phone calls to create urgency and gain remote access.
- Social engineering of senior employees to persuade them to join sessions using Supremo Remote Desktop or Quick Assist.
- Execution of scripts such as MailAccountWizard.jar during remote-management sessions for pre-ransomware staging.
- Defensive Notes
- Require out-of-band, multi-channel verification for help-desk requests involving remote access.
- Use application allow-listing and restrict approved RMM tools to authorized IT personnel; control Quick Assist execution for general users.
- Train executives and managers with simulations that combine email bombing and urgent Teams impersonation.
- Alert on email-bomb activity followed by suspicious Teams outreach and RMM-tool execution.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | griffinintl[.]net | Domain identified in connection with a help-desk impersonation identity. |
| DOMAIN | groupbiocare[.]com | Domain identified in connection with a help-desk impersonation identity. |
| IPV4 | 84[.]42[.]92[.]111 | Threat actor-linked source IP address used to initiate contact. |
| IPV4 | 84[.]42[.]92[.]176 | Threat actor-linked source IP address used to initiate contact. |
| IPV4 | 84[.]42[.]92[.]225 | Threat actor-linked source IP address used to initiate contact. |
| IPV4 | 84[.]42[.]94[.]127 | Threat actor-linked source IP address used to initiate contact. |
MITRE ATT&CK
T1021 · Remote ServicesAttackers abused Supremo Remote Desktop and Quick Assist sessions to gain interactive access to victims' hosts.T1059 · Command and Scripting InterpreterAfter establishing an RMM session, attackers executed malicious scripts, including scripts named MailAccountWizard.jar.T1078 · Valid AccountsThe article reports use of disposable onmicrosoft.com tenant accounts and impersonation identities to pose as help-desk personnel.T1566 · PhishingAttackers used mass email bombing and Microsoft Teams help-desk impersonation to initiate contact and create urgency.
Threat Actors
Vendors
Products
Microsoft Teamshighly automated campaign by likely former Black Basta affiliates combines mass email bombing with Microsoft Teams help-desk impersonation to gain remote access to senior leaders within minutes, often using RMM toolsWindows 11Supremo was not the only RMM tool recently observed; threat actors also used Quick Assist, which is natively installed on Windows 11 devices.
Tools
Quick Assistto gain remote access to senior leaders within minutes, often using RMM tools like Supremo and Quick Assist.Supremo Remote DesktopSupremo Remote Desktop and Quick Assist are primary RMM tools abused to convert social engineering into hands-on access and script execution (e.g., MailAccountWizard.jar) for pre-ransomware staging.
Countries
Industries
ManufacturingManufacturing and Professional, Scientific, and Technical Services (PSTS) each accounted for 26% of incidents, mirroring Black Basta’s historical sector preferences.Professional, scientific, and technical servicesManufacturing and Professional, Scientific, and Technical Services (PSTS) each accounted for 26% of incidents, mirroring Black Basta’s historical sector preferences.