
TrickMo Variant Uses TON C2, SSH Tunneling and SOCKS5 Proxies
Summary
ThreatFabric reports that TrickMo C targets banking and crypto-wallet users in France, Italy and Austria. The variant uses TON for C2 and adds reconnaissance, SSH tunneling and SOCKS5 proxying that can turn infected Android devices into network pivots.
Key points
- ThreatFabric observed the variant targeting banking and cryptocurrency wallet users in France, Italy and Austria between January and February 2026.
- The malware routes C2 requests through an embedded TON proxy to .adnl endpoints.
- Its network subsystem supports reconnaissance commands including curl, dnslookup, ping, telnet and traceroute.
- SSH tunneling and authenticated SOCKS5 proxying can turn infected devices into network pivots and traffic-exit nodes.
- The malware is distributed through phishing websites and dropper apps that impersonate Google Play Services or TikTok-related apps.
- The variant retains capabilities including credential phishing, keylogging, screen recording and SMS interception.
- ThreatFabric says dormant Pine hooking and NFC-related features are present but not implemented.
Article Details
- Attack Vectors
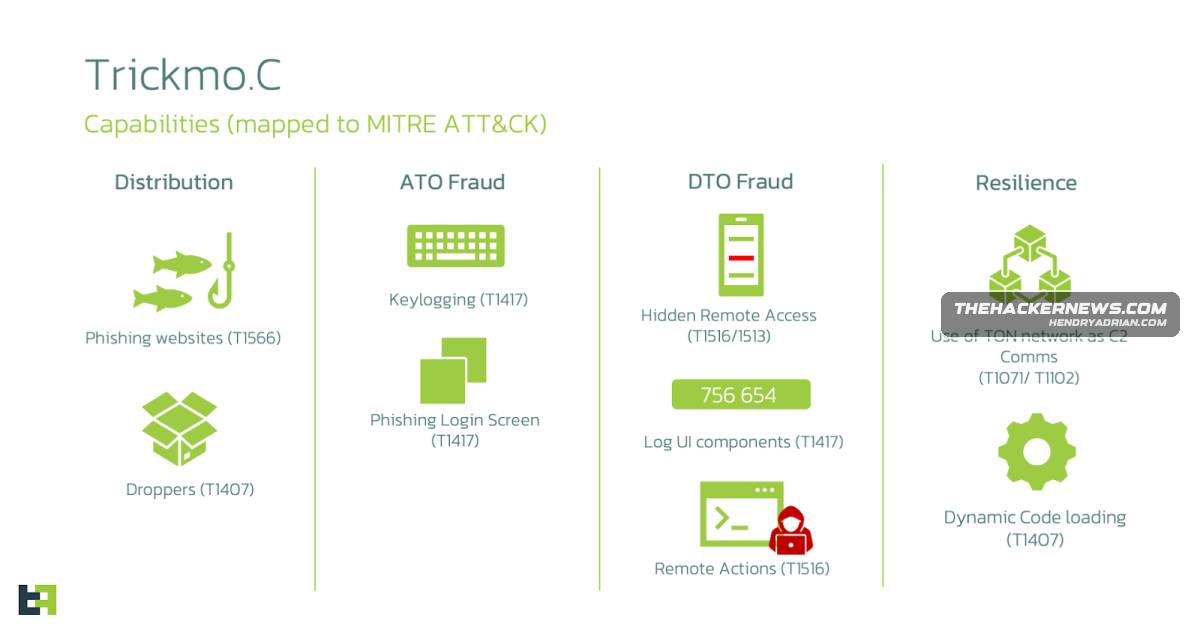
- Phishing websites and dropper apps distribute TrickMo C. The dropper apps masquerade as adult-friendly TikTok-related apps, while TrickMo impersonates Google Play Services.
- The dropper retrieves a runtime-loaded APK module, dex.module, from attacker-controlled infrastructure.
- TrickMo routes HTTP command-and-control requests through an embedded TON proxy to .adnl hostnames.
- The malware uses Android accessibility services to hijack one-time passwords and also supports credential phishing, keystroke logging, screen recording or streaming, and SMS interception.
- SSH tunnelling and authenticated SOCKS5 proxying let compromised devices act as network pivots and traffic-exit nodes. Reconnaissance commands include curl, dnslookup, ping, telnet, and traceroute.
MITRE ATT&CK
T1046 · Network Service DiscoveryThe malware's network subsystem uses commands such as dnslookup, ping, telnet, and traceroute for reconnaissance from the victim device's network position.T1071.001 · Web ProtocolsThe bot's HTTP client sends command-and-control requests through an embedded TON proxy.T1090 · ProxyAuthenticated SOCKS5 proxying turns infected devices into network exit nodes for attacker traffic.T1407The dropper retrieves the dex.module APK at runtime from attacker-controlled infrastructure.T1412TrickMo can intercept SMS messages, including messages relevant to one-time passwords.T1417.001TrickMo is reported to log keystrokes.T1513TrickMo can record screens and facilitate live screen streaming.T1572 · Protocol TunnelingThe variant supports SSH tunnelling to extend its network-pivoting capabilities.T1660The variant is distributed through phishing websites and dropper apps.
Malware
Products
AndroidThreatFabric has identified a new TrickMo Android banking trojan variant that uses The Open Network (TON) for stealthy command-and-control communications.Google Play ServicesThe malware is distributed through phishing websites and dropper apps impersonating Google Play Services and TikTok-related apps.The Open Network (TON)ThreatFabric has identified a new TrickMo Android banking trojan variant that uses The Open Network (TON) for stealthy command-and-control communications.TikTokThe malware is distributed through phishing websites and dropper apps impersonating Google Play Services and TikTok-related apps.
Countries
AustriaThe malware is actively targeting banking and cryptocurrency wallet users in France, Italy, and Austria while adding network pivoting features such as SSH tunnelling and SOCKS5 proxying.FranceThe malware is actively targeting banking and cryptocurrency wallet users in France, Italy, and Austria while adding network pivoting features such as SSH tunnelling and SOCKS5 proxying.ItalyThe malware is actively targeting banking and cryptocurrency wallet users in France, Italy, and Austria while adding network pivoting features such as SSH tunnelling and SOCKS5 proxying.
Industries
BankingThreatFabric has identified a new TrickMo Android banking trojan variant that uses The Open Network (TON) for stealthy command-and-control communications.CryptocurrencyThe malware is actively targeting banking and cryptocurrency wallet users in France, Italy, and Austria while adding network pivoting features such as SSH tunnelling and SOCKS5 proxying.