
DNS and WHOIS Analysis Maps Infrastructure Linked to Eight Iran-Affiliated APT Groups
Summary
Researchers analyzed 191 DNS, domain, IP and WHOIS indicators linked to eight Iran-affiliated APT groups, identifying historical resolutions, likely malicious registrations, look-alike domains and infrastructure assessed as part of an impersonation campaign.
Key points
- The researchers processed 190 indicators from eight cited reports into 191 unique indicators: four subdomains, 136 domains and 51 IP addresses.
- Network data showed 9,849 client IP addresses communicated with nine APT42-linked domains between February and April 2026; 1,841 potential victim-owned IP addresses communicated with 31 IP indicators between October 2025 and April 2026.
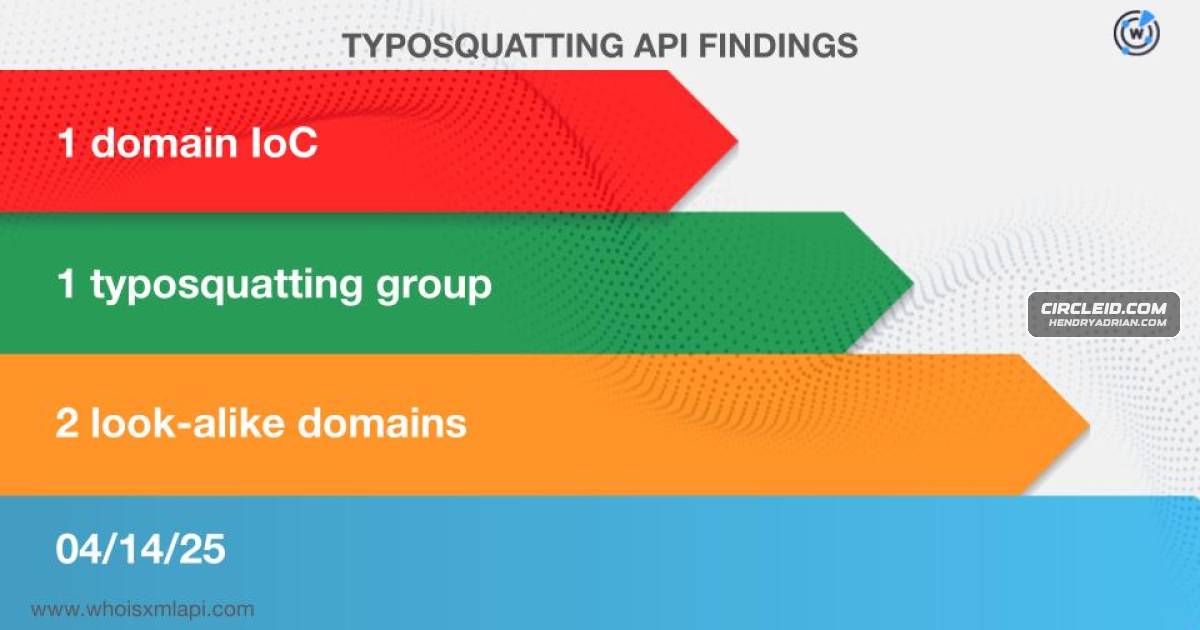
- The analysis identified 73 domains assessed as likely registered with malicious intent and one APT42-linked domain bulk-registered alongside two look-alikes.
- Four Pioneer Kitten subdomains shared infrastructure fingerprints and timelines; the researchers assessed them as appearing to be part of a coordinated impersonation campaign targeting vendors including Sophos and Fortinet.
- The researchers counted 5,455 historical domain-to-IP resolutions across 130 domains; 50 APT42 domains and three Pioneer Kitten domains reportedly continued resolving in 2026.
- WHOIS history for 121 domains contained 148 unique email addresses, including 15 public email addresses.
- The article cautions that entities labeled as threats or malicious may later be found harmless and recommends supplementary investigation.
Article Details
- Attack Vectors
- APT42-linked look-alike domains were bulk-registered alongside work-meeting[.]info.
- Pioneer Kitten subdomains were reported as active malware-distribution infrastructure impersonating cybersecurity and technology vendors, including Sophos and Fortinet.
- DNS queries and historical domain-to-IP resolutions connected client and potential victim IP addresses with APT-related domains and IPs.
- The analysis identified domains reported as likely registered with malicious intent, including examples attributed to APT42 and APT34.
- Defensive Notes
- Monitor the reported APT-related domains, subdomains, and IP addresses in DNS and network telemetry.
- Corroborate threat classifications through supplementary investigation; the article cautions that some identified entities may later be deemed harmless or have their context change.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | arrow-click[.]info | APT42 domain IoC with 360 historical domain-to-IP resolutions reported. |
| DOMAIN | asiacall[.]net | APT34 domain IoC with historical domain-to-IP resolutions reported. |
| DOMAIN | backback[.]info | APT42 domain IoC with 362 historical domain-to-IP resolutions reported. |
| DOMAIN | iqwebservice[.]com | APT34-associated domain identified as likely registered with malicious intent. |
| DOMAIN | live-meet[.]cloud | APT42-associated domain identified as likely registered with malicious intent. |
| DOMAIN | live-meet[.]info | APT42-associated domain identified as likely registered with malicious intent. |
| DOMAIN | rap-art[.]info | APT42 domain IoC with 361 historical domain-to-IP resolutions reported. |
| DOMAIN | sophos[.]one | Pioneer Kitten domain IoC with historical domain-to-IP resolutions reported; the article links related subdomain infrastructure to vendor impersonation. |
| DOMAIN | top-game[.]online | APT42-associated domain identified as likely registered with malicious intent. |
| DOMAIN | work-meeting[.]info | APT42-linked domain IoC reported as bulk-registered with the look-alikes workmeeting[.]info and workmeeting[.]online. |
| DOMAIN | workmeeting[.]info | APT42-linked look-alike domain reported as bulk-registered alongside work-meeting[.]info. |
| DOMAIN | workmeeting[.]online | APT42-linked look-alike domain reported as bulk-registered alongside work-meeting[.]info. |
| DOMAIN | world-shop[.]online | APT42-associated domain identified as likely registered with malicious intent. |
| HOSTNAME | cloud[.]sophos[.]one | Pioneer Kitten-associated subdomain reported as active malware-distribution and C2 infrastructure impersonating a Sophos cloud/API service. |
| HOSTNAME | fortigate[.]forticloud[.]online | Pioneer Kitten-associated subdomain reported as active malware-distribution infrastructure in a campaign impersonating Fortinet and other vendors. |
| IPV4 | 146[.]19[.]254[.]238 | APT42 IP IoC with 1,000 historical IP-to-domain resolutions reported. |
| IPV4 | 162[.]0[.]230[.]185 | MuddyWater IP IoC with 1,000 historical IP-to-domain resolutions reported. |
| IPV4 | 178[.]209[.]51[.]61 | BladedFeline IP IoC with 267 historical IP-to-domain resolutions reported. |
| IPV4 | 185[.]191[.]204[.]203 | Peach Sandstorm IP IoC with historical IP-to-domain resolutions reported. |
| IPV4 | 185[.]82[.]73[.]162 | CyberAv3ngers IP IoC with historical IP-to-domain resolutions reported. |
| IPV4 | 193[.]149[.]187[.]41 | Pioneer Kitten IP IoC with 1,000 historical IP-to-domain resolutions reported. |
| IPV4 | 82[.]25[.]35[.]25 | Void Manticore IP IoC with 515 historical IP-to-domain resolutions reported. |
| IPV4 | 91[.]132[.]95[.]117 | APT34 IP IoC with historical IP-to-domain resolutions reported. |
MITRE ATT&CK
T1071.004 · DNSThe investigation describes client IPs communicating with APT-related domain IoCs through DNS queries and reports historical domain-to-IP resolutions.T1583.001 · DomainsThe article reports maliciously intended domain registrations, including bulk-registered look-alikes associated with APT42.
Threat Actors
BladedFelineThe article says BladedFeline is a subgroup of APT34 and reports IP infrastructure associated with it.BLEAK IONNamed in the article as an alternate name for Peach Sandstorm, which is associated with IP infrastructure.CALANQUE IONThe article attributes domain and IP infrastructure, including bulk-registered look-alike domains, to APT42.Charming KittenNamed in the article as an alternate name for APT42, which is associated with domain and IP infrastructure.COBALT FOXGLOVENamed in the article as an alternate name for Pioneer Kitten, which is associated with malware-distribution infrastructure.ElfinNamed in the article as an alternate name for Peach Sandstorm, which is associated with IP infrastructure.Fox KittenNamed in the article as an alternate name for Pioneer Kitten, which is associated with malware-distribution infrastructure.Helix KittenNamed in the article as an alternate name for APT34, which is associated with maliciously intended domain infrastructure.HOLMIUMNamed in the article as an alternate name for Peach Sandstorm, which is associated with IP infrastructure.Mango SandstormNamed in the article as an alternate name for MuddyWater, which is associated with IP infrastructure.MERCURYNamed in the article as an alternate name for MuddyWater, which is associated with IP infrastructure.MuddyWaterThe article identifies MuddyWater-associated IP IoCs with historical IP-to-domain resolutions.OilRigNamed in the article as an alternate name for APT34, which is associated with maliciously intended domain infrastructure.PARISITENamed in the article as an alternate name for Pioneer Kitten, which is associated with malware-distribution infrastructure.Peach SandstormThe article identifies Peach Sandstorm-associated IP IoCs with historical IP-to-domain resolutions.Pioneer KittenThe article attributes domains, IPs, and subdomains reported as active malware-distribution infrastructure to Pioneer Kitten.SeedwormNamed in the article as an alternate name for MuddyWater, which is associated with IP infrastructure.SOLAR IONThe article attributes domain infrastructure, including domains likely registered with malicious intent, to APT34.Static KittenNamed in the article as an alternate name for MuddyWater, which is associated with IP infrastructure.Storm-842Named in the article as an alternate name for Void Manticore, which is associated with destructive wiping attacks and influence operations.TA450Named in the article as an alternate name for MuddyWater, which is associated with IP infrastructure.UNC788Named in the article as an alternate name for APT42, which is associated with domain and IP infrastructure.Void ManticoreThe article identifies Void Manticore-associated IP IoCs with historical IP-to-domain resolutions and describes the group as conducting destructive wiping attacks and influence operations.Yellow Dev 15Named in the article as an alternate name for Pioneer Kitten, which is associated with malware-distribution infrastructure.
Vendors
Tools
DNS Chronicle APIFinally, we queried the domain IoCs on DNS Chronicle API and learned that:Domain Info APIAfter that, we queried the domain IoCs on WHOIS API and filled in gaps using details from Domain Info API.First Watch Malicious Domains Data FeedNext up, we scoured the First Watch Malicious Domains Data Feed and discovered that 73 domain IoCs for two of the three APT groups—APT42 and APT34—were deemed likely to have been registered with malicious intent.IASCSample network traffic data from the IASC revealed that 9,849 unique client IP addresses under three distinct ASNs communicated with nine domain IoCs all tied to APT42 between 9 February and 9 April 2026 via 129,964 DNSTyposquatting APIOur Typosquatting API searches, meanwhile, showed that one domain IoC connected to APT42 was bulk-registered with two look-alikes on 14 April 2025.WHOIS APIAfter that, we queried the domain IoCs on WHOIS API and filled in gaps using details from Domain Info API.WHOIS History APIFirst off, we queried the 136 domain IoCs on WHOIS History API and discovered that 121 had 148 unique email addresses in their historical WHOIS records.WhoisXML API MCP Serverfrom subdomains, legitimate domain filtering, and weeding out of inactive domains) aided by the WhoisXML API MCP Server we ended up with 191 unique IoCs comprising four subdomains, 136 domains, and 51 IP addresses for
Countries
IranThe article analyzes DNS and WHOIS footprints tied to eight Iran-affiliated APT groups, uncovering extensive infrastructure, historical resolutions, and additional artifacts linked to their domains, IPs, and emailIsraelAlso known as “Soldiers of Solomon” and active since at least 2020, it has made disputed and false claims of critical infrastructure compromises in IsraelSaudi ArabiaAlso known as “APT33,” “HOLMIUM,” or “Elfin” and active since at least 2013, it has targeted organizations in the aviation and energy sectors in the U.S., Saudi Arabia, and South KoreaSouth KoreaAlso known as “APT33,” “HOLMIUM,” or “Elfin” and active since at least 2013, it has targeted organizations in the aviation and energy sectors in the U.S., Saudi Arabia, and South KoreaUnited StatesAlso known as “APT33,” “HOLMIUM,” or “Elfin” and active since at least 2013, it has targeted organizations in the aviation and energy sectors in the U.S., Saudi Arabia, and South Korea
Industries
AviationAlso known as “APT33,” “HOLMIUM,” or “Elfin” and active since at least 2013, it has targeted organizations in the aviation and energy sectors in the U.S., Saudi Arabia, and South KoreaChemicaltargeted Middle Eastern and international victims, specifically from the financial, government, energy, chemical, and telecommunications sectorsDefense2017, it has targeted government and private organizations in the telecommunications, local government, defense, and oil and natural gas sectors in the Middle East, Asia, Africa, Europe, and North AmericaEnergyit has targeted Middle Eastern and international victims, specifically from the financial, government, energy, chemical, and telecommunications sectorsfinancialsince at least 2014, it has targeted Middle Eastern and international victims, specifically from the financial, government, energy, chemical, and telecommunications sectorsGovernmentleast 2014, it has targeted Middle Eastern and international victims, specifically from the financial, government, energy, chemical, and telecommunications sectorsOil and natural gasgovernment and private organizations in the telecommunications, local government, defense, and oil and natural gas sectors in the Middle East, Asia, Africa, Europe, and North AmericaTelecommunicationsand international victims, specifically from the financial, government, energy, chemical, and telecommunications sectors