
DNS and WHOIS Analysis Maps Infrastructure Linked to Six 2025 Ransomware Families
Summary
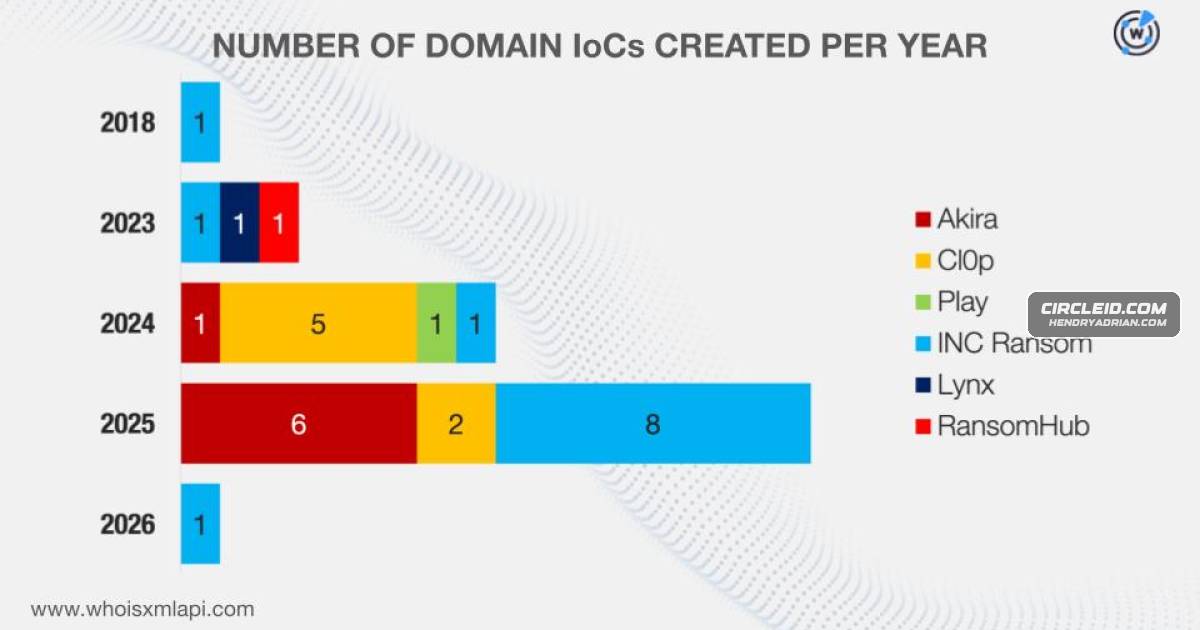
A WhoisXML API analysis of ransomware-linked DNS, WHOIS and traffic data mapped 267 network IoCs across six 2025 top-10 ransomware families, identifying early-flagged Akira domains, look-alike registrations and associated infrastructure.
Key points
- The analysis examined 267 network IoCs—28 domains, 236 IP addresses and three email addresses—linked to Qilin, Akira, Play, INC Ransom, Lynx and RansomHub.
- Three Akira-related domains were classified as malicious 15–37 days before they were publicly reported as such.
- The researchers found simplerwebs[.]world, linked to INC Ransom, was bulk-registered with eight look-alike domains on January 3, 2025.
- Historical DNS queries recorded 2,728 domain-to-IP resolutions for 28 domains and 25,643 IP-to-domain resolutions for 160 IP addresses.
- Sample traffic showed 2,626 potential victim IP addresses across 166 ASNs communicating with 40 IoC IP addresses between February 15 and March 16, 2026.
- WHOIS and email enrichment identified 8,491 email-connected domains, 36 of which the analysis deemed malicious; the article cautions that some flagged entities may prove harmless and recommends further investigation.
Article Details
- Attack Vectors
- The report says the Play ransomware group is known for infiltrating companies through exposed RDP servers and exploiting vulnerabilities.
- The report describes Cl0p as using data theft and ransom demands without file encryption, and SafePay and Lynx as using double-extortion tactics.
- Infrastructure analysis identified bulk-registered look-alike domains and Akira-associated domains that the report says were likely registered with malicious intent.
- Defensive Notes
- The article recommends supplementary investigation to corroborate threat designations, noting some entities identified as threats or malicious may later prove harmless.
- Treat the 2,626 IP addresses observed communicating with 40 IP IoCs as potential victims; the article does not confirm that those systems were compromised.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 2rxyt9urhq0bgj[.]org | Akira-associated domain identified as an IoC; the report says it was classified as malicious 37 days before public reporting. |
| DOMAIN | angryipscanner[.]org | Domain listed as an Akira-related domain IoC in the report's historical DNS analysis. |
| DOMAIN | ev2sirbd269o5j[.]org | Akira-associated domain identified as an IoC; the report says it was classified as malicious 29 days before public reporting. |
| DOMAIN | he1p-center[.]com | Domain listed as a Cl0p-related domain IoC in the report's historical DNS analysis. |
| DOMAIN | ijt0l3i8brit6q[.]org | Akira-associated domain identified as an IoC; the report says it was classified as malicious 15 days before public reporting. |
| DOMAIN | in2pay[.]com | Domain listed as a Cl0p-related domain IoC in the report's historical DNS analysis. |
| DOMAIN | opmanager[.]pro | Domain listed as an Akira-related domain IoC in the report's historical DNS analysis. |
| DOMAIN | pubstorm[.]com | Domain listed as a Cl0p-related domain IoC in the report's historical DNS analysis. |
| DOMAIN | simplerwebs[.]world | Domain linked by the report to INC Ransom and bulk-registered with eight look-alike domains. |
| IPV4 | 109[.]205[.]195[.]21 | IP address listed as an Akira-related IoC in the report's historical DNS analysis. |
| IPV4 | 164[.]138[.]90[.]2 | IP address listed as a RansomHub-related IoC in the report's historical DNS analysis. |
| IPV4 | 176[.]113[.]115[.]209 | IP address listed as a Qilin-related IoC in the report's historical DNS analysis. |
| IPV4 | 212[.]83[.]137[.]94 | IP address listed as an INC Ransom-related IoC in the report's historical DNS analysis. |
| IPV4 | 46[.]161[.]27[.]113 | IP address listed as a Cl0p-related IoC in the report's historical DNS analysis. |
MITRE ATT&CK
Threat Actors
Malware
AkiraThe report analyzes DNS, WHOIS, and network IoCs tied to six of 2025’s top ransomware families—Qilin, Akira, Play, INC Ransom, Lynx, and RansomHub—and shows how they connect to domains, IPs, and emails at scale.BabukIt also highlights early malicious registration patterns, historical DNS activity, and additional artifacts linked to the broader ransomware ecosystem, including Cl0p, Babuk, SafePay, DragonForce, and Babuk2.Babuk2It also highlights early malicious registration patterns, historical DNS activity, and additional artifacts linked to the broader ransomware ecosystem, including Cl0p, Babuk, SafePay, DragonForce, and Babuk2.BianLianand coming ransomware families—RansomHub, LockBit 3.0, Play, Akira, Hunters, Medusa, BlackBasta, Qilin, BianLian, and INC Ransom (aka Lynx).BlackBastadubbed 2025’s up and coming ransomware families—RansomHub, LockBit 3.0, Play, Akira, Hunters, Medusa, BlackBasta, Qilin, BianLian, and INC Ransom (aka Lynx).Cl0pIt also highlights early malicious registration patterns, historical DNS activity, and additional artifacts linked to the broader ransomware ecosystem, including Cl0p, Babuk, SafePay, DragonForce, and Babuk2.DragonForceIt also highlights early malicious registration patterns, historical DNS activity, and additional artifacts linked to the broader ransomware ecosystem, including Cl0p, Babuk, SafePay, DragonForce, and Babuk2.Huntersof what were dubbed 2025’s up and coming ransomware families—RansomHub, LockBit 3.0, Play, Akira, Hunters, Medusa, BlackBasta, Qilin, BianLian, and INC Ransom (aka Lynx).INC RansomThe report analyzes DNS, WHOIS, and network IoCs tied to six of 2025’s top ransomware families—Qilin, Akira, Play, INC Ransom, Lynx, and RansomHub—and shows how they connect to domains, IPs, and emails at scale.LockBitinvestigated the DNS footprint of what were dubbed 2025’s up and coming ransomware families—RansomHub, LockBit 3.0, Play, Akira, Hunters, Medusa, BlackBasta, Qilin, BianLian, and INC Ransom (aka Lynx).LynxThe report analyzes DNS, WHOIS, and network IoCs tied to six of 2025’s top ransomware families—Qilin, Akira, Play, INC Ransom, Lynx, and RansomHub—and shows how they connect to domains, IPs, and emails at scale.Medusawhat were dubbed 2025’s up and coming ransomware families—RansomHub, LockBit 3.0, Play, Akira, Hunters, Medusa, BlackBasta, Qilin, BianLian, and INC Ransom (aka Lynx).PlayThe report analyzes DNS, WHOIS, and network IoCs tied to six of 2025’s top ransomware families—Qilin, Akira, Play, INC Ransom, Lynx, and RansomHub—and shows how they connect to domains, IPs, and emails at scale.QilinThe report analyzes DNS, WHOIS, and network IoCs tied to six of 2025’s top ransomware families—Qilin, Akira, Play, INC Ransom, Lynx, and RansomHub—and shows how they connect to domains, IPs, and emails at scale.RansomHubThe report analyzes DNS, WHOIS, and network IoCs tied to six of 2025’s top ransomware families—Qilin, Akira, Play, INC Ransom, Lynx, and RansomHub—and shows how they connect to domains, IPs, and emails at scale.SafePayIt also highlights early malicious registration patterns, historical DNS activity, and additional artifacts linked to the broader ransomware ecosystem, including Cl0p, Babuk, SafePay, DragonForce, and Babuk2.
Vendors
Tools
Bulk IP Geolocation LookupWe then queried the IP addresses on Bulk IP Geolocation Lookup and found out that:DNS Chronicle API[T1584.001 ] Compromise Infrastructure: Domains – Historical and registered domains were used to support ransomware activity (‘historical WHOIS records’ and ‘DNS Chronicle API queries for the 28 domains’).IASCSample network traffic data from the IASC revealed that 2,626 unique potential victim IP addresses under 166 distinct ASNs communicated with 40 of the IP IoCs between 15 February and 16 March 2026Reverse WHOIS APIOur Reverse WHOIS API queries for the public email addresses led to the discovery of 8,491 unique email-connected domains after those already tagged as IoCs were filtered out.Typosquatting Data FeedWe began our investigation by scouring the Typosquatting Data Feed for signs of the 28 domains.WHOIS APIWe then queried the 29 domains on WHOIS API and learned that:WHOIS History APIFirst, we queried the domains on WHOIS History API and discovered that 16 had 49 email addresses in their historical WHOIS records.WhoisXML API MCP ServerWith the aid of the WhoisXML API MCP Server, we extracted domains from the subdomains identified as IoCs and weeded out those that belonged to legitimate entities, did not leave DNS traces behind, and were only
Industries
Critical infrastructureOften targets the critical infrastructure, financial, and government sectors using encryptionless tactics to steal data and demand ransoms without encrypting filesEducationKnown for highly aggressive, rapid, and targeted attacks against enterprises in the healthcare, manufacturing, education, and government sectors primarily in North America and EuropefinancialOften targets the critical infrastructure, financial, and government sectors using encryptionless tactics to steal data and demand ransoms without encrypting filesGovernmentOften targets the critical infrastructure, financial, and government sectors using encryptionless tactics to steal data and demand ransoms without encrypting filesHealthcareKnown for highly aggressive, rapid, and targeted attacks against enterprises in the healthcare, manufacturing, education, and government sectors primarily in North America and EuropeManufacturingKnown for highly aggressive, rapid, and targeted attacks against enterprises in the healthcare, manufacturing, education, and government sectors primarily in North America and Europe