
Hexastrike Attributes AtlasCross RAT Campaign to Silver Fox APT
Summary
Hexastrike attributes an AtlasCross RAT campaign using look-alike domains impersonating software brands to Silver Fox APT. Its infrastructure analysis identified 13 network IoCs and used DNS and WHOIS pivots to map potential victim connections and related domains.
Key points
- Hexastrike reports a multistage AtlasCross RAT campaign using look-alike domains impersonating brands including Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.
- Hexastrike attributes the activity to Silver Fox APT; the article presents this as the researchers’ attribution.
- The analysis identified 13 network IoCs: 12 domains and one IP address. Hexastrike says its domain-legitimacy checks found none of the 12 domains belonged to legitimate organizations.
- Sample traffic data showed 829 unique client IP addresses communicating with two domain IoCs through 11,388 DNS queries between March 9 and April 28, 2026.
- The researchers identified 33 potentially victim-owned IP addresses that communicated with the IP IoC between November 17, 2025, and February 21, 2026.
- Reverse WHOIS analysis linked four public email addresses to 2,584 unique email-connected domains; the analysis also found 33 IP-connected domains and 35 string-connected domains.
- Hexastrike advises further investigation to corroborate its findings, noting that some entities identified as threats could later prove harmless.
Article Details
- Attack Vectors
- Look-alike domains impersonating trusted software brands were used as infrastructure in a multistage AtlasCross RAT campaign.
- The domains mimicked brands including Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.
- Defensive Notes
- The report recommends supplementary investigation to corroborate entities identified as threats and provides IoCs for threat detection and response.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | app-zoom[.]com | Campaign domain IoC impersonating Zoom. |
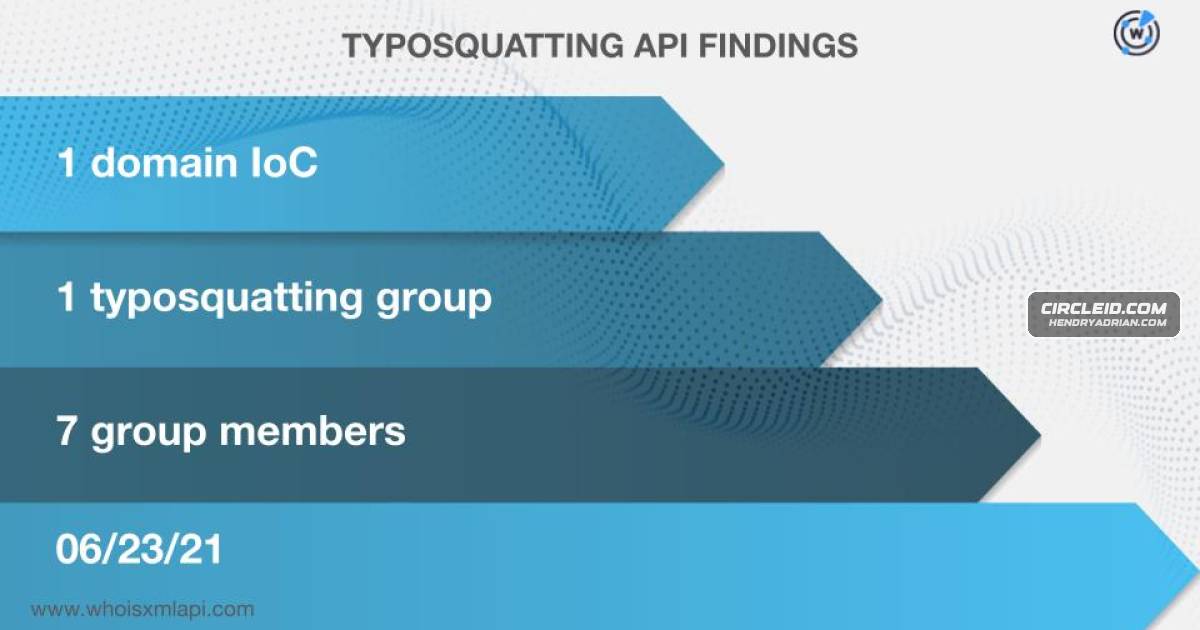
| DOMAIN | bifa0588[.]com | Look-alike domain in the typosquatting group associated with the campaign's bifa668[.]com IoC. |
| DOMAIN | bifa0888[.]com | Look-alike domain in the typosquatting group associated with the campaign's bifa668[.]com IoC. |
| DOMAIN | bifa1688[.]com | Look-alike domain in the typosquatting group associated with the campaign's bifa668[.]com IoC. |
| DOMAIN | bifa668[.]com | Campaign domain IoC in a typosquatting group of look-alike domains. |
| DOMAIN | bifa6868[.]com | Look-alike domain in the typosquatting group associated with the campaign's bifa668[.]com IoC. |
| DOMAIN | bifa688[.]com | Look-alike domain in the typosquatting group associated with the campaign's bifa668[.]com IoC. |
| DOMAIN | kefubao-pc[.]com | Domain identified as one of the campaign's domain IoCs. |
| DOMAIN | quickq-quickq[.]com | Campaign domain IoC reported as likely registered with malicious intent. |
| DOMAIN | ultraviewer-cn[.]com | Domain identified as one of the campaign's domain IoCs. |
| DOMAIN | wwtalk-app[.]com | Campaign domain IoC reported as likely registered with malicious intent. |
| DOMAIN | www-teams[.]com | Campaign domain IoC impersonating Microsoft Teams and reported as likely registered with malicious intent. |
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationDomains mimicked trusted software brands, including Zoom and Microsoft Teams, and the report describes typosquatting.T1583.001 · DomainsThe campaign used look-alike domains as infrastructure, including domains reported as registered with malicious intent.
Threat Actors
Malware
Products
Microsoft TeamsHexastrike Cybersecurity analyzed a multistage AtlasCross RAT campaign that used look-alike domains impersonating trusted software brands such as Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.SignalHexastrike Cybersecurity analyzed a multistage AtlasCross RAT campaign that used look-alike domains impersonating trusted software brands such as Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.Surfshark VPNHexastrike Cybersecurity analyzed a multistage AtlasCross RAT campaign that used look-alike domains impersonating trusted software brands such as Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.TelegramHexastrike Cybersecurity analyzed a multistage AtlasCross RAT campaign that used look-alike domains impersonating trusted software brands such as Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.ZoomHexastrike Cybersecurity analyzed a multistage AtlasCross RAT campaign that used look-alike domains impersonating trusted software brands such as Surfshark VPN, Signal, Telegram, Zoom, and Microsoft Teams.