
DNS Analysis Maps Infrastructure Linked to Axios Supply-Chain Attack
Summary
An analysis of the March 31, 2026 Axios npm supply-chain attack combined 22 IoCs from GTIG, Elastic Security Labs and GitHub, using DNS, WHOIS and related data to map suspected phishing infrastructure and connected artifacts.
Key points
- The analysis consolidated IoCs published by GTIG, Elastic Security Labs and GitHub, producing 22 indicators: five subdomains, seven domains and 10 IP addresses.
- Researchers identified phishing or impersonation indicators in subdomains including cloud[.]dnx[.]capital, crypto[.]hondchain[.]com and deck[.]31ventures[.]info.
- The domains 31ventures[.]info and starbucls[.]xyz appeared in typosquatting groups; dnx[.]capital was assessed as likely registered with malicious intent 651 days before its identification as an IoC.
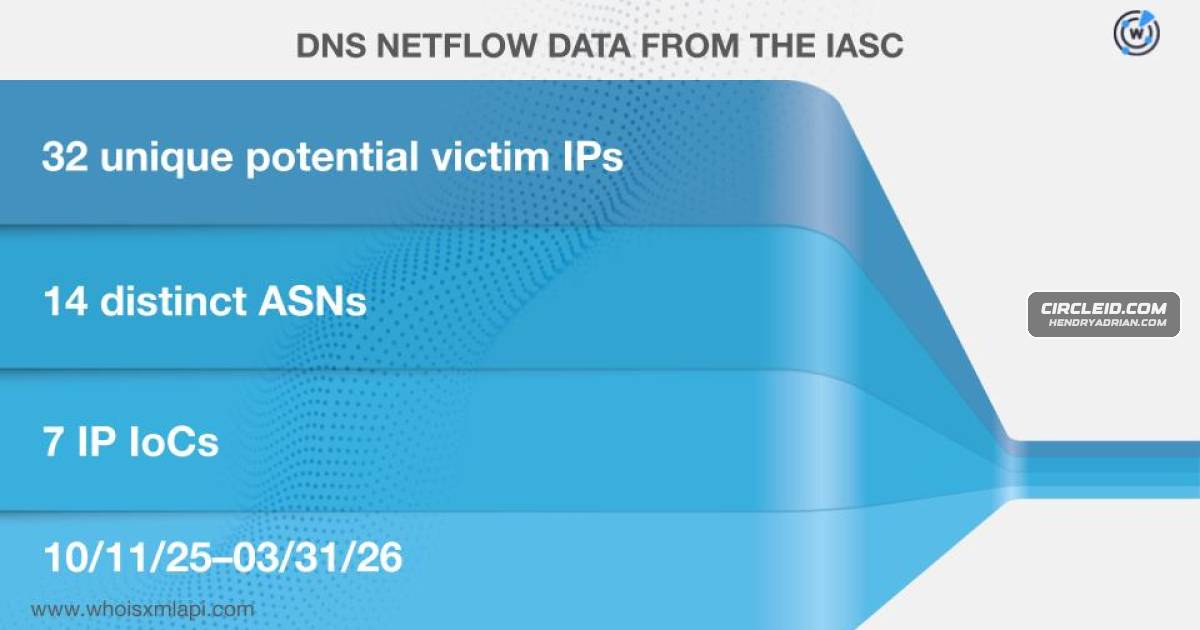
- Network data showed 16 client IPs communicating with two domain IoCs in 3,025 DNS queries, and 32 potentially victim-associated IPs communicating with seven IP IoCs.
- Further searches found 676 domains connected to a public historical WHOIS email address and two additional IP addresses that the article describes as malicious.
- The authors caution that some entities identified as malicious could later prove harmless and recommend further investigation.
Article Details
- Attack Vectors
- The reported attack targeted the npm package axios; the article does not describe the package compromise or payload-delivery mechanics.
- The infrastructure included phishing-like subdomains and typosquatting domains that mimicked legitimate brands or organizations.
- Defensive Notes
- The article advises against clicking links containing the five identified subdomains because they could be associated with scams.
- The article recommends conducting supplementary investigations to corroborate threat identifications.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 31ventures[.]info | Identified as a typosquatting IOC; its subdomain deck[.]31ventures[.]info was reported as likely impersonating 31VENTURES. |
| DOMAIN | dnx[.]capital | Identified as an attack IOC and reported as likely registered with malicious intent. |
| DOMAIN | starbucls[.]xyz | Identified as a typosquatting IOC in a group of domains using the starbucls name. |
| HOSTNAME | cloud[.]dnx[.]capital | Identified as a suspicious subdomain IOC; the article reports it lacks DNS records, WHOIS data, or a web presence. |
| HOSTNAME | crypto[.]hondchain[.]com | Identified as a subdomain IOC with reported hallmarks of a fraudulent or inactive phishing or scam site. |
| HOSTNAME | deck[.]31ventures[.]info | Identified as a likely impersonation of the legitimate 31VENTURES firm and as a possible phishing or investment-fraud setup. |
| HOSTNAME | docsend[.]linkpc[.]net | Identified as a phishing-like fake DocSend subdomain on a free, anonymous dynamic DNS service. |
| HOSTNAME | webhostwatto[.]work[.]gd | Identified as an inactive subdomain using a fabricated name on a free, anonymous subdomain service. |
| IPV4 | 104[.]168[.]167[.]88 | The article identifies this IP as maliciously associated with the attack infrastructure. |
| IPV4 | 23[.]254[.]128[.]114 | The article identifies this IP as maliciously associated with the attack infrastructure. |