
Technical Analysis Details Payload Ransomware’s Encryption and Anti-Forensics
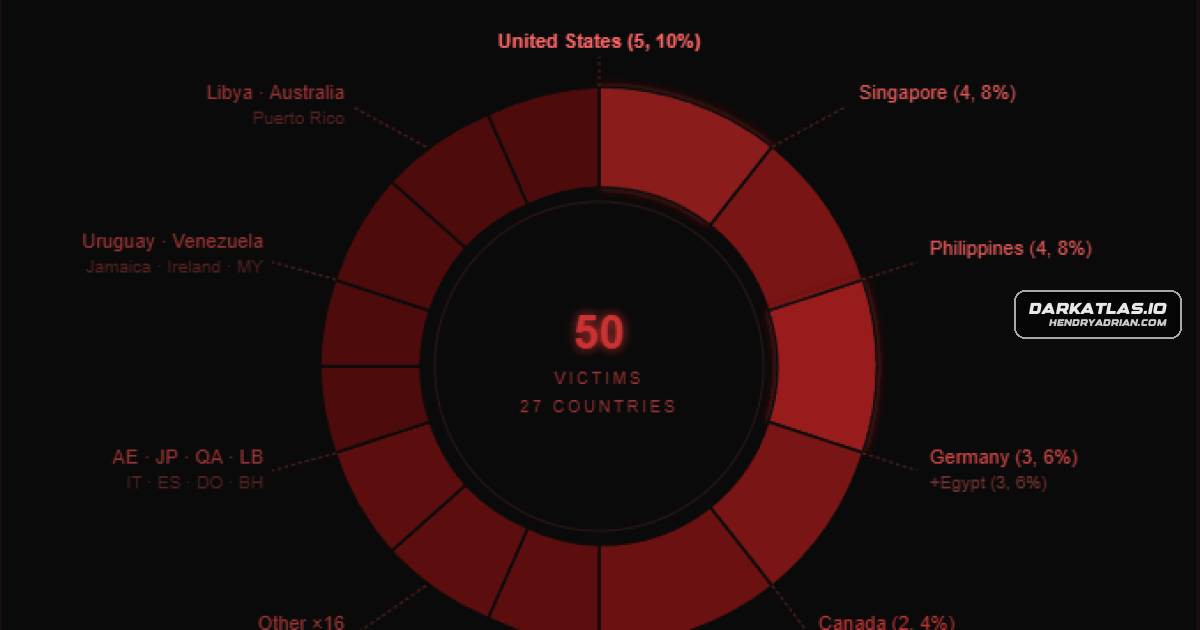
A technical analysis says Payload ransomware uses per-file Curve25519 ECDH-derived ChaCha20 encryption, an RC4-protected file footer, and ETW, VSS and event-log tampering. It reports 50 organizations listed on the group’s leak site by March 24, 2026.