
Fake Software Installers Deliver DinDoor Backdoor and Deno-Based RAT
Summary
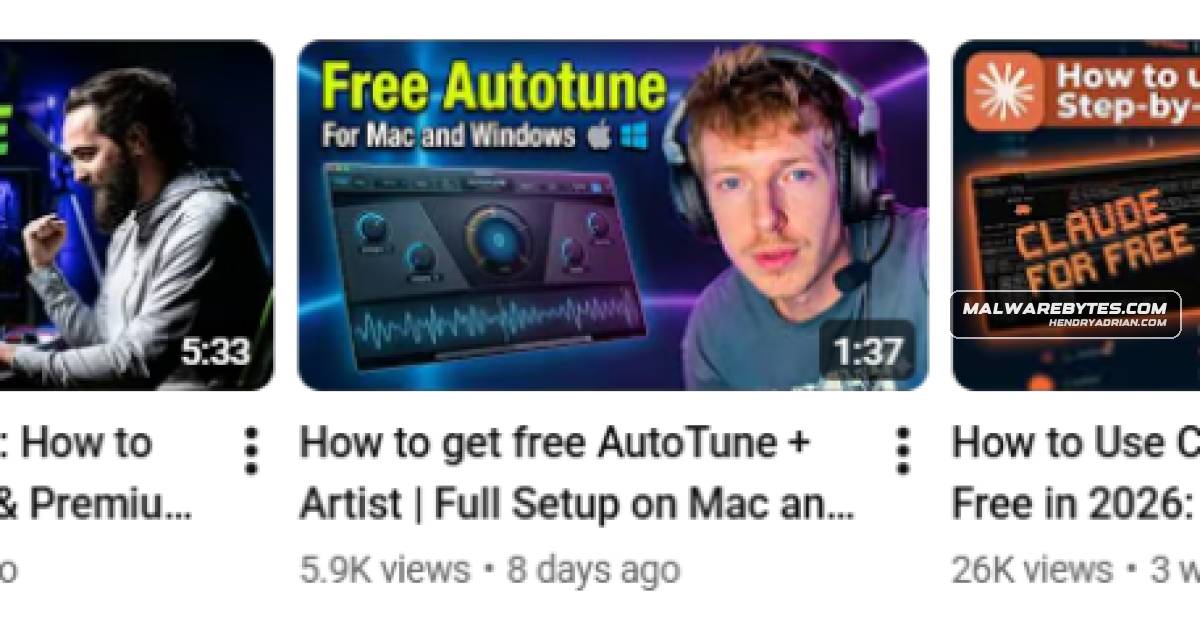
Malwarebytes describes fake software promoted through GitHub, SourceForge, and compromised YouTube channels. The campaign installs DinDoor and an unnamed Deno-based RAT that steals data and uses Edge for peer-to-peer streaming.
Key points
- Fake installers and plugins impersonating popular software are distributed through GitHub and SourceForge, with compromised YouTube channels promoting malicious links.
- In analyzed cases, MSI files or PowerShell scripts start an infection chain that installs Deno using Scoop or WinGet.
- DinDoor establishes persistence, communicates with command-and-control servers, and can execute additional payloads.
- The delivered, unnamed Deno-based RAT can collect browser, wallet, messaging, clipboard, screenshot, and file data, as well as execute commands and additional payloads.
- The RAT supports VNC and SOCKS5 over WebSocket; its peer-to-peer streaming mode uses Microsoft Edge, Chrome DevTools Protocol, and WebRTC to relay screen video to an operator.
- Malwarebytes says it contacted GitHub, which removed the malicious repositories, but warns that attackers may create new ones.
Article Details
- Attack Vectors
- Compromised YouTube channels promote links to GitHub and SourceForge repositories hosting fake software installers and plugins.
- Malicious repositories prompt users to run commands that download and install MSI files; some also use PowerShell scripts to start the infection chain.
- The MSI dropper places CMD and PowerShell files, which install Deno through Scoop or WinGet and use Deno to execute further JavaScript stages.
- DinDoor communicates with C2 infrastructure, establishes persistence through a Run key, and can execute commands and deliver additional payloads.
- The Deno-based RAT collects data from browsers, wallets, messaging applications, the clipboard, and files; it also supports screenshots, VNC, and SOCKS5 over WebSocket.
- The RAT uses Microsoft Edge and WebRTC for peer-to-peer screen streaming, with signaling exchanged through the C2 WebSocket.
- Defensive Notes
- Download software only from official vendor websites and be skeptical of free, cracked, or unofficial software.
- Use caution with downloads from GitHub, SourceForge, forums, and file-sharing sites, especially from new or unknown accounts; check the publisher profile and reputation.
- Check archive contents against what was expected and inspect file publishers and digital signatures before running files; a valid signature does not guarantee safety.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | agilemast3r[.]duckdns[.]org | C2 domain listed for the campaign. |
| DOMAIN | ashpaltlonpro[.]com | C2 domain listed for the campaign. |
| DOMAIN | cf-proxy[.]cloud-analytics-services[.]workers[.]dev | Cloudflare Workers hostname listed as C2 infrastructure for the RAT's light version. |
| DOMAIN | claudescript[.]top | Distribution website for the campaign's malicious software. |
| DOMAIN | dakatawebstick[.]com | C2 domain listed for the campaign. |
| DOMAIN | geralnewlong[.]com | C2 domain listed for the campaign. |
| DOMAIN | hngfbgfbfb[.]cyou | C2 domain listed for the campaign. |
| DOMAIN | logicalnewrestore[.]com | C2 domain listed for the campaign. |
| DOMAIN | ms-telemetry-gateway-us[.]com | C2 domain listed for the campaign. |
| IPV4 | 193[.]233[.]198[.]132 | C2 server listed for the campaign. |
| IPV4 | 23[.]227[.]196[.]107 | C2 server listed for the campaign. |
| IPV4 | 31[.]57[.]129[.]23 | C2 server listed for the campaign. |
| IPV4 | 45[.]137[.]99[.]121 | C2 server listed for the campaign. |
| IPV4 | 66[.]78[.]40[.]107 | C2 server listed for the campaign. |
| URL | hxxps[:]//github[.]com/ai-gen-profi | GitHub repository listed among malicious distribution repositories. |
| URL | hxxps[:]//github[.]com/claude-free-plugin/ | GitHub repository identified as distributing fake software and malicious installers. |
| URL | hxxps[:]//github[.]com/wharfdemolisherpit | GitHub repository listed among malicious distribution repositories. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/claude-free-plugin/install/main/install.msi | Specific GitHub-hosted MSI URL used by the malicious command to download the installer. |
| URL | hxxps[:]//sourceforge[.]net/projects/bluewaveremover/ | SourceForge project listed among malicious software-distribution pages. |
| URL | hxxps[:]//sourceforge[.]net/projects/gearup/ | SourceForge project identified as distributing fake GearUP software and the backdoor. |
MITRE ATT&CK
T1005 · Data from Local SystemThe RAT collects data from local files, browsers, wallets, and messaging applications.T1021.005 · VNCThe RAT supports bidirectional control through a custom VNC implementation over WebSocket.T1027 · Obfuscated Files or InformationThe RAT's configuration data is Base64-encoded.T1041 · Exfiltration Over C2 ChannelThe RAT sends exfiltrated data through its C2 communications.T1059.001 · PowerShellPowerShell scripts install software, launch payloads, and create the persistence entry.T1059.003 · Windows Command ShellA dropped CMD file launches the PowerShell script in the infection chain.T1059.007 · JavaScriptDeno executes the JavaScript stages for DinDoor and the RAT.T1071.001 · Web ProtocolsDinDoor and the RAT use HTTP and WebSocket for C2 communications.T1090.001 · Internal ProxyThe RAT can establish SOCKS5 proxy tunnels over WebSocket.T1105 · Ingress Tool TransferThe infection chain downloads MSI installers and follow-on JavaScript stages from repositories and C2 endpoints.T1113 · Screen CaptureThe RAT captures screenshots and streams the victim's screen to the operator.T1115 · Clipboard DataThe RAT records and modifies clipboard data.T1204.002 · Malicious FileUsers are prompted to download and run fake installers or copy and execute malicious commands from the repositories.T1218.007 · MsiexecThe malicious MSI is installed using msiexec.T1547.001 · Registry Run Keys / Startup FolderDinDoor creates a Run key that launches the downloader again for persistence.
Malware
Products
AutoTuneAttackers are abusing GitHub, SourceForge, and compromised YouTube channels to distribute fake installers and plugins impersonating popular software such as ChatGPT, Claude, AutoTune, and Kontakt.ChatGPTAttackers are abusing GitHub, SourceForge, and compromised YouTube channels to distribute fake installers and plugins impersonating popular software such as ChatGPT, Claude, AutoTune, and Kontakt.ClaudeAttackers are abusing GitHub, SourceForge, and compromised YouTube channels to distribute fake installers and plugins impersonating popular software such as ChatGPT, Claude, AutoTune, and Kontakt.DenoThe campaign delivers DinDoor and a Deno-based RAT that uses alternative JavaScript runtimes, Scoop, and WinGet to install payloads, steal data, and hide traffic through Microsoft Edge.GitHubAttackers are abusing GitHub, SourceForge, and compromised YouTube channels to distribute fake installers and plugins impersonating popular software such as ChatGPT, Claude, AutoTune, and Kontakt.KontaktAttackers are abusing GitHub, SourceForge, and compromised YouTube channels to distribute fake installers and plugins impersonating popular software such as ChatGPT, Claude, AutoTune, and Kontakt.Microsoft EdgeThe campaign delivers DinDoor and a Deno-based RAT that uses alternative JavaScript runtimes, Scoop, and WinGet to install payloads, steal data, and hide traffic through Microsoft Edge.ScoopThe campaign delivers DinDoor and a Deno-based RAT that uses alternative JavaScript runtimes, Scoop, and WinGet to install payloads, steal data, and hide traffic through Microsoft Edge.SourceForgeAttackers are abusing GitHub, SourceForge, and compromised YouTube channels to distribute fake installers and plugins impersonating popular software such as ChatGPT, Claude, AutoTune, and Kontakt.wingetThe campaign delivers DinDoor and a Deno-based RAT that uses alternative JavaScript runtimes, Scoop, and WinGet to install payloads, steal data, and hide traffic through Microsoft Edge.