cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2396 articles

Threat Research · huntress.com

Windows Search URI Handler Can Leak NTLM Hashes From a Single Click

A Huntress researcher found that a Windows search: URI can trigger an NTLMv2 hash leak with one click. Microsoft rated the issue Moderate but closed it without a CVE or fix; mitigations include blocking outbound SMB and restricting NTLM.

Jun 2, 2026
Threat Research · reversinglabs.com

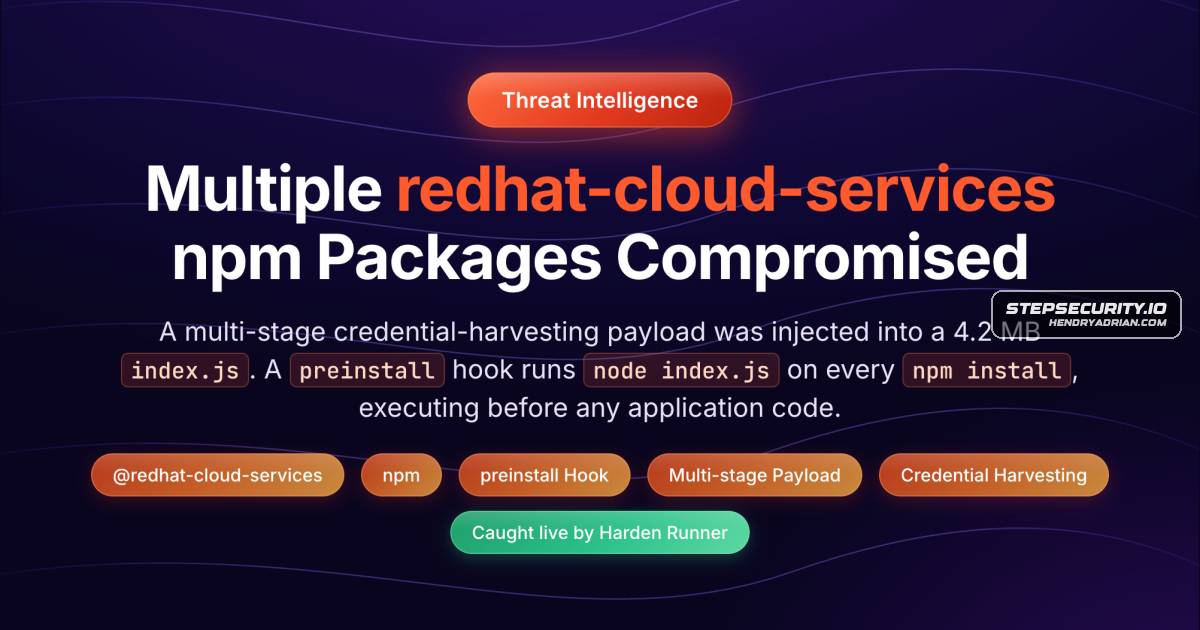
ReversingLabs Finds 32 Backdoored Red Hat npm Packages Published in 72 Seconds

ReversingLabs says 32 malicious @redhat-cloud-services npm versions were published in 72 seconds on June 1, 2026. Its analysis found an obfuscated preinstall credential stealer; clean versions were published and the malicious versions removed.

Jun 1, 2026
Threat Research · dti.domaintools.com

DomainTools Details 1,100+ Suspected Domains Used for Data Collection and Malware Delivery

DomainTools reports that a suspected campaign used more than 1,100 spoofed domains to collect user data and selectively deliver malware, including ValleyRAT and Gh0stRAT, primarily to Chinese-speaking users.

Jun 1, 2026
Threat Research · bleepingcomputer.com

WordPress Malware Hides C2 Data in Steam Profile Comments

GoDaddy researchers found the campaign’s malware on about 1,980 WordPress sites. It hides C2 data in invisible Unicode characters in Steam comments to retrieve JavaScript and install a backdoor; the initial infection vector is unclear.

Jun 1, 2026
Threat Research · malwarebytes.com

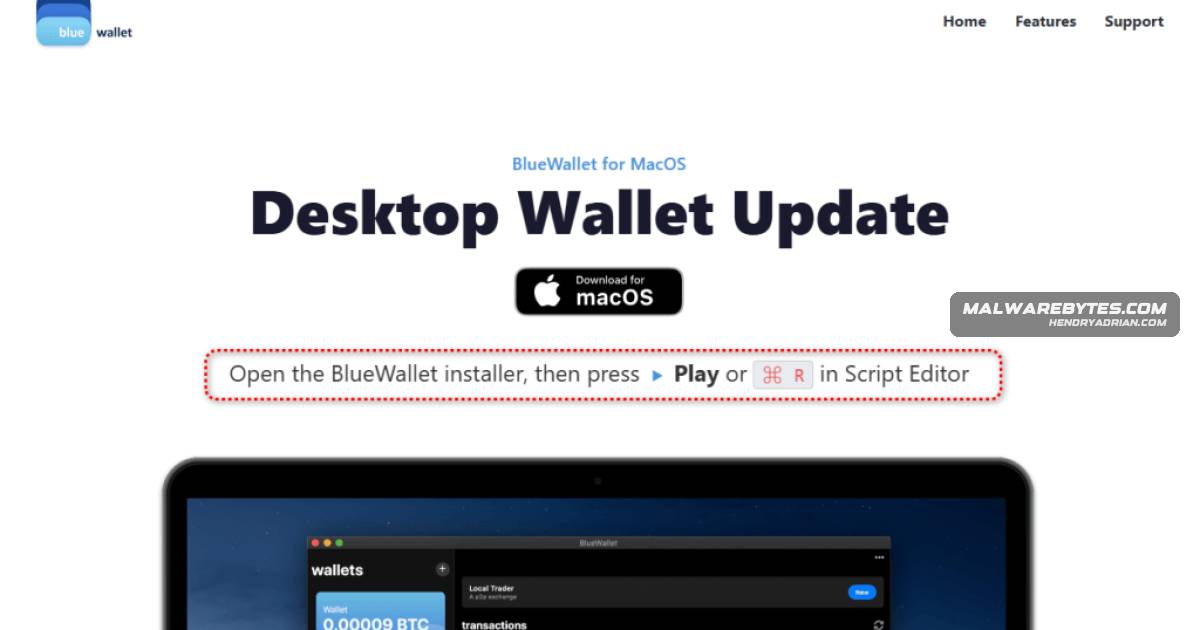
Fake BlueWallet Site Uses AppleScript to Steal Data From Macs

A fake BlueWallet site tricks Mac users into running an AppleScript that installs a data-stealing implant. It targets browser, wallet and other credentials, can replace copied crypto addresses, persists via LaunchAgent, and uses Telegram for command-and-control and exфl

Jun 1, 2026
Threat Research · seqrite.com

Seqrite Details SideCopy-Linked XenoRAT Campaign Targeting Afghanistan’s Finance Ministry

Seqrite Labs details Operation XENOFISCAL, a SideCopy-linked spear-phishing campaign targeting Afghanistan’s Ministry of Finance. A Pashto-named LNK launches a multi-stage loader that deploys XenoRAT; attribution is assessed with medium-to-high confidence.

Jun 1, 2026
Threat Research · socket.dev

Malicious npm Packages Targeting Red Hat Cloud Services Steal Credentials

Socket reports compromised @redhat-cloud-services npm packages that run an obfuscated payload during installation, harvest credentials and CI secrets, and exfiltrate data. The article details the malware’s behavior and recommends exposure review, containment, and secret

Jun 1, 2026
Threat Research · wiz.io

Miasma Supply-Chain Attack Compromises Red Hat npm Packages

Wiz found 32 compromised Red Hat npm package releases. A hijacked employee account used GitHub Actions and OIDC to publish malware that steals developer secrets and collects GCP and Azure identities; most malicious versions were revoked.

Jun 1, 2026
Threat Research · blog.sekoia.io

Sekoia Details Gamaredon’s GammaPhish and GammaWorm Infection Chain

Sekoia reconstructed a January 2026 Gamaredon chain using a CVE-2025-8088 WinRAR archive to deploy GammaPhish and GammaWorm, which persists in NTFS alternate data streams, spreads via USB and network drives, and operates as a backdoor.

Jun 1, 2026
Threat Research · stepsecurity.io

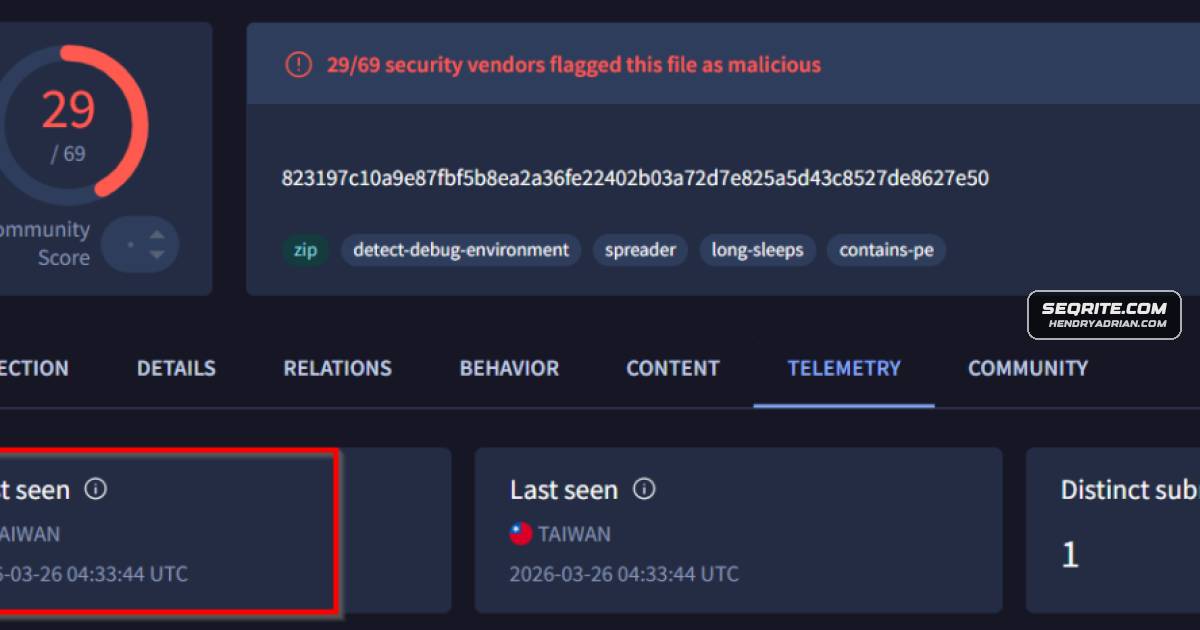
StepSecurity Details Malware in Red Hat Cloud Services npm Packages

StepSecurity reports malicious npm releases that execute at install time, harvest credentials, and can republish backdoored packages. Its analysis describes the malware’s techniques, affected versions, and remediation advice.

Jun 1, 2026
Threat Research · socket.dev

Famous Chollima-Linked Campaign Targets PHP Developers Through Malicious Packagist Branch

Socket researchers found an obfuscated JavaScript loader in an installable development branch of a PHP package. It retrieves encrypted payloads through blockchain infrastructure; Packagist removed the version after notification.

May 31, 2026
Threat Research · rapid7.com

Rapid7 Details Active Exploitation of PAN-OS GlobalProtect Authentication Bypass

Rapid7 observed exploitation of CVE-2026-0257 across multiple customers, using forged GlobalProtect authentication-override cookies to bypass login on specially configured PAN-OS and Prisma Access systems. No successful lateral movement was observed.

May 31, 2026
Threat Research · seqrite.com

Seqrite Analyzes Operation Dragon Weave’s Azure-Based C2 Campaign

Seqrite details a spearphishing campaign targeting the Czech Republic and Taiwan that delivers AZUREVEIL, an Adaptix C2 agent using Azure Blob Storage. The researchers assess a China-based link with moderate confidence.

May 30, 2026
Threat Research · thehackernews.com

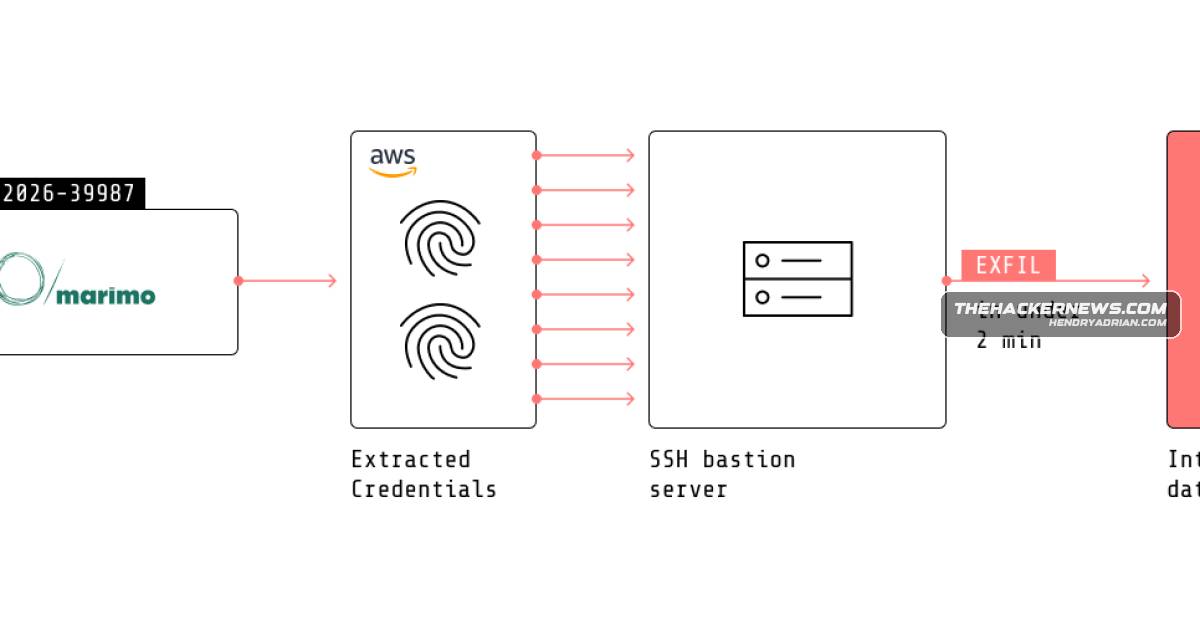
Sysdig Reports LLM-Agent-Driven Post-Exploitation After Marimo CVE Exploit

Sysdig reported that an unknown actor exploited Marimo CVE-2026-39987, used AWS credentials and an SSH key to reach a bastion, and exfiltrated an internal PostgreSQL database. It cited command patterns and other evidence of LLM-agent use.

May 30, 2026
Threat Research · silentpush.com

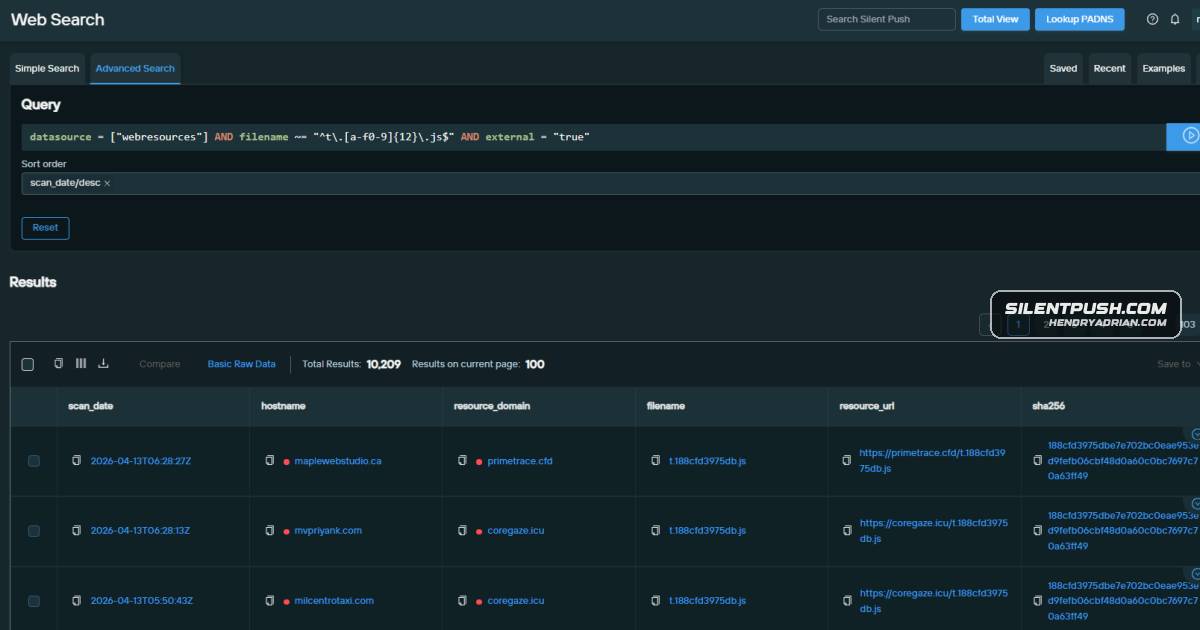
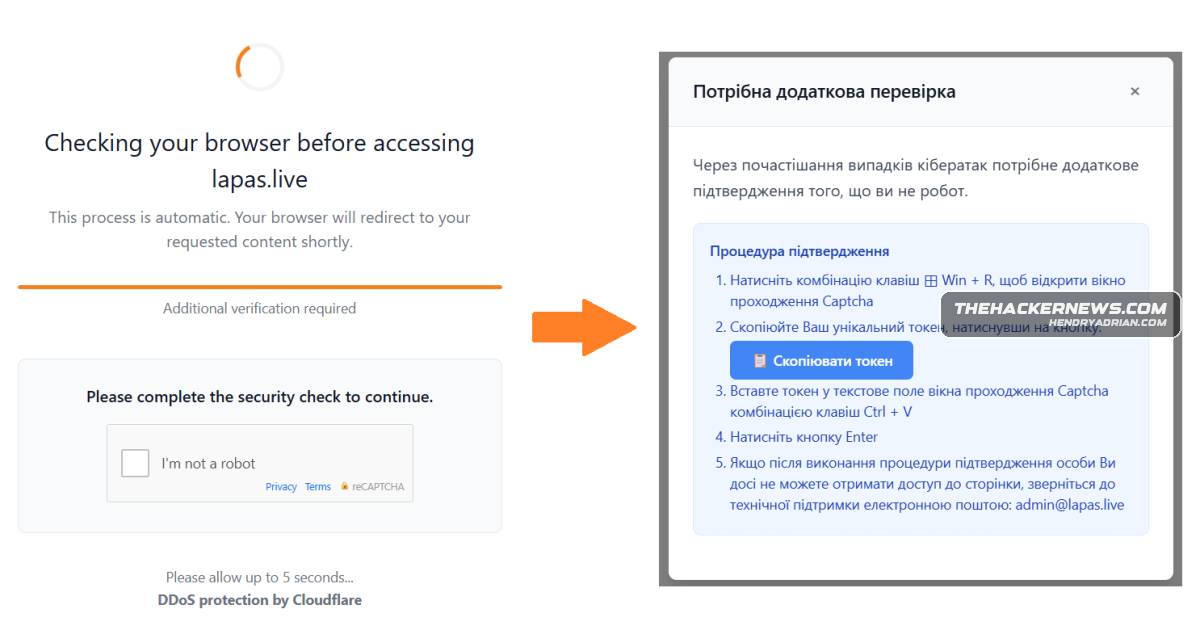
DriveSurge Uses ClickFix and Fake Updates to Deliver Malware Through Compromised Sites

Silent Push researchers identify DriveSurge, a suspected initial-access broker using zTDS to redirect visitors from thousands of compromised sites to ClickFix and fake-update lures. The analysis details infrastructure fingerprints and a macOS clipboard-hijacking payload

May 30, 2026
Threat Research · thehackernews.com

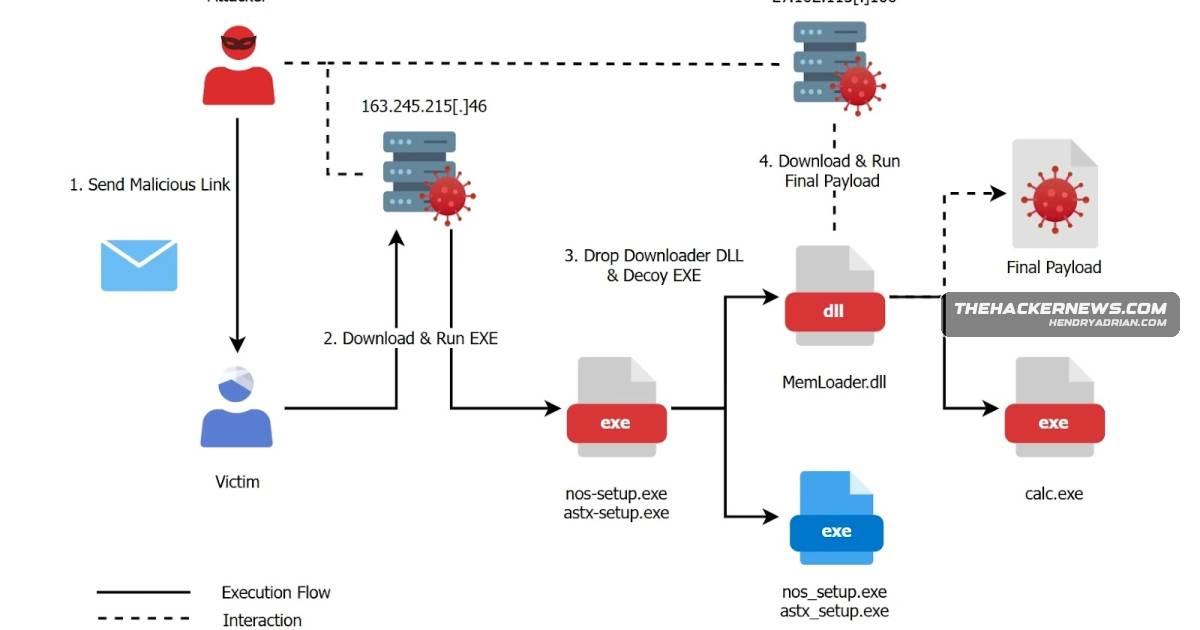
WithSecure Details GREYVIBE’s AI-Assisted Campaigns Targeting Ukraine

WithSecure links GREYVIBE to attacks targeting Ukraine since at least August 2025, detailing phishing and fake-site delivery chains, custom malware, and evidence of AI assistance. The group’s relationship with the Russian state remains unclear.

May 29, 2026
Threat Research · thehackernews.com

Kimsuky Uses Fake Security and Webex Lures to Deploy HTTPSpy

ENKI described Kimsuky campaigns targeting South Korean organizations with fake security-software and Webex lures that delivered HTTPSpy and other payloads. Kaspersky also reported expanded use of malware, remote-access tools and VS Code tunneling.

May 29, 2026
Threat Research · circleid.com

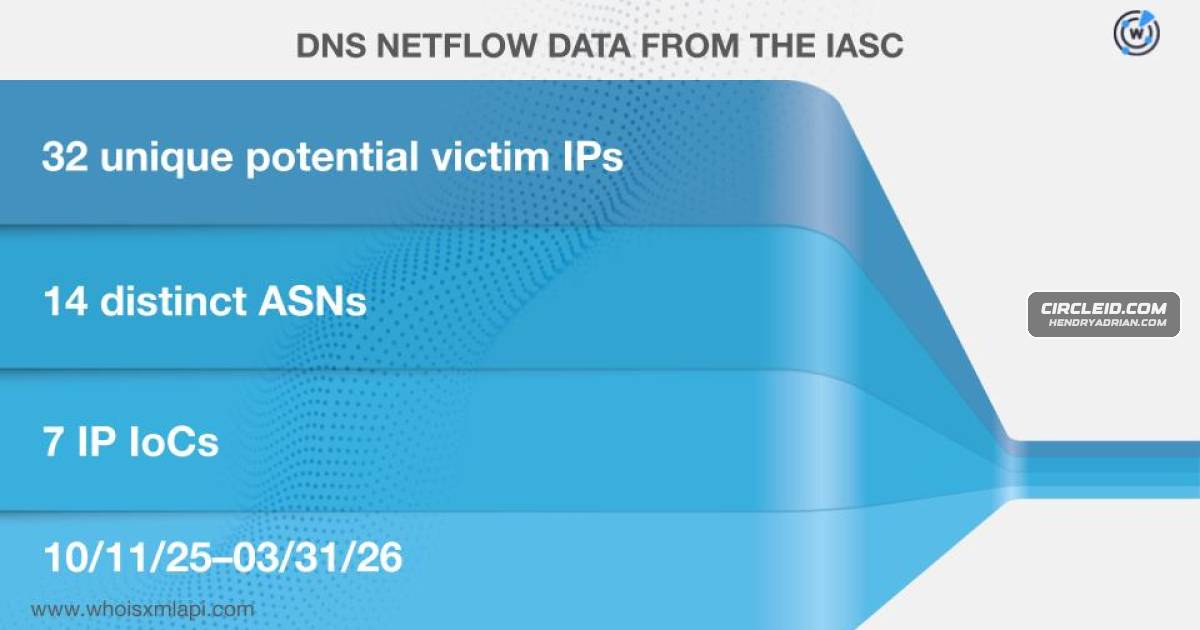
DNS Analysis Maps Infrastructure Linked to Axios Supply-Chain Attack

An analysis of the March 31, 2026 Axios npm supply-chain attack combined 22 IoCs from GTIG, Elastic Security Labs and GitHub, using DNS, WHOIS and related data to map suspected phishing infrastructure and connected artifacts.

May 29, 2026
Threat Research · cyberscoop.com

Researchers Say Chained Zapier Flaws Could Enable Account Takeover

Token Security researchers chained five Zapier flaws, using a free account to reach credentials, private software images and browser code, potentially enabling actions across users’ connected services. Zapier patched the flaws and reports no evidence of exploitation.

May 28, 2026
Threat Research · socket.dev

Malicious Sicoob NuGet SDK Exfiltrated Banking Credentials and Certificates

Socket analyzed Sicoob.Sdk versions 2.0.0–2.0.4, which sent client IDs, PFX passwords, and encoded certificates to a hardcoded Sentry endpoint. NuGet blocked the package after a report.

May 28, 2026
Threat Research · sysdig.com

Sysdig Traces LLM-Driven Intrusion from marimo CVE to PostgreSQL Exfiltration

Sysdig TRT reports an intrusion that began with CVE-2026-39987 in an internet-facing marimo notebook and reached an internal PostgreSQL database. It presents command-stream evidence for real-time LLM-agent execution and recommends patching and rotating exposed secrets.

May 28, 2026
Threat Research · levelblue.com

LevelBlue Details Sapphire Sleet macOS Campaign Using Fake Zoom SDK Update

LevelBlue describes a Sapphire Sleet campaign targeting macOS users in financial, Web3, and cryptocurrency sectors. A fake Zoom SDK update delivered AppleScript payloads that abused TCC permissions, established persistence, and collected credentials and sensitive data.

May 28, 2026
Threat Research · labs.k7computing.com

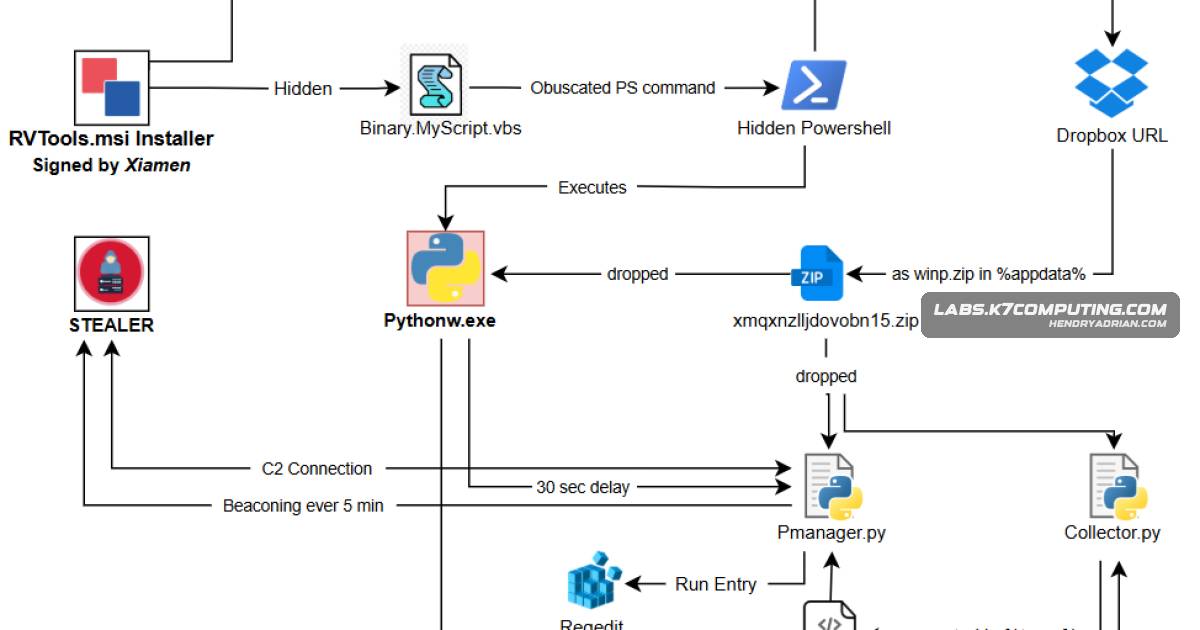
Fake RVTools Installer Deploys Modular Python RAT

A malicious MSI impersonating RVTools, signed with a subsequently revoked Sectigo certificate, uses embedded VBScript and hidden PowerShell to download a WinPython bundle and deploy a modular Python RAT with AD reconnaissance, persistence and encrypted C2.

May 28, 2026
Threat Research · securelist.com

Pirated Content Sites Distribute SilentCryptoMiner Fork and RAT

Researchers detail a campaign active since at least 2022 that uses fake player updates on pirated streaming and library sites to install a SilentCryptoMiner fork and RAT, with DNS-based system checks, persistence, defense evasion and rotating C2.

May 28, 2026
PreviousPage 57 of 100 Next
© 2026 cyber.hendryadrian.com