cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2391 articles

Threat Research · research.checkpoint.com

Researchers Demonstrate Browser-Only Ransomware Using Chrome’s File Access API

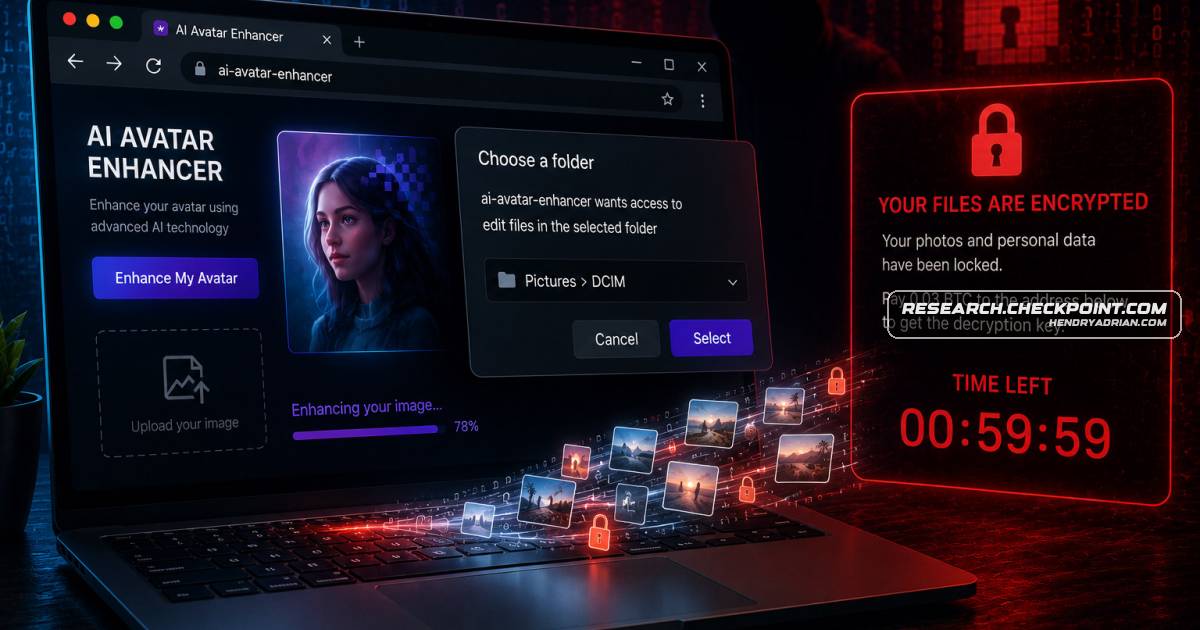
Check Point researchers found that an AI-generated malware sample pointed to a practical browser-only attack: a deceptive site can use Chrome’s File System Access API to access, exfiltrate, or encrypt files after a user grants folder access.
Jul 1, 2026
Threat Research · cyble.com

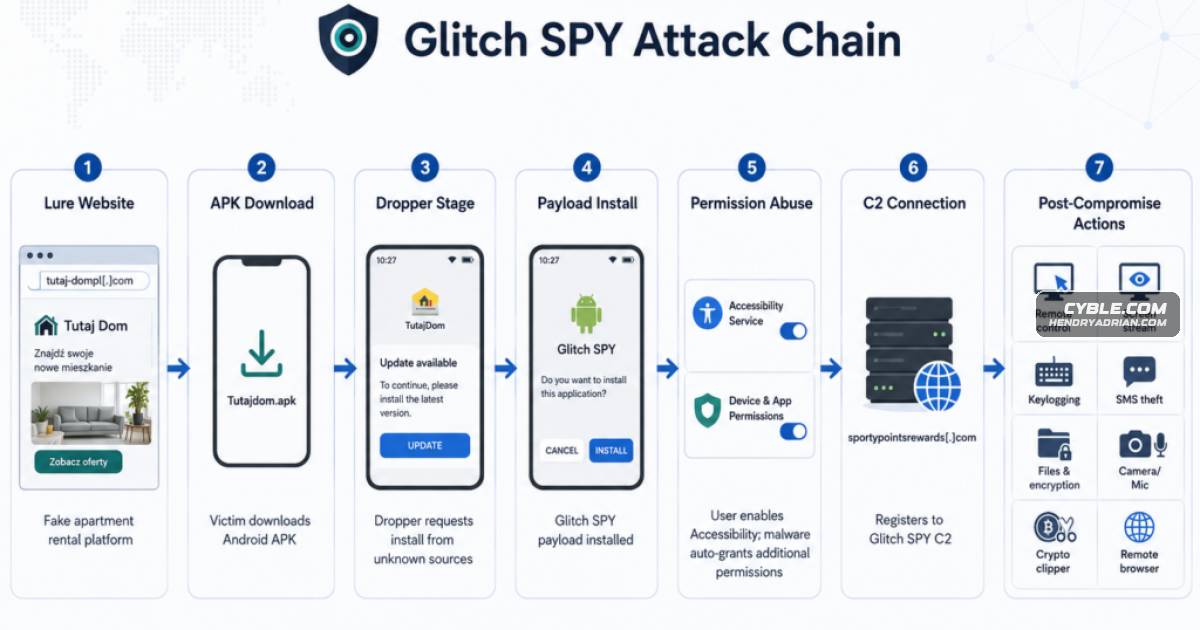
Glitch SPY Android RAT Uses Fake Polish Rental App for Delivery

Cyble analyzed Glitch SPY, an Android RAT delivered through a fake Polish rental app by the Brokewell Android Loader. It abuses Accessibility for control and data theft, and includes crypto-clipping and hidden browser capabilities; distribution appears early-stage.

Jul 1, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Phantom Squatting Attacks Using LLM-Hallucinated Domains

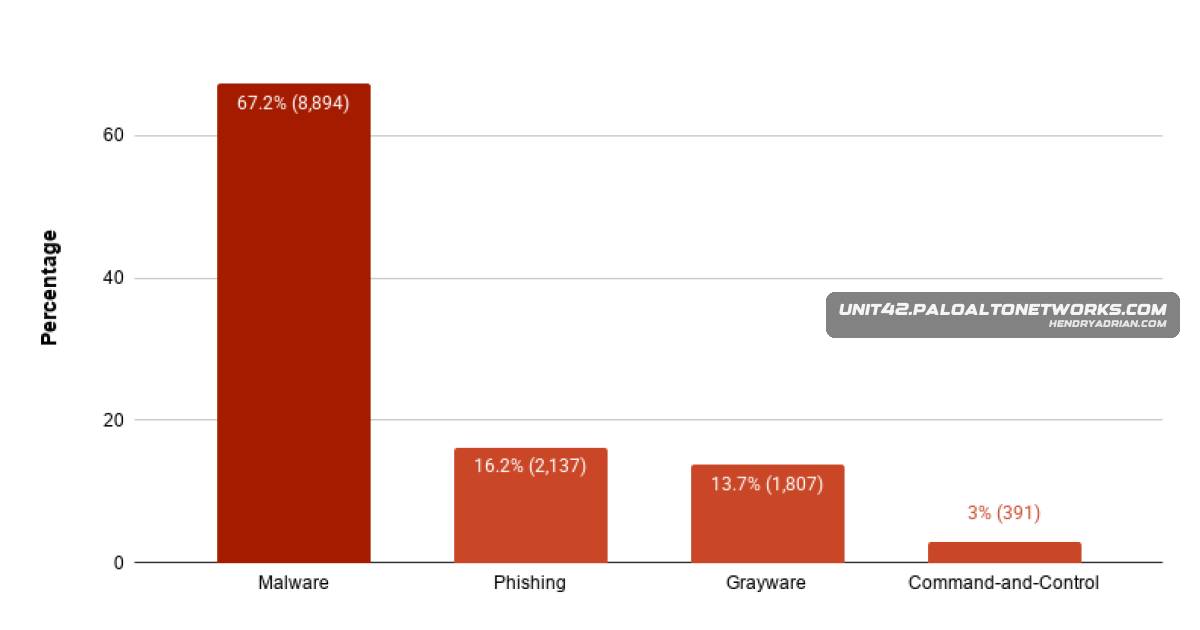
Unit 42 says attackers are registering LLM-hallucinated domains for phishing and malware delivery. Its research found 13,229 URLs flagged as malicious, about 250,000 unregistered phantom domains, and cases involving Montana Empire and a postal-service APK.

Jul 1, 2026
Threat Research · bleepingcomputer.com

Malicious PyPI Pyrogram Forks Add Backdoor to Telegram Bot Servers

Checkmarx reports that Operation Navy Ghost published at least eight trojanized Pyrogram forks on PyPI. Their secret.py backdoor can run Python or shell commands with an infected bot’s permissions and access files, secrets, and Telegram data.

Jul 1, 2026
Threat Research · recordedfuture.com

Iran-Linked TAG-182 Uses MarkiRAT to Spy on Farsi-Speaking Targets

Recorded Future links TAG-182 to MarkiRAT malware distributed through fake VPN and media apps, likely targeting Iranians at home and abroad. The report details infrastructure, malware behavior, possible overlap with Ferocious Kitten, and detection rules.

Jul 1, 2026
Threat Research · dmpdump.github.io

Backdoor Targets Linux-Based iKuai Routers

A technical analysis details an ELF backdoor that appears to target iKuai routers, beaconing to a command-and-control server and supporting shell commands, file exfiltration, and payload execution.

Jul 1, 2026
Threat Research · circleid.com

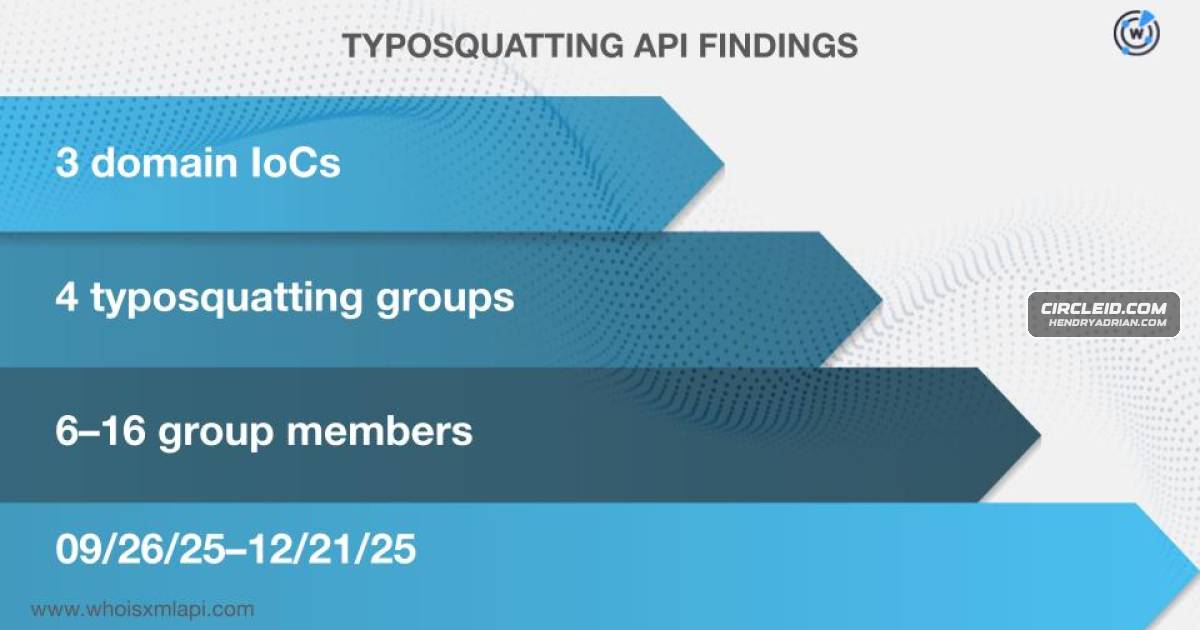
DNS Analysis Maps TA416-Linked Infrastructure and 15 Reported Malicious Domains

A WhoisXML API analysis of Proofpoint-reported TA416 activity examined 91 network indicators, identifying 122 client IPs, 45,197 email-connected domains and 15 domains reported weaponized for phishing or malware distribution.

Jun 30, 2026
Threat Research · thehackernews.com

Langflow CVE-2026-33017 Exploited to Deploy Monero Miner

Trend Micro observed a March 27–April 15, 2026 campaign exploiting Langflow CVE-2026-33017 for unauthenticated RCE and deploying a Monero miner via lambsys, which disables defenses, persists, removes logs and spreads over SSH.

Jun 30, 2026
Threat Research · thehackernews.com

RustDuck Botnet Uses Rust Core and Anti-Analysis Checks to Target Routers and Servers

QiAnXin’s XLab says RustDuck targets routers, cameras, Android boxes and exposed servers for DDoS, using a two-stage loader, a Rust core, sandbox checks and encrypted command traffic. It spreads through weak credentials and known flaws.

Jun 30, 2026
Threat Research · securelist.com

Kaspersky Details ToddyCat’s Umbrij Tool for Stealing Google OAuth Codes

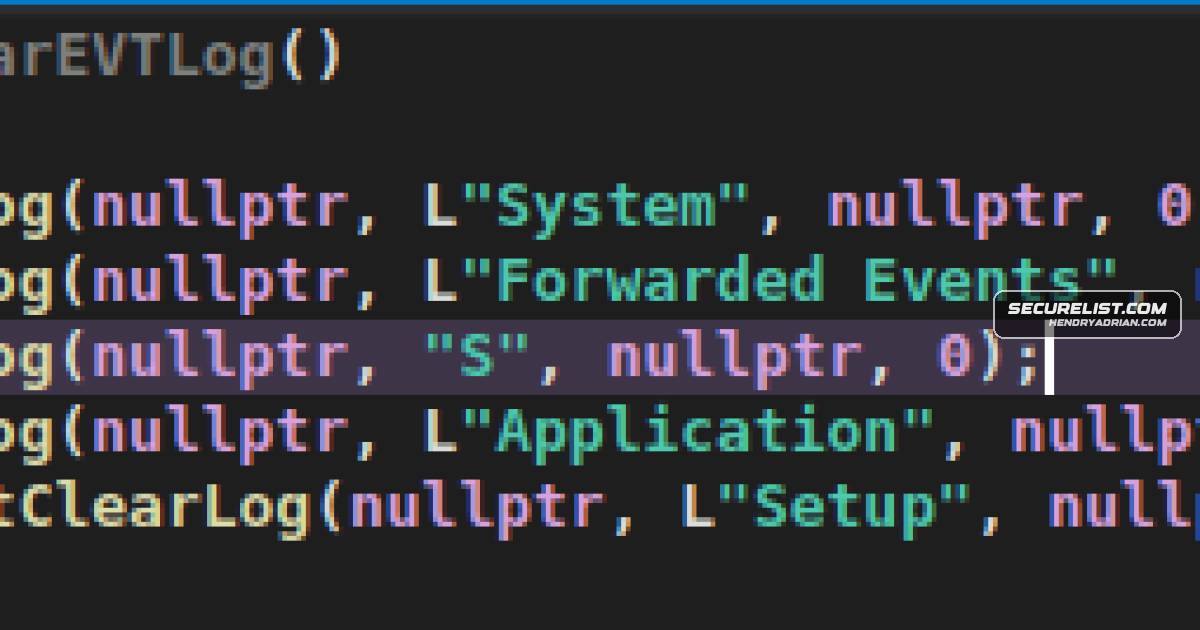
Kaspersky researchers detail ToddyCat’s Umbrij tool, which sideloads through legitimate Windows apps, reuses copied Chrome and Edge profiles, and uses remote debugging to obtain Google OAuth codes for corporate Gmail API access.

Jun 30, 2026
Threat Research · thehackernews.com

Mustang Panda Uses Zoho WorkDrive for C2 in Campaigns Targeting Indian Government

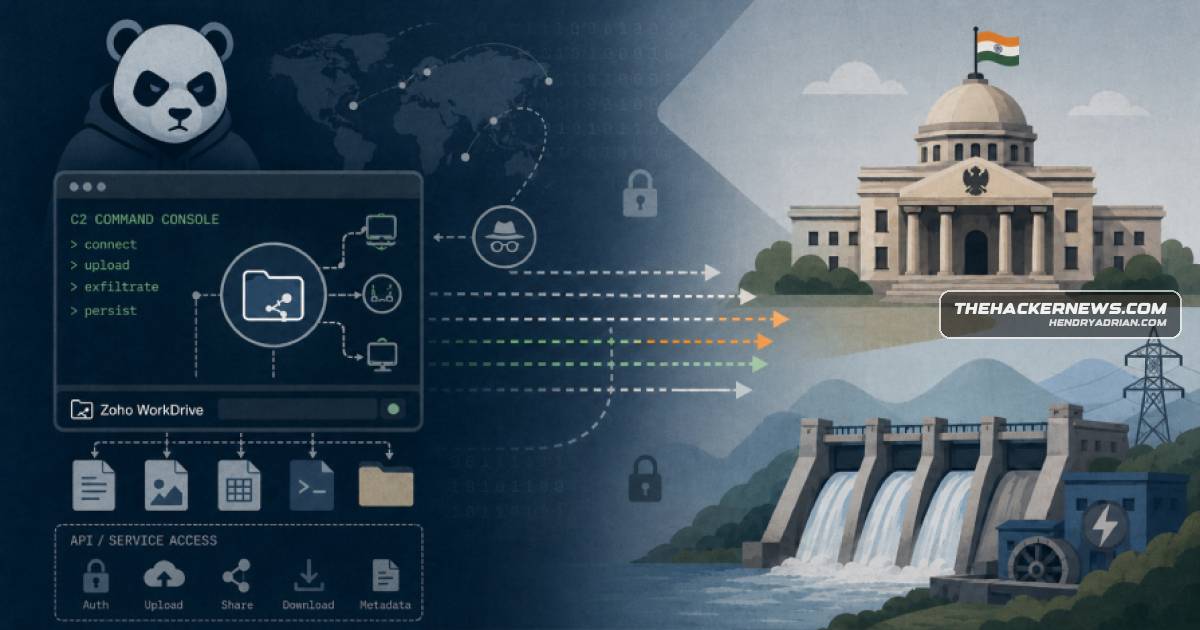
Acronis reports Mustang Panda campaigns targeting Indian government and hydropower organizations, detailing three tools that use signed-binary sideloading and Zoho WorkDrive for command delivery and data exfiltration.

Jun 30, 2026
Threat Research · kudelskisecurity.com

DPRK-Linked Contagious Interview Campaign Uses Fake Developer Interviews to Deliver a Backdoor

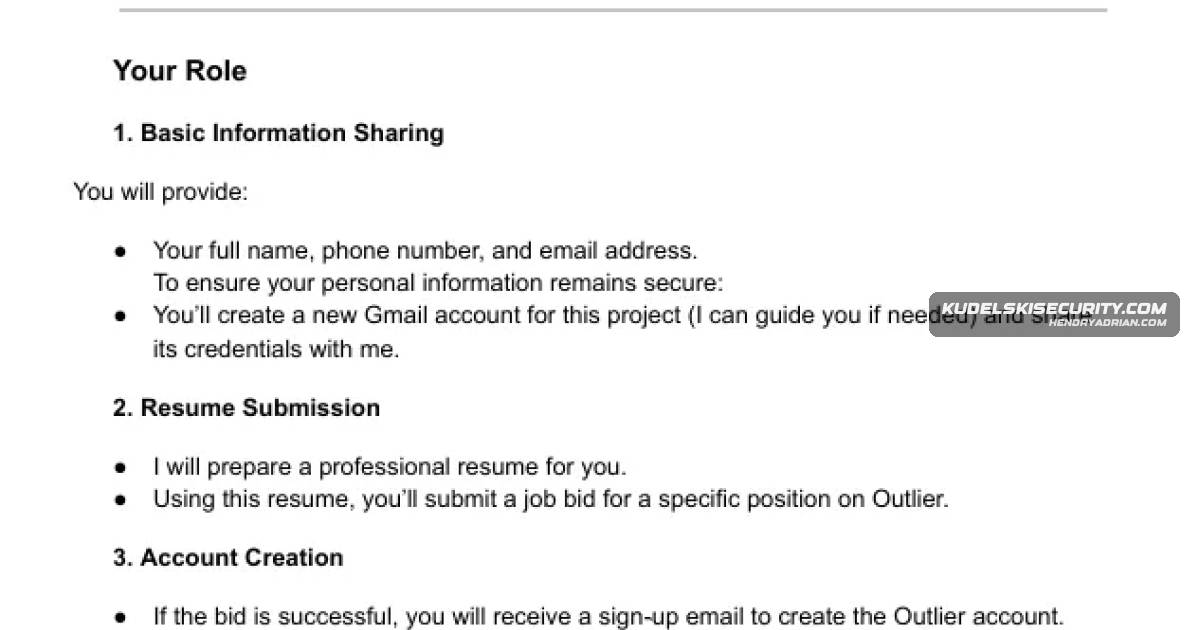
Kudelski researchers describe how DPRK-linked operators use fake developer interviews and a trojanized GitHub project to install a backdoor that collects system data, exposes environment secrets, and enables remote commands.

Jun 30, 2026
Threat Research · huntress.com

Password-Spraying Campaign Compromises 78 Microsoft Accounts by Exploiting Azure CLI ROPC MFA Gaps

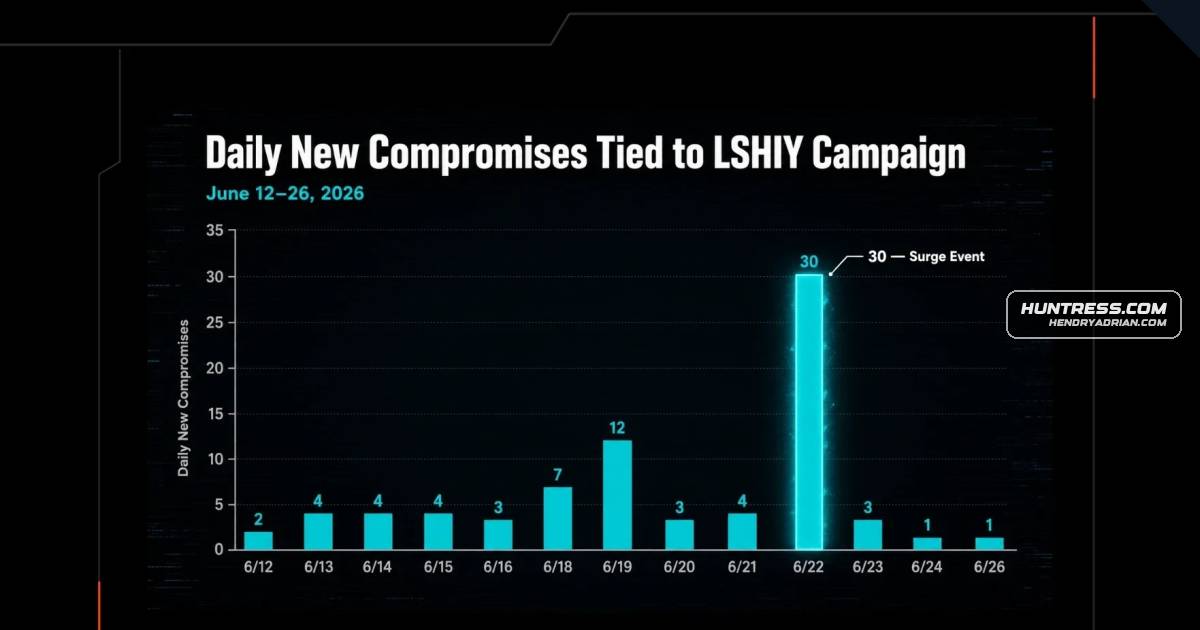
Huntress found a password-spraying campaign that compromised 78 Microsoft accounts across 64 organizations using Azure CLI’s OAuth ROPC flow. Attackers later shifted providers; Huntress recommends properly scoped MFA and restricting Azure CLI access.

Jun 30, 2026
Threat Research · socket.dev

Malicious Chrome and Firefox VPN Extensions Add Clipboard Stealers Through Updates

Socket researchers found Chrome and Firefox VPN Go extensions added clipboard-stealing code in later versions, sending copied data to hardcoded servers. The extensions were reported to Google and Mozilla for review.

Jun 29, 2026
Threat Research · securelist.com

Kaspersky Details The Gentlemen’s Custom Go Backdoor and New Ransomware Variant

Kaspersky details The Gentlemen’s ransomware operations, including exposed-service and credential-based access, reconnaissance, BYOVD defense evasion, a custom Go backdoor for command execution and SOCKS proxying, and Go and C-based ransomware variants.

Jun 29, 2026
Threat Research · securityweek.com

Researchers Detail Claude Code Attack Hidden in Normal-Looking Repositories

Mozilla 0Din researchers describe an attack in which Claude Code follows an installation error’s recovery command, leading a script to fetch and execute a command from a DNS TXT record and open a reverse shell on the developer’s machine.

Jun 29, 2026
Threat Research · thedfirreport.com

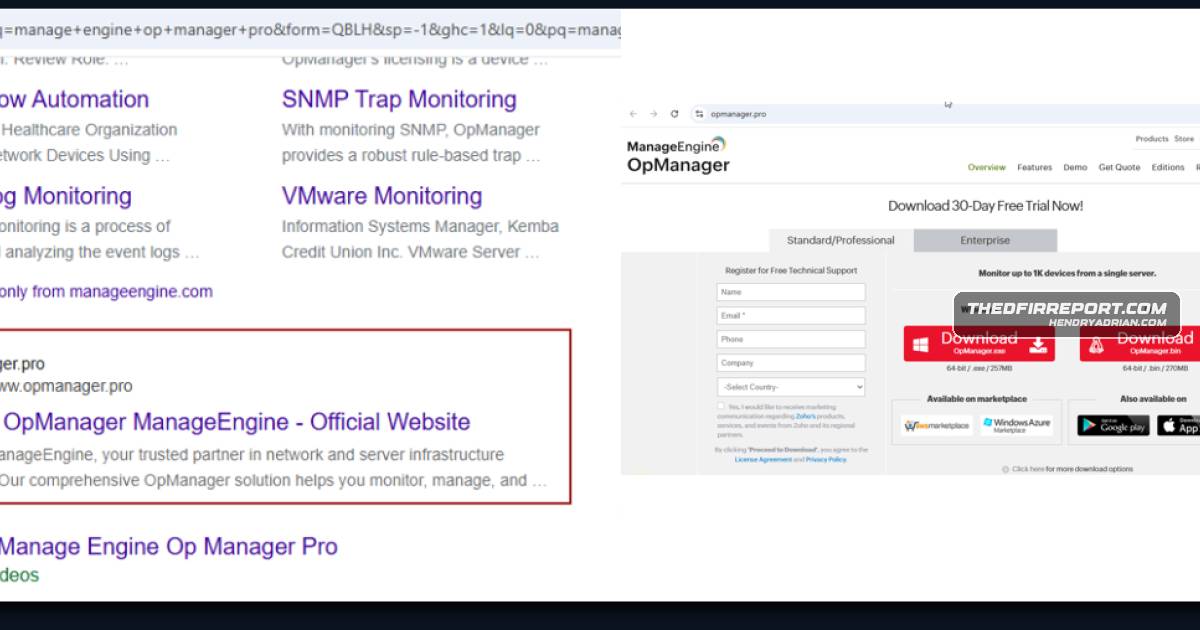
Bing SEO Poisoning Led to BumbleBee, AdaptixC2 and Akira Ransomware Intrusions

A DFIR investigation details two July 2025 intrusions linked to a BumbleBee SEO-poisoning campaign, tracing trojanized software downloads through AdaptixC2, credential theft and data exfiltration to Akira ransomware deployment.

Jun 29, 2026
Threat Research · wiz.io

Autonomous Agent Exploits BOLA in Airline GraphQL API, Exposing Passenger Data

Wiz says its Red Agent autonomously exploited a BOLA flaw in an airline’s GraphQL API, accessing passenger records and gaining the ability to modify or delete bookings. The company says it validated access using 20 sequential booking IDs.

Jun 29, 2026
Threat Research · thehackernews.com

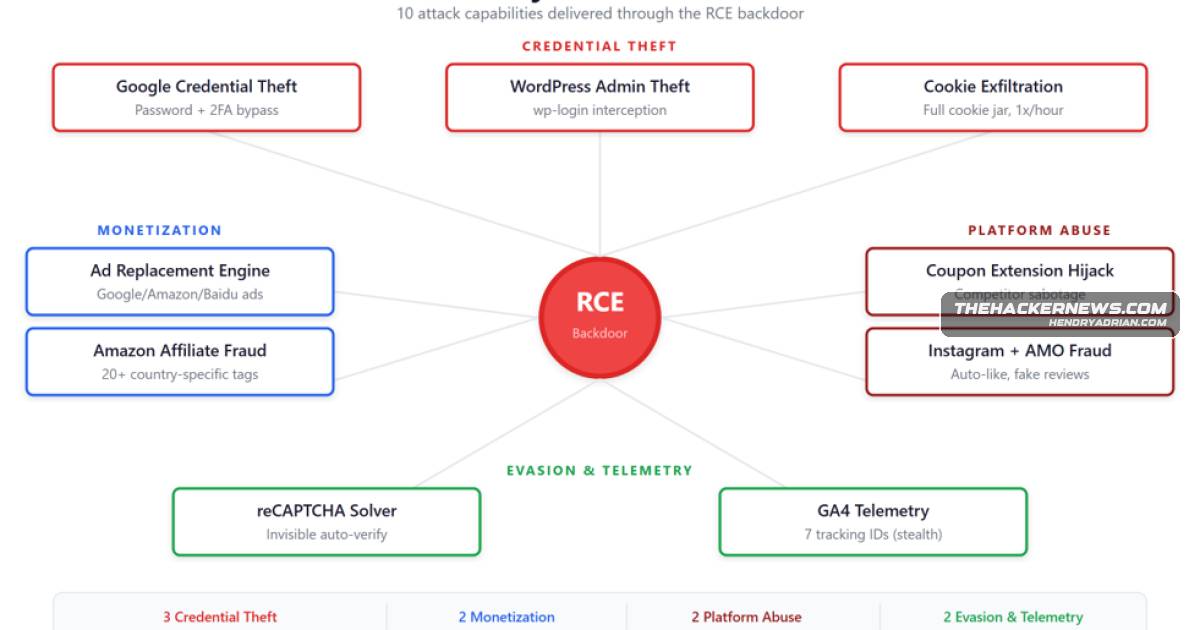
Microsoft Removes 119 Edge Extensions Linked to StegoAd Campaign

Microsoft removed 119 Edge extensions linked to StegoAd, which hid payloads in PNG, WebP and WOFF2 files and used delayed execution to evade analysis. Microsoft says they stole credentials and cookies; installs reached 2.6 million, but the number compromised is unknown.

Jun 29, 2026
Threat Research · huntress.com

Huntress Details Webshell Attack That Disabled Defenses and Dumped Credentials

Huntress details a webshell intrusion in which an attacker disabled logging and security tools, weakened WDigest protection, and dumped credentials. A server was re-compromised after being restored before remediation was complete.

Jun 29, 2026
Threat Research · trendmicro.com

TONResolver RAT Uses TON Blockchain in Phishing Campaign Targeting Japanese Hotels

Trend Micro details a phishing campaign targeting Japanese Booking.com partner hotels. TONResolver runs through Node.js and retrieves its command server from a TON smart contract, allowing attackers to change destinations; observed follow-on activity involved browser-st

Jun 29, 2026
Threat Research · acronis.com

Mustang Panda Campaigns Target Indian Government and Energy Sectors With New Malware

Acronis researchers detail two Mustang Panda campaigns targeting Indian government and hydropower entities with SHARDLOADER, MINIRECON and ZOHOMURK, which uses Zoho WorkDrive for command-and-control and data exfiltration.

Jun 28, 2026
Threat Research · thehackernews.com

StrikeShark Campaign Uses SharkLoader to Deploy Cobalt Strike Beacon

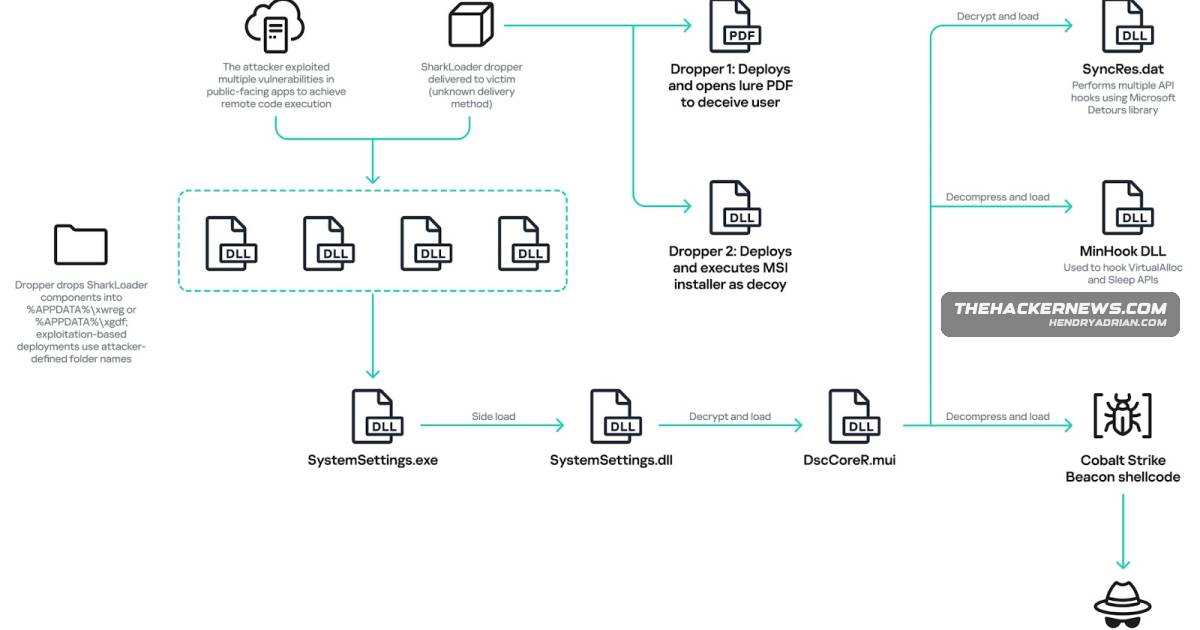
Kaspersky reports that StrikeShark uses SharkLoader to deploy Cobalt Strike Beacon after exploiting public-facing applications or using malicious droppers. The campaign targets organizations in multiple countries; no active data exfiltration has been observed.

Jun 27, 2026
Threat Research · sysdig.com

Sysdig Reports First Known In-the-Wild Exploitation of Langflow CVE-2026-55255

Sysdig says it observed the first known active exploitation of Langflow’s CVE-2026-55255 IDOR: an operator enumerated flow IDs and attempted to extract API keys while repeatedly trying CVE-2026-33017 RCE; the second-stage loader did not land.

Jun 27, 2026
PreviousPage 48 of 100 Next
© 2026 cyber.hendryadrian.com