
Mustang Panda Uses Zoho WorkDrive for C2 in Campaigns Targeting Indian Government
Summary
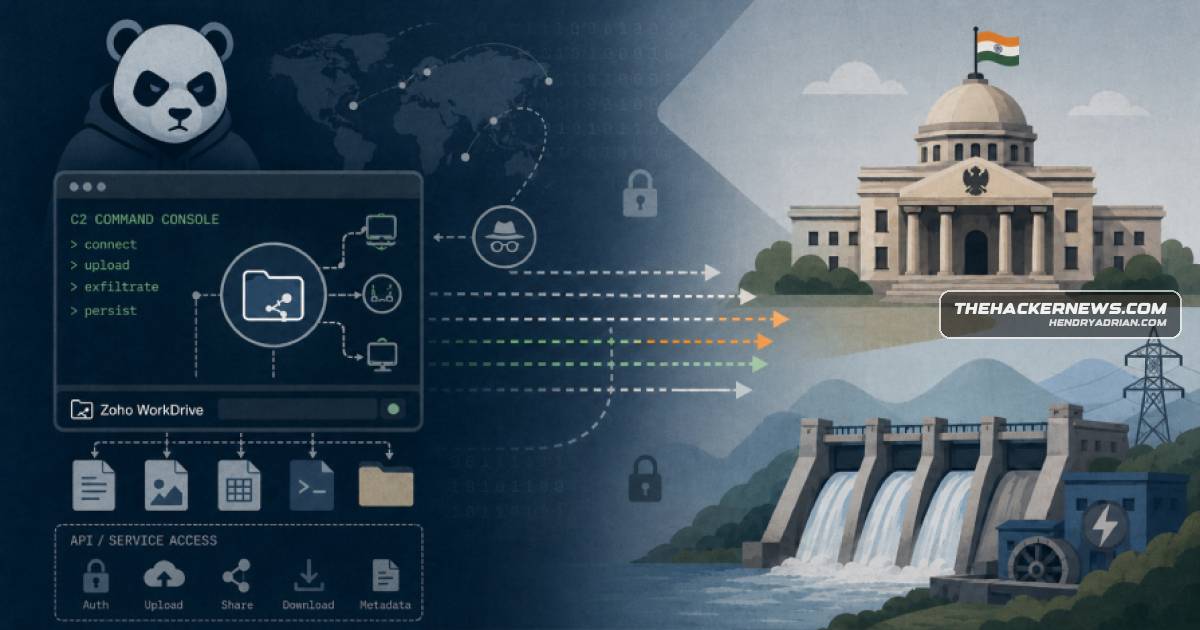
Acronis reports Mustang Panda campaigns targeting Indian government and hydropower organizations, detailing three tools that use signed-binary sideloading and Zoho WorkDrive for command delivery and data exfiltration.
Key points
- Acronis says it found active compromises in Indian government networks, including systems used by senior administrative staff, and worked with CERT-In on notification and cleanup.
- The campaigns allegedly used spear-phishing ZIP archives with hidden malicious DLLs, themed around hydropower cooperation and an India-Taiwan memorandum.
- SHARDLOADER sideloaded a malicious DLL through signed Solid PDF Creator or Citrix Receiver binaries, then deployed an implant.
- MINIRECON is described as a reworked Toneshell variant that beacons over HTTPS WebSockets.
- ZOHOMURK used hardcoded Zoho OAuth credentials to read commands from a WorkDrive inbox and write stolen output to an outbox.
- Acronis attributed the activity to Mustang Panda with high confidence, citing code overlap, reused infrastructure, and a recurring typo across implants.
- Acronis published hunting indicators, including persistence details, a scheduled task, Zoho user-agent patterns, and the C2 domain couldinstallup[.]com.
Article Details
- Attack Vectors
- Acronis believes both campaigns were delivered through spear-phishing ZIP archives themed around hydropower cooperation and an India–Taiwan memorandum of understanding.
- SHARDLOADER sideloaded a malicious DLL through legitimately signed Solid PDF Creator or Citrix Receiver binaries, then deployed an implant.
- ZOHOMURK used hardcoded Zoho OAuth credentials to read commands from an attacker-controlled Zoho WorkDrive inbox and write stolen data to an outbox.
- MINIRECON beaconed over WebSocket on HTTPS; the campaigns also used Zoho WorkDrive as a covert command channel and for data exfiltration.
- Defensive Notes
- Monitor for geopolitical-themed lures and malicious DLL sideloading through signed binaries.
- Hunt for the reported persistence Run keys and the scheduled task named SolidPDFPcl2Bmp.
- Flag endpoint processes making cloud API calls they have no legitimate reason to use, including suspicious Zoho WorkDrive activity.
- Acronis and CERT-In shared indicators and hunting guidance; the article says there is no patch to apply.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | couldinstallup[.]com | C2 domain listed by the article as an indicator for the campaigns. |
MITRE ATT&CK
T1053.005 · Scheduled TaskThe article lists a scheduled task named SolidPDFPcl2Bmp among the campaign hunting indicators.T1071.001 · Web ProtocolsMINIRECON beaconed over a WebSocket connection on HTTPS.T1102.002 · Bidirectional CommunicationZOHOMURK used an attacker-controlled Zoho WorkDrive account to retrieve commands from an inbox and send output to an outbox.T1547.001 · Registry Run Keys / Startup FolderThe article lists persistence Run keys among the campaign hunting indicators.T1564.001 · Hidden Files and DirectoriesThe malicious DLL in the ZIP archives was marked hidden.T1566.001 · Spearphishing AttachmentAcronis believes the campaigns were delivered through spear-phishing ZIP archives.T1567.002 · Exfiltration to Cloud StorageThe malware wrote stolen data to a Zoho WorkDrive outbox, using cloud storage for exfiltration.T1574.002 · DLL Side-LoadingSHARDLOADER sideloaded a malicious DLL through signed Solid PDF Creator or Citrix Receiver binaries.
Threat Actors
Malware
LOTUSLITEIn April, Acronis tied the group’s LOTUSLITE backdoor to attacks on India’s banking sector and South Korean policy circles, also staged through a legitimate cloud service.MINIRECONAcronis linked the activity to three tools—SHARDLOADER, MINIRECON, and ZOHOMURK—and published indicators to help defenders detect the campaign.ShadowPadThe broader China-linked interest in India’s power sector goes back further: the 2021 RedEcho campaign targeted the country’s electricity grid with ShadowPad.SHARDLOADERAcronis linked the activity to three tools—SHARDLOADER, MINIRECON, and ZOHOMURK—and published indicators to help defenders detect the campaign.TONESHELLMINIRECON is a reworked variant of the Toneshell backdoor documented by IBM X-Force, now beaconing over a WebSocket connection on HTTPS.ZOHOMURKAcronis linked the activity to three tools—SHARDLOADER, MINIRECON, and ZOHOMURK—and published indicators to help defenders detect the campaign.
Vendors
AcronisAcronis linked the activity to three tools—SHARDLOADER, MINIRECON, and ZOHOMURK—and published indicators to help defenders detect the campaign.ZohoMustang Panda is targeting Indian government and hydropower-related organizations with spear-phishing, sideloading malware, and abuse of Zoho WorkDrive as a covert command channel.
Products
Citrix ReceiverSHARDLOADER is a loader that runs by sideloading a malicious DLL through a legitimately signed binary, a Solid PDF Creator executable in one campaign, and a Citrix Receiver binary in the other.Solid PDF CreatorSHARDLOADER is a loader that runs by sideloading a malicious DLL through a legitimately signed binary, a Solid PDF Creator executable in one campaign, and a Citrix Receiver binary in the other.Zoho WorkDriveMustang Panda is targeting Indian government and hydropower-related organizations with spear-phishing, sideloading malware, and abuse of Zoho WorkDrive as a covert command channel.
Countries
ChinaThe China-aligned espionage group Mustang Panda is running two campaigns against the Indian government and hydropower targets, deploying new malware and turning a legitimate cloud service into its command channel.IndiaThe malware abuses Zoho WorkDrive, a cloud storage platform common in India’s government sector, to pass commands and exfiltrate data.TaiwanPer Acronis, the goal is intelligence on India’s hydropower plans and its defense ties with Taiwan.
Industries
BankingIn April, Acronis tied the group’s LOTUSLITE backdoor to attacks on India’s banking sector and South Korean policy circles, also staged through a legitimate cloud service.EnergyGovernment and energy organizations, especially those tied to cross-border deals likely to interest Beijing, should watch for geopolitical lures and sideloading from signed binaries.GovernmentMustang Panda is targeting Indian government and hydropower-related organizations with spear-phishing, sideloading malware, and abuse of Zoho WorkDrive as a covert command channel.