
Glitch SPY Android RAT Uses Fake Polish Rental App for Delivery
Summary
Cyble analyzed Glitch SPY, an Android RAT delivered through a fake Polish rental app by the Brokewell Android Loader. It abuses Accessibility for control and data theft, and includes crypto-clipping and hidden browser capabilities; distribution appears early-stage.
Key points
- Cyble identified Glitch SPY branding on an exposed C&C panel; one recovered APK and two identified panel URLs suggest early-stage distribution.
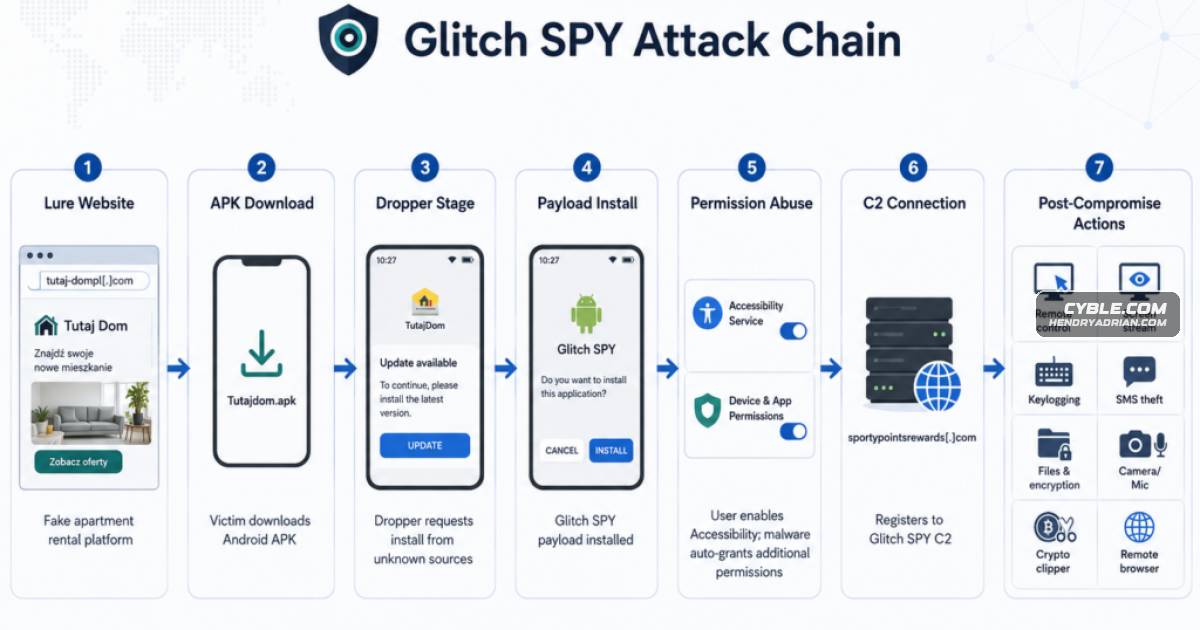
- A fake Polish rental website lures users into downloading an APK; the Brokewell Android Loader acts as a dropper that installs Glitch SPY.
- Glitch SPY abuses Android Accessibility to automate permission flows, interact with the device, extract visible text, and support remote control.
- Its persistent WebSocket C&C supports more than 70 commands, including screen streaming, keylogging, and collection of SMS, contacts, call logs, files, and location data.
- A crypto-clipper can replace copied ETH/EVM, TRON, and Bitcoin wallet addresses with operator-configured addresses.
- A hidden remote browser lets operators control web sessions on the infected device; the article says this could enable account takeover using the victim’s environment.
- The sample has file encryption and decryption functions, but Cyble found no automated mass-encryption routine, ransom note, or payment workflow.
Article Details
- Attack Vectors
- A fake Polish rental website distributes Tutajdom.apk, which presents a rental-themed decoy and acts as a dropper for Glitch SPY.
- The loader prompts users to allow installation from unknown sources; after installation, Glitch SPY prompts for Android Accessibility Service access and abuses it to automate permissions and control the device.
- Glitch SPY maintains a WebSocket C2 channel and supports remote screen viewing, input, file access, surveillance, and theft.
- Its clipboard-monitoring module can replace copied cryptocurrency wallet addresses with operator-configured addresses.
- A hidden remote browser on the infected device can be controlled to navigate websites and enter or submit text.
- Defensive Notes
- Install apps only from trusted official sources and avoid APK links from unfamiliar websites.
- Do not grant installation-from-unknown-sources or Accessibility permissions to apps unless their legitimacy is verified.
- Keep Google Play Protect enabled and keep Android and apps updated.
- Use multi-factor authentication for banking and financial apps.
- If infection is suspected, report it to the bank and local authorities, reset credentials, and consider a factory reset.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | gich[.]etherraffleexchange[.]us | Additional Glitch SPY admin-panel URL identified by the researchers; no communicating APK associated with this panel had been recovered. |
| DOMAIN | sportypointsrewards[.]com | C2 domain observed communicating with Glitch SPY. |
| SHA256 | 80af5e921cf8a3052fe4483bb2eb15953590e72ed003ac61c0b9135575c32075 | SHA-256 hash reported for a Glitch SPY sample. |
| SHA256 | d439475bf09af7b474cdba2c19e136a1dd38e62b088537445ac3c8e4c2d3a8b1 | SHA-256 hash reported for the Brokewell Android Loader sample. |
| URL | hxxps[:]//tutaj-dompl[.]com/Tutajdom.apk | APK distribution URL identified as the download link on the fake Polish rental site. |
MITRE ATT&CK
T1414Glitch SPY monitors clipboard contents and can replace copied cryptocurrency wallet addresses.T1417.001Glitch SPY includes a keylogging module that operators can start and retrieve data from.T1418Glitch SPY enumerates applications installed on the infected Android device.T1420The malware lists files and folders from specified paths on the infected device.T1426Glitch SPY collects device metadata and system information for its C2 panel.T1430The malware can retrieve and report the infected device's location.T1437Glitch SPY maintains a persistent WebSocket-based communication channel with its C2 server.T1453Glitch SPY abuses Android Accessibility Service to inspect UI elements, extract visible text, automate permission grants, and interact with the device.T1471Glitch SPY can encrypt selected files into .enc files and remove the plaintext originals; the analyzed sample did not establish automated mass encryption or a ransom workflow.T1513The malware captures screenshots and streams screen frames from infected devices to its C2 panel.T1516The malware performs remote taps, swipes, gestures, and text entry on the infected device.T1636.003The malware extracts the victim's contact list.T1636.004The malware collects SMS messages from the infected device.T1646The malware returns collected information and files to its C2 server through the established channel.T1660Glitch SPY is distributed through a deceptive rental-themed website that lures users into downloading an APK.