
Astaroth Adds WhatsApp Web Spambot to Spread Malware in Brazil
Summary
CrowdStrike reports that Astaroth added a WhatsApp Web spambot in Q4 2025, using hidden browser automation to send malware to Brazilian contacts. Code overlap links it to Vareg, though the relationship between operators remains uncertain.
Key points
- CrowdStrike says Astaroth installers began distributing a WhatsApp Web spambot in Q4 2025, shifting from traditional email-based spam to messaging contacts.
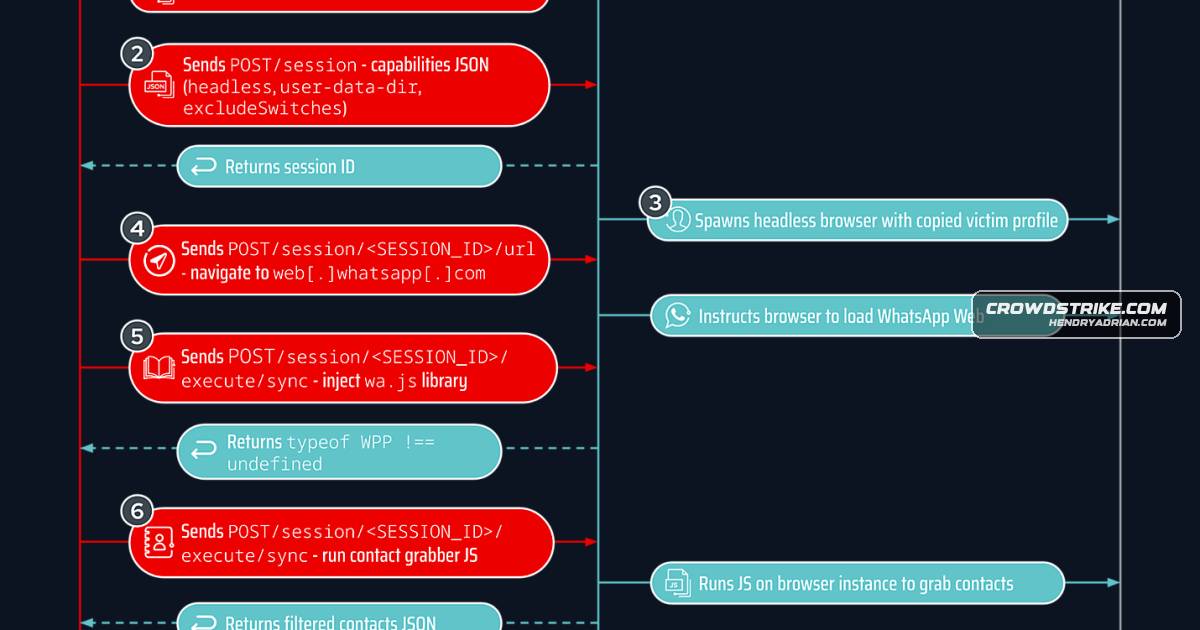
- The spambot downloads a WebDriver with PowerShell, runs Chrome or Edge in hidden headless mode, and uses the victim’s browser profile to access a WhatsApp Web session.
- It collects contacts, filters for Brazilian phone numbers beginning with +55, and sends Portuguese-language messages with a malware ZIP attachment.
- The Delphi spambot reuses Astaroth’s loader chain and encryption methods; its strings use a six-stage obfuscation process.
- Code similarities with Vareg include function and variable names, contact filtering, message delivery, and delay logic. CrowdStrike says this suggests a shared developer or code-sharing arrangement, but does not establish that the operators are the same.
- The report recommends monitoring WebDriver downloads, ChromeAuto_ profile-folder creation, headless browsers, and WPPConnect/WA-JS activity; it also provides a YARA rule and a Falcon LogScale query.
Article Details
- Attack Vectors
- Astaroth is delivered through a downloader component, often a Windows LNK file running JScript, that retrieves an installer; the installer’s loader chain decrypts and executes the core component.
- In Q4 2025, Astaroth’s C2 servers began distributing a WhatsApp Web spambot that uses a hidden browser session and the victim’s profile to access WhatsApp Web.
- The spambot downloads WebDriver and WPPConnect/WA-JS, collects saved contacts with Brazil country code 55, then sends contacts a greeting, a malware ZIP attachment, and a message.
- The spambot’s strings and configuration use layered obfuscation, Base64 encoding, and encryption.
- Defensive Notes
- Monitor PowerShell-driven WebDriver downloads, especially to unusual folder destinations.
- Monitor creation of folders matching ChromeAuto_<BROWSER_ID><DATE> under C:UsersPublicTemp.
- Monitor for headless browser instances and block WebDriver execution when it is not needed for business purposes.
- Consider blocking WhatsApp Web when it is not required for business purposes.
- Monitor downloads and execution of WPPConnect/WA-JS; consider blocking access to its GitHub URL when it is not needed.
- Enable browser download protections and train users to avoid executing files or commands from untrusted sources, including messages from unknown contacts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | graconxonjal[.]empresaeficiente[.]sbs | Listed as an Astaroth installer component C2 server. |
| DOMAIN | plansonval[.]impostosrapido[.]top | Listed as an Astaroth installer component C2 server. |
| DOMAIN | stretar7[.]contabilfacil[.]sbs | Listed as an Astaroth installer component C2 server. |
| SHA256 | 6168d63fad22a4e5e45547ca6116ef68bb5173e17e25fd1714f7cc1e4f7b41e1 | SHA-256 hash of the Vareg spambot Python version. |
| SHA256 | a1aa786e02fb9a37a71e0f76b052ab284ba877f2aaa2fb28f05d60487389976a | SHA-256 hash of the Vareg spambot PowerShell version. |
| SHA256 | c7c62303ee1a37fd7a6e2db9c590ba75c647bc4d22d7dca50cfa8879222ac9e1 | SHA-256 hash of the encrypted Astaroth spambot. |
| SHA256 | d89105c4d567a95f674ed6eac538e32e288b658a4222a3d52e284a77782af4d5 | SHA-256 hash of the decrypted Astaroth spambot binary. |
| SHA256 | ec43a17685e3a555c2eb5f0a2802e9e45d5a2a5d49a0803155acbd74d9ecdbd7 | SHA-256 hash of the encrypted Astaroth spambot configuration file. |
| URL | hxxps[:]//docsmoonstudioclayworks[.]online/arquivoatualizado/gera.php | C2 URL for the Vareg spambot PowerShell version. |
| URL | hxxps[:]//varegjopeaks[.]com/api/ | C2 URL for the Vareg spambot Python version. |
MITRE ATT&CK
T1005 · Data from Local SystemThe spambot reads the victim’s WhatsApp Web contact list and copies the browser profile containing information such as cookies and credentials.T1027 · Obfuscated Files or InformationThe spambot uses multiple layers of string obfuscation, custom transformations, Base64 encoding, and encryption.T1059.001 · PowerShellAstaroth uses a PowerShell command to download a browser WebDriver selected for the installed browser.T1059.007 · JavaScriptThe downloader component can be a Windows LNK file running JScript code.T1105 · Ingress Tool TransferThe spambot retrieves WebDriver, the WPPConnect/WA-JS library, and a Base64-encoded ZIP payload from remote sources.T1140 · Deobfuscate/Decode Files or InformationAstaroth’s loader decrypts the spambot, and the component decodes strings and decrypts its configuration before use.T1185 · Browser Session HijackingThe spambot copies the victim’s browser profile and uses it to launch a browser instance that accesses the victim’s WhatsApp Web session.T1564.003 · Hidden WindowThe spambot launches WebDriver in a hidden window and runs the browser in headless mode.T1566.003 · Spearphishing via ServiceThe spambot sends WhatsApp contacts messages containing a malware ZIP attachment.
Malware
AstarothAstaroth (aka Guildma) operators added a WhatsApp Web spambot in Q4 2025, shifting from email-based distribution to automated messaging that turns infected victims into unwilling propagators of the malware.GuildmaAstaroth (aka Guildma) operators added a WhatsApp Web spambot in Q4 2025, shifting from email-based distribution to automated messaging that turns infected victims into unwilling propagators of the malware.VaregThe analysis shows strong code overlap with the Vareg (aka WATER SACI, Eternidade) spambot and confirms Brazil-focused targeting through contact filtering, Portuguese templates, and Brazil-specific technical checks.WATER SACIThe analysis shows strong code overlap with the Vareg (aka WATER SACI, Eternidade) spambot and confirms Brazil-focused targeting through contact filtering, Portuguese templates, and Brazil-specific technical checks.
Products
Google ChromeThe Astaroth spambot supports Google Chrome and Microsoft Edge browsers.Microsoft EdgeThe Astaroth spambot supports Google Chrome and Microsoft Edge browsers.WhatsApp WebAstaroth (aka Guildma) operators added a WhatsApp Web spambot in Q4 2025, shifting from email-based distribution to automated messaging that turns infected victims into unwilling propagators of the malware.