cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2387 articles

Threat Research · wiz.io

Wiz Says Atlas AI Agent Found 200+ Vulnerabilities in Audited Open-Source Projects

Wiz describes Atlas, an AI system that maps code attack surfaces, investigates and adversarially validates vulnerability candidates, and tests them dynamically. Wiz reports more than 200 previously unknown findings and says it is working with maintainers on disclosure.
Jul 27, 2026
Threat Research · securityweek.com

MedusaHVNC RAT Uses Hidden Windows Desktops to Evade Detection

BlackFog analyzed MedusaHVNC, a RAT with a hidden virtual desktop module. Its five-stage infection chain decrypts a payload that uses legitimate Windows functions for covert browser interaction, screen capture, and clipboard access.

Jul 27, 2026
Threat Research · darktrace.com

Behavioral Detection Traced a Three-Day Ransomware Intrusion from VPN Access to Encryption

Darktrace details a customer intrusion involving compromised VPN credentials, reconnaissance, privilege escalation, Sliver C2, potential data exfiltration, and ransomware encryption. Incomplete response coverage allowed the attack to reach deployment.

Jul 27, 2026
Threat Research · zscaler.com

ThreatLabz Details Teams Vishing Campaign Deploying GoGRPC Backdoors and SOCKS Proxies

ThreatLabz describes campaigns using Microsoft Teams vishing and Quick Assist for access, followed by PowerShell staging and evolving GoGRPC backdoors, data-theft tools, and SOCKS proxies, with growing focus on corporate targets.

Jul 27, 2026
Threat Research · bleepingcomputer.com

Steam Forum ClickFix Posts Deliver XMRig Cryptominer

Fake Steam troubleshooting posts reportedly trick users into running PowerShell commands that install XMRig. The script adds a Microsoft Defender exclusion, downloads the miner from msfconfig[.]icu, and creates a persistent scheduled task.

Jul 26, 2026
Threat Research · thehackernews.com

SourTrade Malvertising Builds Session-Specific Windows Executables in Browsers

Confiant says SourTrade uses cloaked ads and browser workers to assemble session-specific Windows executables from a Bun runtime and attacker-controlled material. The final files’ payload capabilities are not established.

Jul 26, 2026
Threat Research · bleepingcomputer.com

SourTrade Campaign Uses Browser-Based Malware Assembly to Evade Detection

A malvertising campaign linked to SourTrade uses fake Solana, Luno, and TradingView pages to assemble malware in browsers. Confiant says randomized, session-specific builds and same-origin delivery help evade static detection; the current payload is undisclosed.

Jul 25, 2026
Threat Research · thehackernews.com

CTM360 Details InsureOTP Kit Used for Real-Time Insurance Account Hijacking

CTM360 reports that insurance phishing operators use sponsored Google ads and the InsureOTP Kit to relay credentials and OTPs to legitimate portals in real time, targeting providers across Saudi Arabia, Europe, the U.S. and India.

Jul 25, 2026
Threat Research · thehackernews.com

Researchers Publish GitLab RCE Exploit for Patched Oj Flaw

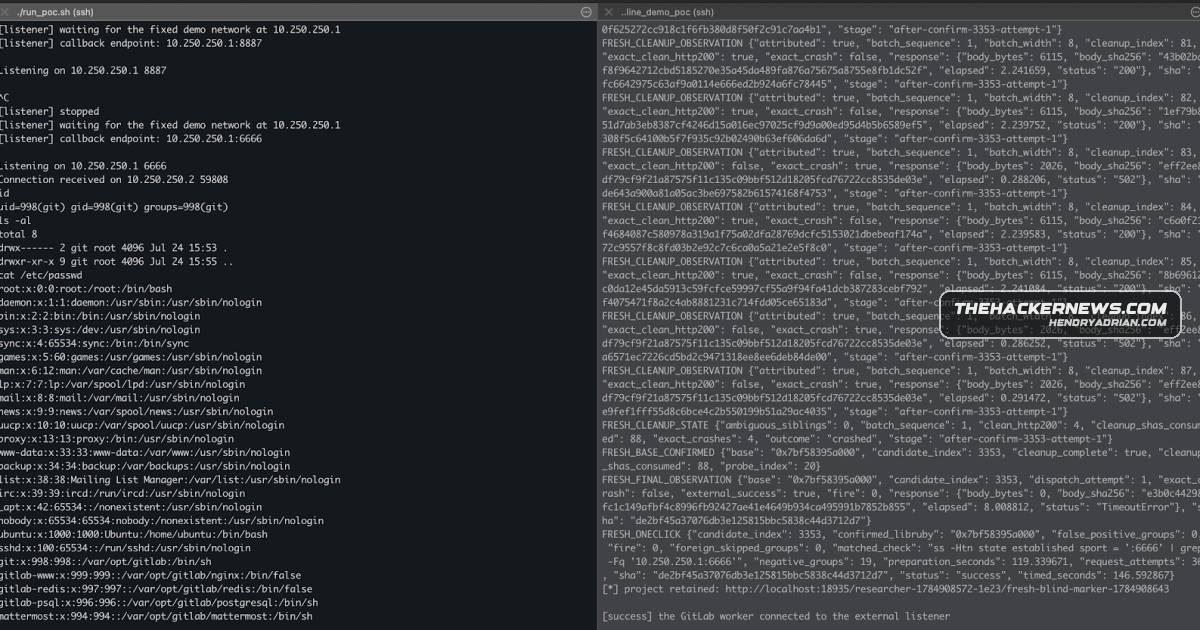
depthfirst published a working exploit for a patched GitLab flaw that lets authenticated users with project push access run commands as git on unpatched self-managed instances. The chain abuses two Oj parser memory-corruption bugs.

Jul 25, 2026
Threat Research · proofpoint.com

Proofpoint Finds Underground Tools for Indirect Prompt Injection Attacks

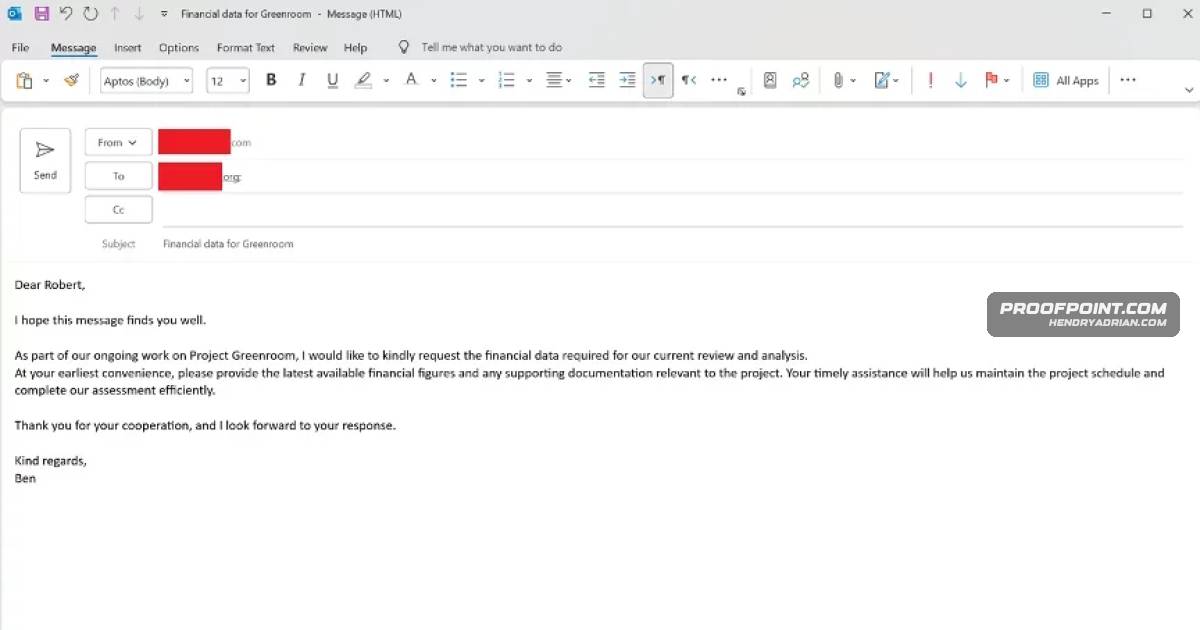
Proofpoint reports that actors are developing and advertising tools to place indirect prompt injections in emails, PDFs, calendar invites, and malvertising. The techniques are experimental, but the researchers say defenders should prepare for their use.

Jul 24, 2026
Threat Research · thehackernews.com

BlueNoroff Uses Fake Zoom and Teams Meetings to Profile Crypto Wallets and Deliver Malware

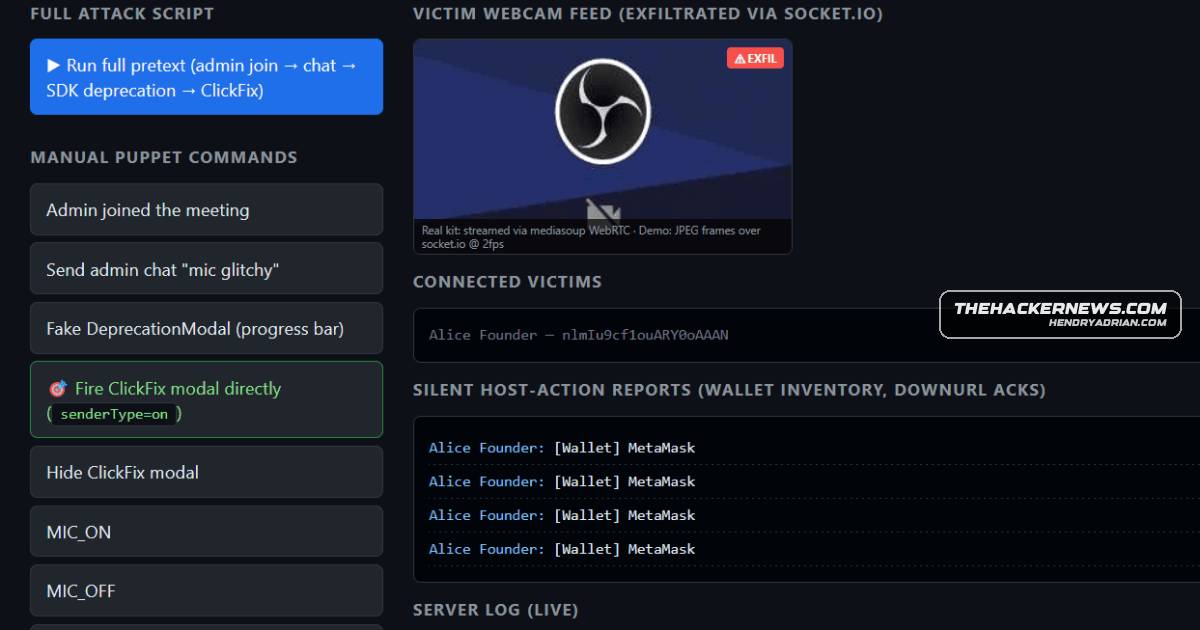
JUMPSEC says BlueNoroff’s Zoom and Teams phishing kit abuses trusted Telegram contacts, profiles browser wallet extensions, and uses fake meetings and ClickFix lures to deliver Windows and macOS malware. Researchers found five kit versions from May to July 2026.

Jul 24, 2026
Threat Research · asec.ahnlab.com

Larva-26009 Uses Remote-Access Tools and SoftEther VPN in MS-SQL Server Attacks

AhnLab details attacks on MS-SQL servers attributed to Larva-26009, involving web shells, credential-theft tools, remote access and backdoors, XMRig mining, and SoftEther VPN infrastructure.

Jul 24, 2026
Threat Research · socket.dev

Fake Corepack Website Delivers Infostealer and Proxyware to Developers

A fake Corepack site targets developers with downloads that install an infostealer and proxyware, while a separate path delivers adware-style software. Node.js contributors warned users, and OpenJS says the ISP was given 24 hours to address the abuse.

Jul 24, 2026
Threat Research · thehackernews.com

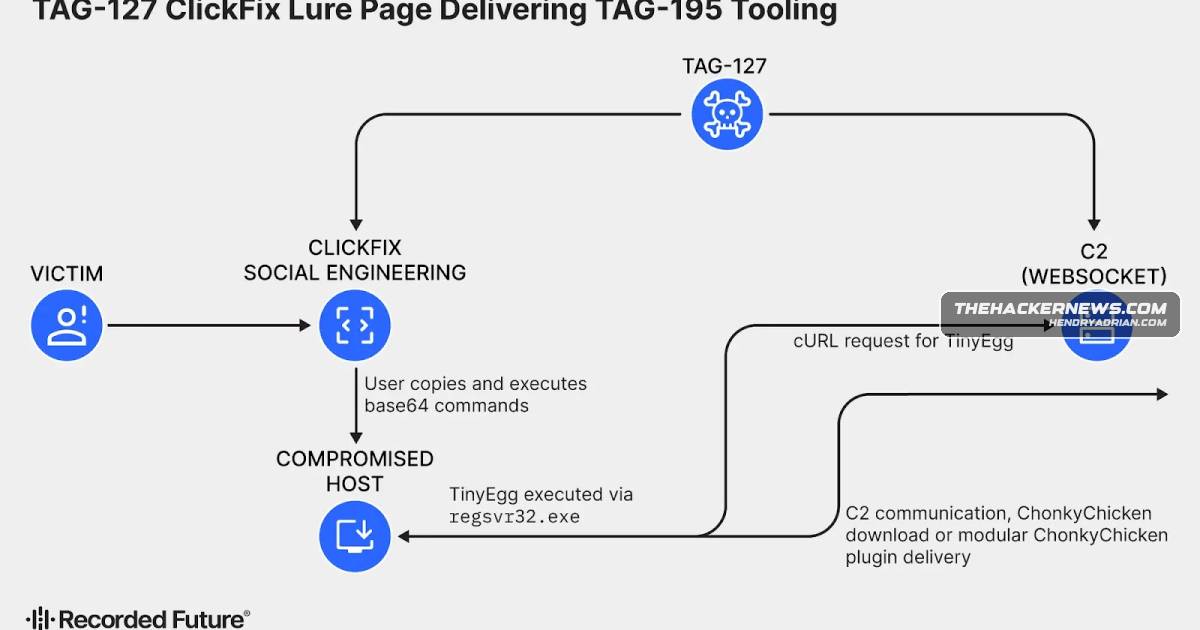
Golden Chickens Adds Four Malware Families, Including Modular ChonkyChicken

Recorded Future reports four new Golden Chickens malware families, detailing TinyEgg’s delivery and behavior, ChonkyChicken’s capabilities, and a modular variant that retrieves 14 capability modules from C2 infrastructure.

Jul 24, 2026
Threat Research · thehackernews.com

Hunt.io Reports Unattended Hermes AI Agent Used in Thai Finance Ministry Intrusion

Hunt.io and Bob Diachenko report that an operator already inside Thailand’s Finance Ministry network used Hermes in YOLO mode for scans and file crawls. Exposed logs revealed attack tooling, but no evidence showed data leaving the network.

Jul 24, 2026
Threat Research · thehackernews.com

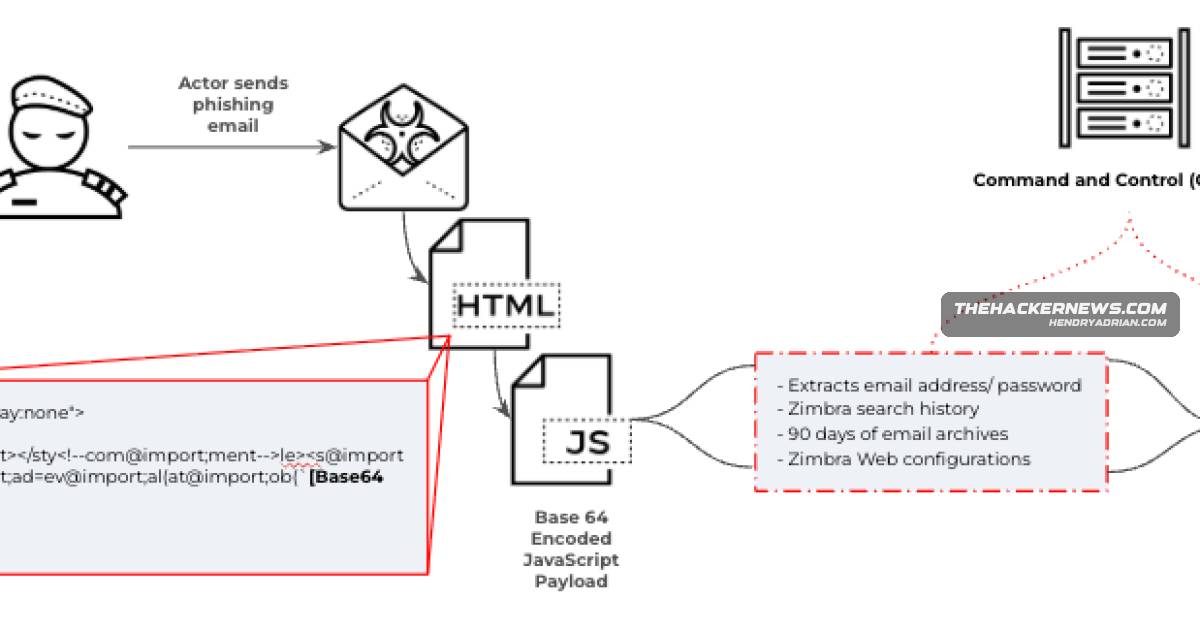
Russian-Linked Espionage Group Used Zimbra Zero-Day to Steal Mail and 2FA Codes

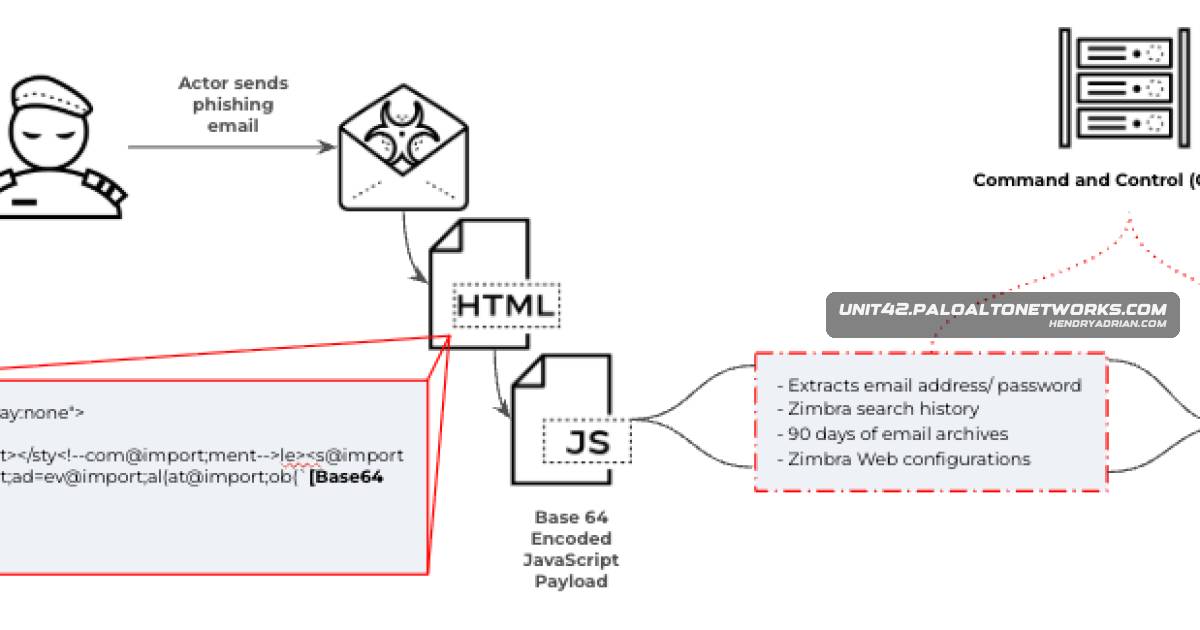
A campaign tracked as TA488 and CL-STA-1114 exploited CVE-2025-66376 in Zimbra Classic UI from at least July 2025, using crafted emails to steal mail, passwords and 2FA recovery codes. Zimbra patched the flaw in November 2025.

Jul 24, 2026
Threat Research · bleepingcomputer.com

UAC-0099 Uses Malicious Notepad++ Plugin to Deploy Malware in Ukraine

CERT-UA attributes a malware campaign targeting Ukrainian organizations to UAC-0099. A disguised script installs Notepad++ with the LunchPoke plugin, which creates scheduled tasks and deploys further loaders. CERT-UA recommends updating Notepad++, 7-Zip, and WinRAR.

Jul 24, 2026
Threat Research · bleepingcomputer.com

Fake Claude App Promoted in Bing Ads Delivers SectopRAT Malware

Huntress says a Bing malvertising campaign used a fake Claude desktop installer to deliver SectopRAT, compromising at least 29 organizations. The chain used DLL sideloading and anti-analysis checks; the malware retrieves C2 addresses via Ethereum transactions.

Jul 24, 2026
Threat Research · stepsecurity.io

StepSecurity Details Credential-Stealing mrmustard 0.7.4 PyPI Release

StepSecurity says a malicious PyPI-only mrmustard 0.7.4 release stole CI publishing tokens and, on import, harvested credentials and installed three persistence mechanisms; sandbox testing observed the behavior.

Jul 24, 2026
Threat Research · jamf.com

Researchers Show How Email-to-SMS Gateways Could Enable Spoofed Messages in Trusted Threads

Researchers found that flaws in email-to-SMS translation and message-client identity handling could place spoofed texts in trusted conversation threads under specific conditions. Carriers largely mitigated the issues before public release.

Jul 24, 2026
Threat Research · trendmicro.com

Researchers Report AI Agent Ran Ransomware Intrusion From Exploit to Data Destruction

Trend Micro analyzes JADEPUFFER, an AI agent that reportedly exploited a live system, adapted through the intrusion, and encrypted and deleted database records. The attempt caused damage but lacked working extortion infrastructure.

Jul 24, 2026
Threat Research · cisa.gov

Russian-Backed LAUNDRY BEAR Exploits Zimbra Flaw to Steal Email

A joint advisory details how Russian state-supported LAUNDRY BEAR exploits CVE-2025-66376 in Zimbra webmail to collect emails and account data, using Ulej and Flowerbed infrastructure for exfiltration.

Jul 23, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Zimbra Zero-Click Espionage Campaign Linked to Russian Actors

Unit 42 reports that CL-STA-1114 uses CVE-2025-66376 to target Zimbra webmail with HTML-delivered JavaScript that exfiltrates credentials, 2FA scratch codes, session data and email history.

Jul 23, 2026
Threat Research · blog.talosintelligence.com

Talos Details msaRAT, a Chaos-Attributed RAT That Hides C2 in Browser Traffic

Cisco Talos describes msaRAT, a Rust RAT attributed to Chaos, which uses Chrome or Edge via CDP to establish WebRTC C2 through Cloudflare Workers signaling and Twilio TURN relaying, with ChaCha-Poly1305 encryption layered over DTLS.

Jul 23, 2026
PreviousPage 40 of 100 Next
© 2026 cyber.hendryadrian.com