cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · socket.dev

Socket Links 77 Firefox Extensions to Crypto Wallet and Credential Theft

Socket traced 77 linked Firefox extensions to a campaign involving wallet-secret theft, credential and clipboard collection, and deceptive sports-score shells. The research confirmed malicious payloads in 40 extensions; Mozilla removed one reported extension.
Aug 19, 2026
Threat Research · netspi.com

BOFScale Runs Tailscale In-Memory to Route C2 Traffic Through CDN-Fronted WebSockets

BOFScale runs a modified Tailscale daemon inside a BOF-PE implant and routes traffic through CDN-fronted WebSockets. The article details its Headscale setup, an NTLM relay workflow, and detection opportunities.

Aug 19, 2026
Threat Research · thehackernews.com

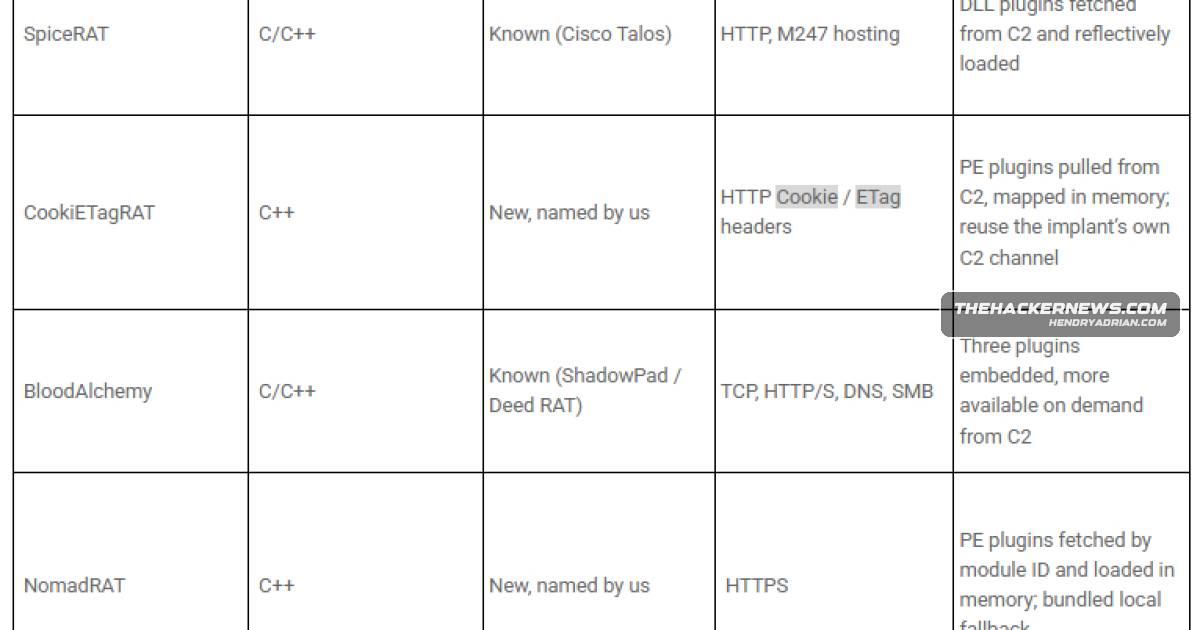
SilkParasite Campaign Targets Central Asian Governments With Five Newly Documented RATs

Bitdefender describes SilkParasite, an espionage campaign targeting Central Asian governments with seven RAT families, five newly documented. The report details spear-phishing, DLL sideloading, modular implants and evidence suggesting a China-nexus cluster.

Aug 19, 2026
Threat Research · rapid7.com

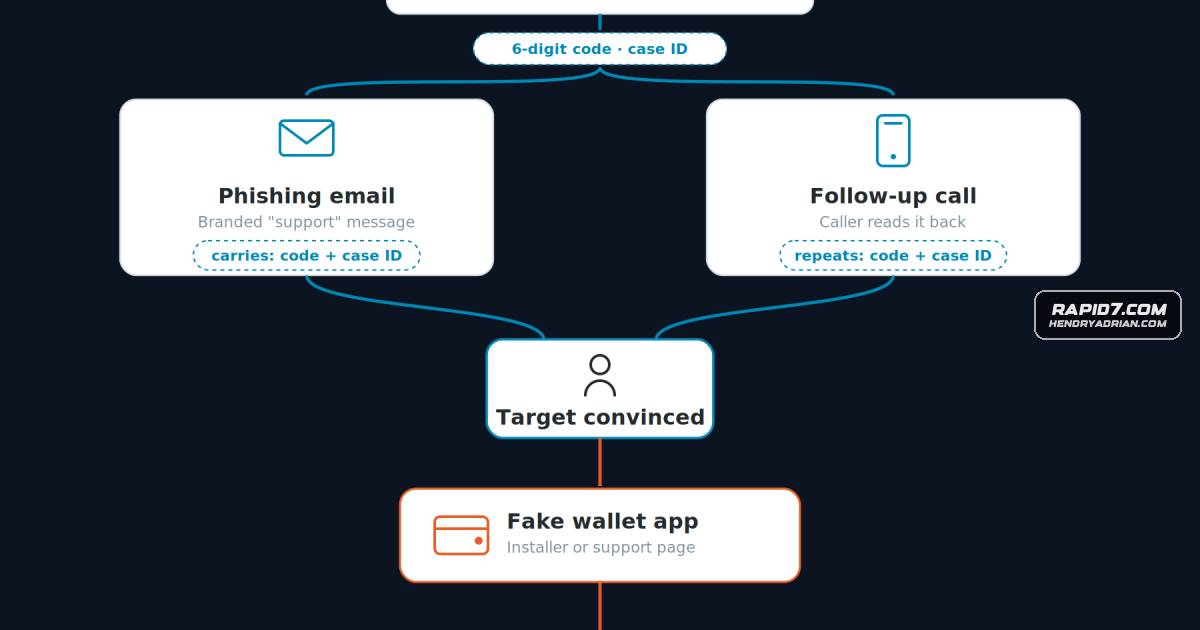
Operation ASTERIX Uses Vishing and Fake Wallet Apps in Crypto Fraud Pipeline

Rapid7 reconstructed Operation ASTERIX from an exposed server, uncovering crypto account enumeration, coordinated phishing and vishing, fake wallet apps, Telegram exfiltration and AI-assisted malware development.

Aug 19, 2026
Threat Research · gendigital.com

WordlistLoader Delivers Amatera Stealer in ClearFake Campaigns

Gen Threat Labs analyzes ClearFake fake-CAPTCHA/ClickFix chains delivering Amatera via WordlistLoader, detailing shellcode decoding and evasion plus Amatera 4.3.3-alpha1’s syscall hardening and Application-Bound Encryption bypass.

Aug 19, 2026
Threat Research · opensourcemalware.com

Researchers Link npm and RubyGems Typosquatting Campaigns to the Same Infostealer

Researchers linked npm and RubyGems typosquatting campaigns to the same actor through identical payload hashes and shared infrastructure. The npm packages were removed; the malware targeted Windows hosts and stole credentials and other data.

Aug 19, 2026
Threat Research · guardsix.com

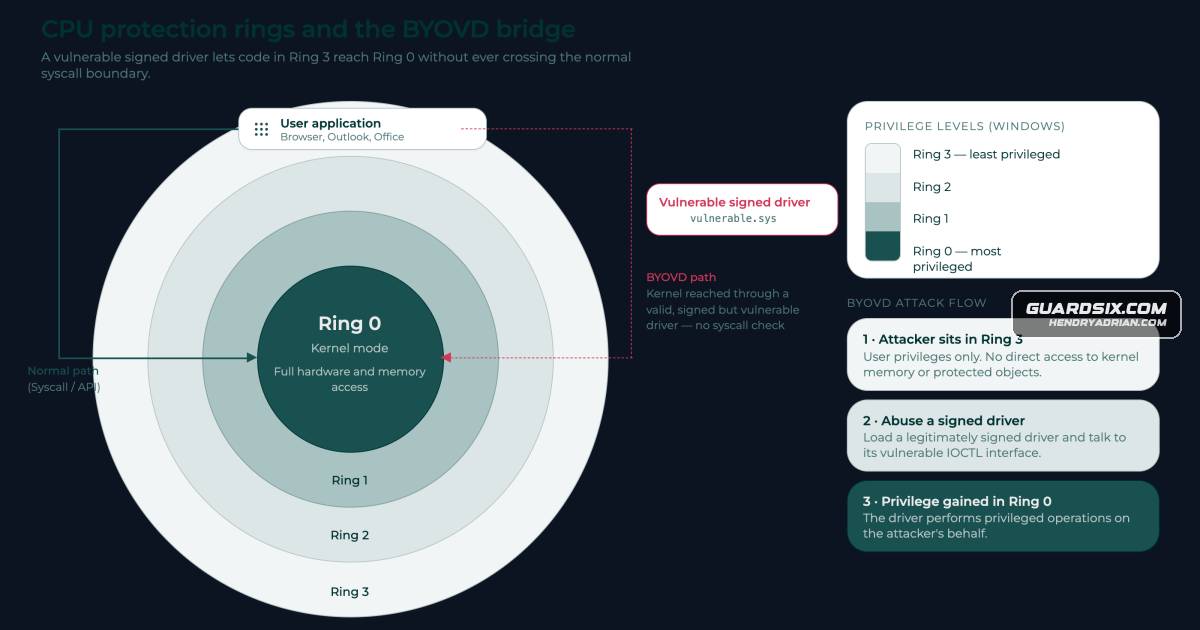
BYOVD Attacks Turn Signed Vulnerable Drivers into Kernel-Level Backdoors

The article examines how ransomware operators abuse signed, vulnerable Windows drivers to gain kernel-level access and disable endpoint defenses, highlighting active groups, driver-blocklist evasions, and gaps in signature enforcement.

Aug 19, 2026
Threat Research · circleid.com

Researchers Detail Hotel-Targeting Photo ZIP Campaign and Related Infrastructure

Microsoft reported a hotel-targeting campaign using photo-themed ZIPs and fake image shortcuts; the article adds DNS, WHOIS and email-domain analysis. The actors’ objective remains unclear, and 2,357 IPs were only potentially victim-associated.

Aug 19, 2026
Threat Research · netskope.com

Malware Uses Blockchain Dead Drops to Retrieve Runtime C2 Pointers

A Netskope primer explains how malware retrieves runtime C2 pointers through EVM smart contracts, Solana transaction memos and TON lookups, and recommends correlating RPC details, decoded results and process context to detect the activity.

Aug 19, 2026
Threat Research · aikido.dev

Researchers Detail Gogs RCE, Push Authorization Bypass and Notebook XSS

Aikido details three Gogs flaws: path-traversal RCE (CVE-2026-52813), a Git push authorization bypass (CVE-2026-52810), and stored XSS in .ipynb rendering. The RCE is fixed in 0.14.3; the bypass remains exploitable through a reported incomplete fix.

Aug 19, 2026
Threat Research · huntress.com

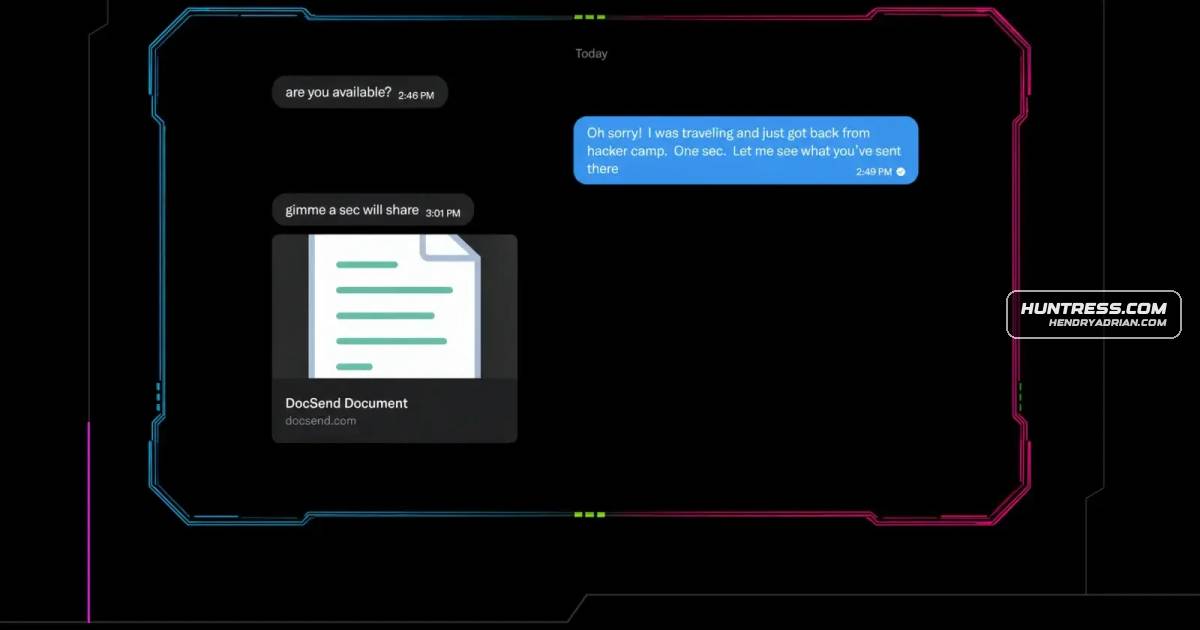
Post-DEF CON Phishing Lures Deliver AMOS Stealer, NetSupport RAT and Other Malware

Huntress detailed phishing lures using X DMs and malicious documents to target a researcher with malware for macOS and Windows. The researcher did not fall for the lures; analysis uncovered infostealing, remote access, wallet theft and traffic interception.

Aug 19, 2026
Threat Research · cloudsek.com

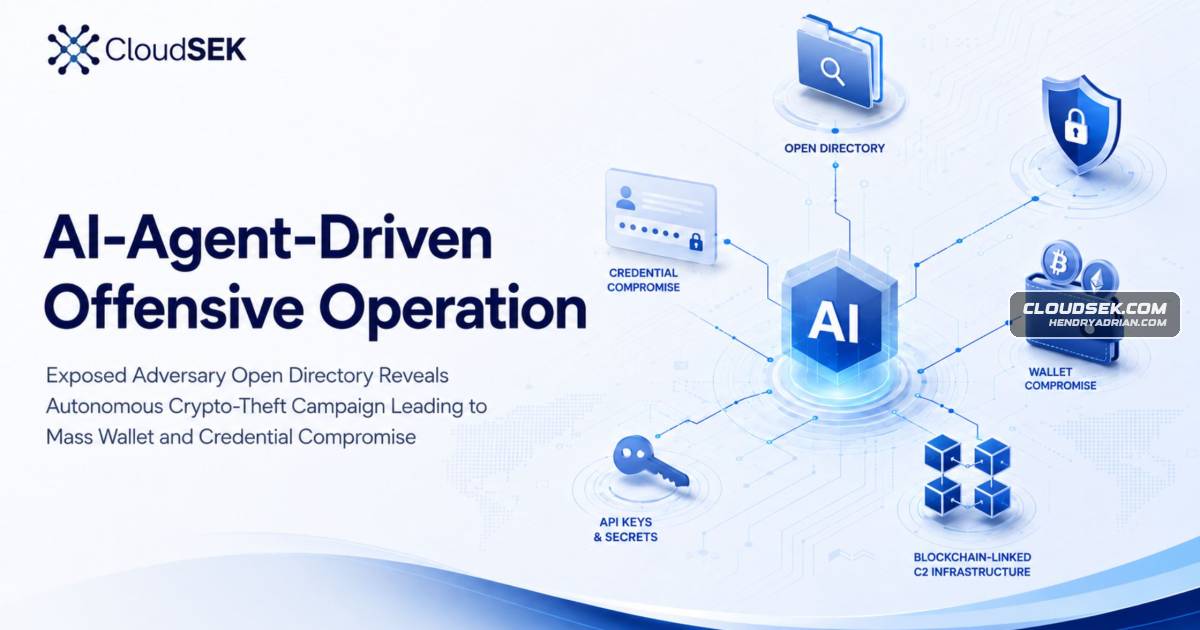
CloudSEK Finds AI-Agent-Driven Campaign Behind 12,000 WordPress Backdoors and Crypto Theft

CloudSEK traced mass WordPress compromises, crypto theft, and cryptojacking to an operator using AI coding agents. An exposed directory revealed the operation; its blockchain C2 project was tested locally but never deployed.

Aug 19, 2026
Threat Research · securitylabs.datadoghq.com

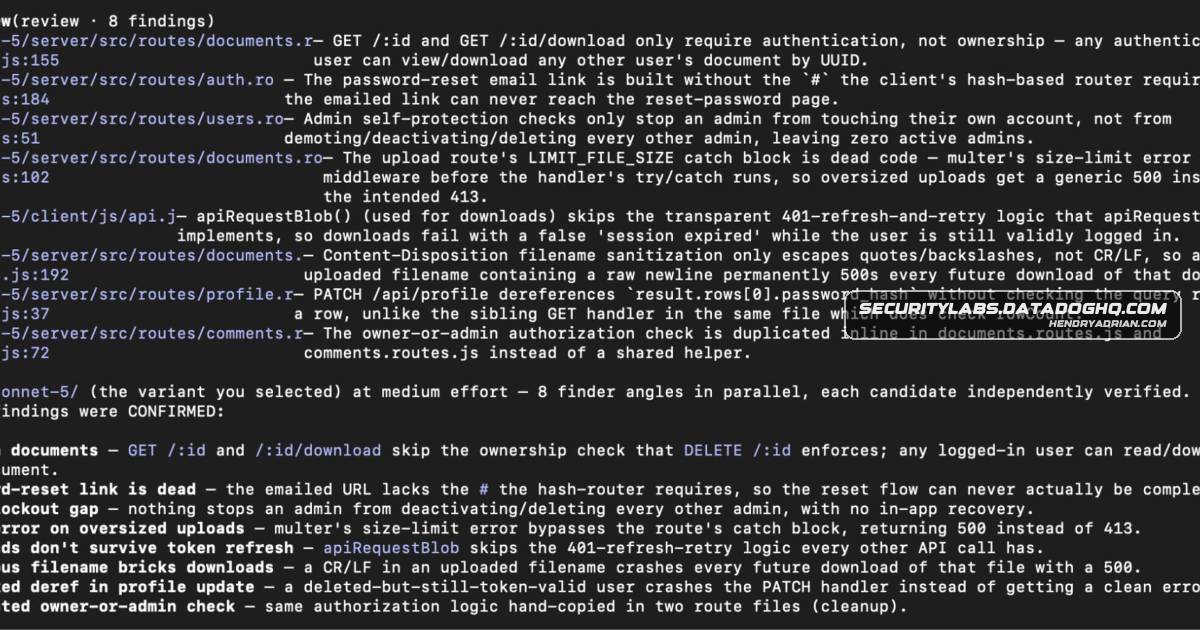
Testing AI Coding Agents Finds IDOR Vulnerabilities in All Six Generated Apps

A Datadog Security Labs experiment compared three coding models in plan and default modes. All six generated document portals had IDOR vulnerabilities, and the study found no meaningful correlation between plan mode and more secure code.

Aug 19, 2026
Threat Research · esentire.com

ErrTraffic ClickFix Campaigns Use Cruciferra Loader to Disable Security Tools

eSentire analyzed late-July 2026 ErrTraffic ClickFix campaigns that used fake CAPTCHA and BSOD prompts to run PowerShell and deploy Cruciferra, which can abuse a signed vulnerable driver to terminate security processes before loading the Remus stealer.

Aug 19, 2026
Threat Research · acronis.com

Grandoreiro Uses DLL Sideloading in a Campaign Targeting Mexico

Acronis details a Grandoreiro campaign observed in May 2026 that sideloads a malicious DLL through Duplicate Files Finder. The malware uses extensive anti-analysis checks, and telemetry shows the most activity in Mexico.

Aug 19, 2026
Threat Research · bleepingcomputer.com

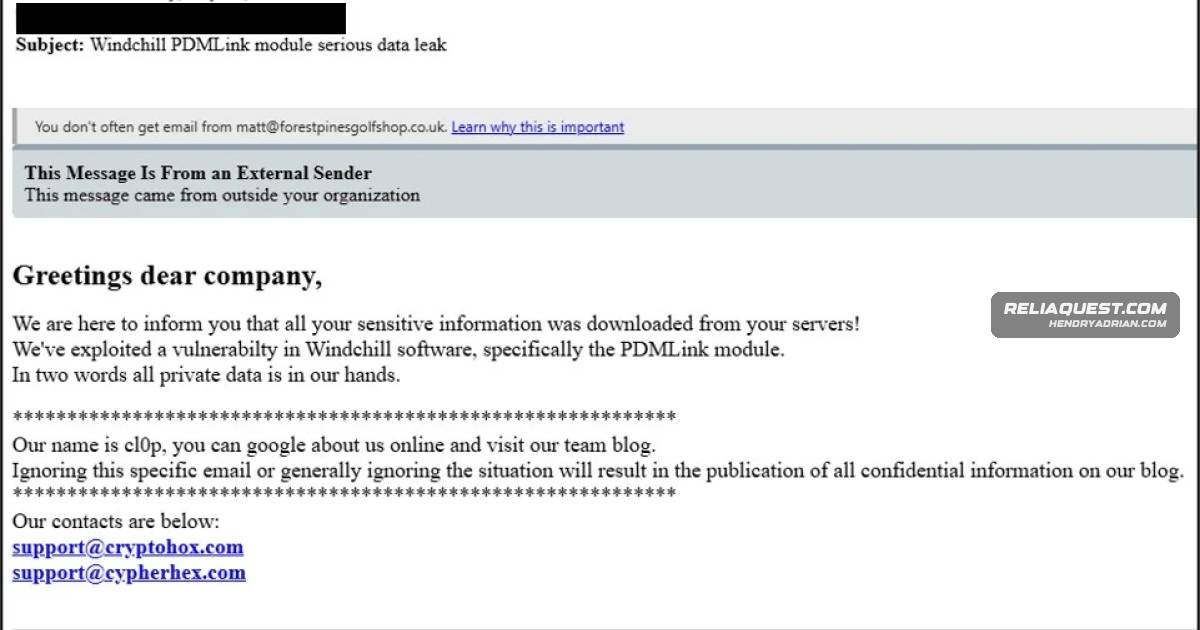
ReliaQuest Details Windchill Web Shell Likely Linked to Clop

ReliaQuest analyzed a Windchill-specific JSP web shell likely linked to Clop and deployed in attacks exploiting CVE-2026-12569. It can decrypt stored credentials, map vaults, retrieve or delete files, and execute Java code; patching and credential rotation are advised.

Aug 18, 2026
Threat Research · toxsec.com

Researchers Extract Hidden AI Reasoning and Secrets from Encrypted API Traces

Researchers found that compatible AI models could expose reasoning from encrypted API blocks, recovering credentials and personal information from public traces and demonstrating that replayed blocks could carry malicious instructions.

Aug 18, 2026
Threat Research · research.checkpoint.com

StopAndProtect Campaign Uses Thousands of Hacked WordPress Sites to Deliver Malware and Steal Data

Check Point researchers detail a campaign using compromised WordPress sites for ClickFix malware delivery, command and control, and stolen-data storage. The toolkit can encrypt files, steal data, spread across devices, and capture screenshots; logs showed more than 6,

Aug 18, 2026
Threat Research · reliaquest.com

Clop-linked Windchill Web Shell Steals Credentials and Maps Engineering Data

ReliaQuest analyzes a custom web shell highly likely linked to Clop, deployed after exploitation of the Windchill CVE-2026-12569 flaw. The implant can decrypt stored credentials, map files for theft, and run additional code in memory.

Aug 18, 2026
Threat Research · securityonline.info

Researchers Rebuild Tiangou Gateway and Find Technical Links to China’s Great Firewall

Researchers rebuilt Tiangou Secure Gateway from leaked code and examined how it detects and blocks circumvention tools. DNS-handling and TCP-reset similarities provide strong technical evidence of a link to Great Firewall components.

Aug 18, 2026
Threat Research · forcepoint.com

Researchers Detail ValleyRAT Campaign Using Signed Overwolf Binary to Sideload Malware

Forcepoint researchers dissected an India-focused ValleyRAT campaign using fake tax notices and a signed Overwolf executable to sideload a DLL; the malware runs in memory, persists via a logon task, and injects into svchost.exe.

Aug 18, 2026
Threat Research · seqrite.com

Operation QUICSILVER Uses Disguised VHDs to Target Myanmar Government Personnel

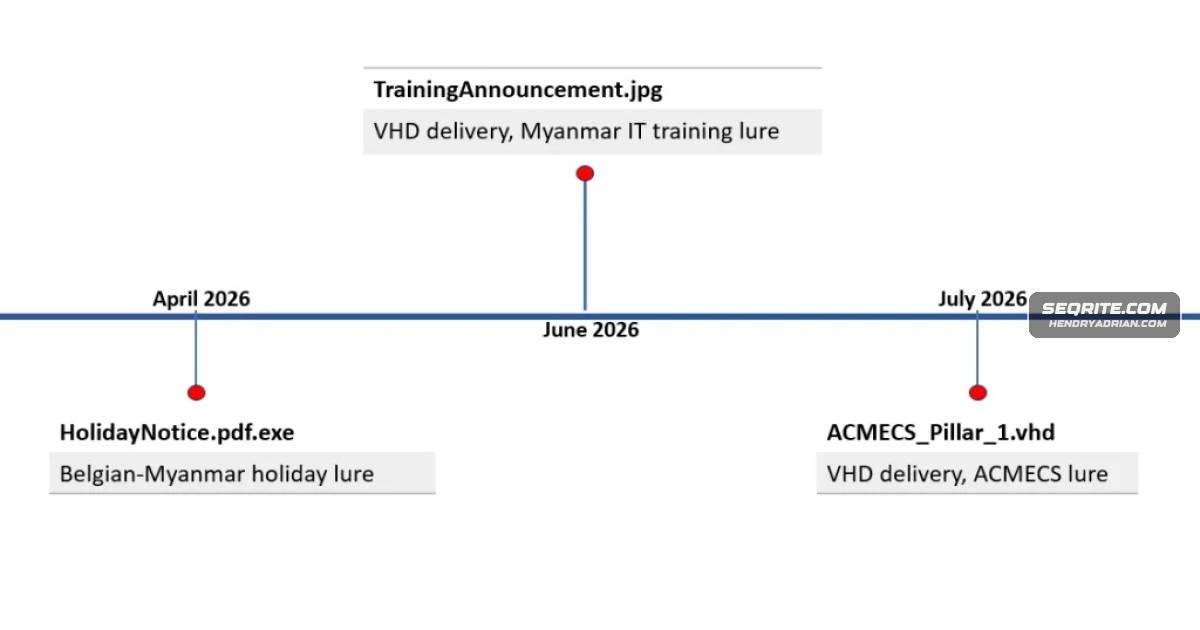
Seqrite details Operation QUICSILVER, targeting Myanmar government personnel with a disguised VHD lure and Go backdoor QUICAgent. The malware resolves C2 via Cloudflare Workers and uses QUIC with RC4 encryption; Seqrite assesses a China nexus with moderate confidence.

Aug 18, 2026
Threat Research · recordedfuture.com

CopyCop Impersonated Media and Iranian Military to Target Armenia’s Firebird AI Data Center

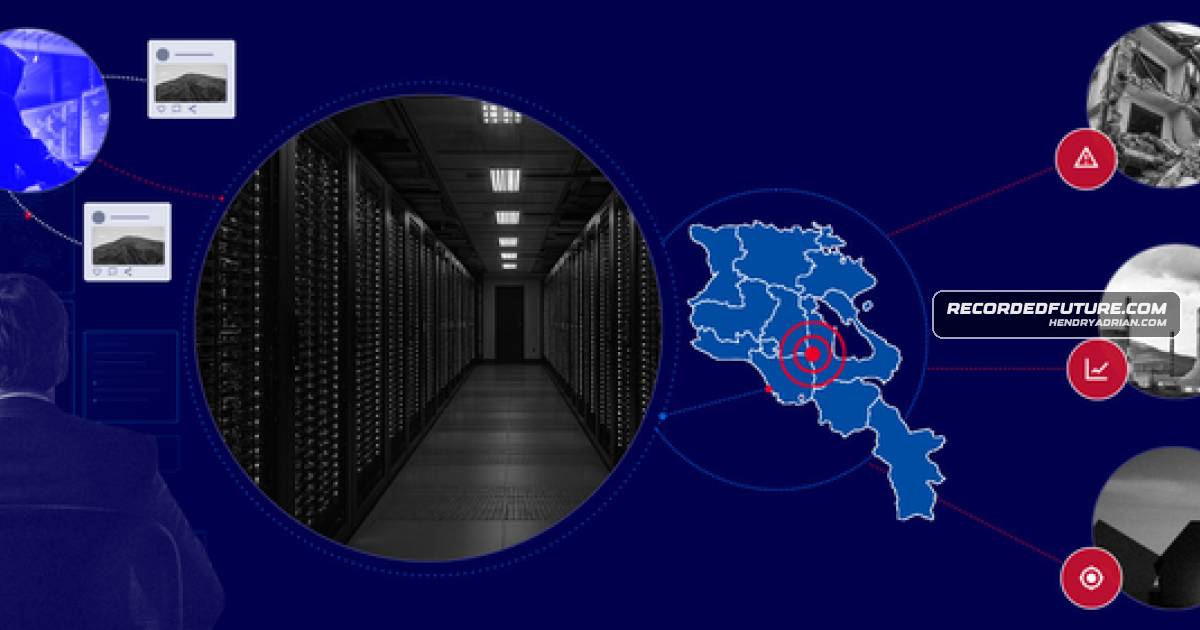
Recorded Future linked three CopyCop influence operations to fabricated claims about Armenia’s Firebird AI data center, including earthquake risks, power instability, and Iranian military targeting. The campaign’s third video reached more than 1.6 million views.

Aug 18, 2026
Threat Research · any.run

Mirage2FA Uses AiTM Phishing to Steal Microsoft 365 Sessions

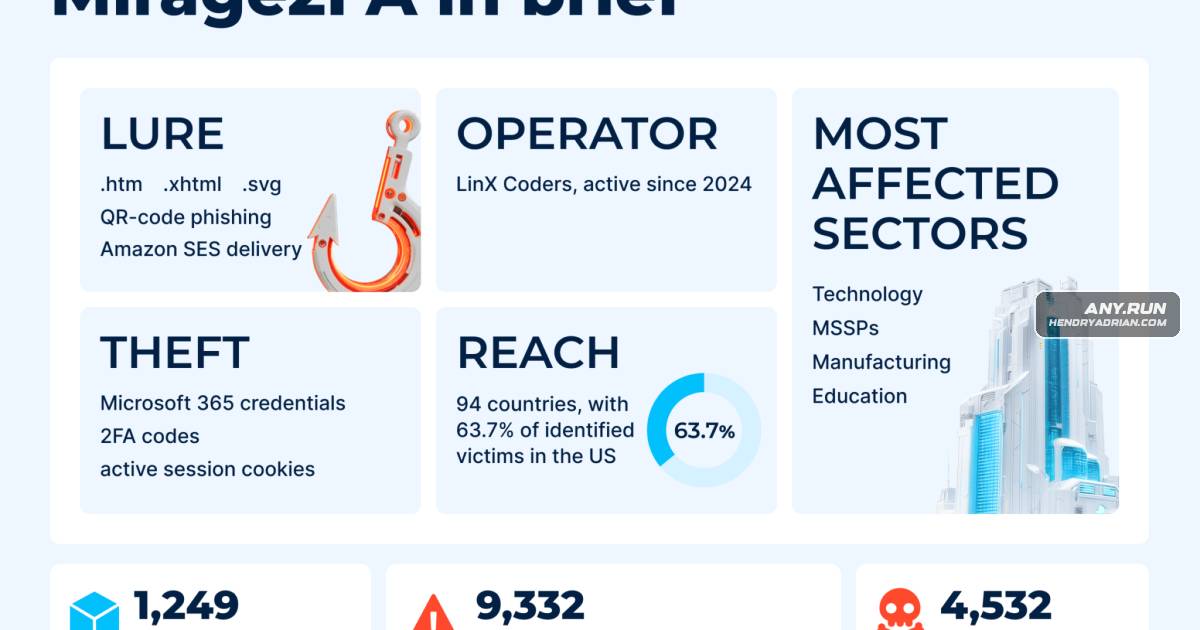
ANY.RUN researchers detail Mirage2FA, a phishing-as-a-service toolkit that uses browser-based attachments and an AiTM proxy to capture Microsoft 365 credentials and session cookies. Its dataset suggests 63.7% of identified victims were in the US.

Aug 18, 2026
PreviousPage 32 of 100 Next
© 2026 cyber.hendryadrian.com