Mirage2FA Uses AiTM Phishing to Steal Microsoft 365 Sessions
Summary
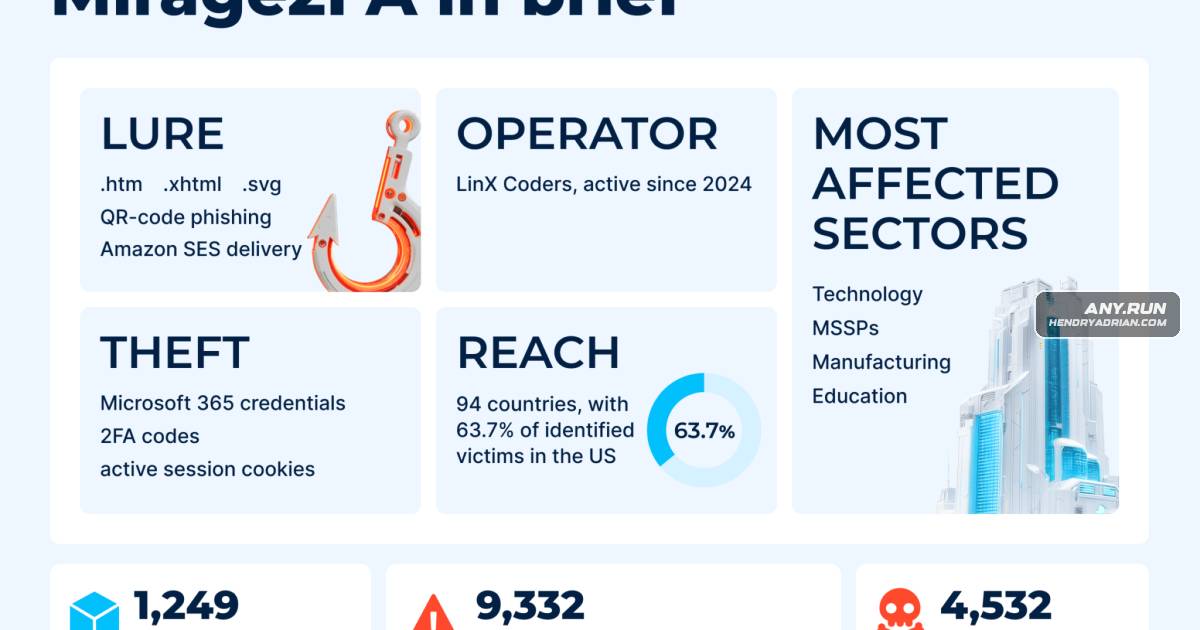
ANY.RUN researchers detail Mirage2FA, a phishing-as-a-service toolkit that uses browser-based attachments and an AiTM proxy to capture Microsoft 365 credentials and session cookies. Its dataset suggests 63.7% of identified victims were in the US.
Key points
- Mirage2FA uses fake Microsoft 365 login pages and a real-time AiTM proxy to capture credentials and 2FA codes, then steal authenticated session cookies.
- Delivery includes .htm, .xhtml, and .svg attachments, QR-code lures, and email distribution; the attack largely runs in the browser rather than using binary malware.
- Researchers observed obfuscated JavaScript, WebSocket activity, recipient-specific tokens, and recurring /xls/*.js loader paths.
- The dataset recorded 9,332 potential compromise events, including 4,561 session-cookie theft events. The figures are estimates, not independently confirmed compromises.
- ANY.RUN telemetry identified 2,885 victims in the US, or 63.7% of identified victims, with activity across 94 countries.
- The toolkit was observed from 2024 through July 2026 and attributed with high likelihood to the LinX Coders cluster.
- Recommended defenses include phishing-resistant MFA, behavioral detection of loader and WebSocket patterns, and revoking active sessions and tokens after suspected compromise.
Article Details
- Attack Vectors
- Phishing emails deliver malicious .htm, .xhtml, or .svg attachments, or links to QR-code lures; the article also reports distribution through Amazon SES.
- Opening an attachment runs a browser-based stager. Obfuscated HTML or SVG JavaScript retrieves Mirage2FA harvesting logic using /xls/<token>.js loader paths.
- An Adversary-in-the-Middle reverse proxy presents a fake Microsoft 365 login page and relays credentials and one-time 2FA codes to the legitimate service over WebSocket.
- The toolkit captures authenticated session cookies and sends them, along with credentials, to the operator panel; attackers can reuse the sessions to access Microsoft 365 accounts.
- Defensive Notes
- Block or quarantine .htm, .xhtml, and .svg attachments where possible; detect HTML smuggling, obfuscated JavaScript, suspicious QR-code lures, and browser-executed attachment behavior.
- Analyze suspicious files in an isolated environment and monitor for /xls/*.js loader requests, Base64-encoded email addresses in DNS labels, and outbound WebSocket connections following loader retrieval.
- Use phishing-resistant MFA such as FIDO2/WebAuthn or passkeys for high-risk users; consider shorter session lifetimes, token binding, and Continuous Access Evaluation in Microsoft Entra ID.
- After suspected session theft, revoke active sessions and tokens, review Microsoft 365 mail-forwarding rules and OAuth grants, and investigate activity performed through the compromised identity; a password reset alone may be insufficient.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | adp[.]pslcertlive[.]site | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | ans[.]rsxbenefits[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | ari[.]vslbertlive[.]info | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | ars[.]greebys[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | asvbtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | avsbtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | bezdelz[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | bns[.]baseasix[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | bsf[.]allmetreod[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | bverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | cementslabconstruction[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | cer[.]septey[.]shop | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | cer[.]verpox[.]shop | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | cureaveritax[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | cvs[.]pcvgtech[.]online | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | dezbelz[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | dverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | everster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | fureaveritax[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | fverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | gacorslot7d[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | galatasaraydanhaberler[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | gectech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | gverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | gztev[.]it[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | hpn[.]bandhiem[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | hverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | hvr[.]volatilesour[.]store | Mirage2FA C2/loader domain identified by ANY.RUN. |
| DOMAIN | hynutech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | implentedgucedirectory[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | intrugementslayerdocuservice[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | iverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | jscvbtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | jureaveritax[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | jverster[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | mettsoll[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | oectech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | office[.]avcbtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | office[.]pcvgtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pancincorp[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pavetech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pectech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pezbelz[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pureaveritax[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pvf[.]schwiessdoors[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pvs[.]schwiessdoors[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pxvbtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | pynutech[.]store | Listed as Mirage2FA loader infrastructure and in the article’s phishing-domain list. |
| DOMAIN | rfm[.]m3-bulders[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | rmf[.]diversesgs[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | rmf[.]m3-bulders[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | sopbtech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | svn[.]dpsindustrialsgroup[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | svr[.]schwiessdoors[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | user[.]cheacker[.]store | Mirage2FA C2/loader domain identified by ANY.RUN. |
| DOMAIN | ver[.]bandhiem[.]com | Mirage2FA C2/loader domain identified by ANY.RUN. |
| DOMAIN | ver[.]verpox[.]shop | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vezbelz[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vns[.]pigotnet[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vns[.]tvgsv[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vns1[.]pigotnet[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vrf[.]atskinsonel[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vrf[.]bereetro[.]it[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vrf[.]gavernova[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | vrf[.]iar0nline[.]com | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | wectech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | wes[.]cadsta[.]online | Listed by the article as a Mirage2FA phishing domain. |
| DOMAIN | zectech[.]store | Listed by the article as a Mirage2FA phishing domain. |
| IPV4 | 139[.]28[.]36[.]38 | Reported as an operator cross-bot test IP; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 141[.]95[.]59[.]233 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 146[.]70[.]195[.]104 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 181[.]214[.]165[.]173 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 185[.]174[.]100[.]20 | Reported as an operator cross-bot test IP; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 185[.]174[.]100[.]224 | C2/loader IP identified by ANY.RUN for Mirage2FA. |
| IPV4 | 185[.]174[.]100[.]76 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 185[.]199[.]103[.]116 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 185[.]91[.]122[.]32 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 192[.]52[.]166[.]55 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 199[.]233[.]237[.]30 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 209[.]205[.]192[.]6 | Reported as an operator infrastructure test IP; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 209[.]205[.]197[.]130 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 83[.]147[.]53[.]130 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 84[.]239[.]25[.]135 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 84[.]239[.]25[.]139 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 84[.]239[.]25[.]144 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 84[.]239[.]27[.]17 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 84[.]239[.]43[.]155 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 98[.]144[.]204[.]109 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 98[.]93[.]13[.]101 | Reported as a recent operator infrastructure test IP; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
| IPV4 | 98[.]98[.]79[.]35 | Reported among IPs used for operator infrastructure tests; the article notes the open-source IP/geo data may reflect VPN or spoofing. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe stagers obscure their logic using JavaScript obfuscation, including XOR/Base64/eval and hex-string decoding.T1027.006 · HTML SmugglingHTML smuggling is used in browser-based stagers to decode and execute content.T1071.001 · Web ProtocolsThe article associates reuse of stolen sessions to access Microsoft 365 with this technique.T1105 · Ingress Tool TransferThe stager retrieves remote harvesting logic through Mirage2FA loader paths such as /xls/<token>.js.T1111 · Multi-Factor Authentication InterceptionThe phishing flow captures the victim’s one-time 2FA code.T1204.002 · Malicious FileOpening a malicious attachment causes the browser to execute its embedded stager.T1539 · Steal Web Session CookieMirage2FA steals authenticated session cookies and stores them as Base64-encoded .txt dumps for reuse.T1557 · Adversary-in-the-MiddleAn AiTM reverse proxy relays the victim’s authentication to Microsoft 365 in real time.T1566.001 · Spearphishing AttachmentPhishing emails deliver malicious .htm, .xhtml, or .svg attachments.T1566.002 · Spearphishing LinkPhishing messages direct victims to links, including QR-code links.
People
Threat Actors
Vendors
Products
Microsoft 365HomeMalware AnalysisMirage2FA Hijacks Companies’ Microsoft 365 Sessions, with Over 4K Victims in the USMicrosoft Entra IDShorter session lifetimes, token binding, and Continuous Access Evaluation in Microsoft Entra ID can also reduce the window in which a stolen authenticated session remains useful.
Tools
Countries
CanadaVictim activity was also observed in India, Singapore, the United Kingdom, Canada, Saudi Arabia, South Africa, and other countries.IndiaVictim activity was also observed in India, Singapore, the United Kingdom, Canada, Saudi Arabia, South Africa, and other countries.Saudi ArabiaVictim activity was also observed in India, Singapore, the United Kingdom, Canada, Saudi Arabia, South Africa, and other countries.SingaporeVictim activity was also observed in India, Singapore, the United Kingdom, Canada, Saudi Arabia, South Africa, and other countries.South AfricaVictim activity was also observed in India, Singapore, the United Kingdom, Canada, Saudi Arabia, South Africa, and other countries.United KingdomVictim activity was also observed in India, Singapore, the United Kingdom, Canada, Saudi Arabia, South Africa, and other countries.United States2,885 victims, or 63.7% of the total, were located in the United States, while victim activity was recorded across 94 countries.
Industries
ConsultingConsulting EducationANY.RUN research shows that 63.7% of identified victims are in the US, with Technologies, Manufacturing, and Education among the most targeted industries.financeFraud and impersonation exposure: Compromised accounts can be used to target employees, customers, suppliers, or finance teams.HealthHealth ManufacturingANY.RUN research shows that 63.7% of identified victims are in the US, with Technologies, Manufacturing, and Education among the most targeted industries.MSSPsTechnology, MSSPs, and Manufacturing Face the Highest ExposureTechnologyMirage2FA phishing targets US companies in technology and manufacturingTelecommunicationsTelecommunications