cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · securityweek.com

Researchers Detail Encrypted Prompt Injections Against Grok and Gemini

Adversa AI researchers describe Cryptographic Context Injection, which uses encrypted prompts to evade AI safety filters. Their examples target Grok and Gemini; they say the attack’s success against Gemini had declined but may still be possible.
Aug 21, 2026
Threat Research · securityweek.com

iAuthFlow V2 May Use Passkeys to Retain Gmail Access After Password Resets

Abnormal researchers say iAuthFlow V2 may relay phishing authentication through an attacker-controlled browser and register a passkey, potentially preserving Gmail access after password resets. Their analysis is based on seller material, not malware testing.

Aug 21, 2026
Threat Research · bleepingcomputer.com

FTP Banners Used to Deliver E4del and PINHOLE Windows RATs

SOCRadar reports that attackers use FTP server banners as dead-drop resolvers to deliver E4del and PINHOLE RATs. The report details their infection routes, capabilities and evasion techniques, and says the activity continued through August 2026.

Aug 21, 2026
Threat Research · zimperium.com

ToxicPanda 2.0 Adds ADB Pairing, Lock-Screen Theft and Expanded Banking Targets

zLabs says ToxicPanda 2.0 targets financial apps across 16 countries, using Accessibility overlays to steal credentials. Its analysis details Wireless Debugging/ADB shell access, lock-screen credential theft, and delivery through Amazon AWS-hosted buckets.

Aug 21, 2026
Threat Research · securelist.com

Android Malware Uses Car Head-Unit Updaters to Build Proxy Botnet

Researchers traced a multi-stage Android malware infection to DoFun head-unit update software. Attributed with high confidence to MoYu Group, the malware enables ad fraud and proxy-botnet activity; the vendor says it fixed the distribution issues.

Aug 21, 2026
Threat Research · global.ptsecurity.com

FamousSparrow Deploys New SquawkDoor Backdoor and Updated SparrowDoor

Positive Technologies details FamousSparrow attacks in 2026 using new SquawkDoor and updated SparrowDoor backdoors, delivered through malicious LNK files and compromised websites displaying fake certificate prompts.

Aug 21, 2026
Threat Research · therecord.media

Bitdefender Links SilkParasite Campaign to China, Finds AI-Assisted Malware

Bitdefender reports that SilkParasite targeted government bodies across Central Asia for nearly a year, using seven malware families. Its investigation found spearphishing delivery, DriveSilkRAT’s Google Drive command channel, and evidence of AI-assisted development.

Aug 20, 2026
Threat Research · thehackernews.com

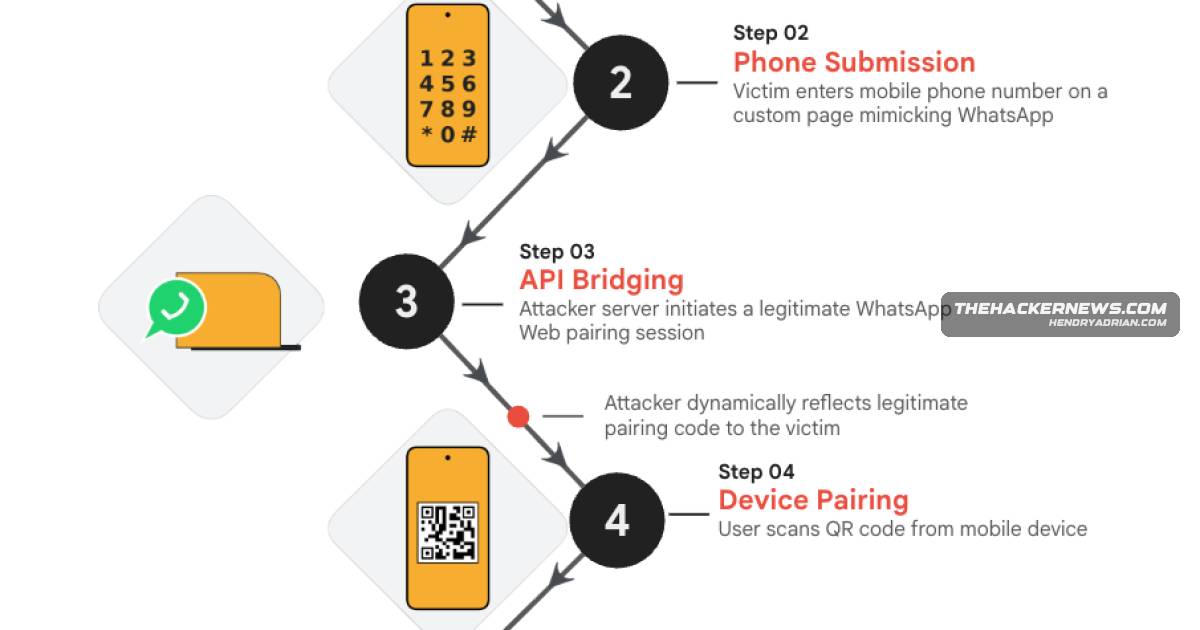
Google Details OAuth and WhatsApp Phishing by Suspected Russian Clusters

Google and other researchers describe suspected Russian clusters using OAuth, app-password and WhatsApp device-linking lures, alongside infostealers and malware, to steal tokens and expand access across academia, defense and government targets.

Aug 20, 2026
Threat Research · thehackernews.com

Malicious Rust Crate Releases Added a Build-Time Payload Through a Typosquatted Dependency

Three malicious Rust crate releases added a typosquatted dependency whose build script downloaded and ran a payload during compilation. The releases were removed within 86–107 minutes; RustSec reported no evidence they were used.

Aug 20, 2026
Threat Research · wiz.io

Malicious Rust Crates Deliver Backdoor Through Build Scripts

Three hijacked Rust crates introduced a typosquatted dependency whose build script downloads and runs a platform-specific backdoor. The crates were removed, and researchers report infrastructure overlap with campaigns attributed to North Korean actors.

Aug 20, 2026
Threat Research · socket.dev

Malicious Rust Crates Deliver Cross-Platform Backdoor During Builds

A supply-chain attack compromised three Rust crates, adding a typosquatted dependency that ran malware during Cargo builds. The backdoor targeted Linux, macOS and Windows; Rust removed the releases, and affected build hosts should be treated as compromised.

Aug 20, 2026
Threat Research · securityweek.com

Hunt.io Details Operation CameraSwarm and 14,530 Compromised Dahua Cameras

Hunt.io reports that Operation CameraSwarm compromised 14,530 Dahua cameras in Ukraine and Russia, using brute force and authentication bypasses to deploy a persistent backdoor. The report does not establish the operator’s motivation.

Aug 20, 2026
Threat Research · research.checkpoint.com

Researchers Show How Windows Defender’s BTR.sys Driver Can Be Abused to Disable Security Tools

Check Point researchers reverse-engineered Microsoft’s signed BTR.sys remediation driver and demonstrated that attackers with load-driver privileges can use it for kernel-level file and registry operations, including disabling security tools. No real-world abuse was||||

Aug 20, 2026
Threat Research · levelblue.com

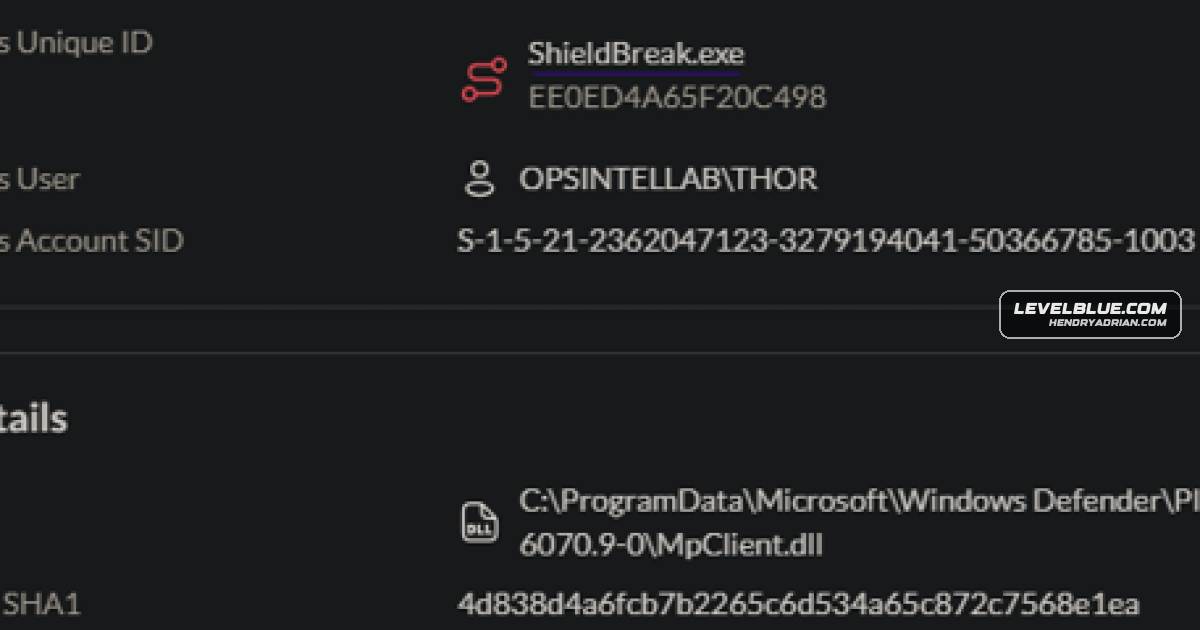
ShieldBreak PoC Uses Windows Defender Cleanup Race for SYSTEM Privilege Escalation

LevelBlue says it reproduced ShieldBreak on patched Windows 11 24H2 and Server 2025: a PoC that redirects Defender cleanup through a timing race to plant phoneinfo.dll, then triggers SYSTEM execution via QueueReporting.

Aug 20, 2026
Threat Research · silentpush.com

Researchers Link Peer2Profit to Astroproxy and Demonstrate DNS-Based Access to Internal Networks

Silent Push researchers confirmed Astroproxy resells Peer2Profit bandwidth and found its proxy network could reach internal resources when a DNS name resolved to an internal IP, despite a filter blocking direct internal-IP requests.

Aug 20, 2026
Threat Research · thehackernews.com

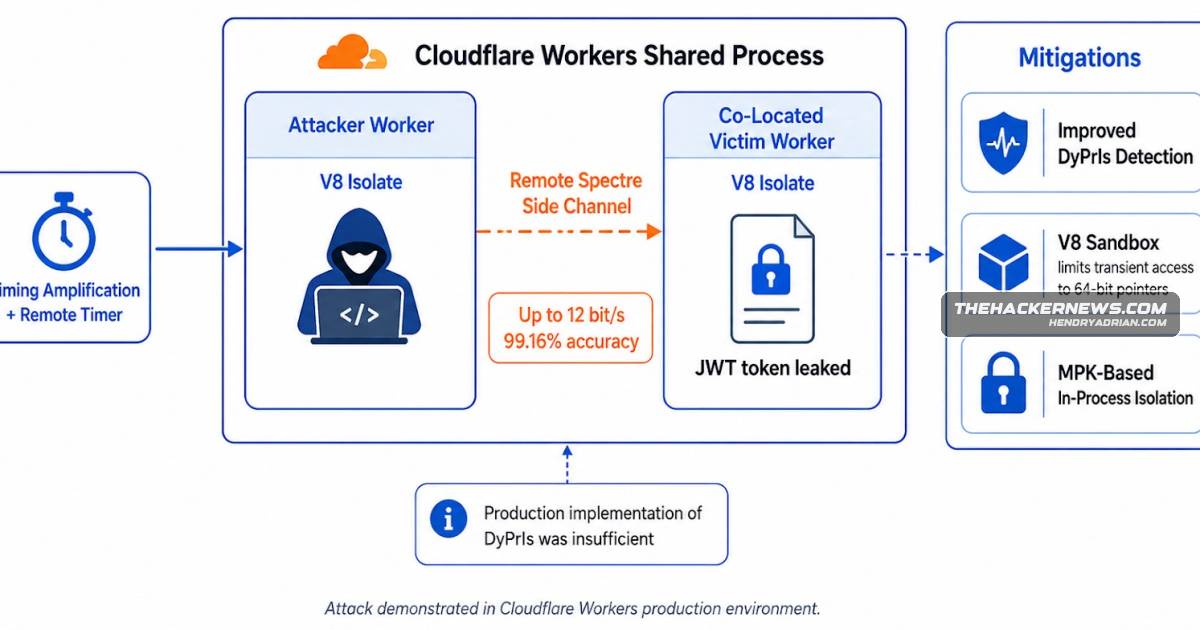
Researchers Demonstrate Remote Spectre Attack Recovering JWT from Cloudflare Workers

Researchers demonstrated a remote Spectre attack that recovered a deliberately planted JWT from a co-located Cloudflare Worker at up to 12 bits/s and 99.16% accuracy. Cloudflare says mitigations are deployed and it found no signs of exploitation.

Aug 20, 2026
Threat Research · aikido.dev

Malicious Dependency Compromises Three Popular Rust Crates, Deploys Infostealer

Aikido reports that malicious dependency proc-macro1 compromised append-only-vec, arrayref and internment, using build-time payloads to target browser credentials and wallet data and establish macOS persistence; the C2 uses 23.254.165.112.

Aug 20, 2026
Threat Research · stepsecurity.io

Rust Supply-Chain Attack Poisoned Three Crates With a Build-Time Dropper

A compromised maintainer account published poisoned arrayref, internment and append-only-vec releases that pulled in typosquatted Rust droppers, enabling code execution during builds. Step Security traced the attack and reproduced its outbound connection; the malicious1

Aug 20, 2026
Threat Research · threatfabric.com

Manic Android Malware Combines Banking Fraud, Spyware and Wi-Fi Mesh Relays

ThreatFabric details Manic, an Android malware family focused on Ukraine that steals credentials, spies on victims and remotely controls devices. It can also relay encrypted data through nearby infected phones when direct internet access is unavailable.

Aug 20, 2026
Threat Research · cloudsek.com

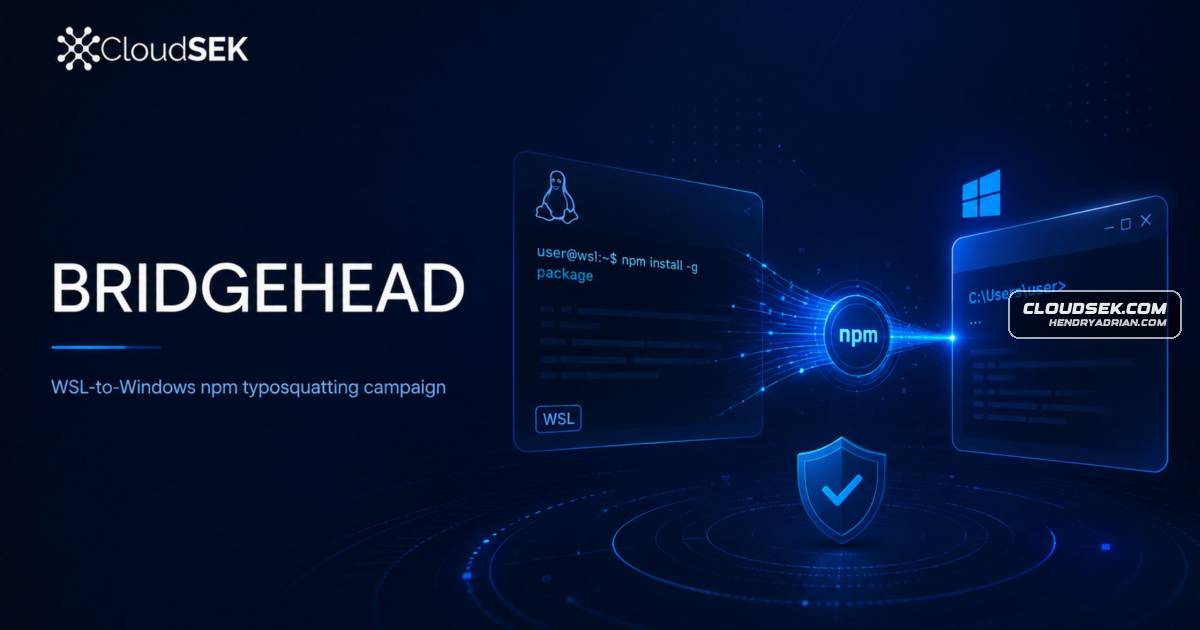
Npm Typosquatting Campaign Uses WSL to Deliver a Windows Crypto and Credential Stealer

CloudSEK analyzed 40 removed npm typosquatting packages that used WSL to deliver a Windows stealer targeting crypto wallets, browser data and Telegram sessions. The payload host was removed, but the C2 was still responding at the time of analysis.

Aug 20, 2026
Threat Research · securitylabs.datadoghq.com

N4D Linux Malware Abuses MCP Tools and Scans for Exposed Services

Datadog’s analysis of N4D’s 33.8-go-titan agent confirms MCP command-tool abuse, broad autonomous scanning, multiple Linux persistence methods, and controller reporting. The researchers provide indicators and defensive guidance.

Aug 20, 2026
Threat Research · cloud.google.com

Google Details Russian Espionage Clusters Abusing Authentication Flows to Target Individuals

Google tracks three suspected Russian espionage clusters targeting academics, diplomats, and defense-related individuals through app-password and OAuth phishing, device linking, and infostealer malware. It reports disrupting infrastructure and offers mitigation guidance

Aug 20, 2026
Threat Research · malwarebytes.com

41 Fake Download Sites Redirect Users to Download Studio

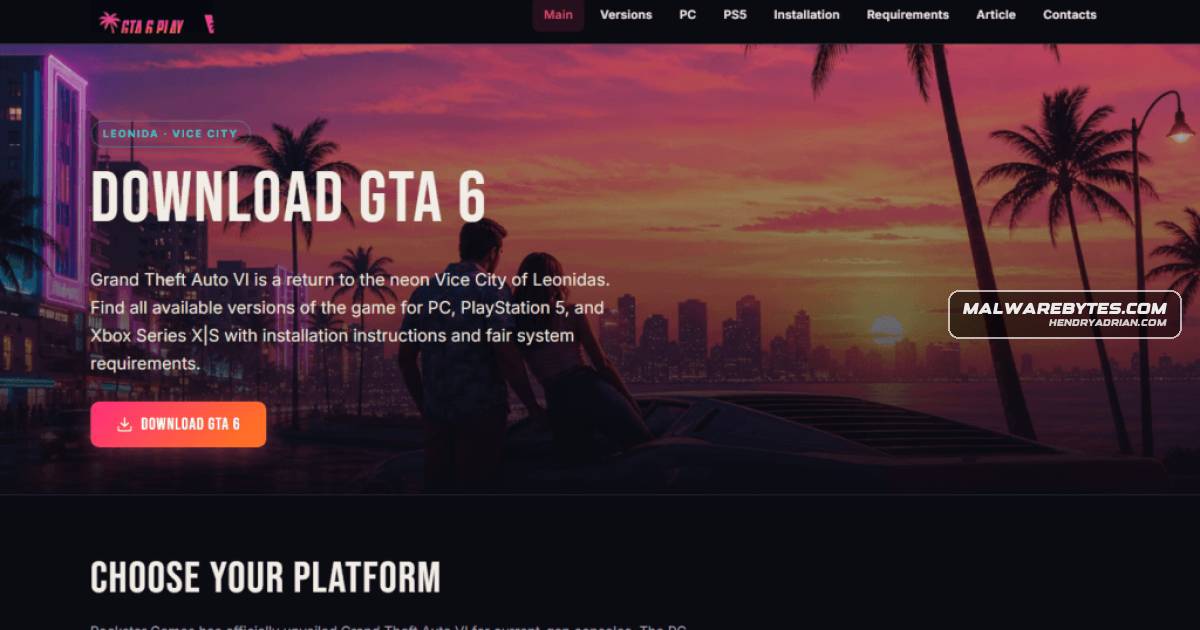
Malwarebytes found 41 fake game and software download sites using JavaScript click handlers and affiliate redirects to deliver a signed Download Studio installer. The installer was not shown to be malware, but its updater was abused in 2020.

Aug 19, 2026
Threat Research · bleepingcomputer.com

CameraSwarm Campaign Compromised 14,530 Dahua Cameras, Researchers Report

Hunt.io says the 35-day CameraSwarm campaign compromised 14,530 Dahua cameras using brute force, two vulnerabilities, and recovery codes. Attackers installed persistent p2pwn accounts; owners are advised to check devices and update firmware.

Aug 19, 2026
PreviousPage 31 of 100 Next
© 2026 cyber.hendryadrian.com