
Operation ASTERIX Uses Vishing and Fake Wallet Apps in Crypto Fraud Pipeline
Summary
Rapid7 reconstructed Operation ASTERIX from an exposed server, uncovering crypto account enumeration, coordinated phishing and vishing, fake wallet apps, Telegram exfiltration and AI-assisted malware development.
Key points
- An exposed web directory revealed source code, phone datasets, phishing panels, wallet malware and AI session logs, allowing Rapid7 to reconstruct the operation.
- Account-checking tools processed roughly 885,000 phone numbers; recovered logs recorded 43,066 Crypto.com account matches in a German dataset of 316,002 numbers.
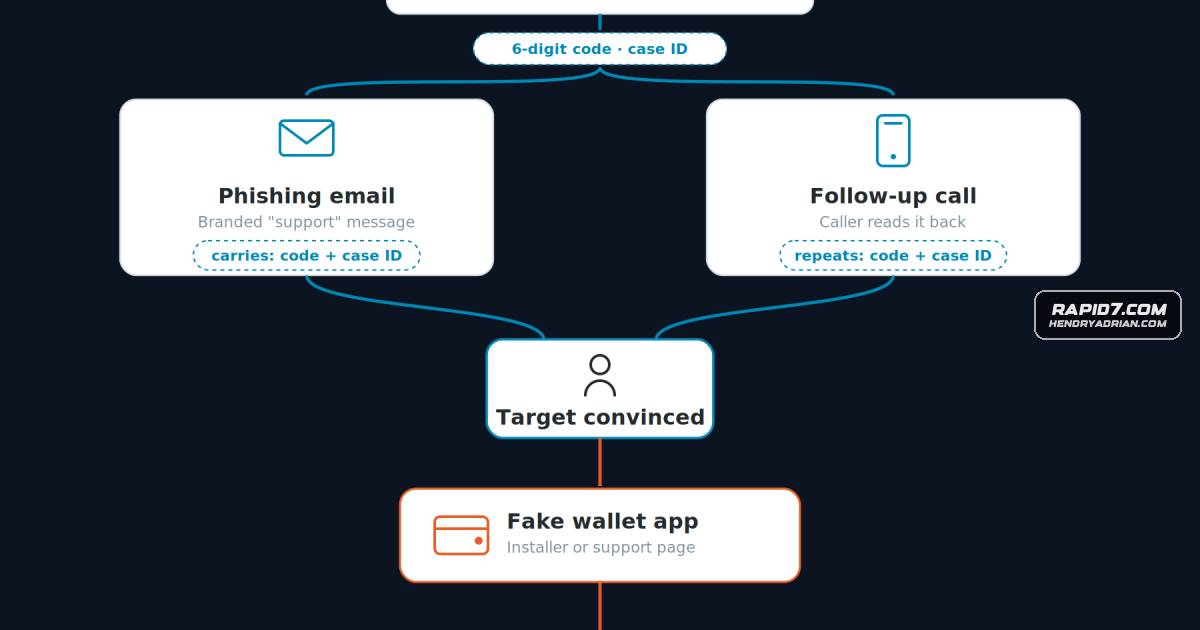
- Branded phishing emails and Asterisk-based calls shared fake support-case details to build trust and steer targets toward counterfeit Trezor Suite, Ledger Live and Exodus applications.
- The macOS Trezor impersonator monitored for the legitimate wallet, terminated it and displayed a counterfeit recovery form; collected phrases, passphrases and public IP addresses were sent to Telegram.
- macOS builds used LaunchAgents for persistence. Configuration errors left the recovered Windows Trezor build functioning only as a static seed-phrase collector, without its intended persistence or process-replacement behavior.
- A cloned Claude Code documentation page delivered an installer that installed a hidden fake Ledger Live application before running the legitimate Claude installer.
- Recovered artifacts showed AI-assisted coding, packaging and troubleshooting. The operator switched providers after refusals and attempted a Kimi jailbreak, but Rapid7 could not confirm whether it succeeded.
Article Details
- Attack Vectors
- Account-validation scripts checked bulk phone-number datasets against cryptocurrency exchanges, then enriched confirmed matches for targeted social engineering.
- Branded phishing emails generated fake support cases and verification codes that operators referenced during follow-up vishing calls.
- Counterfeit wallet applications collected recovery phrases and optional passphrases while impersonating legitimate wallet software.
- A cloned Claude Code documentation site substituted an installation command that deployed a fake Ledger Live application before installing legitimate Claude Code.
- The fake Ledger Live Windows build replaced copied cryptocurrency addresses with attacker-controlled addresses.
- A trojanized jquery.min.js in the Exodus build fetched a remote payload after installation.
- Defensive Notes
- The macOS samples used LaunchAgents, including com.trezormovement.agent.plist, io.trezor.agent.plist, and com.ledger.live.agent.plist, for persistence.
- The fake Trezor application scanned for the legitimate wallet every five seconds, terminated it, and displayed a counterfeit recovery interface.
- The recovered Windows Trezor build had an undefined platform configuration; its persistence, process-replacement, and second-stage execution paths were unreachable. It still functioned as a static recovery-phrase collector.
- Rapid7 Labs reported disclosing the infrastructure and findings to relevant providers and authorities, including Apple’s security team.
- Rapid7 stated that recovered indicators were ingested into Intelligence Hub to protect its customers.
- Recovered evidence did not establish whether the attempted Kimi jailbreak succeeded.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 36mcrypto[.]com | Campaign infrastructure domain also listed under beacon indicators. |
| DOMAIN | ledger[.]com[.]lv | Campaign domain identified as a phishing page. |
| DOMAIN | ledgerhelp[.]com | Campaign domain identified as a phishing page. |
| DOMAIN | macos-claude[.]com | Hosted cloned Claude Code documentation and a malicious installer delivering counterfeit Ledger Live. |
| DOMAIN | ses-noreply[.]com | Listed as email infrastructure associated with the phishing operation. |
| DOMAIN | xcjnrucne9xfvmci[.]com | Listed as a beacon domain in the operation's network indicators. |
| IPV4 | 31[.]57[.]35[.]88 | Listed as infrastructure supporting the fraud operation. |
| IPV4 | 82[.]25[.]35[.]200 | Listed as infrastructure supporting the fraud operation. |
| IPV4 | 82[.]25[.]35[.]77 | Listed as infrastructure supporting the fraud operation. |
| SHA256 | 0f2c7194f1f577e73460db9ec2e75fc0c7f845588cbd4246333b7a4fbec90d9f | macOS x64 launcher associated with the counterfeit Trezor application. |
| SHA256 | 4bee9affff9fa718a2c94f02ebe6a75143d4d461d291c2df9b769920fc927bf8 | Recovered kraken_checker artifact used in the operation's account-validation pipeline. |
| SHA256 | 7073b2a3a34525c5969921dd17ef1fa5607af92be78b3fc6129cdea73216691a | macOS arm64 launcher associated with the counterfeit Trezor application. |
| SHA256 | 961a398a5c71e837626b5fce68e44b14a5d220e3bd74a3d0ecd61a2762c38176 | Counterfeit Trezor Suite.exe Windows executable. |
| SHA256 | ba9d459169a303067a4fe36c8b8582a5ea023b9c270dafe89613bab840501b19 | Shared malicious app.asar payload in all three counterfeit Trezor Suite builds. |
| URL | hxxp[:]//136[.]0[.]213[.]184:1337/api/kraken-numio | Endpoint explicitly identified as Kraken checker C2. |
MITRE ATT&CK
T1027 · Obfuscated Files or Informationjavascript-obfuscator was used on js/connect.js, and the Ledger build contained control-flow flattening.T1036.005 · Match Legitimate Resource Name or LocationCounterfeit wallets used names, icons, and bundle identifiers resembling legitimate wallet applications.T1056.003 · Web Portal CaptureCounterfeit recovery forms captured wallet recovery phrases and optional passphrases.T1057 · Process DiscoveryThe macOS Trezor payload scanned the process list every five seconds for the genuine Trezor Suite.T1059.004 · Unix ShellThe cloned Claude Code page supplied a shell command that downloaded and executed the malicious installer.T1059.007 · JavaScriptElectron main-process JavaScript implemented recovery-phrase collection, process monitoring, and Telegram exfiltration.T1082 · System Information DiscoveryThe installer detected Arm versus Intel architecture, and wallet code checked process.platform for platform-specific behavior.T1204.002 · Malicious FileSocial engineering directed victims to manually install counterfeit wallet applications.T1543.001 · Launch AgentmacOS payloads installed LaunchAgents and loaded them with launchctl to run at login and relaunch the applications.T1564.001 · Hidden Files and DirectoriesThe malicious installer placed Ledger Live under a nested .SystemData directory and marked that directory hidden with chflags hidden.T1564.003 · Hidden WindowThe fake Trezor application created a transparent one-pixel Electron window hidden from the taskbar.T1567 · Exfiltration Over Web ServiceThe fake Trezor application sent recovery phrases, optional passphrases, and victim public IP addresses to Telegram bots.T1587.001 · MalwareThe operator built counterfeit Trezor Suite, Ledger Live, and Exodus applications on the exposed server.T1608.001 · Upload MalwareCounterfeit wallet archives, installers, and LaunchAgent files were staged on the operation's delivery infrastructure.T1657 · Financial TheftThe Ledger Live Windows build replaced copied cryptocurrency addresses with attacker-controlled addresses to redirect funds.
Vendors
AliyunThe operation also relied on Bright Data proxies for account validation, Aliyun DirectMail for outbound phishing emails, and three Telegram bots forwarding results to a command chat.Bright Datacountry prefixes and setting up automated checking scripts (“cdc checker v1” and “v2”) integrated with Bright Data proxy pools:Rapid7Rapid7 uncovered Operation ASTERIX, a cryptocurrency fraud campaign that used exposed infrastructure to stage phishing panels, vishing tools, fake wallet apps, and Telegram exfiltration while heavily relying on AI
Products
3CXThe recovered server included Asterisk and 3CX , a commercial business phone system often used by organizations for call routing and customer support.Asterisk#OperationASTERIX #TrezorSuite #LedgerLive #Exodus #Asterisk #Crypto.com #KrakenClaude CodeRecovered tooling included fake Trezor Suite, Ledger Live, Exodus, and a trojanized Claude Code installer used as a delivery path.Crypto.com#OperationASTERIX #TrezorSuite #LedgerLive #Exodus #Asterisk #Crypto.com #KrakenExodus#OperationASTERIX #TrezorSuite #LedgerLive #Exodus #Asterisk #Crypto.com #KrakenGitHub CopilotEvidence showed extensive AI-assisted development with GitHub Copilot, Claude Code, and Kimi, including code packaging, obfuscation, and troubleshooting.KimiEvidence showed extensive AI-assisted development with GitHub Copilot, Claude Code, and Kimi, including code packaging, obfuscation, and troubleshooting.Kraken#OperationASTERIX #TrezorSuite #LedgerLive #Exodus #Asterisk #Crypto.com #KrakenLedger LiveRecovered tooling included fake Trezor Suite, Ledger Live, Exodus, and a trojanized Claude Code installer used as a delivery path.Trezor SuiteRecovered tooling included fake Trezor Suite, Ledger Live, Exodus, and a trojanized Claude Code installer used as a delivery path.
Tools
cdc checker v1numbers (103K+POLAND.txt), formatting country prefixes and setting up automated checking scripts (“cdc checker v1” and “v2”) integrated with Bright Data proxy pools:cdc v2 checkerThe operator used Claude to manage and execute phone validation scripts, including “cdc checker v1” and “cdc v2 checker”, against targeted lead files, among them a cleaned list of 100,000 Polish numbers.javascript-obfuscator(‘javascript-obfuscator was used’ / ‘control-flow flattening’)kraken_checkerkraken_checker bulk-validates phone numbers against Kraken accounts.
Countries
BulgariaThe largest file included 316,002 German mobile numbers, with additional lists covering Hong Kong, Bulgaria, and directories referencing UK, US, Canadian fintech, and Ledger-related lists split across 54 countries.TheHong KongThe largest file included 316,002 German mobile numbers, with additional lists covering Hong Kong, Bulgaria, and directories referencing UK, US, Canadian fintech, and Ledger-related lists split across 54 countries.TheUnited KingdomGerman mobile numbers, with additional lists covering Hong Kong, Bulgaria, and directories referencing UK, US, Canadian fintech, and Ledger-related lists split across 54 countries.The operator ran the numbersUnited StatesGerman mobile numbers, with additional lists covering Hong Kong, Bulgaria, and directories referencing UK, US, Canadian fintech, and Ledger-related lists split across 54 countries.The operator ran the numbers through