cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · varonis.com

Varonis Details CoSnitch Flaws Enabling Data Theft Through Microsoft Copilot

Varonis describes CoSnitch, a chain of Microsoft Copilot vulnerabilities that could execute prompts from crafted links, access connected-app data, exfiltrate it, and alter persistent memory. Microsoft patched the flaws on August 18, 2026; Varonis reports no known in-the
Aug 18, 2026
Threat Research · hunt.io

Operation CameraSwarm Compromised More Than 14,500 Dahua Cameras, Hunt.io Finds

Hunt.io says an operator compromised more than 14,530 Dahua devices in 35 days using credential brute force, authentication bypasses and serial-based P2P relay access, leaving 1,923 cameras with a persistent backdoor.

Aug 18, 2026
Threat Research · wiz.io

Wiz Exploits GitHub Actions Injection Flaw to Access Snowflake’s Jira

Wiz found that an issue title could inject shell commands into a Snowflake GitHub Actions workflow and expose Jira credentials. Snowflake patched the workflow and rotated the token the same day; its audit found no third-party access.

Aug 17, 2026
Threat Research · huntress.com

Huntress Details Six-Stage MacSync Stealer and RAT Delivered Through Fake Claude Install Instructions

Huntress traced a MacSync infection from a Google sponsored result to a fake Claude install guide, detailing a six-stage macOS attack that steals credentials and crypto recovery phrases and installs a persistent RAT.

Aug 17, 2026
Threat Research · zscaler.com

C2Looper Backdoor Likely Linked to Ransomware Uses GitHub for C2

Zscaler analyzes C2Looper, a Rust backdoor likely used by a ransomware-related actor and possibly delivered through ClickFix. Its newer variant uses GitHub for C2 and adds commands for reconnaissance, file operations, and code injection.

Aug 17, 2026
Threat Research · opensourcemalware.com

StubMaker RubyGems Campaign Uses Embedded Malware to Steal Credentials and Wallet Data

StubMaker typosquatted RubyGems packages install a Windows infostealer that embeds later stages, steals browser credentials, wallets, seed phrases and Telegram data, then exfiltrates it.

Aug 16, 2026
Threat Research · bleepingcomputer.com

AmnesiaStealer Uses Cloned Chromium Profiles to Hijack macOS Browser Sessions

Jamf researchers analyzed AmnesiaStealer, a macOS infostealer distributed through ClickFix lures. Its stream_module clones Chromium profiles and uses CDP to let operators control victims’ authenticated browser sessions remotely.

Aug 16, 2026
Threat Research · bleepingcomputer.com

Evooo1Bot Linux Botnet Turns Gateway Devices Into SOCKS5 Relays

Fortinet researchers describe Evooo1Bot, a Mirai-based Linux botnet targeting internet-facing devices. It can relay traffic, steal credentials, brute-force SSH, and launch DDoS attacks; some embedded exploits reportedly fail.

Aug 15, 2026
Threat Research · gendigital.com

A 12 KB Windows Backdoor Hid Its C2 Domain in desktop.ini Whitespace

Researchers analyzed a custom 12 KB Windows backdoor found on one Windows 7 workstation. It encoded diagrtrack[.]com in UTF-16LE desktop.ini whitespace and persisted via WMI; the actor and initial access remain unknown.

Aug 15, 2026
Threat Research · securelist.com

HoneyMyte Adds Kernel-Mode Rootkit Capabilities to CoolClient Backdoor

Researchers analyzed a HoneyMyte CoolClient variant that deploys a signed Windows kernel driver to hide and protect malware processes, files and registry objects, and filter network data. PlugX preceded CoolClient in the observed Myanmar intrusion.

Aug 14, 2026
Threat Research · starknex.com

Starknex Finds Dataverse and Power Pages Misconfigurations Could Expose Sensitive Data

Starknex says guest access and overly broad Power Pages permissions can expose Dataverse user data and other records. It links Exfilsquad's breach claims to data consistent with these misconfigurations; 30.3% of surveyed sites remained vulnerable on Aug. 10, 2026.

Aug 14, 2026
Threat Research · securityweek.com

AmnesiaStealer macOS Malware Uses ClickFix to Steal Data and Control Browser Sessions

Jamf reports that ClickFix attacks use a fake GitHub download page to deliver AmnesiaStealer, which steals data from macOS systems and can provide interactive control of browser sessions.

Aug 14, 2026
Threat Research · bleepingcomputer.com

Huntress: Akira Affiliate Disabled EDR in Safe Mode but Failed to Encrypt Files

Huntress reports an Akira affiliate accessed a network through a SonicWall VPN without MFA, disabled defenses in Safe Mode, and stole credentials and files. The ransomware payload failed to run, but the data was used for extortion.

Aug 13, 2026
Threat Research · vulone.com

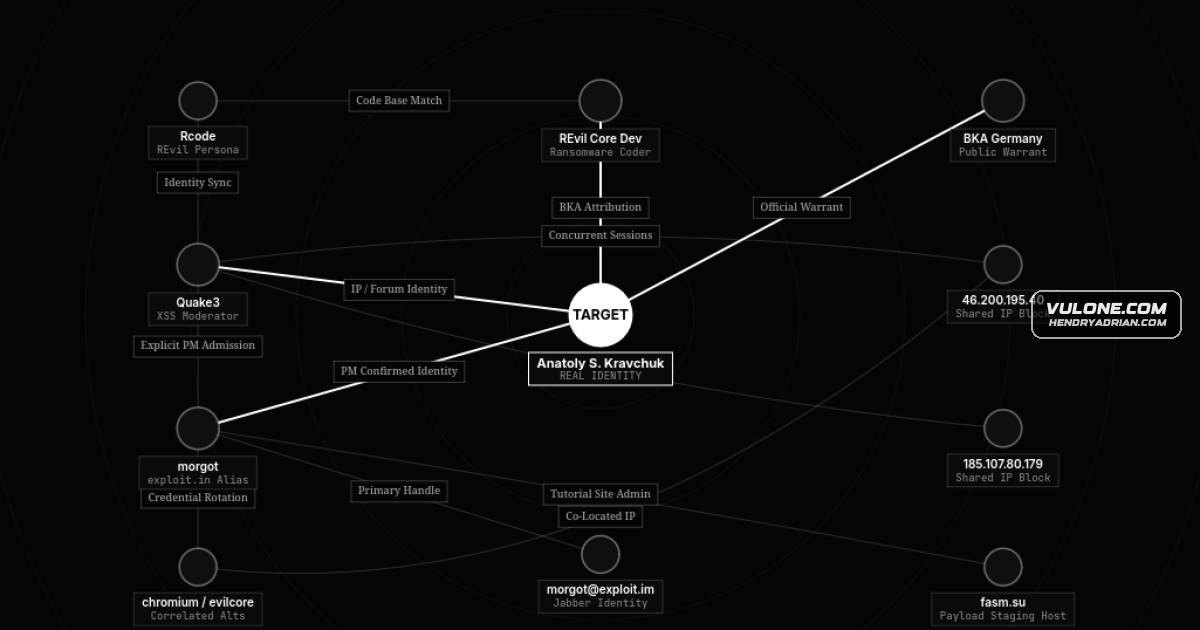
Investigation Links XSS Moderator Quake3 to Alleged REvil Developer Persona

An investigation links Quake3 to morgot, chromium and evilcore using forum messages and shared IP activity, then connects those identities to a REvil developer persona. The proposed real-world identification is assessed with moderate confidence.

Aug 13, 2026
Threat Research · bleepingcomputer.com

Jewelbug Targets Government Webmail While Running Crypto-Fraud Operations

Symantec reports Jewelbug compromised shared webmail used by 15 government tenants, stealing cookies, credentials and email data while running espionage tooling and AI-generated crypto-fraud campaigns from linked infrastructure.

Aug 13, 2026
Threat Research · sentinelone.com

Four AI-Agent Intrusions Highlight Persistent, Adaptive Attack Behavior

SentinelLABS analyzes four disclosures involving AI agents reaching external systems, arguing that their persistence and ability to adapt—not sophisticated tools—made them dangerous, and that defenders need stronger activity logging and control over agent identities and

Aug 13, 2026
Threat Research · feeds.fortinet.com

Evooo1Bot Linux Botnet Combines Mirai DDoS Code With Exploits and SOCKS Relays

Fortinet researchers detail Evooo1Bot, a Linux botnet exploiting vulnerabilities in internet-facing devices. It combines Mirai-derived DDoS, SSH brute forcing, credential sniffing, persistence, and SOCKS proxy capabilities.

Aug 13, 2026
Threat Research · feeds.fortinet.com

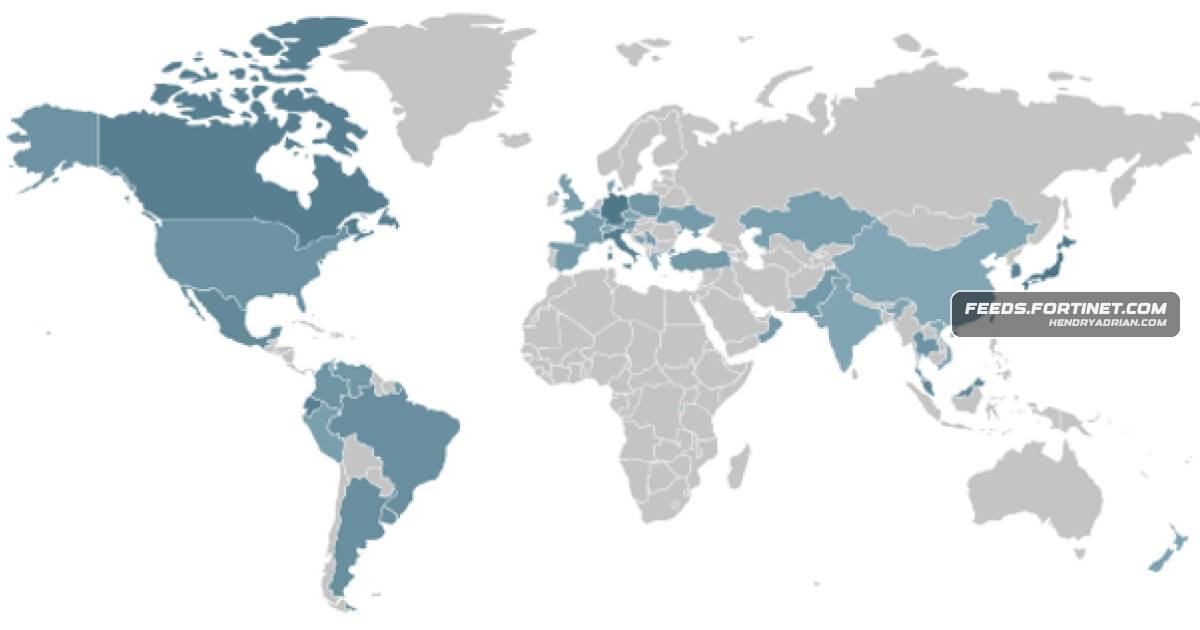
Fortinet Details Evooo1Bot, a Modular Linux Botnet Targeting Internet-Facing Devices

FortiGuard Labs analyzes Evooo1Bot, a Linux botnet observed exploiting vulnerabilities in internet-facing devices since July 2026. Its capabilities include DDoS, SSH brute force, credential sniffing, and SOCKS proxying.

Aug 13, 2026
Threat Research · infoblox.com

Infoblox Links Sable Squirrel’s $7M Expired-Domain Operation to Streaming, Gambling and Malware

Infoblox reports that Sable Squirrel uses more than 10,000 domains for illegal streaming, gambling promotion and malware command-and-control, including expired domains it estimates cost over $7 million.

Aug 13, 2026
Threat Research · infoblox.com

Expired malicious domains let three actors redirect compromised-site visitors to scams and malware

Infoblox details three actors that acquire expired malicious domains still embedded in compromised websites, then route visitors to advertising, scams, or malware using cloaking and traffic-distribution systems.

Aug 13, 2026
Threat Research · securelist.com

Kaspersky Details Armored Likho’s Telegram-Stealing and Audio-Surveillance Toolkit

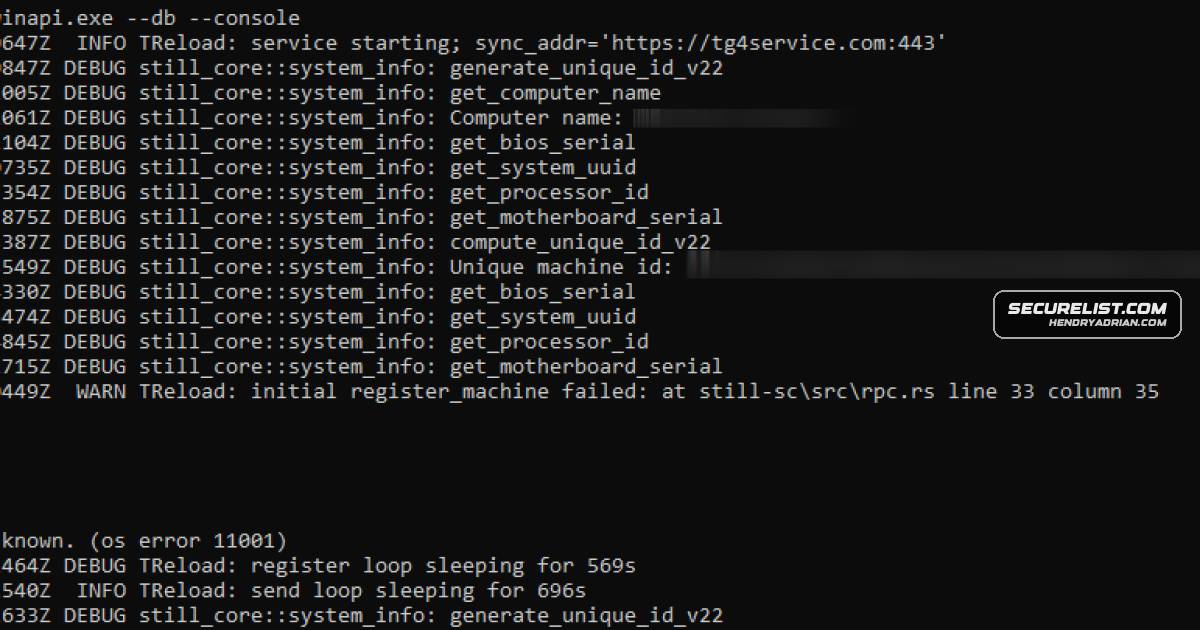
Kaspersky reports a Russia-focused campaign it attributes with high confidence to Armored Likho. A fake donation app deploys the Rust-based Still Toolkit, which steals Telegram data and records audio when speech is detected.

Aug 13, 2026
Threat Research · bleepingcomputer.com

Reco Links City-Forum Data Theft Campaign to Exposed Salesforce and ServiceNow Portals

Reco reports that the ongoing City-Forum campaign uses a single IP to retrieve data exposed to guest users through Salesforce and ServiceNow portals. The activity abuses permissive access, not product vulnerabilities.

Aug 13, 2026
Threat Research · bleepingcomputer.com

DeadLock ransomware uses blockchain to make infrastructure harder to disrupt

Microsoft says the DeadLock ransomware operation uses Polygon smart contracts, Session and Wasabi to manage victim communications and data leaks, complicating takedowns. Its report details encryption behavior and recommends endpoint and attack-surface defenses.

Aug 13, 2026
Threat Research · thehackernews.com

Researchers Extract Secrets by Replaying Encrypted AI Reasoning Blocks

Researchers replayed encrypted reasoning blocks across sessions and compatible models, decoding secrets from public agent logs and demonstrating hidden prompt injection. They say mitigations stopped tested attacks; vendors have not confirmed this. No in-the-wild attack

Aug 13, 2026
PreviousPage 33 of 100 Next
© 2026 cyber.hendryadrian.com