
Researchers Detail Hotel-Targeting Photo ZIP Campaign and Related Infrastructure
Summary
Microsoft reported a hotel-targeting campaign using photo-themed ZIPs and fake image shortcuts; the article adds DNS, WHOIS and email-domain analysis. The actors’ objective remains unclear, and 2,357 IPs were only potentially victim-associated.
Key points
- Microsoft said unknown actors targeted hospitality organizations in Europe and Asia, particularly Japan, since April 2026.
- Photo-themed ZIP archives contained fake image shortcut files that launched a chain involving obfuscated PowerShell, a Node.js implant and dual registry persistence.
- Reported post-compromise activity included C&C beaconing, forced shutdowns and PE payload compilation; the actors’ ultimate objective was unclear.
- Phishing emails reportedly used Calendly notification infrastructure and Google URL redirects with multilingual lures, in an attempt to bypass conventional email-authentication checks.
- Microsoft identified 78 network IoCs; the article’s analysis excluded one legitimate domain, leaving 77 for further analysis.
- Traffic data showed 2,357 unique IP addresses potentially associated with victims communicating with five IP IoCs.
- The article’s enrichment found 2,840 email-connected domains, of which 26 were identified as malicious by a cited threat-intelligence lookup.
Article Details
- Attack Vectors
- Photo-themed ZIP archives contained fake image shortcut files that users were tricked into launching.
- The infection chain used an obfuscated PowerShell script and a Node.js-based implant, with dual registry persistence.
- Multilingual phishing emails abused Calendly email notifications and Google URL redirects to attempt to bypass email authentication checks.
- Defensive Notes
- The researchers recommend supplementary investigation to corroborate entities identified as threats or malicious, since some may later prove harmless or require re-evaluation.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | haobbao[.]com | Listed among the campaign domain IOCs; the article reports historical domain-to-IP resolutions. |
| DOMAIN | heliosup[.]info | Listed among the campaign domain IOCs; the article reports historical domain-to-IP resolutions. |
| DOMAIN | lestresot[.]info | Listed among the campaign domain IOCs; the article reports historical domain-to-IP resolutions. |
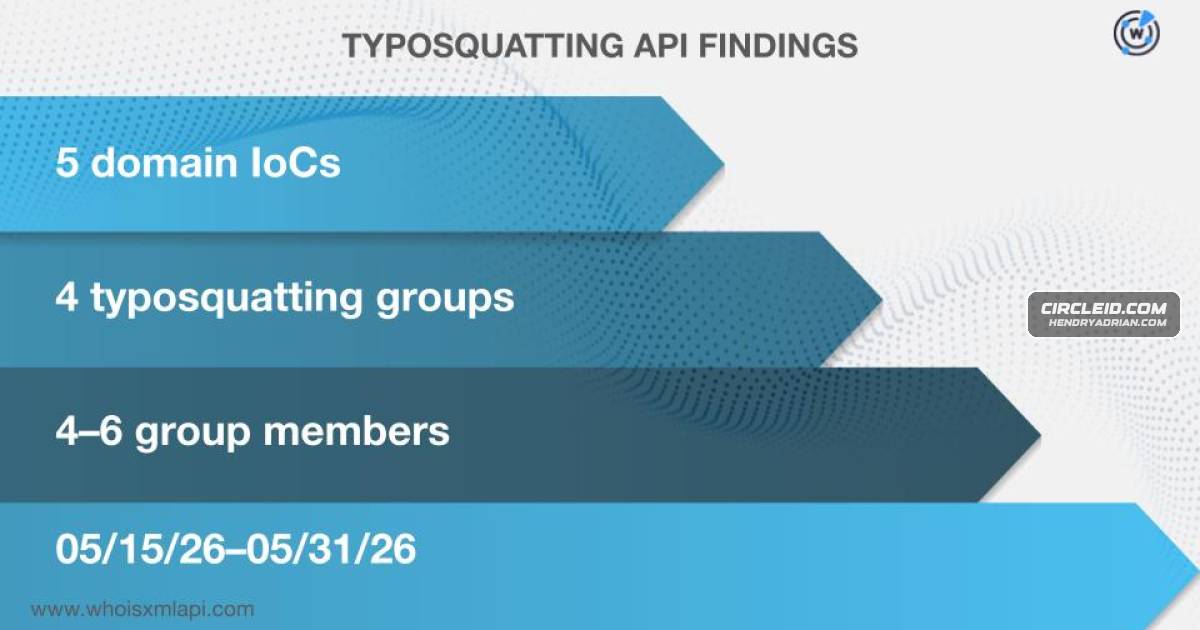
| DOMAIN | photo-132454[.]cfd | Identified as a campaign domain IOC and included in a typosquatting group. |
| DOMAIN | photo-21473[.]xyz | Identified as a campaign domain IOC and included in a typosquatting group. |
| DOMAIN | photo-26254[.]cfd | Identified as a campaign domain IOC and included in a typosquatting group. |
| DOMAIN | photo-26653[.]cfd | Listed as a network IOC associated with the photo ZIP campaign; two client IP addresses reportedly communicated with it. |
| DOMAIN | photo-26654[.]cfd | Identified as a campaign domain IOC and included in a typosquatting group. |
| DOMAIN | photo-26656[.]cfd | Listed as a network IOC associated with the photo ZIP campaign; two client IP addresses reportedly communicated with it. |
| DOMAIN | photo-27857[.]cfd | Listed as a network IOC associated with the photo ZIP campaign; two client IP addresses reportedly communicated with it. |
| DOMAIN | photo-8632454[.]cfd | Identified as a campaign domain IOC and included in a typosquatting group. |
| DOMAIN | photo-box[.]info | Listed among the campaign domain IOCs; the article reports historical domain-to-IP resolutions. |
| DOMAIN | visaphoto-secure[.]info | Listed among the campaign domain IOCs; the article reports historical domain-to-IP resolutions. |
| DOMAIN | zloapobikahy23[.]bond | Campaign domain IOC that the researchers said was likely registered with malicious intent. |
| IPV4 | 172[.]67[.]161[.]215 | Identified as one of the campaign's five IP IOCs; the article reports historical IP-to-domain resolutions for this address. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe campaign used an obfuscated PowerShell script to conceal behavior.T1059.001 · PowerShellAn obfuscated PowerShell script was used in the initial execution chain.T1204.002 · Malicious FileUsers were tricked into launching fake image shortcut files inside photo-themed ZIP archives, starting the infection chain.T1547.001 · Registry Run Keys / Startup FolderThe article reports dual registry persistence on infected devices.T1566.002 · Spearphishing LinkMultilingual phishing emails used links, including Google URL redirects, to deliver campaign lures.T1583.001 · DomainsThe campaign investigation identified numerous domain IOCs, including domains in typosquatting groups and one likely registered with malicious intent.
Vendors
CalendlyThe threat actors abused Calendly email notifications and Google URL redirects to send multilingual phishing emails and evade authentication checks through authentication laundering.GoogleThe threat actors abused Calendly email notifications and Google URL redirects to send multilingual phishing emails and evade authentication checks through authentication laundering.