Android Head-Unit Malware Abuses DoFun Updater for Ad Fraud and Proxy Botnet
Summary
Kaspersky says malware abuses DoFun Android head-unit updates via TWCore to install JarService for ad fraud, device-data collection and proxy-botnet activity. It attributes the campaign with high confidence to MoYu Group and says the distribution issue was addressed.
Key points
- Kaspersky discovered malware targeting DoFun-powered Android head units and described this as the first documented infection chain tailored to these systems.
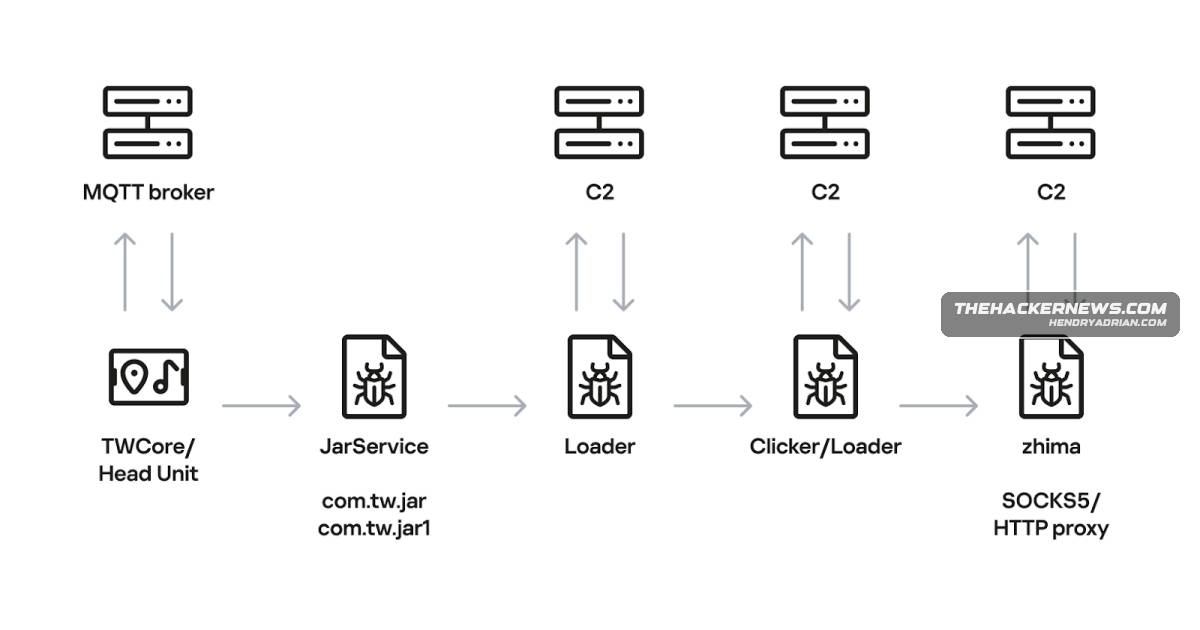
- The malware abuses the TWCore system app’s software-update mechanism to deliver the JarService dropper.
- The hidden payload checks in to its command-and-control service every 90 minutes by default and sends device and configuration information.
- Its commands can display ads, conduct ad fraud, make HTTP requests, open links, and download additional code.
- The operators reportedly use the http and loadlib2 commands to retrieve zhima, a reverse-proxy module.
- Kaspersky attributes the activity with high confidence to MoYu Group and links it to the BADBOX ecosystem.
- Following responsible disclosure, the issue enabling abuse of the software-distribution mechanism was addressed.
Article Details
- Attack Vectors
- The malware abuses the built-in TWCore update mechanism on DoFun-powered Android head units to deliver the JarService dropper.
- JarService launches a loader that sends device information to an attacker server, which responds with a link to the next-stage payload.
- The installed malware checks in with its C2 endpoint over HTTP every 90 minutes by default and can receive updated C2 configuration and commands.
- The malware can download additional modules, including the zhima reverse proxy module, and use commands to display ads and commit ad fraud.
- Defensive Notes
- Following responsible disclosure, the issue enabling abuse of the software distribution mechanism was addressed.
- The article warns that automotive platforms require robust protection against malware.
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryThe malware collects network-related details, including the connected Wi-Fi network identifier and MAC address.T1059.007 · JavaScriptA malware command can open a link in WebView and execute JavaScript within it.T1071.001 · Web ProtocolsThe malware uses HTTP POST requests to send device information and check in with its C2 endpoint.T1082 · System Information DiscoveryThe malware collects device details including the model and display resolution.T1105 · Ingress Tool TransferThe malware downloads the next-stage payload and additional modules, including zhima.T1496 · Resource HijackingThe malware supports ad fraud and proxy botnet operations using infected head units.
People
Threat Actors
Malware
BADBOXThe campaign, linked to the MoYu Group and BADBOX activity, supports ad fraud and proxy botnet operations while stealing device details and fetching additional modules like zhima.JarService#DoFunzhimaThe campaign, linked to the MoYu Group and BADBOX activity, supports ad fraud and proxy botnet operations while stealing device details and fetching additional modules like zhima.