Fake GTA 6 Demo Sites Deliver Vidar Infostealer, Malwarebytes Finds
Summary
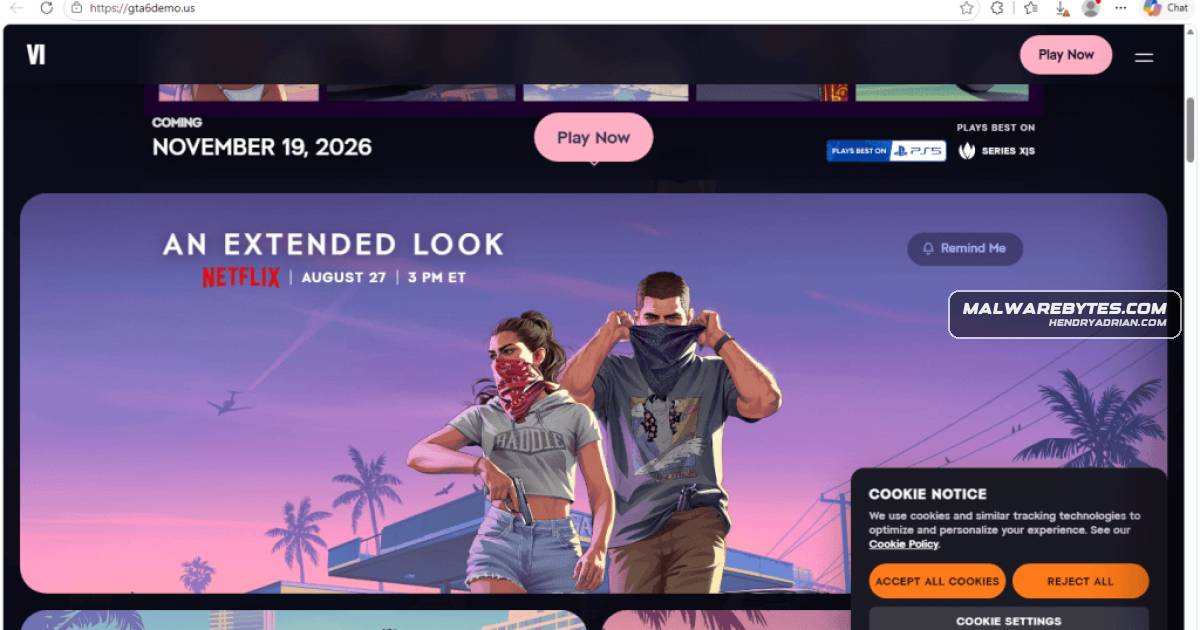
Malwarebytes analyzed fake GTA 6 demo sites delivering Vidar, which targets browser credentials and session cookies. The sample launched installed browsers to access protected data and used social-media profiles to retrieve infrastructure.
Key points
- Fake sites impersonating Rockstar used “Play Now” links to deliver gta6_installer.exe, a 1.1 MB file identified as the Vidar infostealer.
- The sample targeted saved passwords, session cookies, browsing history, autofill data, and FTP credentials across 19 browsers and related applications.
- During analysis, Vidar launched installed Chrome, Edge, and Firefox browsers in headless mode with temporary user-data directories to access protected browser data.
- Stolen session cookies may let attackers reuse authenticated sessions without repeating the usual login process, potentially bypassing 2FA prompts depending on the service.
- The sample used profile URLs on Telegram, Pinterest, and Steam Community as dead-drop resolvers; analysts also observed connections to attacker infrastructure.
- Malwarebytes reported no persistence mechanism in the sample and said it blocks the malicious sites and associated infrastructure.
- For suspected infection, the article advises scanning the device, changing important passwords from a clean device, and revoking active sessions.
Article Details
- Attack Vectors
- Fake websites impersonating Rockstar Games appeared in search results and used deceptive “Play Now” buttons to deliver gta6_installer.exe.
- The 1.1 MB executable was the Vidar infostealer, which collected saved browser passwords, session cookies, browsing history, autofill data, and FTP credentials.
- Vidar used attacker-controlled profiles on Telegram, Pinterest, and Steam Community as dead-drop resolvers to retrieve infrastructure destinations.
- The sample launched installed Chrome, Edge, and Firefox executables in headless mode with temporary user-data directories to access browser data, then deleted those directories.
- The sample sent multipart POST requests to attacker infrastructure and established a TLS connection to another observed attacker-controlled host.
- Defensive Notes
- Verify game downloads through the publisher’s official website or official store pages; do not trust unofficial demos, leaked builds, search results, or copied branding.
- Treat an unusually small game installer as suspicious; the malicious executable described in the article was 1.1 MB.
- If the installer was run, scan the affected computer with a trusted security product and change important passwords from a clean device.
- Revoke active sessions or use account options such as “sign out everywhere”; changing passwords alone may not invalidate stolen sessions.
- Review accounts for unfamiliar devices, recovery details, forwarding rules, and authorized applications, and monitor for unusual activity.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | bib[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | bob[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | brr[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | ges[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | gta6demo[.]asia | Fake GTA 6 distribution site identified as part of the campaign. |
| DOMAIN | gta6demo[.]eu | Fake GTA 6 distribution site identified as part of the campaign. |
| DOMAIN | gta6demo[.]us | Fake GTA 6 distribution site identified as part of the campaign. |
| DOMAIN | ket[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | ket[.]sm188daftar[.]mom | Attacker infrastructure contacted by the sample over TLS. |
| DOMAIN | kra[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | ljr[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | m1duusp[.]me | Domain listed among attacker-controlled Vidar dead-drop resolver sources. |
| DOMAIN | nhg[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | rex[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | rockstar-gta-6[.]com | Fake distribution site impersonating Rockstar Games and associated with malware delivery. |
| DOMAIN | ses[.]1001gacor[.]org | Attacker infrastructure that received multipart POST requests from the sample. |
| DOMAIN | sii[.]11gokil[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | sii[.]sm188dnsx[.]top | Listed as additional Vidar infrastructure. |
| DOMAIN | sto[.]1001gacor[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | tax[.]11gokil[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | tax[.]sm188dnsx[.]top | Listed as additional Vidar infrastructure. |
| DOMAIN | zaf[.]11gokil[.]org | Listed as additional Vidar infrastructure. |
| DOMAIN | zaf[.]sm188dnsx[.]top | Listed as additional Vidar infrastructure. |
| SHA256 | a8f19d598e6a49d8510d73d41fc445246755ed321c2f76985a463a9fef537eb0 | SHA-256 hash of the malicious gta6_installer.exe Vidar sample. |
MITRE ATT&CK
T1005 · Data from Local SystemThe sample collected locally stored browsing history, autofill data, and browser profile information.T1070.004 · File DeletionAfter using temporary browser directories, the malware issued commands to delete them.T1071.001 · Web ProtocolsThe sample used web traffic, including multipart POST requests and a TLS connection, to communicate with infrastructure.T1102.001 · Dead Drop ResolverVidar retrieved destination information from attacker-controlled profiles on Telegram, Pinterest, and Steam Community.T1105 · Ingress Tool TransferThe fake download flow delivered the Vidar executable gta6_installer.exe.T1119 · Automated CollectionVidar searched browser profiles and client directories for stored credentials and other data.T1204.001 · Malicious LinkVisitors could follow the fake sites’ “Play Now” links to reach the malicious download.T1204.002 · Malicious FileVictims who ran the supposed GTA 6 installer executed the malicious file.T1539 · Steal Web Session CookieThe infostealer collected session cookies that could allow reuse of authenticated browser sessions.T1555.003 · Credentials from Web BrowsersVidar targeted saved passwords and login details stored by browsers.T1566 · PhishingFake Rockstar-branded sites and deceptive download prompts lured visitors into the malware delivery flow.T1583.001 · DomainsThe campaign used fake GTA 6 distribution domains to host impersonation sites and malware delivery pages.
Malware
Products
BraveOur analysis showed 19 browser targets, including Chrome, Edge, Firefox, Brave, Opera, and Vivaldi.CometIt also searched Thunderbird profile directories and targeted Perplexity’s Comet browser and the WebView2 browser embedded inside Roblox Studio.Edgelegitimate installed browser binaries to access protected browser data (‘It launched the actual Chrome, Edge, and Firefox executables installed on the system’).Google Chromelaunched legitimate installed browser binaries to access protected browser data (‘It launched the actual Chrome, Edge, and Firefox executables installed on the system’).GTA 6Fake Rockstar sites are using hype around GTA 6 leaks and the upcoming Extended Look to push a malicious gta6_installer.exe that installs the Vidar infostealer.Mozilla Firefoxinstalled browser binaries to access protected browser data (‘It launched the actual Chrome, Edge, and Firefox executables installed on the system’).Mozilla ThunderbirdIt also searched Thunderbird profile directories and targeted Perplexity’s Comet browser and the WebView2 browser embedded inside Roblox Studio.OperaOur analysis showed 19 browser targets, including Chrome, Edge, Firefox, Brave, Opera, and Vivaldi.Roblox StudioIt also searched Thunderbird profile directories and targeted Perplexity’s Comet browser and the WebView2 browser embedded inside Roblox Studio.VivaldiOur analysis showed 19 browser targets, including Chrome, Edge, Firefox, Brave, Opera, and Vivaldi.WebView2It also searched Thunderbird profile directories and targeted Perplexity’s Comet browser and the WebView2 browser embedded inside Roblox Studio.