BengalSEO Uses SEO Poisoning and MayaBot to Drive Malware and Tech-Support Scams
Summary
The DFIR Report details BengalSEO’s SEO-poisoning operation, which uses malicious lure pages and traffic filtering to deliver MayaBot malware or direct victims to tech-support scams.
Key points
- The researchers attribute the operation, with high confidence, to individuals and IT service providers in Rajasthan, India, and say it has operated since at least 2015.
- BengalSEO promotes fake support and software pages through search results, using black-hat SEO tactics to draw in victims.
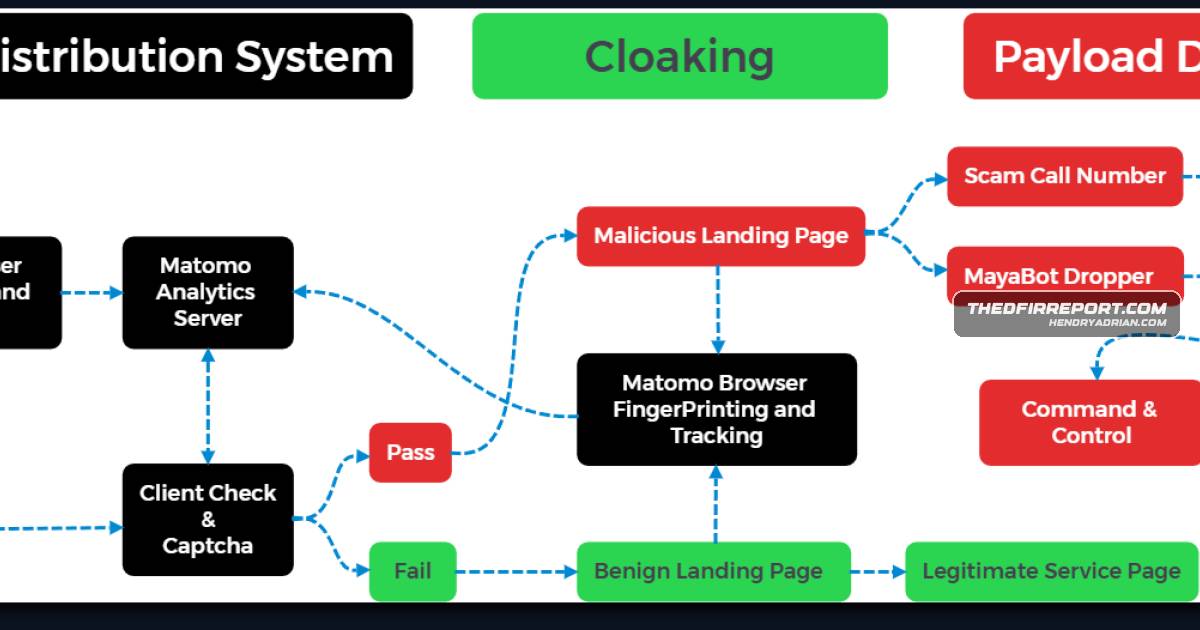
- A traffic distribution system uses rotating redirectors, browser fingerprinting, and CAPTCHA challenges to filter visitors and route selected victims to malicious pages.
- Victims may download a ZIP containing a JavaScript dropper disguised as an executable; running it through wscript.exe initiates the custom MayaBot infection.
- Some visitors are instead directed to pages urging them to call the operation’s tech-support scam centers.
- The researchers link WeConnect Solutions and Garage2Global to the operation and identified 84 active related GitHub accounts between January 2024 and March 2026.
Article Details
- Attack Vectors
- BengalSEO promotes malicious lure pages through SEO poisoning, including backlink spam, keyword stuffing, DOM injection, and DOM shuffling.
- Lure pages impersonate software support, downloads, and service activation portals and direct visitors through rotating TDS redirectors.
- The TDS uses CAPTCHA challenges and browser fingerprinting to decide whether to serve a malicious landing page or a benign page.
- Malicious landing pages offer ZIP downloads containing a MayaBot JavaScript dropper disguised as an EXE file. The dropper executes through wscript.exe when opened.
- Some visitors are instead directed to pages prompting them to call a tech-support scam number.
- Defensive Notes
- The TDS can serve benign content when a visitor fails its checks, complicating automated inspection.
- BengalSEO-linked GitHub repositories periodically rotate embedded redirector domains or temporarily replace them with legitimate URLs.
- The report identifies shared Matomo tracking infrastructure across lure pages, landing pages, and some BengalSEO business websites.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 4jio[.]com | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | cus[.]cam | Domain identified as serving MayaBot C2. |
| DOMAIN | dll[.]lat | Domain identified as serving MayaBot C2. |
| DOMAIN | flosyr[.]com | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | fm[.]ci | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | link72[.]com | Observed TDS redirector embedded in multiple lure pages. |
| DOMAIN | pltechoo[.]pro | Identified payload-delivery landing-page domain. |
| DOMAIN | pre[.]im | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | q82[.]net | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | reficon[.]pro | Identified payload-delivery landing-page domain. |
| DOMAIN | u320[.]my | Identified payload-delivery landing-page domain. |
| DOMAIN | url90[.]com | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | us00[.]net | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | us3[.]org | Domain registered for BengalSEO Matomo tracking infrastructure. |
| DOMAIN | us6[.]my | Observed TDS redirector routing visitors from lure pages. |
| DOMAIN | us99[.]org | Domain identified as serving MayaBot C2. |
| DOMAIN | ustechnio[.]com | Identified payload-delivery landing-page domain and first domain in a MayaBot SEO campaign series. |
| DOMAIN | ustechnio100[.]com | Named endpoint of the sequential domain series featured in MayaBot SEO campaigns. |
| DOMAIN | wapp[.]live | BengalSEO-controlled domain whose subdomains were observed serving as redirectors. |
| DOMAIN | ww0[.]us | Observed TDS redirector routing visitors from lure pages. |
| HOSTNAME | activate[.]uhc[.]com | Lure-page link promoted through forum profile spam. |
| HOSTNAME | ajax[.]googleapis[.]com[.]co | Typosquatted host constructed by lure-page JavaScript to fetch an SEO-poisoning HTML payload. |
| HOSTNAME | tax[.]dll[.]lat | Identified payload-delivery landing-page domain. |
| HOSTNAME | to[.]ghredir[.]com | Observed TDS redirector routing visitors from lure pages. |
| HOSTNAME | ts[.]remdos[.]com | Observed TDS redirector routing visitors from lure pages. |
| HOSTNAME | tx[.]newredir[.]com | Observed TDS redirector routing visitors from lure pages. |
| HOSTNAME | tx[.]platdir[.]com | Observed TDS redirector routing visitors from lure pages. |
| URL | hxxps[:]//oculus-app[.]com/ | BengalSEO impersonation lure page identified in Matomo tracking data. |
| URL | hxxps[:]//stats[.]us3[.]org/matomo[.]php | BengalSEO Matomo endpoint receiving tracking information and browser fingerprints. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article shows an obfuscated MayaBot JavaScript dropper and lure-page script that constructs a typosquatted host from ASCII character codes.T1036 · MasqueradingA MayaBot JavaScript dropper inside the ZIP archive masquerades as an EXE file.T1059.007 · JavaScriptThe MayaBot JavaScript dropper executes through wscript.exe.T1204.002 · Malicious FileLanding pages instruct visitors to open and execute a downloaded ZIP archive containing the MayaBot dropper.T1583.001 · DomainsBengalSEO registered domains in bulk for redirectors, landing pages, and other campaign infrastructure.
People
Threat Actors
Malware
Vendors
CloudflareBefore being redirected to the final landing page, the redirector domains deploy a Cloudflare Turnstile or hCaptcha challenge to filter out automated crawlers, scanners, and bots.GitHubMatomo was not the only analystics system used by BengalSEO, lure pages on hosting platforms such as github.io and pages.dev instead typically use analytics services such as Google Tag Manager.HostmazaIdentifying consistent use of the Hostmaza hosting provider alongside the Spaceship domain registrar.NamecheapBetween 2023 and 2026, BengalSEO primarily registered domains through Spaceship (47.6%) and Namecheap (28.6%).SpaceshipIdentifying consistent use of the Hostmaza hosting provider alongside the Spaceship domain registrar.
Products
Cloudflare TurnstileBefore being redirected to the final landing page, the redirector domains deploy a Cloudflare Turnstile or hCaptcha challenge to filter out automated crawlers, scanners, and bots.Google Tag ManagerMatomo was not the only analystics system used by BengalSEO, lure pages on hosting platforms such as github.io and pages.dev instead typically use analytics services such as Google Tag Manager.hCaptchaBefore being redirected to the final landing page, the redirector domains deploy a Cloudflare Turnstile or hCaptcha challenge to filter out automated crawlers, scanners, and bots.MatomoThis TDS uses a rotating series of redirector domains to route victims to payload delivery domains, as well as a Matomo analytics instance to support victim tracking and fingerprinting.
Tools
AhrefsUsing the Ahrefs service, our team noted that in one example, a lure page had 1900 generated backlinks.ANY.RUNA breakdown of an example traffic flow can be seen in the Any.Run sandbox analysis below: CyberChefFigure 6: CyberChef Base62 decode of redirector tracking parameterStopForumSpamThese accounts were often flagged on StopForumSpam, where reports traced some of the activity to residential IPs in Jaipur, Rajasthan.urlscan.ioFigure 10: urlscan.io requests showing matomo.js on WeConnect siteValidinUsing Validin, our team observed these redirectors embedded in multiple lure pages, for example we observed 73 in June 2026 for the link72[.]com redirector.VirusTotalPivoting on VirusTotal connections and DNS records.
Countries
Industries
Antivirus softwareAntivirus software downloads and support.Financial ServicesGamingGaming software downloads and support.HealthcareActivation of credit, healthcare and gift cards.IT servicesStreaming servicesActivation and support for streaming services.Tax softwareTax software downloads and Tax support.