China-Aligned TA419 Uses Impersonation and AiTM Phishing to Target U.S. AI Policy Experts
Summary
Proofpoint reports that China-aligned TA419 used impersonation and multi-stage adversary-in-the-middle phishing to target U.S. AI policy experts, stealing Microsoft 365 credentials and session cookies through a customized Browser-in-the-Browser tool.
Key points
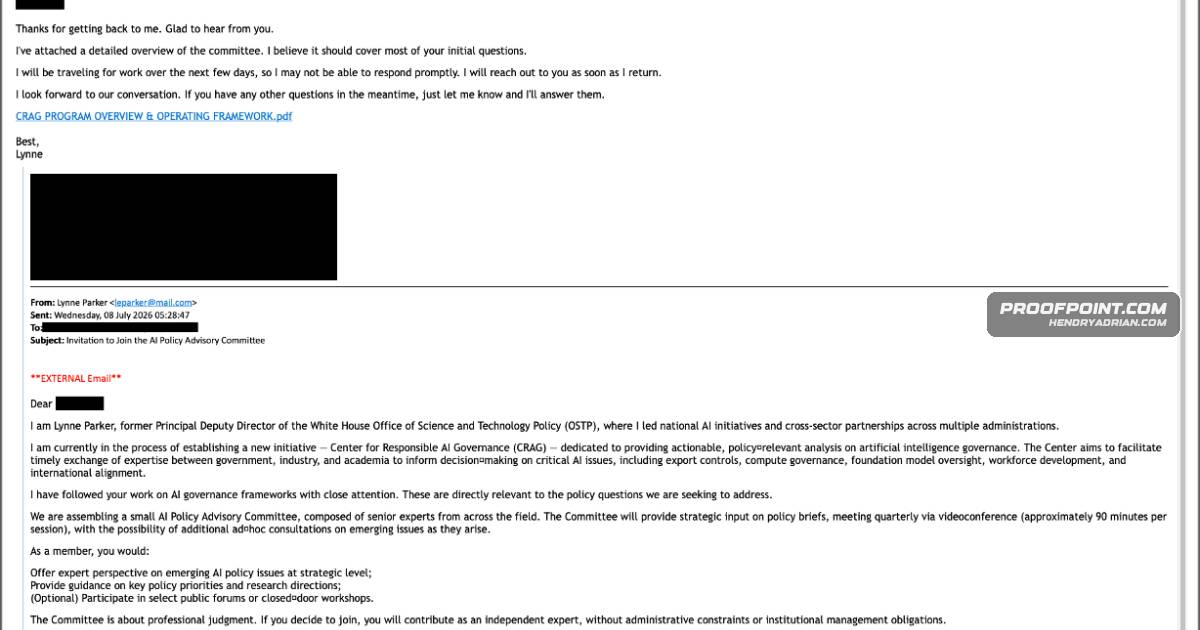
- In July 2026, TA419 impersonated prominent economists and AI policymakers in phishing campaigns targeting experts at U.S. think tanks, universities, and law firms; a similar campaign targeted a think-tank analyst in February.
- The campaigns began with benign outreach about fictitious AI policy initiatives. After recipients replied, shortened links redirected them to fake OneDrive pages.
- The phishing chain used a customized Frameless BitB tool to proxy Microsoft 365 / Entra ID sign-ins, capture passwords, MFA codes, and session cookies, and automate parts of the login flow.
- The July campaigns used driftshare[.]co as a first-stage domain and globalfileshareplatform[.]com as a second-stage phishing domain.
- Proofpoint assesses the targeting as consistent with Chinese intelligence interests in U.S. AI policy and recommends phishing-resistant, origin-bound authentication and independently verifying unexpected outreach.
Article Details
- Attack Vectors
- TA419 sent emails impersonating AI policy experts and other prominent individuals, using benign outreach to elicit a reply before sending a phishing link.
- Shortened links redirected targets through an actor-controlled filtering domain and then to an adversary-in-the-middle credential phishing domain.
- A fake OneDrive loading screen presented a Cloudflare Turnstile check before the phishing page.
- A customized Frameless BitB overlay presented lure documents while a proxy relayed the Microsoft sign-in flow and captured session cookies.
- Defensive Notes
- Proofpoint recommends phishing-resistant, origin-bound authentication such as passkeys for organizations in scope.
- Proofpoint recommends independently verifying unexpected subject-matter outreach through another medium.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cirrushare[.]co | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | cloudsyncpulse[.]com | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | driftshare[.]co | First-stage redirect domain used in both July 2026 phishing campaigns. |
| DOMAIN | fileswiftonline[.]cloud | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | globalfileshareplatform[.]com | Second-stage domain hosting the adversary-in-the-middle phishing page. |
| DOMAIN | goshshare[.]online | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | heritiage[.]org | TA419 domain impersonating The Heritage Foundation. |
| DOMAIN | heritiages[.]org | TA419 domain impersonating The Heritage Foundation. |
| DOMAIN | msfile[.]online | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | mypublicshare[.]com | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | onecloudfilesync[.]com | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | publicsharefile[.]cloud | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | quickfly[.]online | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | sharehub[.]space | TA419 phishing sender domain listed in the source's indicators. |
| DOMAIN | shinjirou[.]info | TA419 domain impersonating Shinjirō Koizumi’s official website. |
| DOMAIN | smartsyncbox[.]com | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | synchvault[.]co | TA419 phishing domain listed in the source's indicators. |
| DOMAIN | tw-koryu[.]org | TA419 domain impersonating the Japan-Taiwan Exchange Association. |
| DOMAIN | winsync[.]cloud | TA419 phishing domain listed in the source's indicators. |
hcrediker@mail[.]com | Attacker-controlled email address listed for the July 2026 phishing activity. | |
hcrediker@outlook[.]com | Attacker-controlled email address listed for the July 2026 phishing activity. | |
leparker@mail[.]com | Attacker-controlled email address listed for the July 2026 phishing activity. | |
| IPV4 | 108[.]61[.]163[.]187 | VPS identified in an example TA419 phishing email header as actor-controlled. |
| SHA256 | b314a1499cd728ca3e54b7150661fd0c7d2279065fe3f570f0f66c395d744460 | SHA256 fingerprint of a TLS certificate associated with likely TA419 anonymization infrastructure. |
MITRE ATT&CK
T1111 · Multi-Factor Authentication InterceptionTA419's adversary-in-the-middle phishing flow handled targets' MFA codes as part of the relayed sign-in.T1539 · Steal Web Session CookieTA419's phishing proxy relayed the genuine Microsoft sign-in flow while capturing the resulting session cookies.T1566.002 · Spearphishing LinkAfter targets replied to impersonation emails, TA419 sent shortened links leading to credential phishing pages.T1656 · ImpersonationTA419 impersonated named economists, AI policy figures, and an Anthropic employee in outreach to targets.
Threat Actors
Vendors
CloudflareThe first actor-controlled domain serves as an initial filter; it conducts a Cloudflare Turnstile check behind a fake OneDrive loading screen before redirecting the target to an AitM credential phishing page hosted on aMicrosoftThe AitM phishing chain used by TA419 targets Microsoft 365 / Entra ID through the first-party OfficeHome application (client_id=4765445b-32c6-49b0-83e6-1d93765276ca).NameSiloTA419 consistently uses Cloudflare’s content delivery network (CDN) to obscure the backend hosting IP address for its domains, which are typically registered via NameSilo.
Products
Cloudflare TurnstileThe first actor-controlled domain serves as an initial filter; it conducts a Cloudflare Turnstile check behind a fake OneDrive loading screen before redirecting the target to an AitM credential phishing page hosted on aEntra IDThe AitM phishing chain used by TA419 targets Microsoft 365 / Entra ID through the first-party OfficeHome application (client_id=4765445b-32c6-49b0-83e6-1d93765276ca).Microsoft 365The AitM phishing chain used by TA419 targets Microsoft 365 / Entra ID through the first-party OfficeHome application (client_id=4765445b-32c6-49b0-83e6-1d93765276ca).OfficeHomeThe AitM phishing chain used by TA419 targets Microsoft 365 / Entra ID through the first-party OfficeHome application (client_id=4765445b-32c6-49b0-83e6-1d93765276ca).OneDriveThe link ultimately led to a fake OneDrive AitM credential phishing page designed to gain access to the target’s cloud account.
Tools
EvilginxFrameless BitB, an open-source Browser-in-the-Browser kit, which contains the BitB overlay alongside an Evilginx phishlet for Microsoft 365 and server-side substitution rules that inject the kit into proxied pages.Frameless BitBthat employed a customized version of the open-source Browser-in-the-Browser (BitB) phishing tool Frameless BitB.
Countries
ChinaIn July 2026, a China-aligned threat actor Proofpoint tracks as TA419 conducted multiple credential phishing campaigns impersonating prominent economists and artificial intelligence (AI) policymakers to target AIJapanconducting regular targeted credential phishing campaigns against individuals working for US- and Japan-based think tanks, defense contractors, universities, and law firms since at least April 2025.United Statesprominent economists and artificial intelligence (AI) policymakers to target AI experts working for US think tanks, universities, and legal sector organizations.
Industries
Defensetargeted credential phishing campaigns against individuals working for US- and Japan-based think tanks, defense contractors, universities, and law firms since at least April 2025.EducationEnergyTA419 has consistently shown an interest in defense, national security, energy, international relations, and foreign policy targets, predominantly with a nexus to the US and Japan.Legalintelligence (AI) policymakers to target AI experts working for US think tanks, universities, and legal sector organizations.