LevelBlue Details CVE-2026-88771 Exploitation Activity Targeting NetScaler Appliances
Summary
LevelBlue observed attackers exploiting CVE-2026-88771 against NetScaler appliances, with commands and payloads targeting configuration data, privileged access, reverse shells, and web shells. It provides behavioral indicators for investigation.
Key points
- LevelBlue’s threat-hunting team found malicious NetScaler authentication events containing attacker-controlled usernames designed to exploit the critical pre-authentication command-injection vulnerability.
- Observed commands tested execution and attempted to retrieve payloads, collect or stage NetScaler configuration data, and deploy reverse shells and web shells.
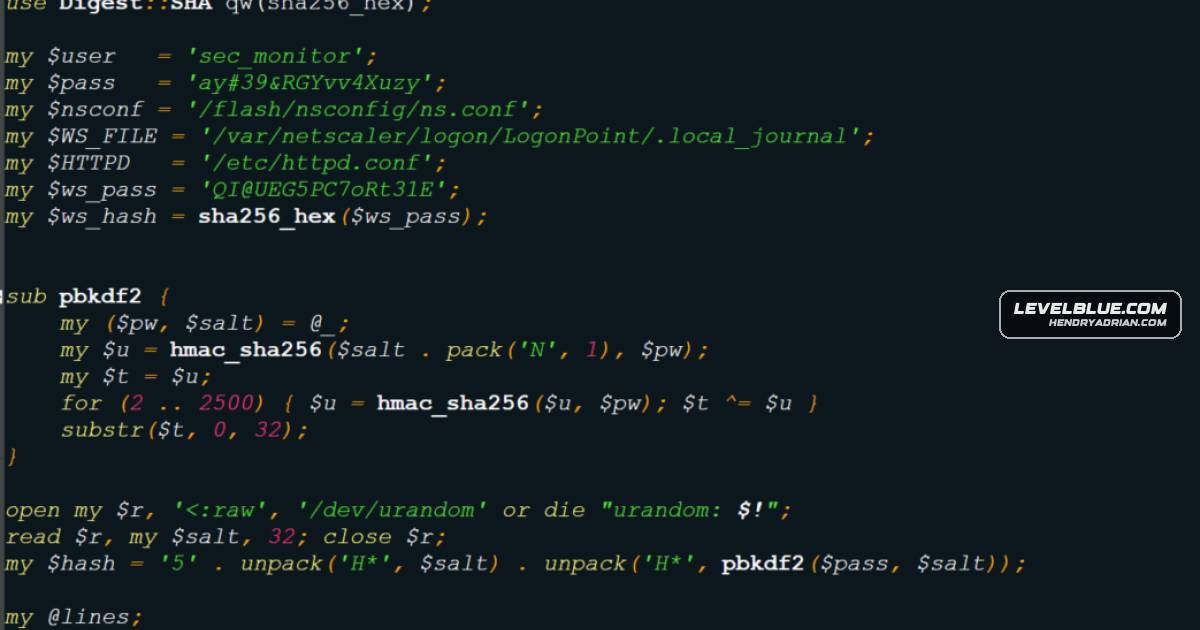
- A Python payload targeted /var/python/bin/customsnmpd to establish a reverse shell; a Perl payload could create a privileged sec_monitor account, expose a PHP web shell, and attempt to exfiltrate configuration data.
- Hunt indicators include shell commands in authentication fields, unexpected access to /flash/nsconfig, web-directory artifacts, changes to appliance configuration or /bin/sh permissions, and related network connections.
- The report cautions that indicators are not exhaustive and that deleted payloads or archives do not prove execution failed; defenders should investigate beyond the initial authentication event.
- Organizations should patch affected NetScaler appliances and review historical telemetry for signs of exploitation before remediation.
Article Details
- Attack Vectors
- Pre-authentication command injection through attacker-controlled NetScaler authentication usernames containing pitboss and NSPPE strings.
- Injected commands tested execution, retrieved second-stage payloads with curl or wget, and copied or archived NetScaler configuration data.
- The main.py payload overwrote /var/python/bin/customsnmpd with code that establishes a reverse shell.
- The update_c08937.pl payload attempted configuration exfiltration, created a privileged local account, and installed a PHP web shell.
- Defensive Notes
- Patch affected NetScaler appliances and review historical authentication telemetry, including failed authentication events, for shell commands embedded in authentication fields.
- Investigate unexpected access to /flash/nsconfig, creation of files in NetScaler web directories, and network connections following command-injection attempts.
- Check for the sec_monitor account, modifications to /var/python/bin/customsnmpd or /etc/httpd.conf, the .local_journal web shell, and /bin/sh permissions changed to 6555.
- Absence of the configuration archive or Perl payload does not rule out execution: the analyzed payload deletes both.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 162[.]243[.]36[.]88 | Exploitation-related IP listed in the investigation's IOC table; its specific role is not stated. |
| IPV4 | 173[.]40[.]135[.]209 | Exploitation-related IP listed in the investigation's IOC table; its specific role is not stated. |
| IPV4 | 23[.]27[.]143[.]20 | Exploit source and host of the main.py reverse-shell payload. |
| IPV4 | 31[.]56[.]197[.]72 | Host of the lula payload referenced in injected retrieval commands. |
| IPV4 | 45[.]141[.]21[.]130 | Reverse-shell C2 address contacted by the modified customsnmpd. |
| IPV4 | 47[.]230[.]224[.]154 | Exploitation-related IP listed in the investigation's IOC table; its specific role is not stated. |
| IPV4 | 62[.]133[.]62[.]80 | Payload-hosting infrastructure. |
| IPV4 | 64[.]94[.]85[.]67 | Exploit and payload infrastructure used for attempted configuration exfiltration. |
| IPV4 | 70[.]172[.]58[.]168 | Source of observed NetScaler exploitation attempts. |
| IPV4 | 87[.]224[.]84[.]82 | Source of a configuration-staging attempt. |
| IPV4 | 92[.]118[.]204[.]229 | Source of command-execution testing. |
| SHA256 | 974b69782fdf5d67b97cfd508465939e44ee10798dbcc1e82b92d78776bad938 | Hash of the update_c08937.pl payload. |
| SHA256 | e9fe43968c6c0955300e3bc4d7fb0b05a18570b4733aaf4f5c6f7f09be5a242c | Hash of the main.py payload. |
| URL | hxxp[:]//23[.]27[.]143[.]20:9000/main[.]py | URL hosting the analyzed Python reverse-shell payload. |
| URL | hxxp[:]//31[.]56[.]197[.]72:9090/lula | Payload URL referenced in injected wget and curl commands. |
| URL | hxxp[:]//62[.]133[.]62[.]80/xd7h/x | Payload download URL. |
| URL | hxxp[:]//64[.]94[.]85[.]67:443/update_c08937[.]pl | URL hosting the analyzed Perl post-exploitation payload. |
| URL | hxxp[:]//64[.]94[.]85[.]67:443/update_result_3567cs[.]tgz | Identified NetScaler configuration exfiltration endpoint. |
MITRE ATT&CK
T1005 · Data from Local SystemInjected commands and the Perl payload collected NetScaler configuration data from /flash/nsconfig.T1059.004 · Unix ShellInjected usernames contained shell commands including whoami, curl, wget, cat, and tar; the reverse-shell payload launched interactive /bin/sh.T1059.006 · PythonThe main.py payload overwrote customsnmpd with Python code designed to establish a reverse shell.T1070.004 · File DeletionAfter attempting to transfer the configuration archive, the Perl payload removed the archive and deleted itself.T1105 · Ingress Tool TransferInjected commands used curl or wget to retrieve second-stage payloads from external hosts.T1136.001 · Local AccountThe Perl payload modified ns.conf to create the local sec_monitor account with superuser privileges.T1190 · Exploit Public-Facing ApplicationAttackers placed command-injection strings in pre-authentication NetScaler authentication data to exploit CVE-2026-88771.T1222.002 · Linux and Mac PermissionsThe Perl payload changed /bin/sh permissions to 6555.T1505.003 · Web ShellThe Perl payload deployed a PHP web shell at /var/netscaler/logon/LogonPoint/.local_journal.T1560.001 · Archive via UtilityInjected tar commands and the Perl payload archived the /flash/nsconfig directory.