Fake Hotel Guest Complaints Deliver EtherRAT and TONResolver via Blockchain-Based C2
Summary
Cofense details campaigns targeting hotel staff with fake guest complaints that deliver EtherRAT or TONResolver. The malware retrieves changeable C2 addresses from public blockchains, complicating conventional infrastructure takedowns.
Key points
- Emails posing as guest complaints, reviews, or inquiries prompt hotel staff to open an archive containing an LNK shortcut disguised with a JPG extension.
- Running the shortcut downloads a Node.js runtime and installs either EtherRAT or TONResolver.
- EtherRAT retrieves C2 data from Ethereum smart-contract storage; TONResolver reads data associated with a TON wallet or smart contract.
- Threat actors can update blockchain-stored C2 addresses through transactions, making conventional domain or hosting takedowns alone ineffective.
- Cofense assesses with moderate confidence that the campaigns continue earlier Booking.com-spoofing activity, but says shared tools could also be used by separate actors.
- Cofense recommends scrutinizing unsolicited, urgent complaint emails and training staff to recognize malicious messages.
Article Details
- Attack Vectors
- Fake guest complaints, negative reviews, and accommodation inquiries sent to hotel front desk, reservations, or guest relations staff link to archives containing malicious LNK shortcuts disguised as JPG images.
- Some malicious messages are sent as replies within email threads after an initially legitimate conversation.
- Executing the disguised LNK downloads a NodeJS runtime environment and installs EtherRAT or TONResolver.
- Archives also contain a dummy MP4 whose size changes between downloads, likely to produce different hashes and reduce static hash-based detection effectiveness.
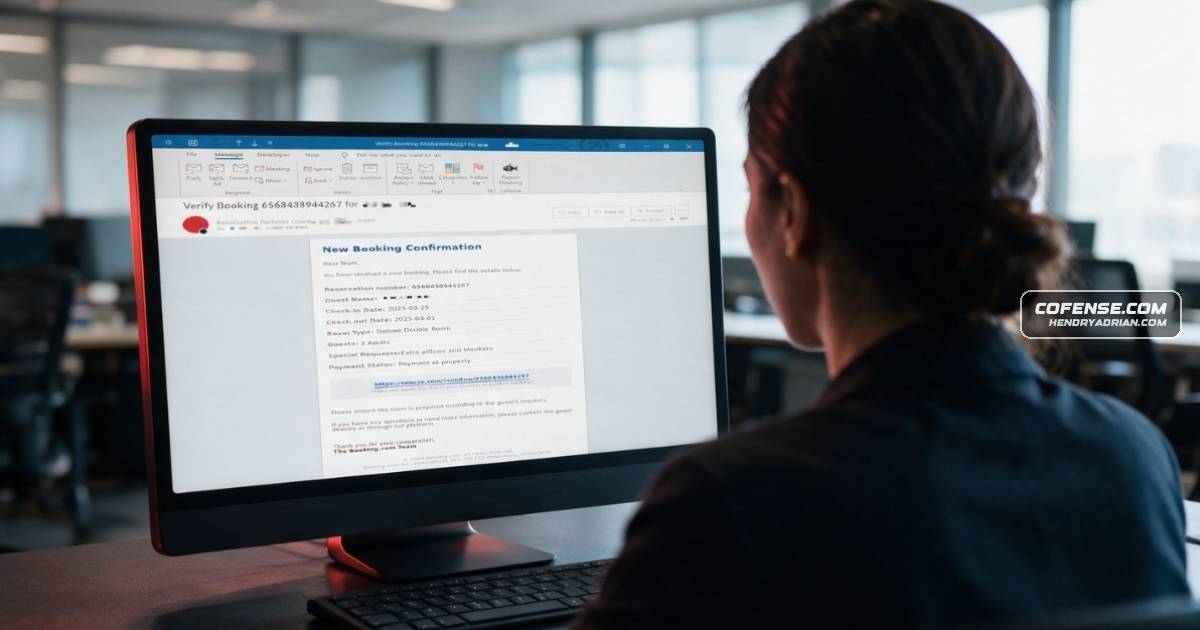
- Earlier Booking.com-spoofing emails linked to fake CAPTCHA pages that placed malicious scripts on the clipboard and instructed recipients to execute them through the Windows Run dialog.
- EtherRAT and TONResolver retrieve changing C2 addresses from public blockchain data rather than relying on hardcoded domains or IP addresses.
- Defensive Notes
- Train employees to recognize malicious email indicators and apply consistent scrutiny to unsolicited complaints or negative reviews, particularly those threatening immediate consequences.
- Do not rely solely on static email wording or file hashes: lure wording varies substantially, and the dummy MP4 changes size between downloads.
- Conventional domain and IP takedowns alone cannot prevent infected hosts from retrieving replacement C2 addresses from persistent blockchain records.
- Requests to public blockchain APIs are not inherently malicious and can blend with legitimate cryptocurrency traffic.
- Blocking Ethereum API access alone may not cover malware that resolves C2 infrastructure through TON APIs.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | amanohuguta[.]cfd | TONResolver C2 domain associated with the TON smart contract examined in ATR 422158. |
| DOMAIN | fdffofofofo4[.]com | EtherRAT C2 domain associated with the Ethereum smart contract examined in ATR 422147. |
| DOMAIN | hsaertyuoang34[.]sbs | TONResolver C2 domain associated with the TON smart contract examined in ATR 422158. |
| DOMAIN | njzlopghznkamkl[.]cfd | TONResolver C2 domain associated with the TON smart contract examined in ATR 422158. |
| DOMAIN | nuypoiaklber[.]lol | TONResolver C2 domain associated with the TON smart contract examined in ATR 422158. |
| DOMAIN | tonajukbhuakpo2[.]shop | TONResolver C2 domain associated with the TON smart contract examined in ATR 422158. |
| DOMAIN | zloapobikahy23[.]bond | TONResolver C2 domain associated with the TON smart contract examined in ATR 422158. |
MITRE ATT&CK
T1036 · MasqueradingMalicious LNK shortcuts masquerade as JPG image files associated with fabricated guest complaints.T1059.007 · JavaScriptEtherRAT and TONResolver run through a NodeJS runtime environment used to execute JavaScript.T1102.001 · Dead Drop ResolverEtherRAT reads Ethereum smart-contract data and TONResolver reads TON wallet or smart-contract data to resolve current C2 addresses.T1105 · Ingress Tool TransferExecuted LNK files download a NodeJS runtime environment and install EtherRAT or TONResolver.T1204.002 · Malicious FileRecipients are persuaded to execute an LNK shortcut presented as an image requiring review, initiating malware installation.T1566.002 · Spearphishing LinkFake hotel guest complaints and reviews contain links to archives delivering malicious LNK files; earlier Booking.com-spoofing emails linked to ClickFix pages.
People
Malware
EtherRATemail templates, how the Ethereum and TON blockchains are being abused, and the similarities between the EtherRAT and TONResolver malware payloads found in these campaigns.NetSupport Manager RATdeliver malicious scripts to the clipboard in order to deliver various RATs (typically PureRAT or NetSupport Manager RAT) and/or information stealers. These emails typically impersonated a guest reservation, paymentPureRatBooking.com-spoofing, travel assistance-themed campaigns that delivered more conventional RATs like PureRAT, based on overlapping lure themes and targeted industry sector.TONResolverhow the Ethereum and TON blockchains are being abused, and the similarities between the EtherRAT and TONResolver malware payloads found in these campaigns.
Products
Booking.commalware. These emails appear to likely be a continuation of a prior series of predominantly Booking.com-spoofing emails that were seen delivering various remote access trojans (RAT) via ClickFix fake CAPTCHAEthereumand the targeted industry. This report is a broad overview of these campaigns’ email templates, how the Ethereum and TON blockchains are being abused, and the similarities between the EtherRAT and TONResolver malwareNode.jsreduce the effectiveness of static file hash-based detections. Once the LNK file is run, it downloads a NodeJS runtime environment (a legitimate tool used to run JavaScript as a standalone piece of software on aTONindustry. This report is a broad overview of these campaigns’ email templates, how the Ethereum and TON blockchains are being abused, and the similarities between the EtherRAT and TONResolver malware payloads