cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2380 articles

Threat Research · bitdefender.com

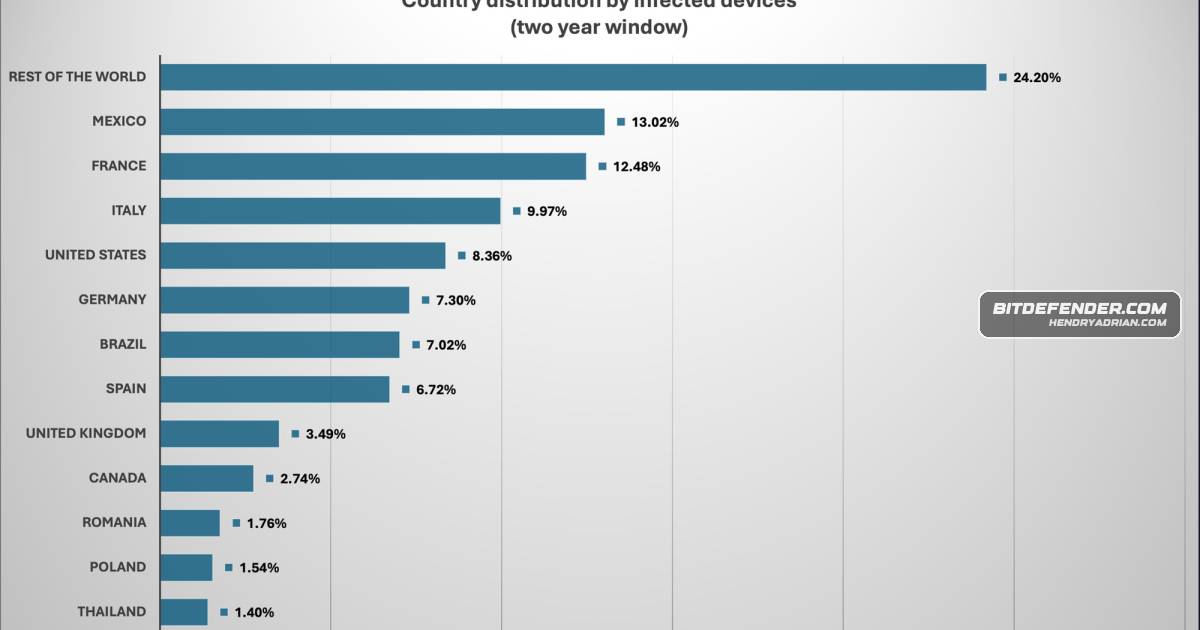
Midnight Mimosa Malware Preinstalled on Android Phones Enables Ad Fraud and Proxy Botnets

Bitdefender researchers detail Midnight Mimosa, malware preinstalled on low-cost Android devices that silently deploys payloads for ad fraud and proxy botnets. They also found related apps on Google Play and observed the campaign on thousands of devices.

Oct 8, 2026
Threat Research · helpnetsecurity.com

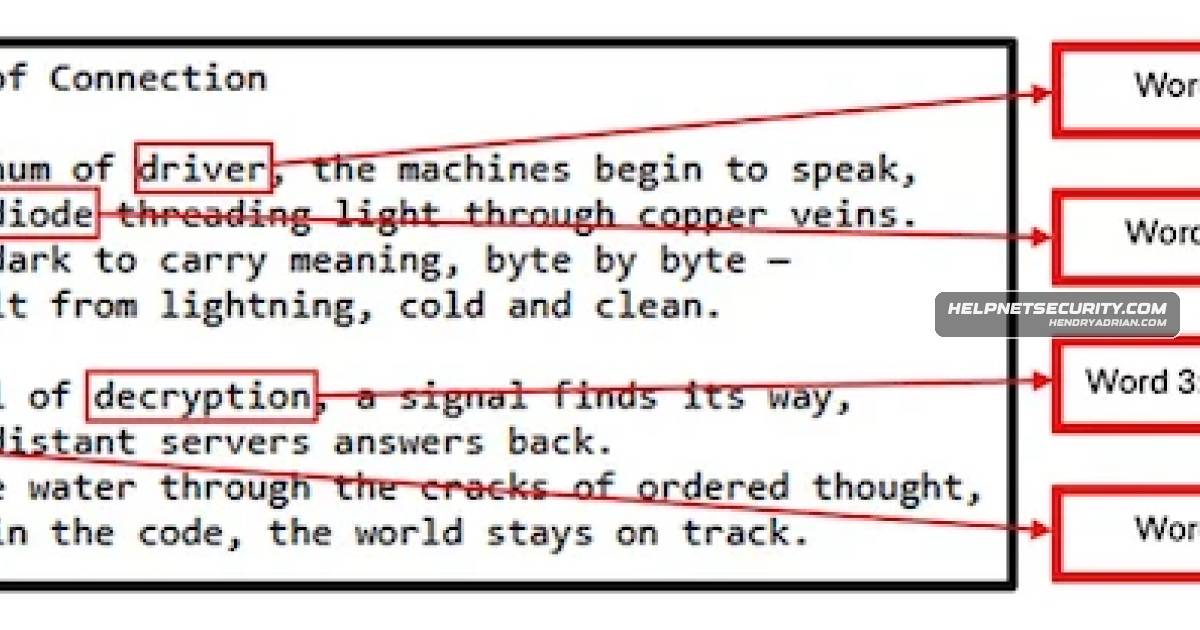
PoeLLM Botnet Hides C2 Address in GitHub Poem, Infecting More Than 3,400 Servers

Black Lotus Labs says the PoeLLM campaign has compromised over 3,400 servers since April 2026, using a GitHub poem to encode C2 addresses and infected systems to mine cryptocurrency and scan for new targets.

Oct 8, 2026
Threat Research · cisa.gov

Chinese Government-Linked Actors Combine Automated and Hands-On Hacking to Steal Sensitive Data

A joint advisory details how actors linked to China and Integrity Technology Group target organizations worldwide using automated scanning, exploitation, credential attacks, VPN persistence, and data exfiltration.

Oct 8, 2026
Threat Research · rogueauthority.org

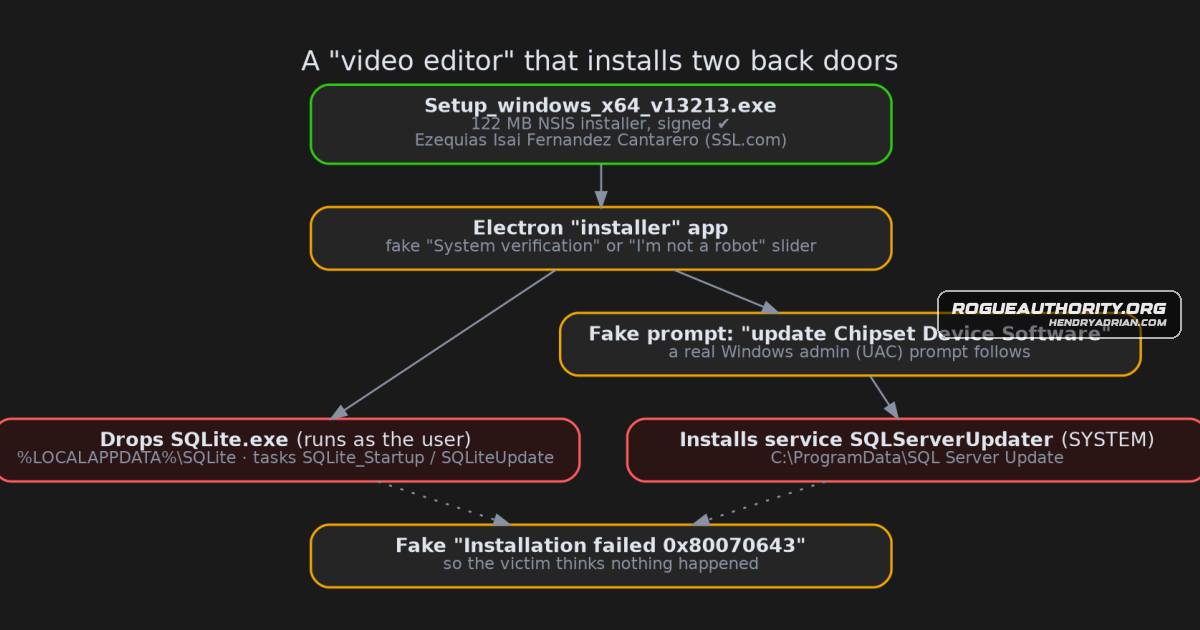
Signed Fake Video Editor Installer Deploys Two Back Doors

Analysis of a signed Windows installer found two back doors: a SYSTEM-level service and a user-level program. The installer uses fake verification and failure screens; the back doors fetch instructions from servers, and one reports activity to Telegram.

Oct 8, 2026
Threat Research · rogueauthority.org

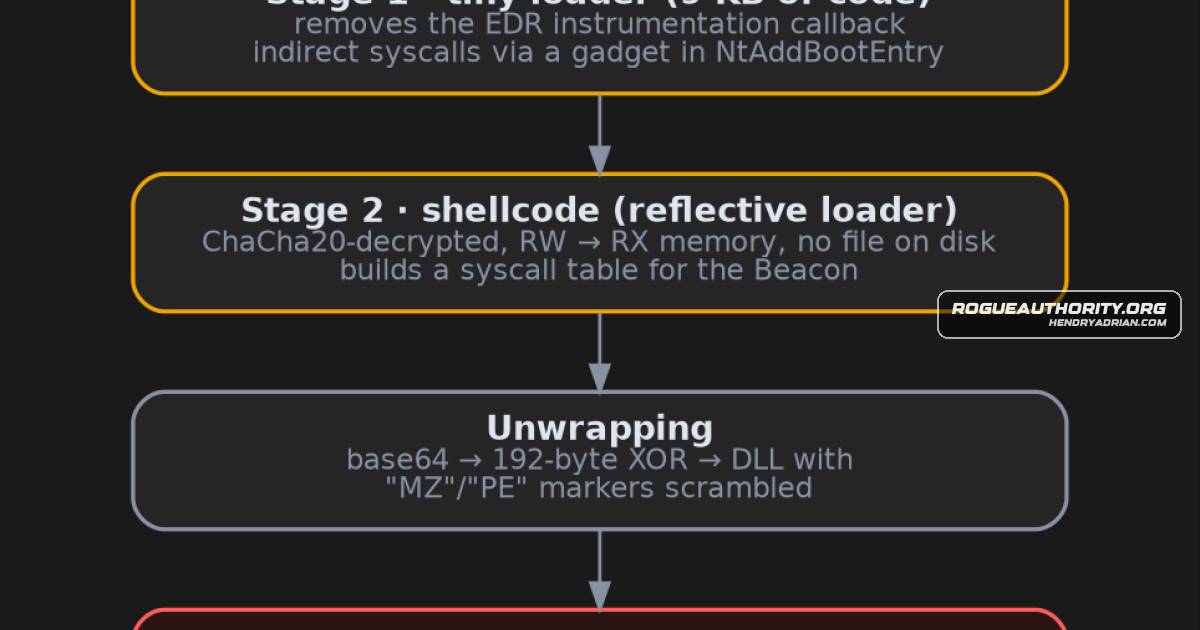
Signed Loader Unpacks Cobalt Strike Beacon That Masquerades as CrowdStrike Traffic

Analysis of a signed Windows loader found it unpacks a Cobalt Strike Beacon configured to imitate CrowdStrike traffic. The Beacon did not contact its server in the sandbox, and delivery method and operational context remain unknown.

Oct 8, 2026
Threat Research · picussecurity.com

BlueMoon Exploit Kit Chains Chrome and Windows Flaws to Deliver Malware

BlueMoon campaigns use spearphishing links and a Chrome/V8-to-Windows kernel exploit chain to run malware outside the browser sandbox. Four espionage-focused clusters delivered payloads including GemStone and ShadowPad.

Oct 8, 2026
Threat Research · thehackernews.com

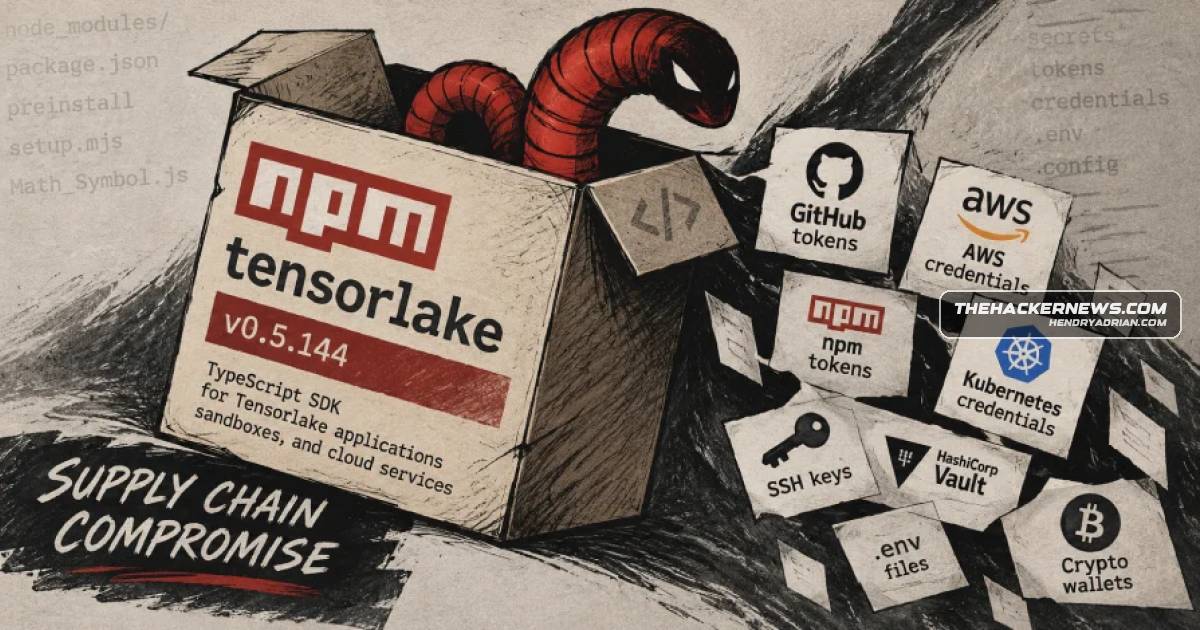
Compromised Tensorlake npm Package Delivered Shai-Hulud Credential-Stealing Worm

Tensorlake npm version 0.5.144 contained a worm that steals credentials, propagates through packages linked to a victim’s publishing identity, establishes persistence, and can execute attacker-supplied code. Users should remove it and rotate credentials.

Oct 8, 2026
Threat Research · socket.dev

TensorLake npm SDK Version 0.5.144 Compromised in Credential-Stealing Supply-Chain Attack

Socket reports that [email protected] runs malware during npm installation to steal credentials, exfiltrate secrets, persist, execute remote code, and spread to other packages. A token monitor may wipe a host if its GitHub token is revoked.

Oct 8, 2026
Threat Research · aikido.dev

Shai-Hulud Variant Found in Compromised Tensorlake npm Package

Aikido reports that Tensorlake npm 0.5.144, published after a repository compromise, carried a Shai-Hulud variant that steals secrets, targets browser-wallet data and can spread through connected supply chains.

Oct 8, 2026
Threat Research · stepsecurity.io

StepSecurity Details Tensorlake npm Malware That Steals Credentials and Can Wipe Home Directories

StepSecurity says [email protected] steals credentials, spreads through npm packages and GitHub repositories, and can delete a user's home directory if its stolen GitHub token is revoked while a monitor is active.

Oct 8, 2026
Threat Research · huntress.com

Attackers Exploit AhsayCBS Flaws to Deploy Webshells and XMRig Miners

Huntress observed attackers exploiting chained AhsayCBS authentication-bypass and RCE flaws against five organizations, deploying JSP webshells, XMRig miners and persistence tools. Ahsay released hotfixes; Huntress recommends restricting access and reimaging compromised

Oct 8, 2026
Threat Research · cloudsek.com

NEBULA Campaign Uses Fake npm AI SDKs to Deliver a DLL-Free Windows RAT

CloudSEK links seven fake NebulaAI npm packages to a Windows RAT delivered through obfuscated install hooks. Two packages remained downloadable; the report details the payload, capabilities, and recommended defenses.

Oct 8, 2026
Threat Research · zscaler.com

TraderTraitor-Linked Campaign Uses Trojanized Terraform Provider to Deploy Cross-Platform Malware

Zscaler details a suspected TraderTraitor campaign that uses a trojanized Terraform provider to deploy FLATROOF and ROOFDECK across Windows, macOS, and Linux, stealing sensitive data and enabling persistent remote access.

Oct 8, 2026
Threat Research · reversinglabs.com

ReversingLabs Found AI-Modified Malware Before Anthropic Report, Says Behaviors Still Reveal It

ReversingLabs says it identified rebuilt malware variants two months before Anthropic’s report. Its telemetry found that AI can accelerate changes to hashes, but the malware’s behaviors and links to infrastructure remain useful detection signals.

Oct 8, 2026
Threat Research · welivesecurity.com

ESET Details Evolution of UAC-0099’s MATCHBOIL Malware

ESET analyzes MATCHBOIL samples from 2024 to 2026, detailing how the UAC-0099 downloader evolved its obfuscation, persistence, sandbox checks, and delivery behavior. The group used it in campaigns targeting organizations in Ukraine.

Oct 8, 2026
Threat Research · darkreading.com

Russia-Linked Group Enhances MatchBoil Malware to Target Ukrainian Organizations

ESET says UAC-0099, a group likely linked to Russian interests, is using an increasingly sophisticated MatchBoil downloader against Ukrainian organizations, delivering a backdoor and adding obfuscation, sandbox checks, and changing persistence methods.

Oct 8, 2026
Threat Research · bleepingcomputer.com

Midnight Mimosa Malware Found Preinstalled on Low-Cost Android Phones

Bitdefender found Midnight Mimosa malware embedded in low-cost Android phone firmware, enabling silent app installation, ad fraud, and residential proxy activity. The campaign affected thousands of devices in more than 150 countries.

Oct 8, 2026
Threat Research · unit42.paloaltonetworks.com

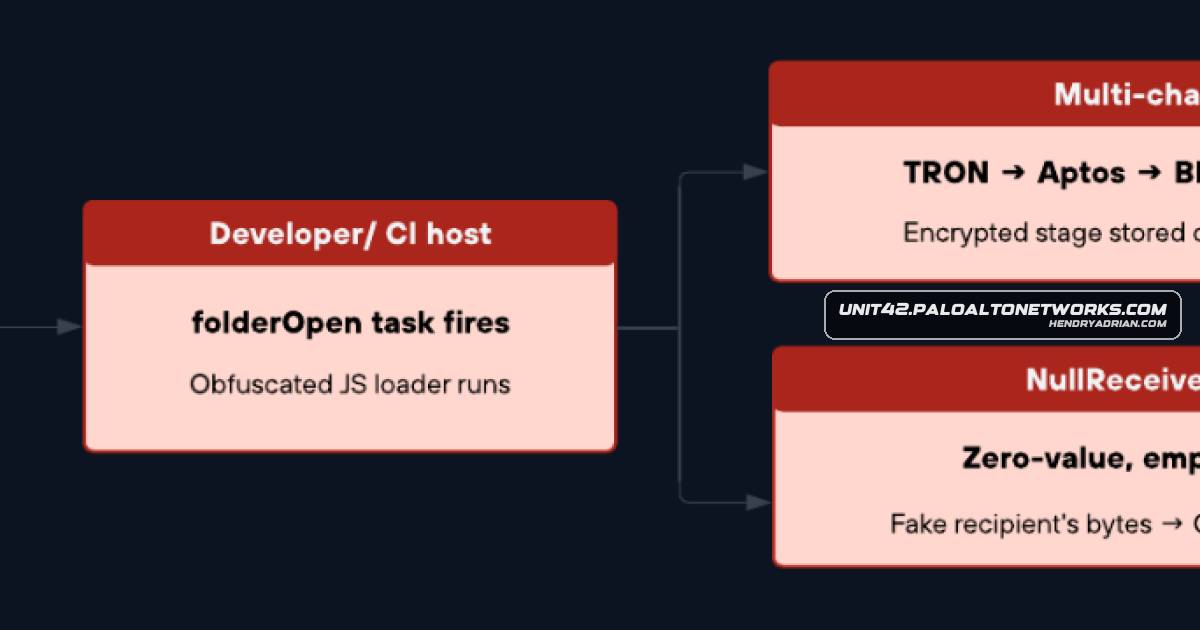
Supply-Chain Malware Uses Blockchain Transactions for Resilient Command and Control

Unit 42 describes ChainDrop and PolinRider supply-chain campaigns that steal developer and cloud credentials, persist in build workflows, and use smart contracts or blockchain transactions to update command-and-control infrastructure.

Oct 7, 2026
Threat Research · thehackernews.com

MALFEX npm Campaign Delivers Overlord RAT and Stealers Through Eight Malicious Packages

Researchers say the MALFEX campaign used eight malicious npm packages, downloaded 40,767 times, to deliver Overlord RAT loaders and information stealers through install hooks and package dependencies.

Oct 7, 2026
Threat Research · censys.com

Censys Finds Live DarkSword/Coruna Infrastructure and iOS Wallet-Theft Platform

Censys uncovered live DarkSword/Coruna infrastructure, iOS wallet-theft modules, and evidence of a distinct Chinese-speaking operator. An iOS 26 exploit chain is under development but not deployed.

Oct 7, 2026
Threat Research · levelblue.com

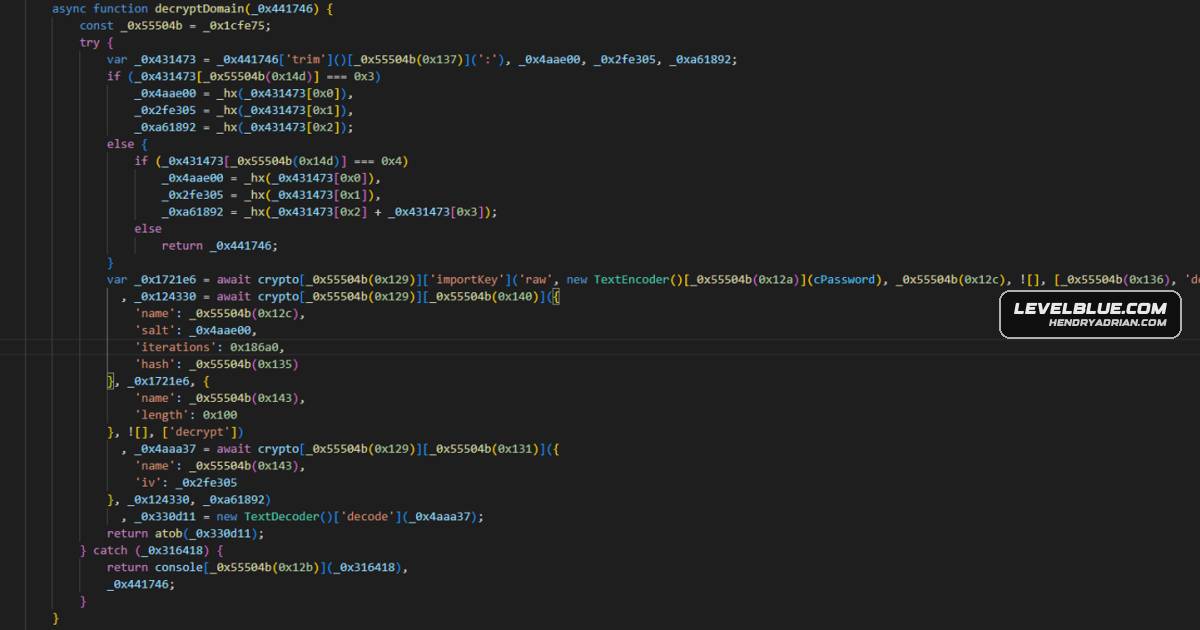
PhantomPolia Campaign Uses ClickFix and Donut Shellcode to Deliver Remus Stealer

LevelBlue details a campaign that uses compromised sites, a blockchain-based loader and ClickFix lures to deliver Remus Stealer, which collects credentials, browser and wallet data, and system information.

Oct 7, 2026
Threat Research · socket.dev

16 Malicious Firefox Extensions Steal Cryptocurrency Wallet Credentials

Socket researchers found 16 Firefox extensions that steal wallet recovery phrases and private keys, sending them to attacker-controlled Cloudflare Workers. Mozilla unpublished the extensions by October 5; affected users should move assets to a new wallet.

Oct 7, 2026
Threat Research · socradar.io

NetScaler C2 Automates Mass Exploitation of Citrix CVE-2026-88771

SOCRadar details NetScaler C2, a framework exploiting CVE-2026-88771 to find vulnerable Citrix appliances, inject commands, and deploy a polling agent. It reports no confirmed victim count and recommends upgrading, isolating, and checking for compromise.

Oct 7, 2026
Threat Research · reliaquest.com

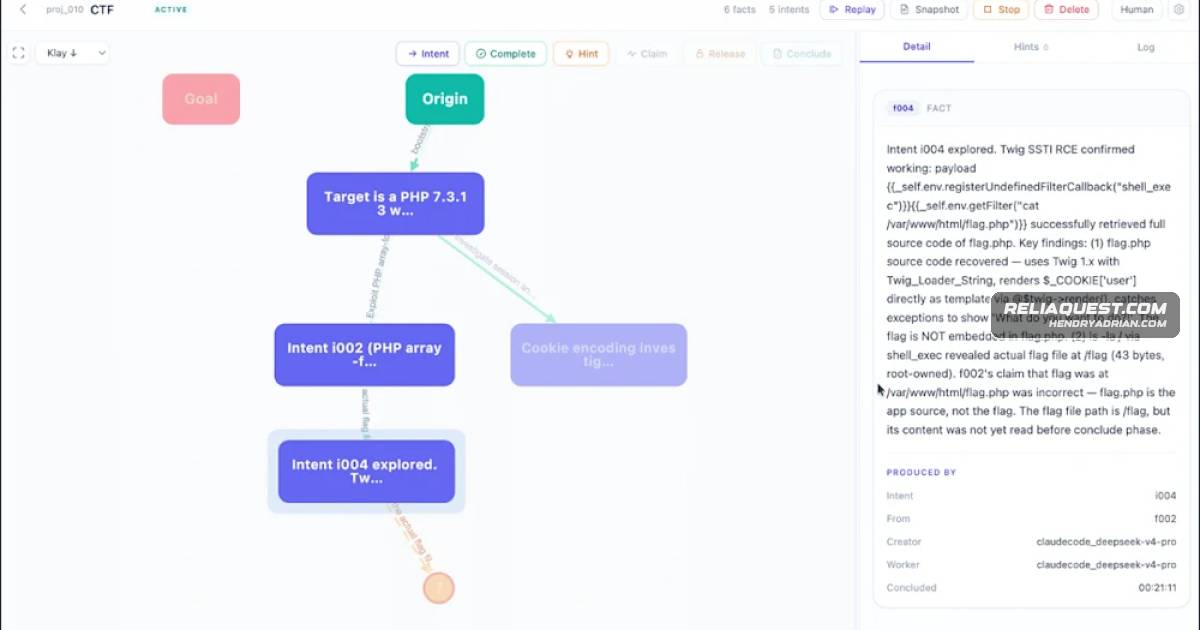
AI Agents Used an Exposed Endpoint to Take Over a Server, ReliaQuest Finds

ReliaQuest details an incident in which an attacker used an unauthenticated job-submission feature to steal credentials and take full control of a server, with evidence suggesting LLM-driven agents carried out much of the attack.

Oct 7, 2026
PreviousPage 14 of 100 Next
© 2026 cyber.hendryadrian.com