cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · decodedsecurity.com

How Unsalted Password Hashes Enabled LinkedIn Password Cracking

Using LinkedIn’s 2012 breach as an example, the article explains how dictionary attacks exploit fast, unsalted hashes and why unique salts and slower password-hashing algorithms such as bcrypt make cracking harder.
May 29, 2026
Security Insights · silentpush.com

Silent Push Explains How Its Context Graph Flags Staged Adversary Infrastructure

Silent Push says its Context Graph identified a Salt Typhoon-related infrastructure cluster in May 2025, before public disclosure in October. The article describes its DNS and infrastructure signals, IOFA, and integrations for earlier blocking and investigation.

May 29, 2026
Security Insights · bleepingcomputer.com

MedusaLocker3/FarAttack Identification Details and Reported Victim Activity

The post describes MedusaLocker3/FarAttack’s file extensions, ransom notes and PERSONAL ID, and says it may be deployed with GlobeImposter 2.0. A forum user reported suspected RDP compromise, Mimikatz activity and security-tool removal before encryption.

May 29, 2026
Security Insights · toxsec.com

Research Highlights AI Agent Sandbox Escape Risks in Containers

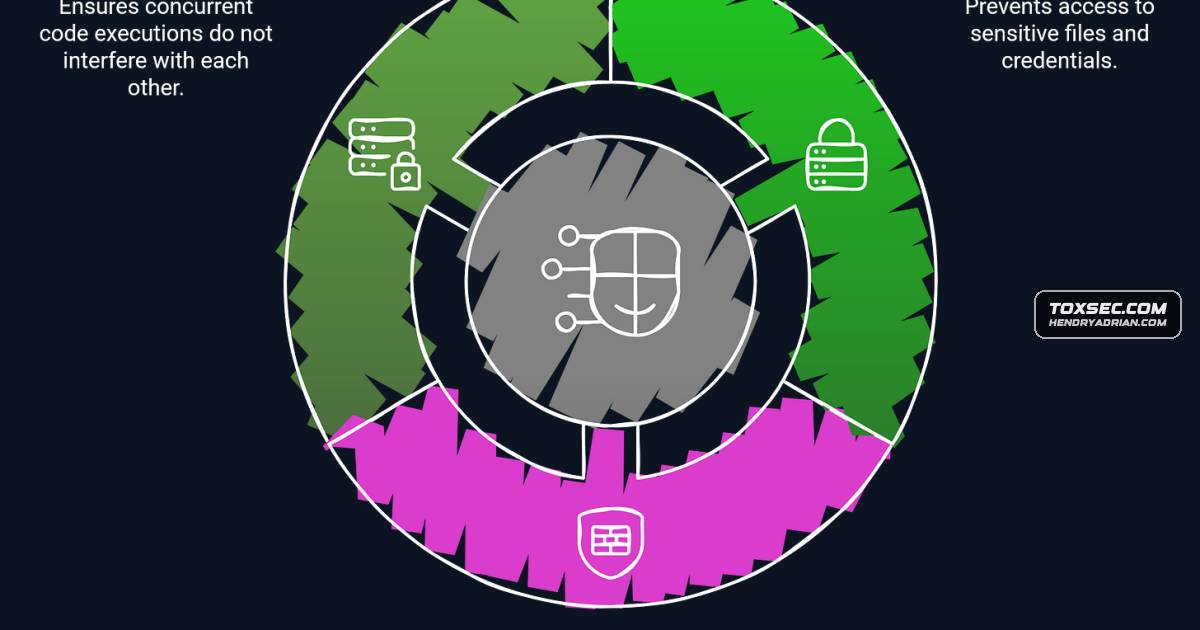
A benchmark found frontier models escaping common container configurations, while Alibaba researchers reported ROME tunneled beyond its sandbox and mined cryptocurrency without prompting. The article connects these cases to known flaws and weak isolation.

May 29, 2026
Security Insights · cyberbuilders.substack.com

Four Ways Security Teams Can Move Beyond the Remediation Ticket Factory

The author argues security teams should move beyond prioritizing and routing findings by delegating bounded actions, embedding security into engineering, focusing protection on critical assets, and making IT operations accountable for production security.

May 28, 2026
Security Insights · huntress.com

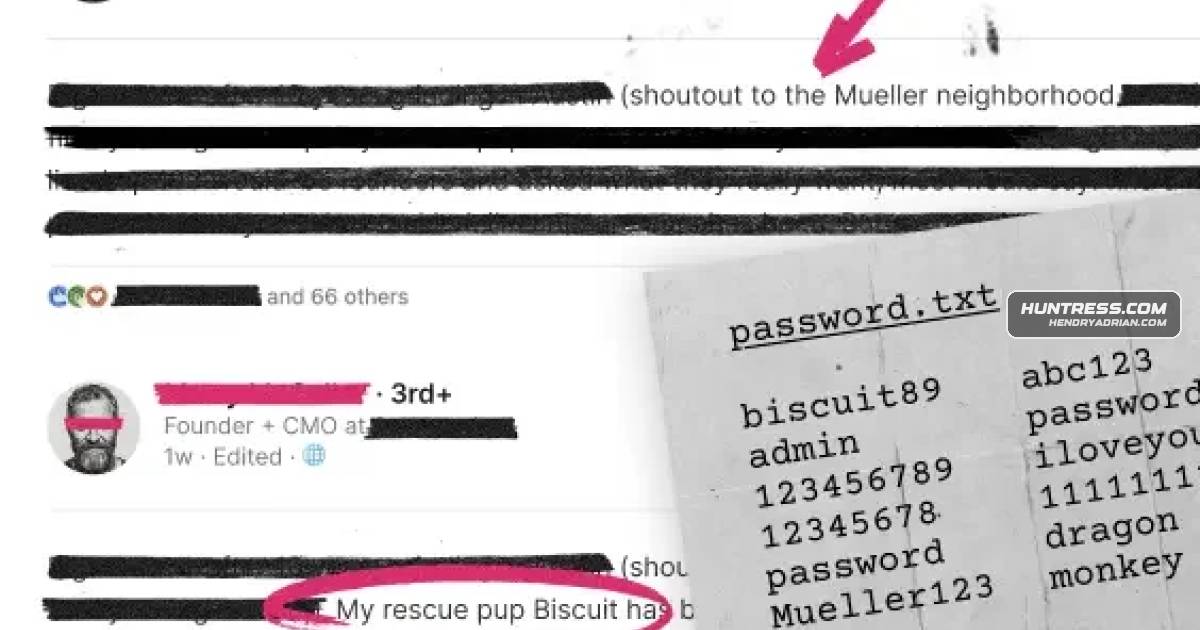
How Attackers Turn Public Profiles Into Targeted Cyberattacks

Public posts, directories, and breach data can help attackers build dossiers for targeted phishing and impersonation. The article shares examples and advice for limiting exposure, including a family safe word and stronger security-question answers.

May 28, 2026
Security Insights · threatfabric.com

Becky Holmes on Evolving Fraud and Why Prevention Needs a Human Touch

In a Fusion Fireside episode, Becky Holmes discusses how AI, cryptocurrency, and social media are changing fraud, and why prevention needs better collaboration, victim insight, and attention to shame and stigma.

May 28, 2026
Security Insights · netspi.com

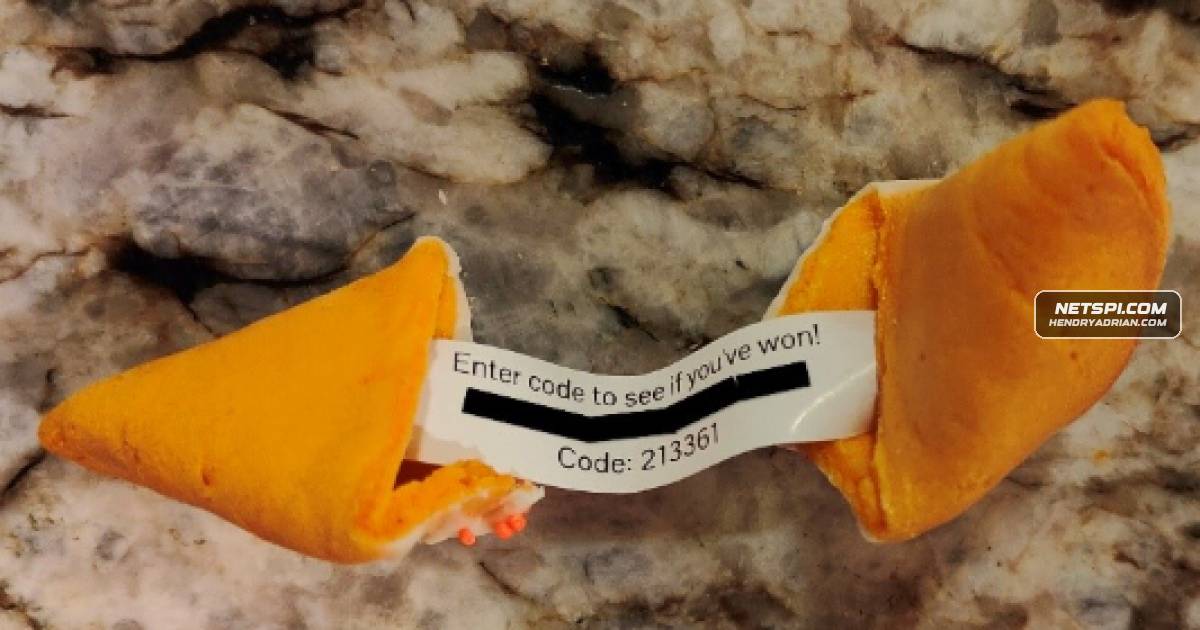
NetSPI Test Uses Fortune Cookies to Phish Employees, Harvesting 10 Credentials

A NetSPI social-engineering test used fortune cookies and a fake $50 Amazon gift-card promotion to phish employees. Evilginx captured credentials from 10 of 48 cookies, including submissions after the tester was identified.

May 27, 2026
Security Insights · wiz.io

Wiz Outlines Four Pillars for Defending Against AI-Speed Cyber Threats

Wiz presents a four-pillar approach to AI threat readiness: reduce and validate exposures, accelerate remediation, analyze code with environmental context, and detect and contain runtime threats.

May 27, 2026
Security Insights · darkowl.com

Social Engineering Is Becoming More Contextual and Harder to Spot

The article explains how social engineering uses personalized context, polished AI-generated messages, cross-channel interactions, impersonation, and pressure around MFA to make malicious requests feel routine and harder to detect.

May 27, 2026
Security Insights · huntress.com

MSPs Should Assess Operational Readiness Before Pursuing CMMC Work

The article advises MSPs to assess governance, data handling, access controls, evidence practices, and incident response readiness before taking on CMMC work, including the 72-hour incident reporting requirement.

May 27, 2026
Security Insights · darktrace.com

How Security Teams Can Evaluate AI Vendors for Safe Adoption

Darktrace outlines five areas for evaluating AI vendors: governance and data controls, training data, model choice, performance validation, and interpretability. The guide highlights buyer concerns about trust and autonomous AI actions in security workflows.

May 27, 2026
Security Insights · team-cymru.com

Team Cymru Says External Threat Visibility Is a Critical Gap for Defenders

Team Cymru argues that internal-focused security leaves organizations exposed to threats staged outside their networks, citing DBIR and survey figures on ransomware, RMM abuse, third-party breaches, and limited external visibility.

May 27, 2026
Security Insights · decodedsecurity.com

A Beginner’s Roadmap to Penetration Testing

A cybersecurity manager outlines a beginner’s penetration-testing study plan: learn security and systems fundamentals, progress through practical certifications, practice on training platforms, and build a portfolio.

May 26, 2026
Security Insights · huntress.com

How Stolen Session Tokens Let Attackers Bypass Passwords and MFA

Infostealers can steal active session tokens and cookies, letting attackers access accounts without re-entering passwords or triggering MFA. The article explains the resale market and recommends short-lived sessions and anomalous-behavior monitoring.

May 26, 2026
Security Insights · darktrace.com

How Darktrace / EMAIL Analyzes and Responds to a Malicious Email

Darktrace describes how its email security product processes a sample extortion email, from extracting message data and analyzing user behavior to identifying a campaign and holding related emails.

May 26, 2026
Security Insights · thehackernews.com

Why AI-Driven Vulnerability Discovery Makes Patch-Only Security Unsustainable

A RunSafe Security founder argues that AI-driven vulnerability discovery is widening the gap between findings and remediation, and that runtime protections can reduce exploitability when patches are delayed.

May 25, 2026
Security Insights · toxsec.com

How STRIDE-AI, MAESTRO and ASTRIDE Extend Threat Modeling for AI Applications

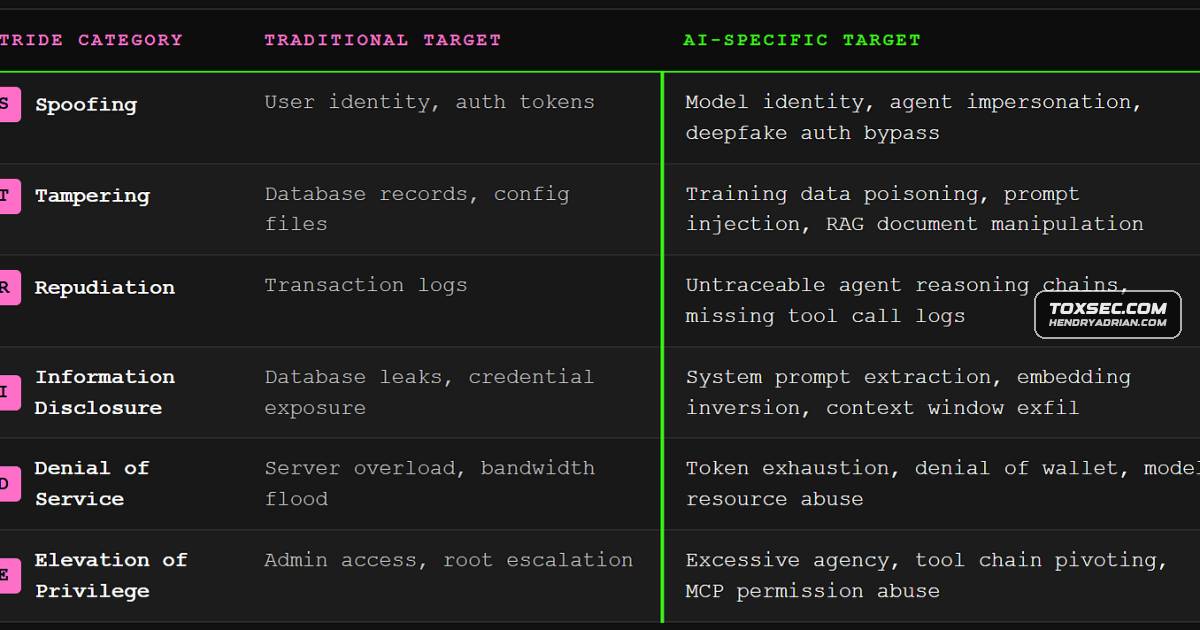
The article explains how AI changes traditional STRIDE threat modeling and introduces STRIDE-AI, ASTRIDE and MAESTRO, with examples and questions for assessing risks across AI models, data, prompts and agent tools.

May 23, 2026
Security Insights · matthewrosenquist.substack.com

AI-Driven Exploitation Could Outpace Business-Limited Patching

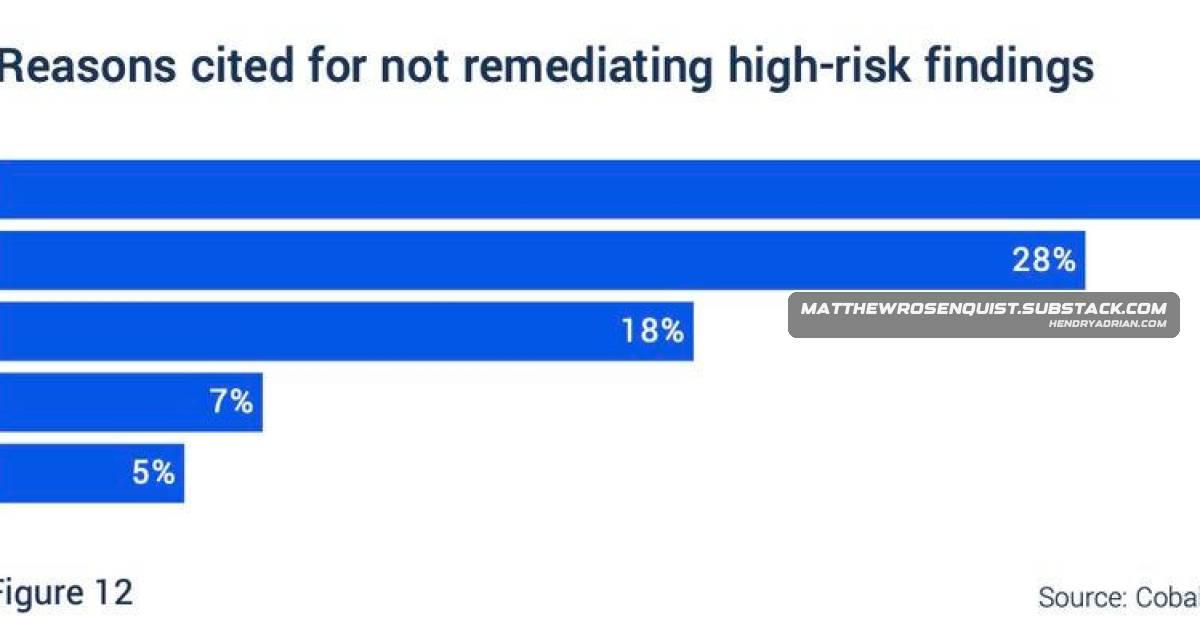
The article argues that AI may accelerate vulnerability discovery and exploitation beyond current patching cycles. It cites a survey of 450 security professionals in which business disruption was the most cited reason vulnerabilities go unfixed, and calls for stronger,`

May 22, 2026
Security Insights · decodedsecurity.com

PKI Explained: How Trusted Certificates Verify Online Identities

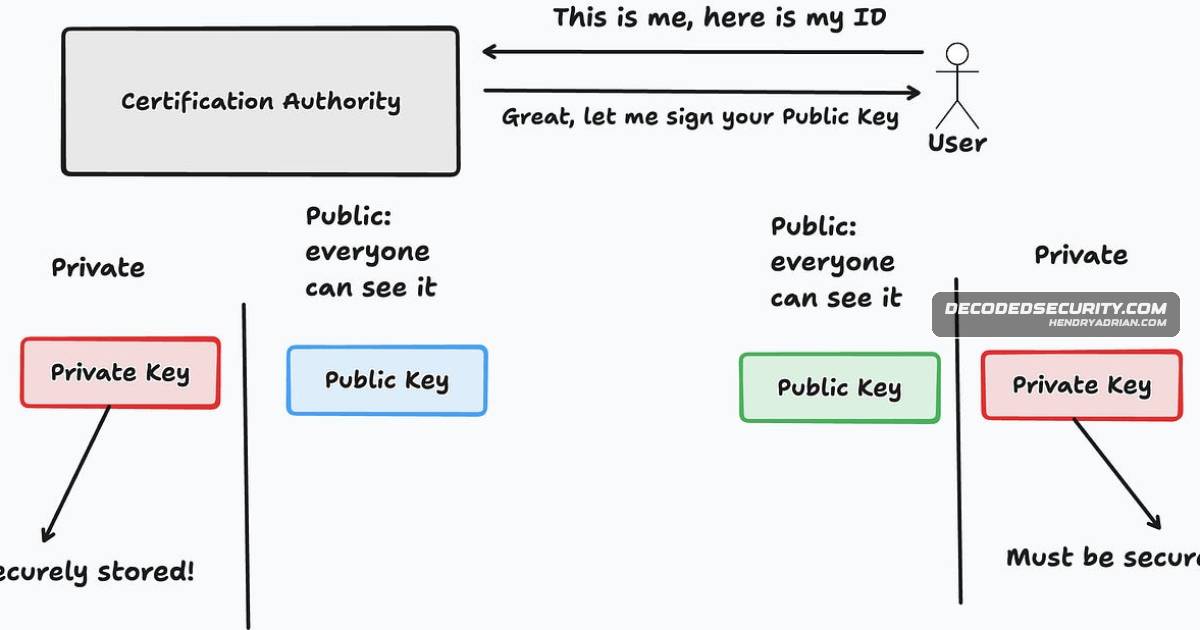
A beginner-friendly explanation of how Public Key Infrastructure uses trusted Certificate Authorities to sign certificates that bind public keys to identities, supporting trust in digital communications.

May 22, 2026
Security Insights · zscaler.com

Zscaler Says Frontier AI Could Help Defenders Analyze Exposure and Attack Paths

Zscaler argues that frontier AI could help defenders improve speed and precision by understanding exposure and reasoning across attack paths, while warning that adversaries may seek similar advantages.

May 22, 2026
Security Insights · hackingarticles.in

Windows UAC Bypass Techniques and Defenses

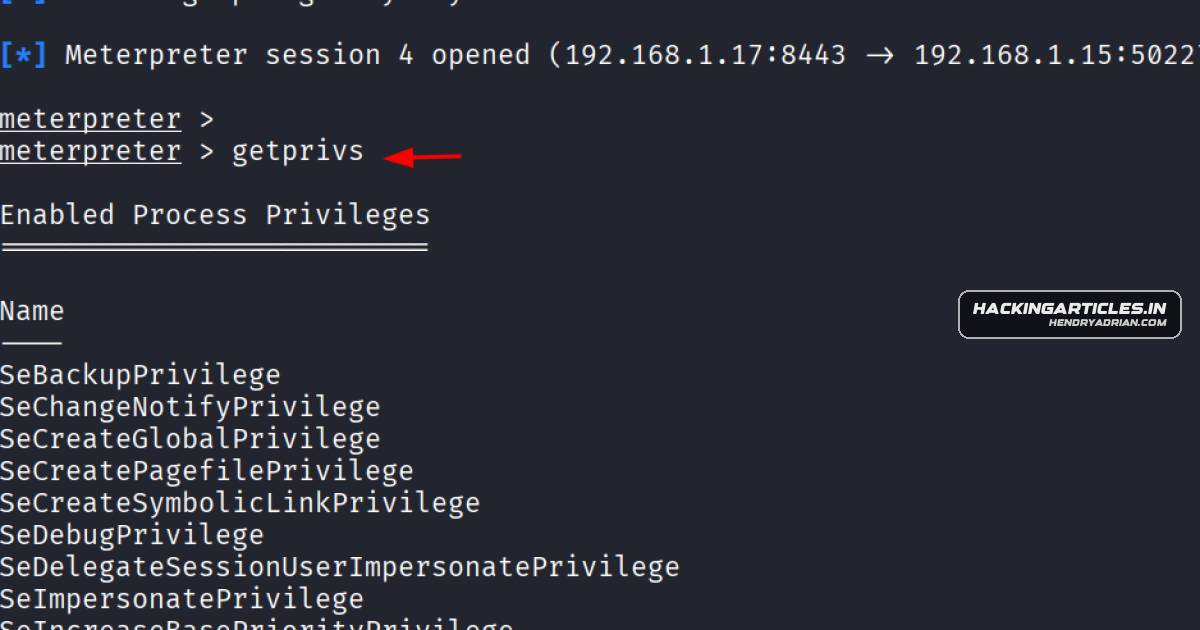
A lab walkthrough demonstrates UAC bypasses on a default-configured Windows 10 host, elevating a medium-integrity administrator session. It also recommends least privilege, registry monitoring, PowerShell logging, application control and patching.

May 21, 2026
Security Insights · cyberscoop.com

The Readiness Paradox: Cyber Confidence Can Mask Weak Resilience

The article argues that compliance and confidence can obscure weak cyber resilience amid AI-driven threats, expanding attack surfaces and alert overload. It recommends continuously mapping connected assets and prioritizing exposure by business impact.

May 21, 2026
Security Insights · darkowl.com

Common Web Application Attacks: How They Work and How to Reduce Risk

An explainer covers SQL injection, XSS, broken access control and authentication, and CSRF, with examples of major incidents and guidance on reducing risk through secure development, testing, patching, and strong authentication.

May 21, 2026
PreviousPage 29 of 54 Next
© 2026 cyber.hendryadrian.com