
AI-Driven Exploitation Could Outpace Business-Limited Patching
Summary
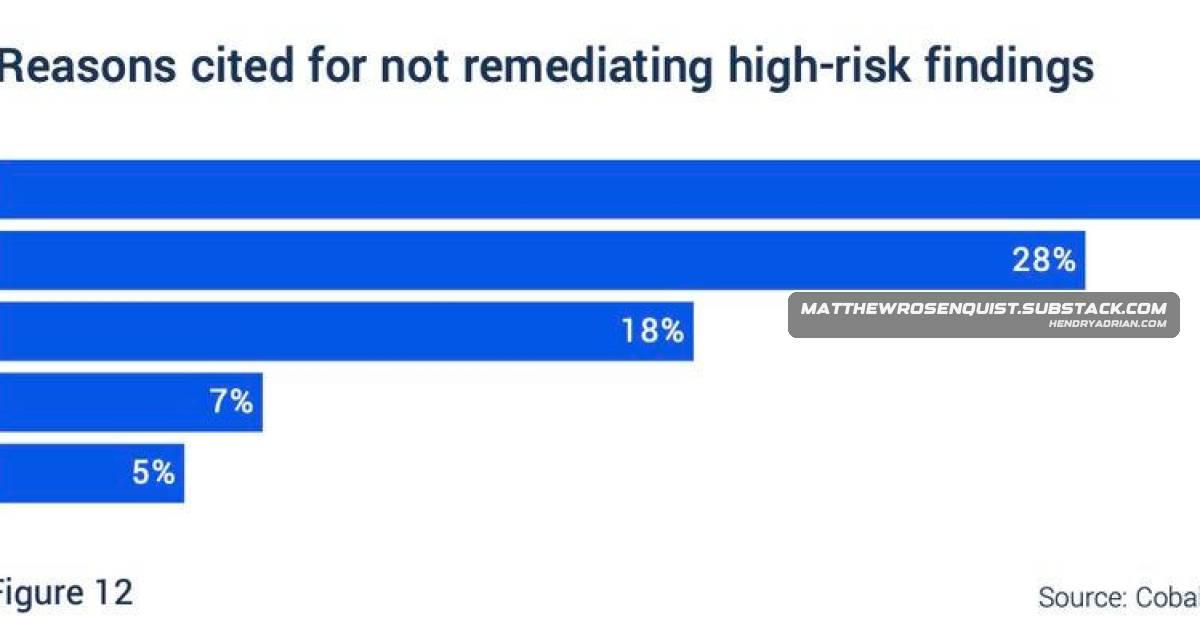
The article argues that AI may accelerate vulnerability discovery and exploitation beyond current patching cycles. It cites a survey of 450 security professionals in which business disruption was the most cited reason vulnerabilities go unfixed, and calls for stronger,`
Key points
- The article warns that AI-powered tools could find and exploit vulnerabilities faster than organizations can remediate them.
- It argues that technical remediation is only part of the problem; staffing, process delays, and business priorities also constrain patching.
- The author says customer concerns about downtime and performance can lead organizations to bundle or delay patches.
- A Cobalt and Cyentia Institute survey of 450 security professionals reportedly found business disruption was the most cited reason vulnerabilities are not fixed.
- The article recommends new defensive tools, revised remediation processes, dedicated oversight resources, and changed expectations about operational disruption.
Article Details
- Topic
- AI-enabled vulnerability discovery and exploitation outpacing organizational vulnerability remediation