How Stolen Session Tokens Let Attackers Bypass Passwords and MFA
Summary
Infostealers can steal active session tokens and cookies, letting attackers access accounts without re-entering passwords or triggering MFA. The article explains the resale market and recommends short-lived sessions and anomalous-behavior monitoring.
Key points
- Session hijacking uses stolen authentication cookies or tokens to access an already authenticated account, often without another password or MFA prompt.
- Infostealers collect session data, credentials, developer tokens, and password-manager vaults from browsers and apps.
- Stolen logs and access data are traded on underground markets, with prices varying by freshness, data type, and access value.
- Attackers can replay stolen sessions to access cloud, email, collaboration, and developer environments, potentially leading to data theft or ransomware.
- A password reset may not invalidate existing sessions unless tokens are explicitly revoked or expire under policy.
- The article recommends short session lifetimes, secure cookie settings, anomaly monitoring, MFA, and user education.
Article Details
- Topic
- Session hijacking through stolen browser session tokens and authentication cookies, including their use in session replay attacks.
MITRE ATT&CK
T1528 · Steal Application Access TokenAttackers steal application access tokens, including developer tokens, to gain unauthorized access.T1539 · Steal Web Session CookieAttackers steal browser session cookies to access users' authenticated sessions.T1550.004 · Web Session CookieAttackers replay stolen web session cookies to access accounts without repeating authentication.
People
Malware
Products
AWSDeveloper tokens for GitHub, AWS, or CI/CD systemsGitHubDeveloper tokens for GitHub, AWS, or CI/CD systemsGoogle WorkspaceSession cookies from Google Workspace, Microsoft 365, Slack, and moreMicrosoft 365 Apps for EnterpriseLogs containing valid session tokens for tools like Microsoft 365 or Slack sell for as little as $5 on dark web markets and as much as $500 for high-value targets.OktaLogs containing Fortune 500 credentials, valid Microsoft 365 sessions, or tokens for tools like Slack, Okta, or AWS can sell for $100 to over $500, depending on exclusivity.SlackLogs containing valid session tokens for tools like Microsoft 365 or Slack sell for as little as $5 on dark web markets and as much as $500 for high-value targets.
Tools
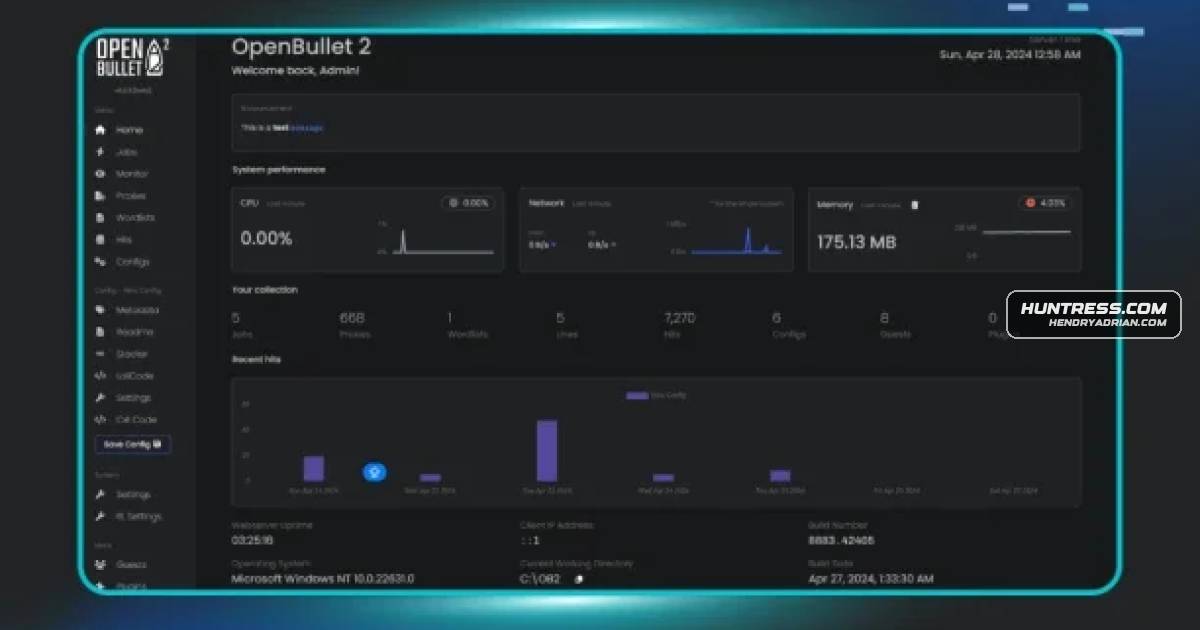
OpenBulletOpenBullet Configs (pre-built for Shopify, AWS, GitHub, etc.): $20-$150 eachOpenBullet2Figure 7: Hackers use OpenBullet2 for credential stuffing and session replayStealyBotThey use tools like OpenBullet, StealyBot, or custom replay scripts to simulate logins, bypassing authentication in under an hour.