cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · securityweek.com

Supply Chain Vulnerability Risk Grows as Exploitation Outpaces Visibility

Black Kite’s 2026 report says over 48,000 CVEs were published in 2025, but only 58 of 1,024 prioritized CVEs were readily discoverable to attackers. The article examines shrinking patch windows, AI-related exposure and visibility gaps.
May 21, 2026
Security Insights · hackingarticles.in

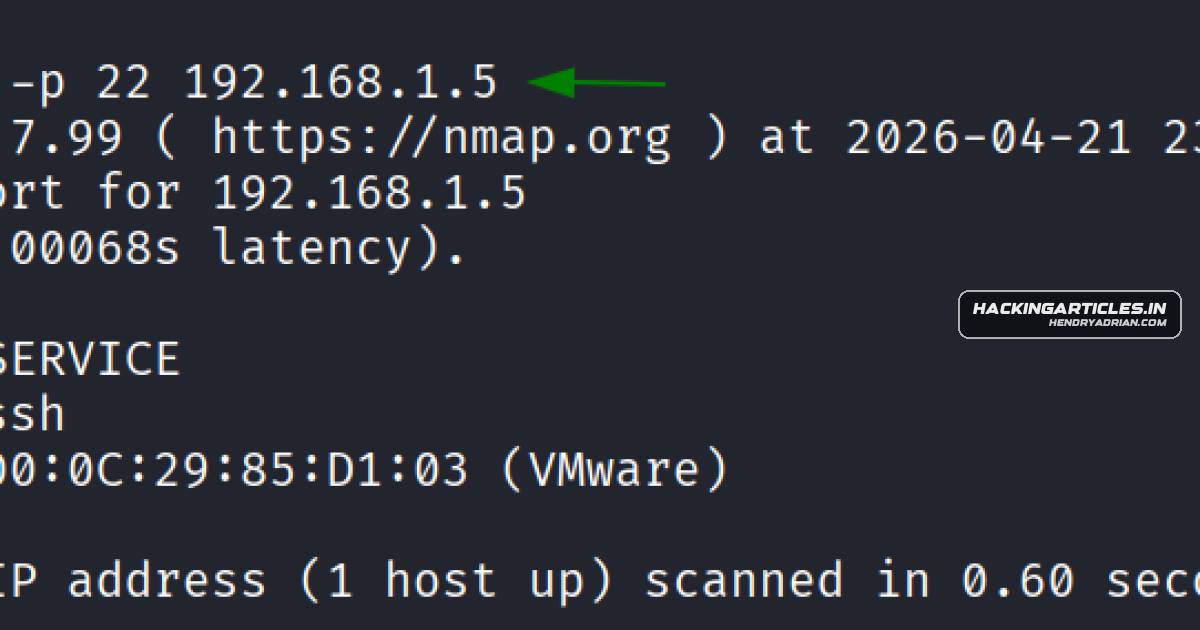
Nmap Firewall-Evasion Walkthrough Shows Limits of Static iptables Rules

A lab walkthrough demonstrates how Nmap scans evade static iptables rules by varying TCP flags, packet length, TTL, source fields, payloads and options. It recommends stateful inspection, IDS/IPS, rate limiting and host monitoring.

May 21, 2026
Security Insights · huntress.com

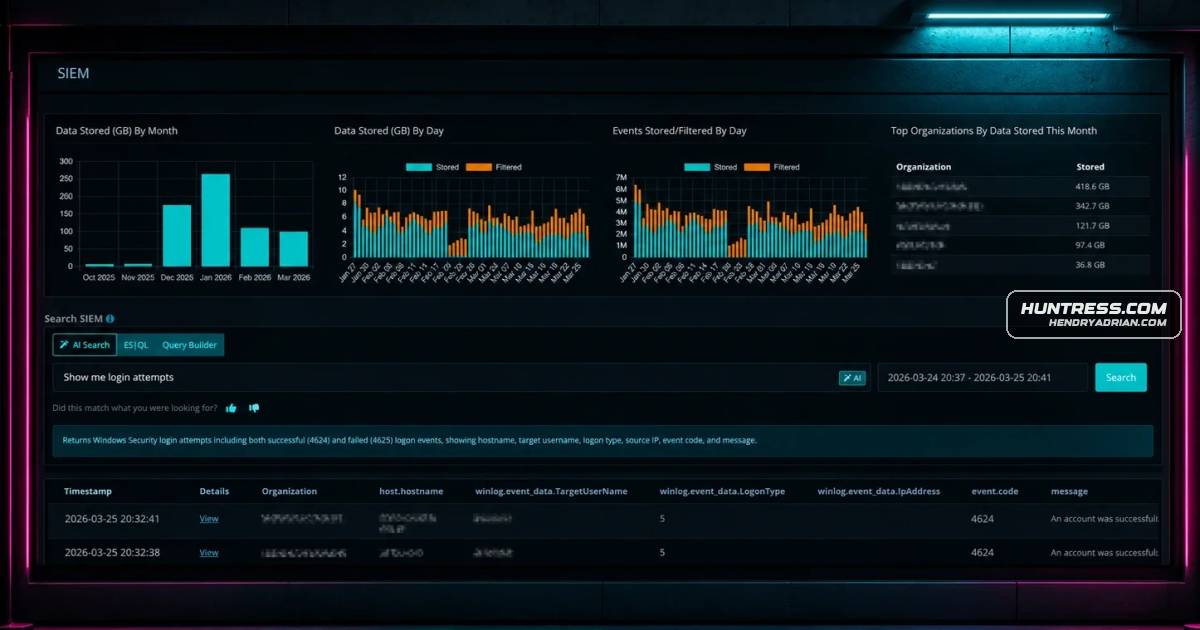
How Huntress Uses Managed SIEM to Speed Threat Detection and Investigations

Huntress describes how its teams use Managed SIEM to investigate incidents, correlate logs, and detect threats. In one case, EDR stopped a malware infection and SIEM logs helped confirm no data was exfiltrated.

May 21, 2026
Security Insights · securityweek.com

How Security Teams Can Prepare for AI Applications in Production

The article recommends preparing to secure AI applications before they reach production by involving security teams early, strengthening operational workflows, maintaining application and API security, and adding proactive scanning and AI-aware runtime monitoring.

May 20, 2026
Security Insights · securityweek.com

ICS Security Practitioners Share Real-World OT Risks and Lessons

Practitioners recount ICS/OT risks including IT-to-OT access attempts, a scan that stopped turbines, internet-reachable systems with default credentials, hidden assets and suspicious DNS traffic. Their experiences underscore inventory, monitoring and careful network and

May 20, 2026
Security Insights · huntress.com

Ransomware Affiliates Use Varied Intrusion Tactics, Huntress Says

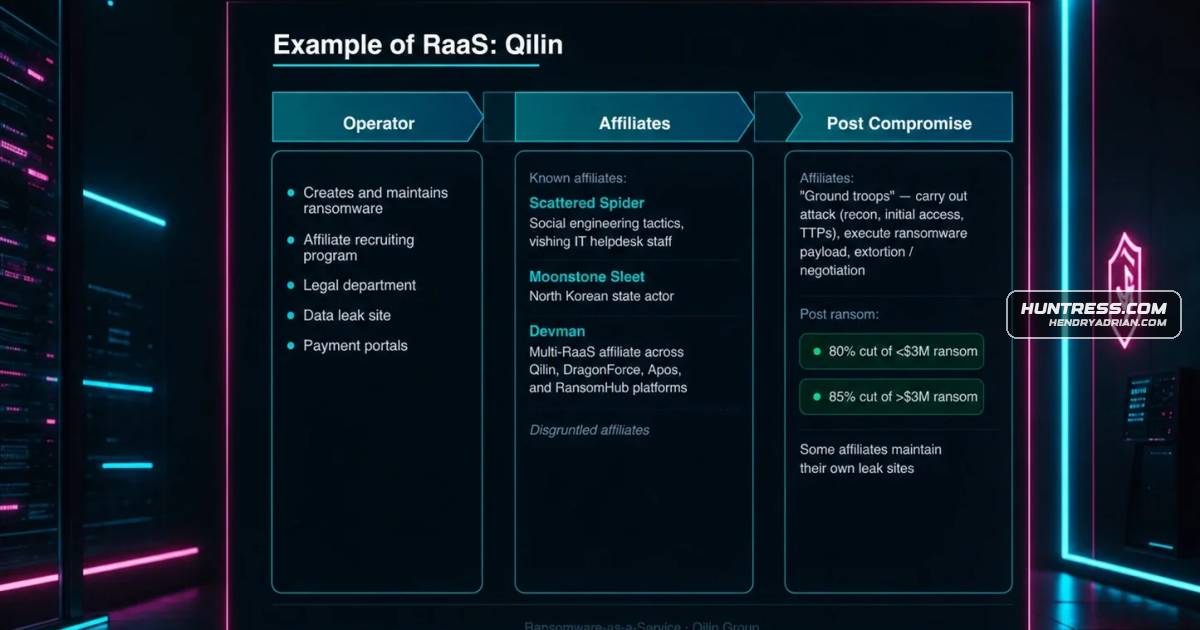
Huntress explains that RaaS affiliates use varied access and intrusion methods, so a ransomware brand alone does not reveal an attack’s path. It highlights common tactics and recommends broad monitoring and sound security fundamentals.

May 20, 2026
Security Insights · thehackernews.com

EvilTokens OAuth Phishing Reportedly Compromises 340+ Microsoft 365 Organizations

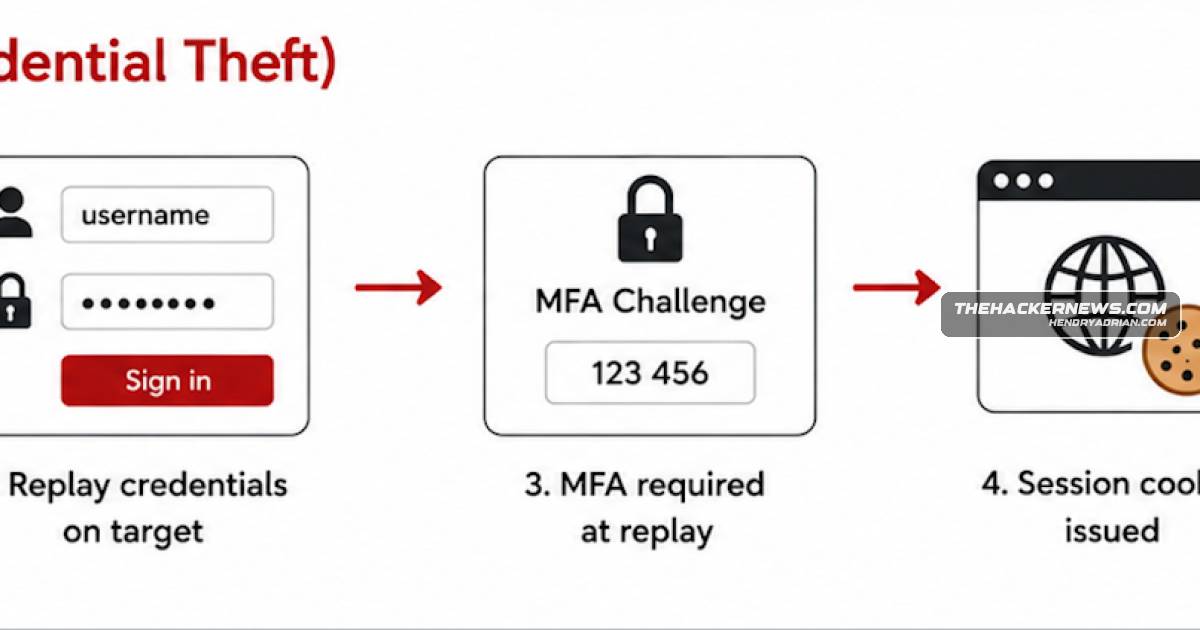
The article says EvilTokens used OAuth consent phishing to obtain refresh tokens from users at more than 340 Microsoft 365 organizations. The tokens could evade MFA protections and survive password resets; recommended defenses include grant monitoring and token-level re

May 19, 2026
Security Insights · hackingarticles.in

NetExec Walkthrough Demonstrates Active Directory Lab Compromise and Defenses

A hands-on NetExec tutorial walks through compromising a Windows Server 2019 Active Directory lab from low-privileged credentials to domain control and SYSTEM on an MSSQL host, then maps the chain to hardening and detection measures.

May 19, 2026
Security Insights · toxsec.com

How the CIA Triad Maps to LLM Security Risks

The article maps LLM security failures to confidentiality, integrity and availability, describing prompt and chat-history leaks, prompt injection and poisoning, and costly inference DoS. It also argues the triad misses probabilistic and cognitive risks.

May 18, 2026
Security Insights · thehackernews.com

Developer Workstations Emerge as Software Supply Chain Targets

The article reports campaigns targeting secrets in developer environments and CI/CD across npm, PyPI and Docker Hub, and argues that workstations should be treated as a local software supply chain boundary.

May 18, 2026
Security Insights · cyberscoop.com

Canvas Breach Highlights Need for SaaS Security Beyond Prevention

An op-ed says ShinyHunters used compromised Free-For-Teacher accounts to breach Canvas and steal data, arguing for stronger identity governance, reduced access, cryptographic protections and post-quantum planning.

May 18, 2026
Security Insights · thehackernews.com

Why Non-Human Identity Governance Must Go Beyond Secret Vaulting

The article argues that growing non-human identities (NHIs), including service accounts, tokens and AI agents, create security and compliance risks when ownership, lifecycle controls and auditability are weak; it recommends governance beyond secret vaulting.

May 18, 2026
Security Insights · trendmicro.com

How Security Teams Can Govern AI Agents With Credentials and Business-System Access

AI agents can misuse delegated credentials, follow prompt-injection instructions, and trigger rapid changes. The article recommends inventorying agents, assigning owners, limiting permissions by action, gating risky operations, and keeping linked audit evidence.

May 18, 2026
Security Insights · recordedfuture.com

How AI and Threat Intelligence Could Make Cyber Defense More Adaptive

The article argues that combining AI with threat intelligence could help defenders prioritize real exposure, anticipate attacker actions and deploy adaptive deception, while warning about containment, governance and intelligence-quality risks.

May 15, 2026
Security Insights · huntress.com

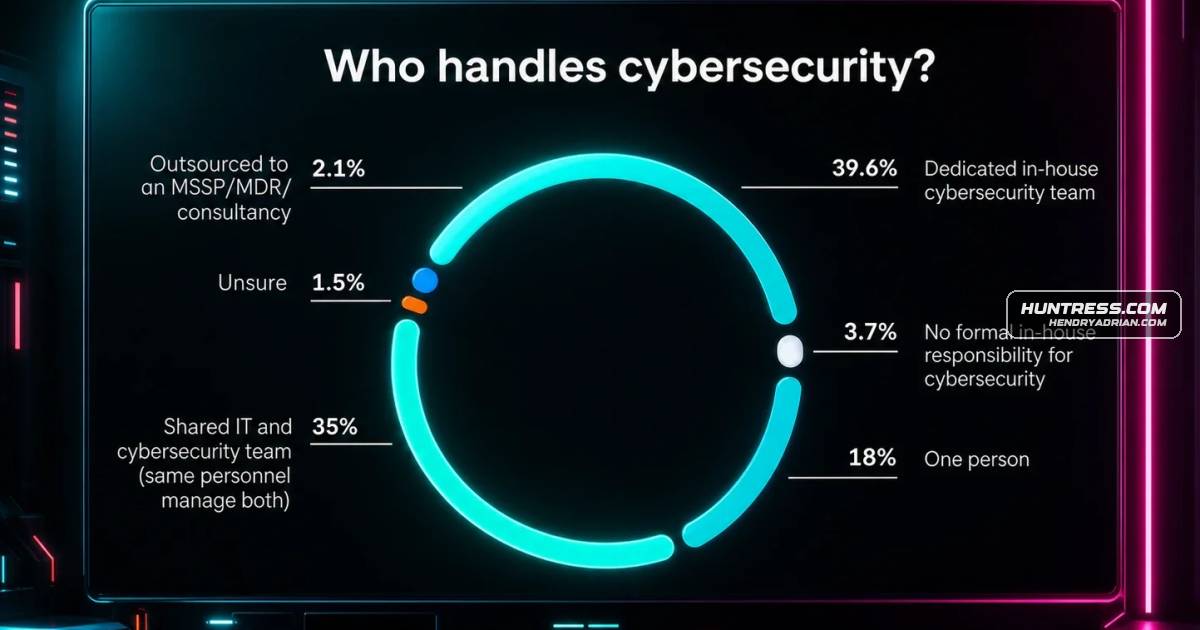
How to Build a Resilient Security Stack and Team

Huntress discusses how security teams can improve resilience by reducing alert noise, clarifying ownership, strengthening identity and asset visibility, and pairing security tools with workflows that support timely response.

May 15, 2026
Security Insights · huntress.com

What Single Sign-On Is and How It Works

An overview of single sign-on (SSO), explaining its authentication flow, common protocols, benefits and risks, and considerations for implementing it securely, including MFA, session timeouts, and least privilege.

May 15, 2026
Security Insights · huntress.com

19 Cloud Security Risks and Ways to Reduce Them

An overview of 19 cloud security risks, including misconfigurations, excessive access, account hijacking, insecure APIs, ransomware and MFA fatigue, with basic guidance on limiting access and monitoring cloud settings.

May 15, 2026
Security Insights · bleepingcomputer.com

How Cybercriminals Use Phishing and Email Compromise to Steal Freight

NMFTA explains how criminals use phishing, compromised email and fraudulent carrier identities to reroute freight, and recommends stronger authentication, out-of-band verification and industry-focused security guidance.

May 14, 2026
Security Insights · sentinelone.com

LABScon Talk Tests Whether Public Breach Signals Can Predict Stock-Market Moves

A LABScon25 presentation examines whether public indicators of cyber breaches can anticipate market reactions, testing a “15/30” trading hypothesis with breach disclosures and time-series analysis. Results were mixed.

May 14, 2026
Security Insights · darkowl.com

Data Extortion Cases Show How Attackers Steal and Weaponize Sensitive Information

The article reviews extortion incidents involving Vastaamo, Salesforce-connected data, Jaguar Land Rover and Oracle E-Business Suite, then outlines steps organizations can take to contain breaches, investigate exposure and notify affected parties.

May 14, 2026
Security Insights · huntress.com

CMMC Final Rule: Requirements and Preparation for DoD Subcontractors

A guide to CMMC requirements for DoD contractors, covering certification levels, rollout and subcontractor flow-downs, Level 2 assessment expectations, and steps organizations can take to prepare.

May 14, 2026
Security Insights · cyberscoop.com

Incode Executive Recommends Faster Defenses Against AI-Driven Identity Fraud

An Incode strategy executive argues that AI-enabled impersonation and synthetic-identity fraud require defenses updated within 7–10 days, and urges enterprises to assess identity-verification vendors on certifications, error reporting, update speed and intelligence分享.

May 13, 2026
Security Insights · decodedsecurity.com

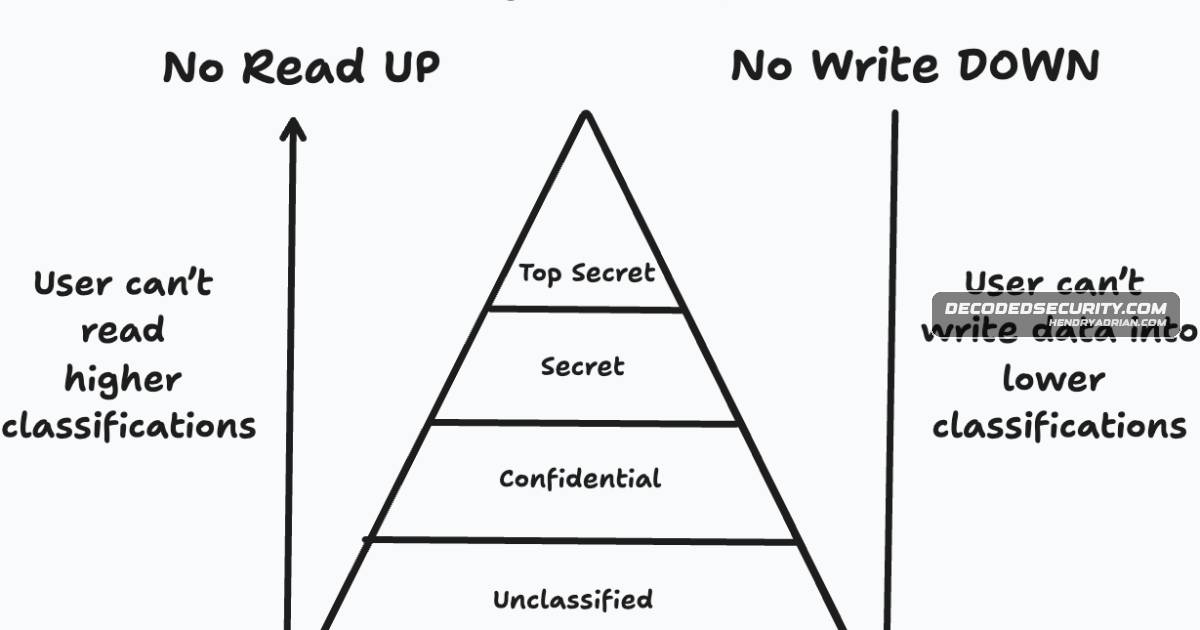
CISSP Guide Maps Security Models to Confidentiality and Integrity Scenarios

A CISSP study guide offers a scenario-based way to distinguish security models by whether they protect confidentiality or integrity, explaining Bell-LaPadula, Biba, Clark-Wilson, Brewer-Nash, Graham-Denning, and Take-Grant.

May 13, 2026
Security Insights · cybersecuritypulse.net

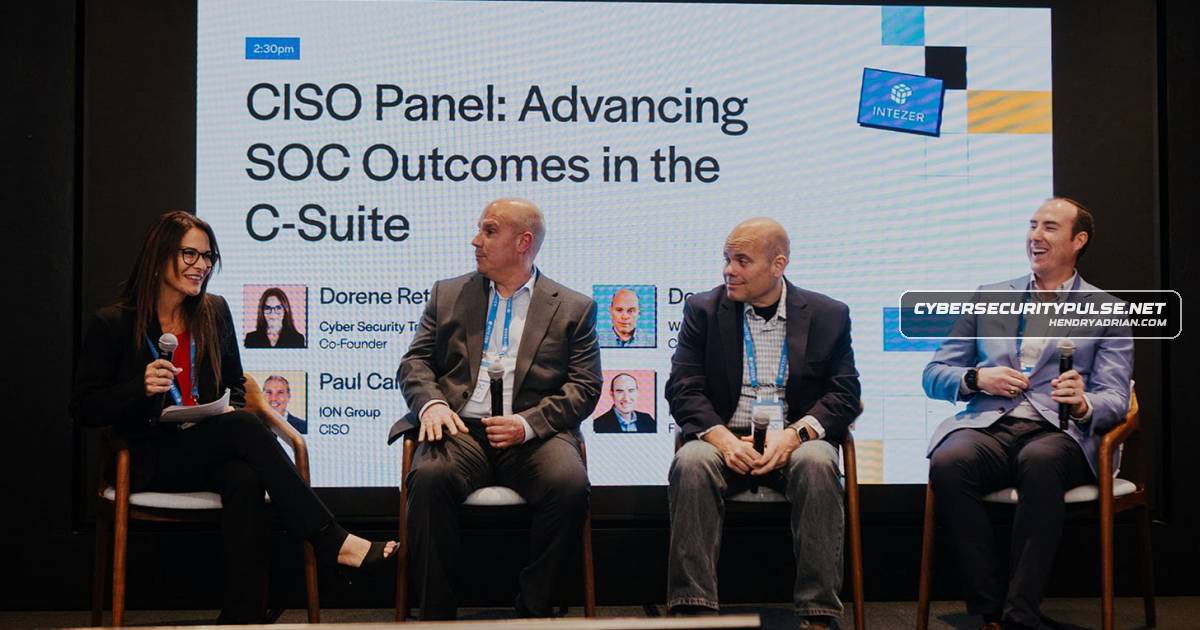
CISO Takeaways on AI SOCs, Security Budgets and SOC Metrics

Drawing on an Intezer AI SOC event, the author argues that AI is changing SOC operations, security budgets and vendor contracts. The article highlights a proposed executive metric, AVERT, and the importance of mature SOC foundations.

May 13, 2026
PreviousPage 30 of 54 Next
© 2026 cyber.hendryadrian.com