
NetSPI Test Uses Fortune Cookies to Phish Employees, Harvesting 10 Credentials
Summary
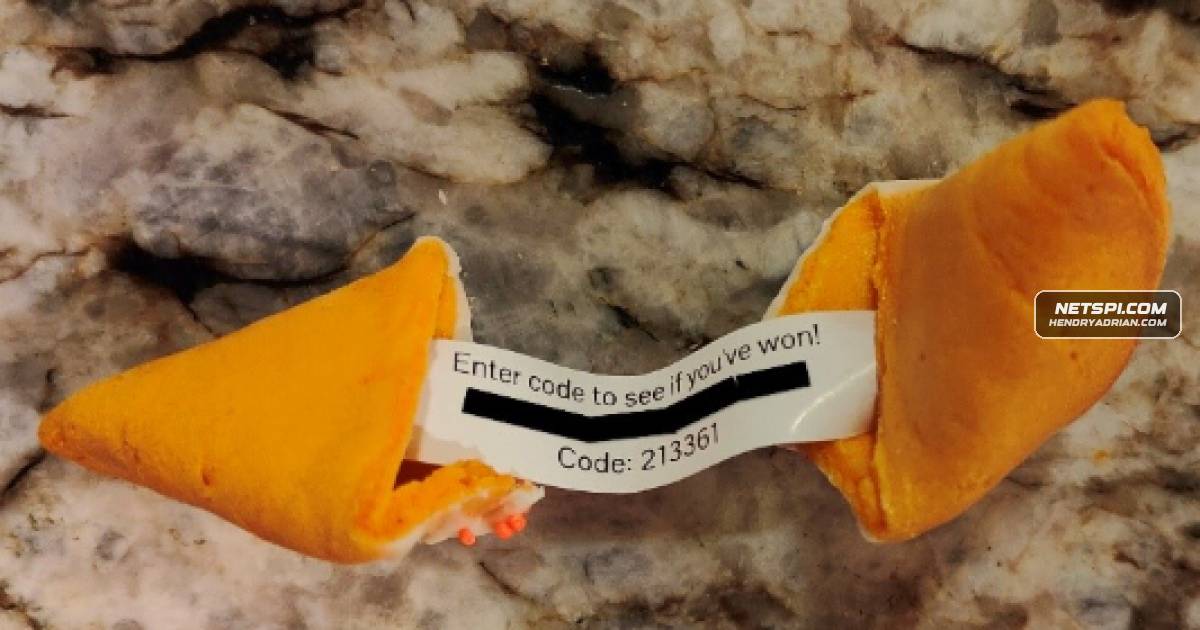
A NetSPI social-engineering test used fortune cookies and a fake $50 Amazon gift-card promotion to phish employees. Evilginx captured credentials from 10 of 48 cookies, including submissions after the tester was identified.
Key points
- The test used custom fortune cookies at a client site to promote a fake $50 Amazon gift-card giveaway.
- Cookie links led to a code-entry page and then an impersonated company login; Evilginx was used to capture sessions.
- Ten of 48 cookies resulted in harvested employee credentials, including submissions after the tester was identified.
- The tester used fake employee IDs and tailgated into the site, but was identified and escorted to HR within one to two hours.
- The article recommends accounting for physical phishing lures, mailed treats and QR codes in security-awareness training.
Article Details
- Topic
- A physical social-engineering phishing test used fortune cookies and a fake gift-card promotion to harvest employee credentials.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cookiegiveaways[.]com | Identified as the malicious phishing site used in the test to collect employee credentials. |
MITRE ATT&CK
T1185 · Browser Session HijackingEvilginx was used in the impersonated login flow to capture victims' sessions.T1204 · User ExecutionThe phishing required employees to take a cookie, enter its code, follow the link, and sign in.T1566.002 · Spearphishing LinkThe fortune cookies directed targets to a malicious link.