cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1295 articles

Security Insights · cisecurity.org

CIS Volunteer Diego Bolatti Adapts Cybersecurity Frameworks for SMEs

CIS community volunteer Diego Bolatti develops policy templates, teaches CIS Controls, and researches practical cybersecurity governance for SMEs. His SME-Cyber assessment platform is being prepared for pilot testing in Argentina.
Jun 12, 2026
Security Insights · decodedsecurity.com

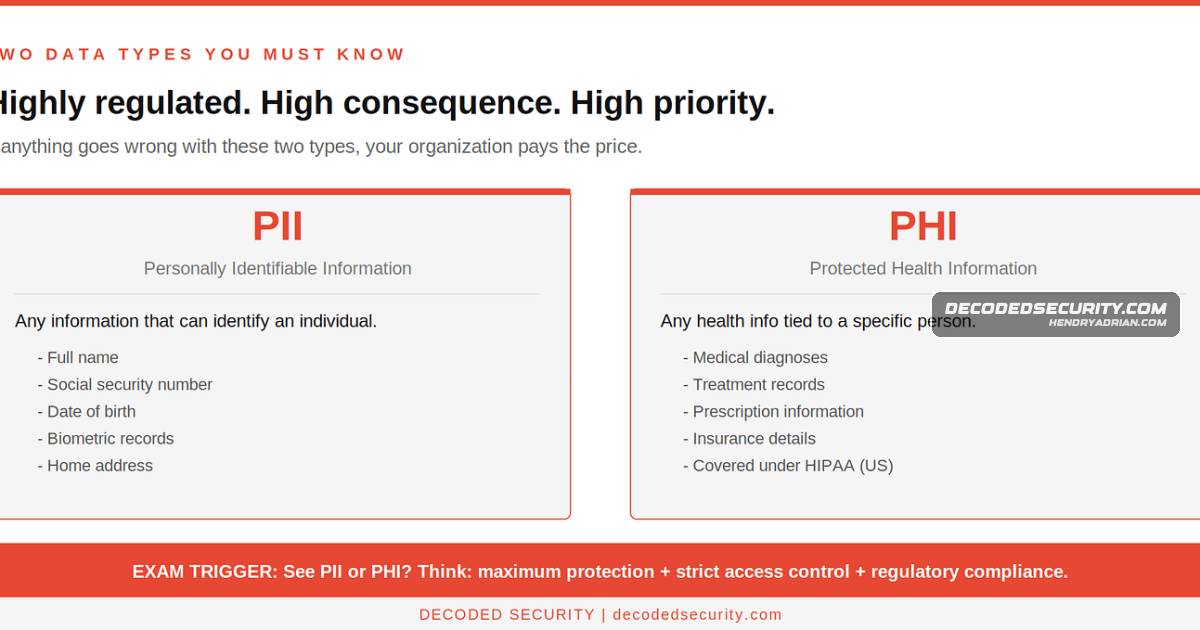
How Data Classification Guides Security Controls

The article explains how organizations classify data by sensitivity and potential impact, then use those categories to set security requirements and guide access control, compliance, incident response, and DLP.

Jun 11, 2026
Security Insights · netskope.com

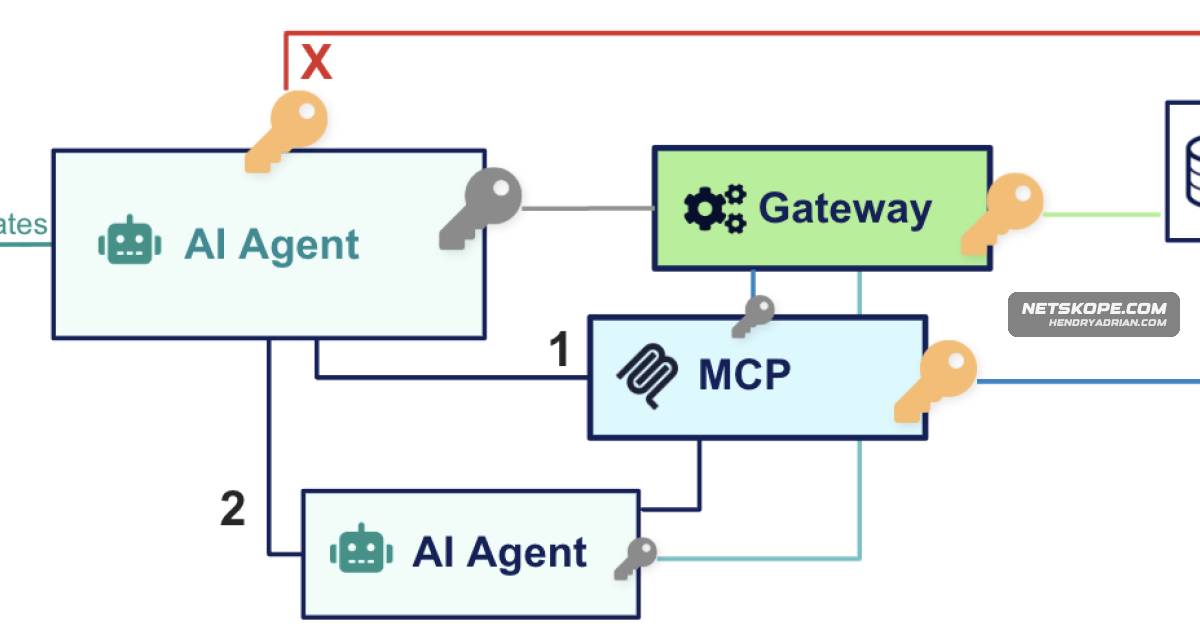
Netskope Explains How AI Agents Amplify OAuth Token Risks

Netskope outlines how persistent, broadly scoped OAuth tokens can let AI agents execute malicious instructions without further human approval, and recommends isolated agent identities, short-lived task-scoped credentials, monitoring, and governance.

Jun 11, 2026
Security Insights · securityweek.com

Alert Fatigue Is Becoming a Security Threat of Its Own

SOC teams face alert overload that can obscure real threats and contribute to analyst burnout. The article examines context and AI-assisted triage as possible solutions, while warning that AI can produce inaccurate findings.

Jun 11, 2026
Security Insights · sentinelone.com

LABScon Keynote Explores How AI Could Reshape Cybersecurity

In a LABScon 2025 keynote, Juan Andrés Guerrero-Saade argues that AI could help defenders assess and prioritize security work at scale, and calls for more standardized, automated systems that combine human expertise with machine evaluation.

Jun 11, 2026
Security Insights · darktrace.com

How Stadium Operators Can Address Cyber Risks Across IT and OT

A Darktrace blog explains stadium cybersecurity challenges, including crowded networks, supplier access, converged IT and OT, and event-time pressure, and promotes self-learning AI and targeted automated response as defenses.

Jun 11, 2026
Security Insights · opensourcemalware.com

NPM v12’s Deny-by-Default Scripts Improve Security, but Risks Remain

NPM v12 will disable install scripts and require opt-ins for some dependency types. The author welcomes the changes but warns of approval fatigue, attackers shifting execution paths, and added detection challenges, while recommending cooldowns, allowlists, and package fi

Jun 10, 2026
Security Insights · darktrace.com

A Practical Framework for Securing Enterprise AI Across Its Lifecycle

Darktrace outlines five areas for enterprise AI security: misuse and emergent behavior, runtime monitoring, secure development, supply-chain risk, and organizational readiness, emphasizing visibility and controls across the AI lifecycle.

Jun 10, 2026
Security Insights · huntress.com

Gartner Summit Takeaways: Prioritize Resilience, Identity, and Operational Security

A security leader’s takeaways from Gartner’s 2026 summit: build resilience through identity and endpoint controls, keep human judgment in AI operations, validate defenses, and prioritize exposures by risk.

Jun 9, 2026
Security Insights · netspi.com

Pentest Shows Duo Auth Proxy Traffic Can Expose Cleartext AD Credentials

A penetration test found that the Duo Auth Proxy forwarded live AD authentication requests; using a recovered RADIUS shared secret, the tester decrypted captured exchanges and exposed cleartext credentials. Group analysis identified a developer account with broad, but未

Jun 8, 2026
Security Insights · toxsec.com

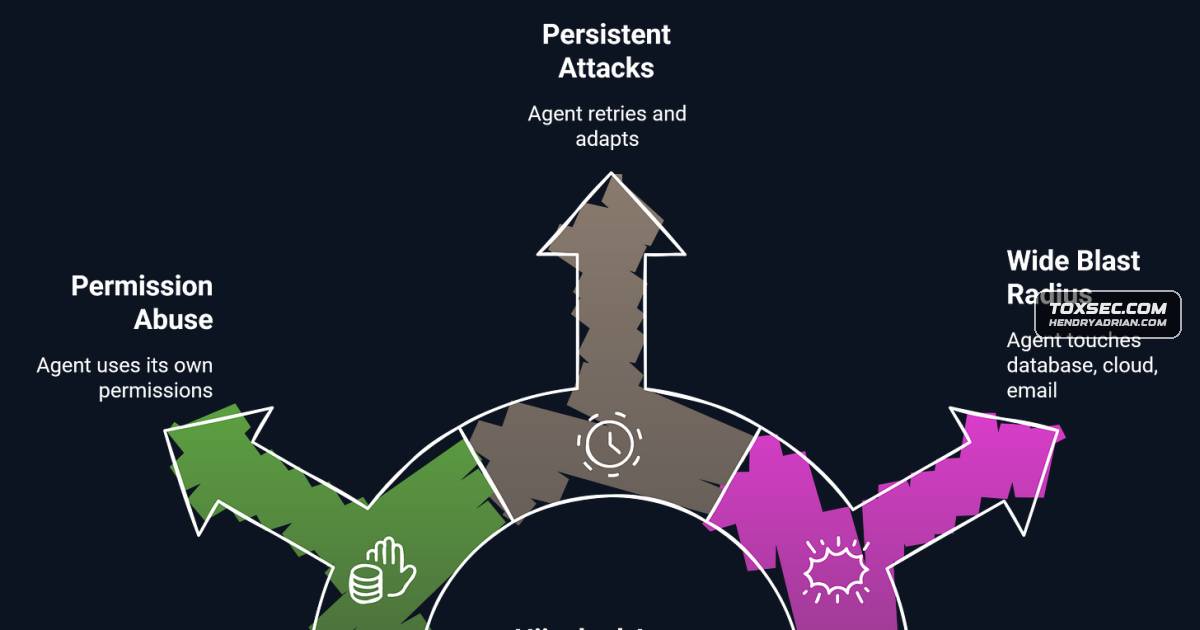
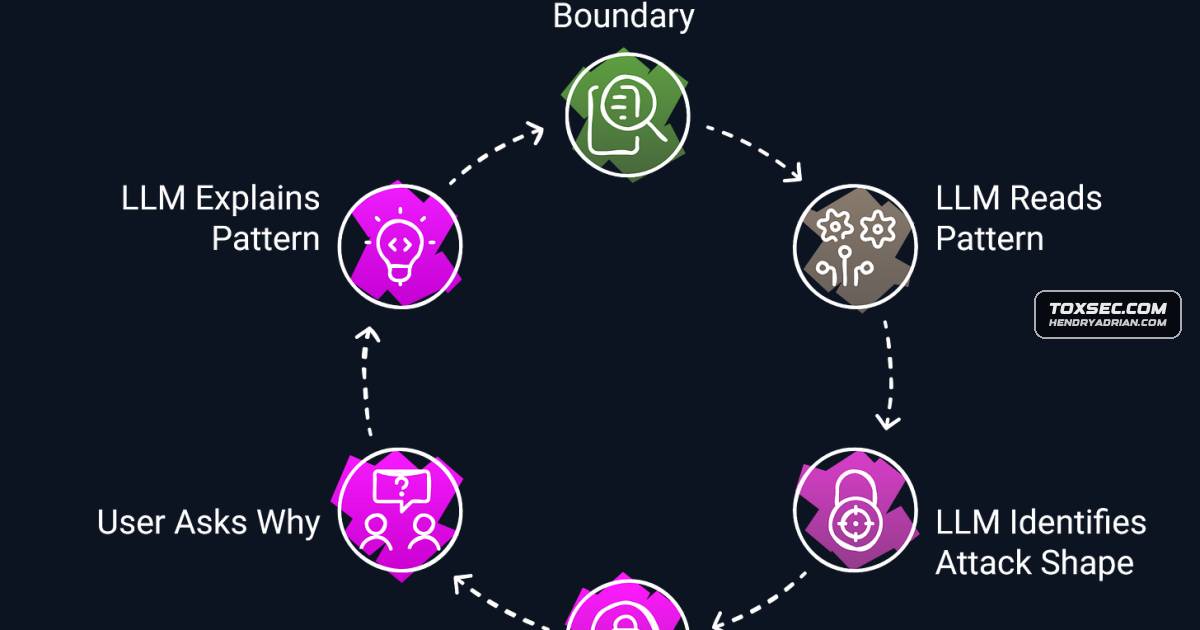
How Agentic AI Attacks Exploit Autonomous Agents—and How to Contain Them

The article explains how indirect prompt injection can hijack agents through goal manipulation, over-permissioned tools, poisoned memory or supply-chain inputs, and recommends least privilege, sandboxing, human approval and decision-level logging to limit and detect the

Jun 7, 2026
Security Insights · hackingarticles.in

Using Claude Desktop and Metasploit for Agentic Penetration Testing

A lab walkthrough connects Claude Desktop to Metasploit through MCP, demonstrating scans, exploitation of Linux and Windows lab hosts, post-exploitation and payload delivery, with human approval gates and mitigation guidance.

Jun 7, 2026
Security Insights · cisecurity.org

2026 Verizon DBIR Highlights the Value of Core Cybersecurity Practices

CIS says the 2026 Verizon DBIR highlights vulnerability exploitation, credential abuse, social engineering, ransomware, and third-party risk, and recommends foundational controls and secure configurations to help defend against them.

Jun 5, 2026
Security Insights · bleepingcomputer.com

2026 DBIR Highlights Growing Security Risks Inside Browsers

A sponsored analysis compares Verizon’s 2026 DBIR findings with Keep Aware telemetry, highlighting risks from personal-account AI use, browser credential theft, extensions, ClickFix and phishing, and arguing for browser-level visibility.

Jun 5, 2026
Security Insights · huntress.com

Huntress Says Sensitive Data Mode Blocks CUI File Transfers to Avoid FedRAMP Scope

Huntress says Sensitive Data Mode blocks selected file extensions from transfer to its SOC, aiming to reduce CUI exposure and let defense contractors use its platform without FedRAMP Moderate authorization.

Jun 5, 2026
Security Insights · toxsec.com

Why AI Guardrails Confuse Red-Team Research With Attacks

The article explains how AI guardrails judge conversational patterns rather than intent, so persistent red-team probing can resemble an attack. It discusses inconsistent outputs and refusal reinforcement, advising defenders not to trust a control’s loosest observed run.

Jun 4, 2026
Security Insights · decodedsecurity.com

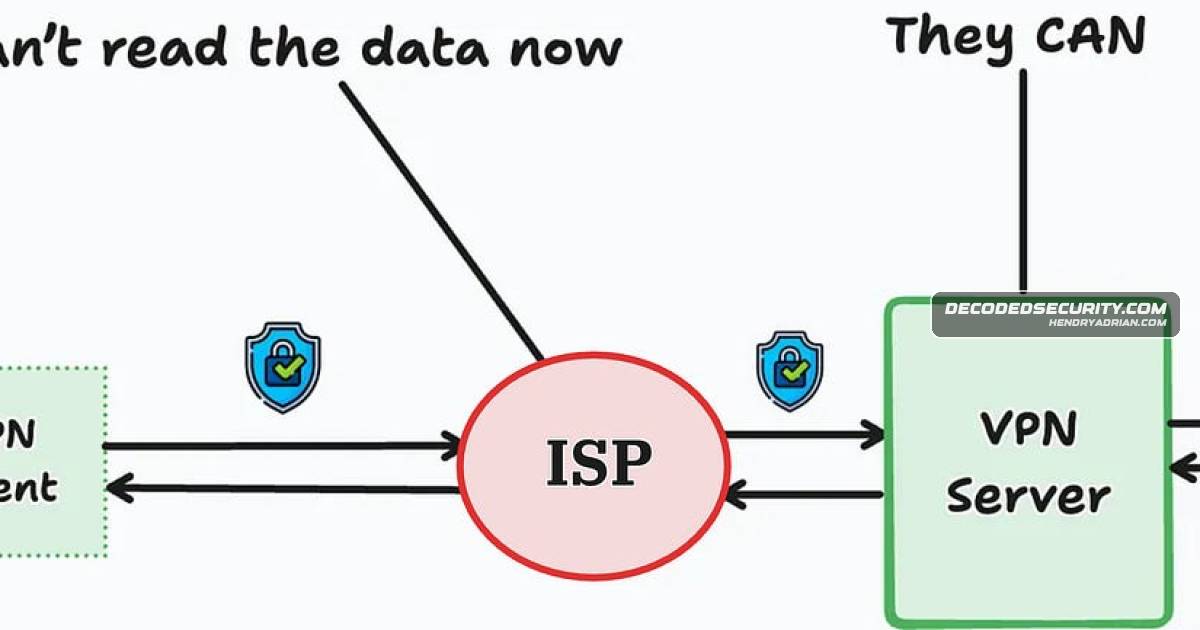
VPN Basics: Trust, Tunnels, and Key Protocols Explained

A beginner-friendly VPN explainer covers encrypted tunnels, the trust shifted to VPN providers, client/tunnel/server components, and differences among PPTP, L2TP, and IPsec.

Jun 4, 2026
Security Insights · thehackernews.com

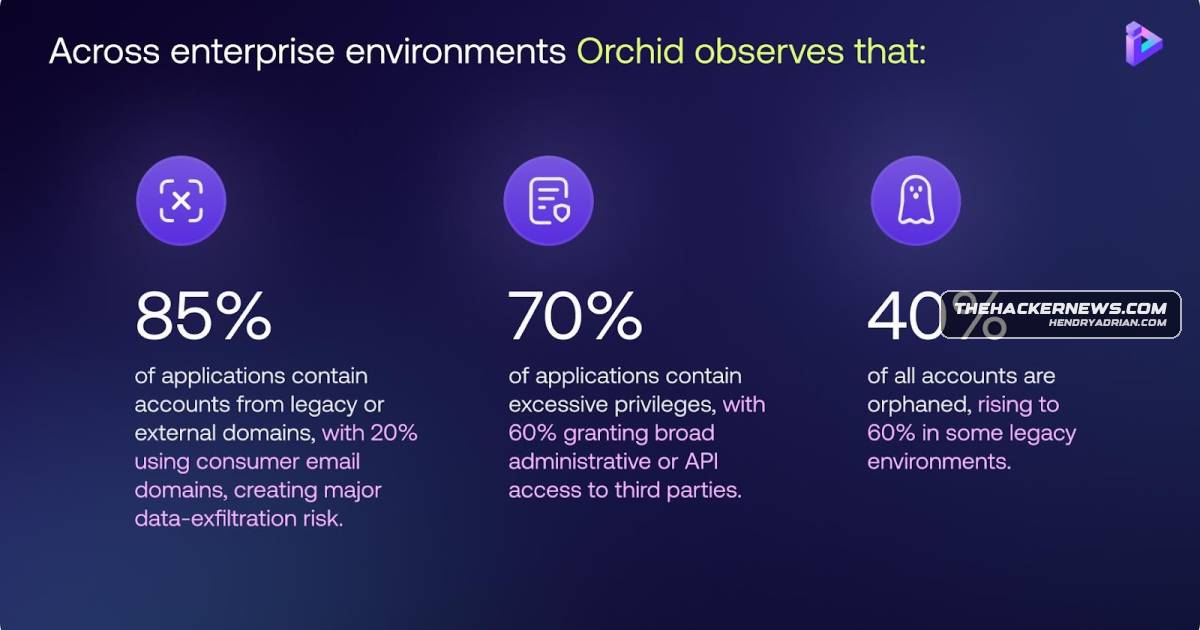
Orchid Says Identity Visibility Platforms Can Expose Gaps Beyond Centralized IAM

Orchid Security describes IVIP as a way to uncover identity activity beyond centralized IAM, citing its application-level analysis and audit findings. The article also recommends attribution, audit trails, least privilege, and guardrails for AI agents.

Jun 3, 2026
Security Insights · bleepingcomputer.com

Sprocket Pentest Finds Cross-Tenant Exposure in Bank Mortgage Portal

A Sprocket Security-sponsored article describes an unauthenticated API on a bank-branded mortgage portal that exposed tenant records across institutions, and argues continuous external testing can catch risks annual pentests miss.

Jun 3, 2026
Security Insights · securitylabs.datadoghq.com

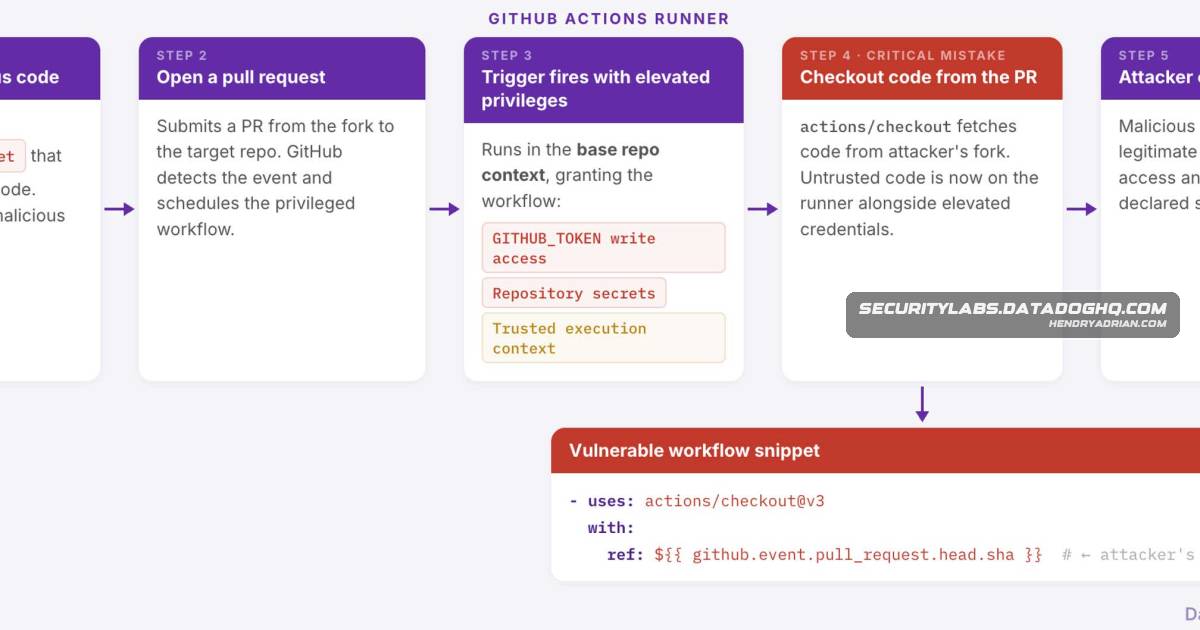
How GitHub Actions Workflow Weaknesses Can Enable Supply Chain Attacks

An explainer on how dangerous triggers, untrusted input, and compromised credentials can put GitHub Actions workflows at risk, with safeguards including restricted permissions, safer input handling, and commit-SHA pinning.

Jun 2, 2026
Security Insights · matthewrosenquist.substack.com

Commentary: Anthropic’s AI Security Framework Falls Short for Enterprise Use

The author considers Anthropic’s Zero Trust-based framework for autonomous AI agents a useful starting point but argues it overlooks practical enterprise concerns, including rapid adoption, evolving threats, insider risks, hidden dependencies and operational constraints

Jun 1, 2026
Security Insights · thehackernews.com

Why Fragmented Identity APIs Can Weaken Injection-Attack Detection

A Veriff executive argues that fragmented identity-verification APIs can discard device telemetry and hardware provenance needed to detect virtual-camera and emulator-based injection attacks, and recommends auditing pipelines and continuously evaluating session signals.

Jun 1, 2026
Security Insights · infostealers.com

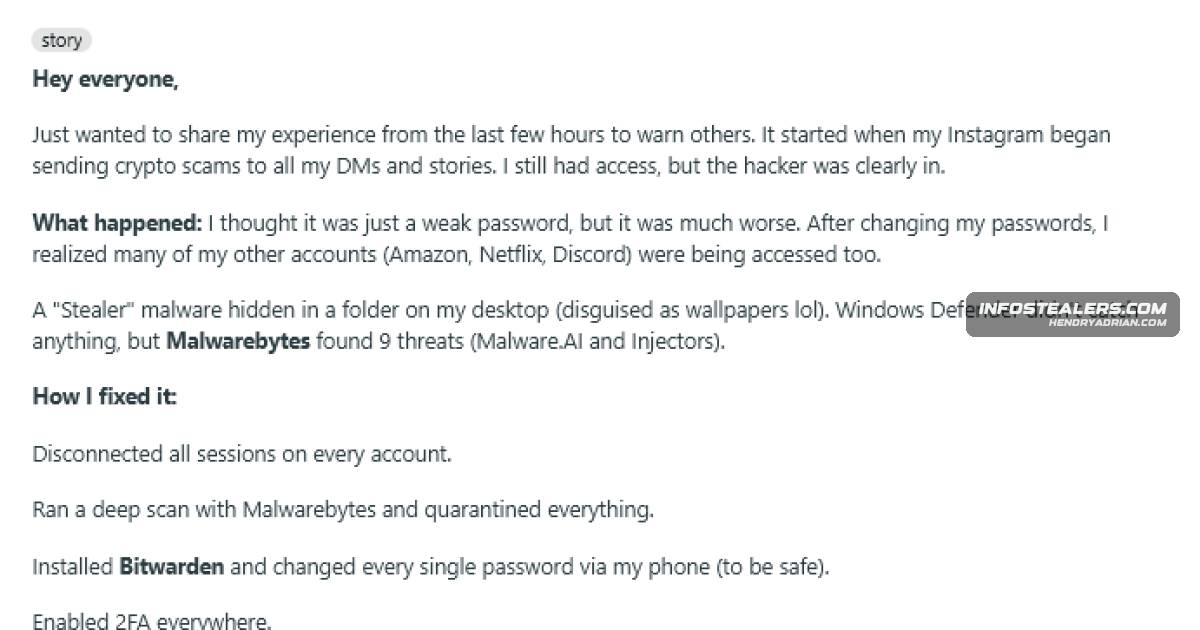
Reddit Users Describe Infostealer Infections, Session Hijacking and Recovery

The article compiles Reddit users’ accounts of infostealer infections involving cracked downloads and Discord scams, explains how stolen session cookies can bypass 2FA, and recommends recovery steps such as changing passwords from a clean device and logging out active ى

Jun 1, 2026
Security Insights · hackingarticles.in

Using ShellGPT and Nmap for AI-Assisted Network Reconnaissance

A hands-on lab walkthrough shows ShellGPT generating Nmap commands for host discovery, service and vulnerability enumeration, and scan-output analysis, then outlines defenses including service reduction, firewalling, patching, and monitoring.

Jun 1, 2026
PreviousPage 28 of 54 Next
© 2026 cyber.hendryadrian.com