cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · huntress.com

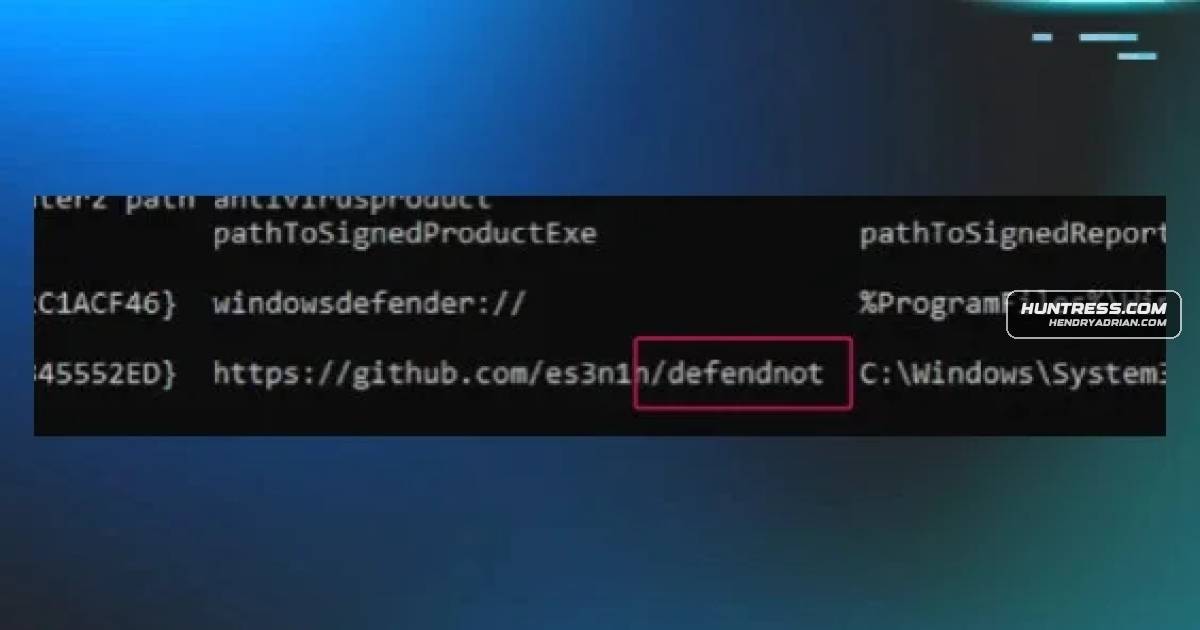
How to Detect defendnot’s Windows Defender Bypass Technique

Huntress outlines detection opportunities for defendnot, which registers a fabricated antivirus through undocumented Windows Security Center APIs to disable Defender, and recommends prioritizing behavioral signals such as process injection and WSC abuse.
May 23, 2025
Detection & Defense · huntress.com

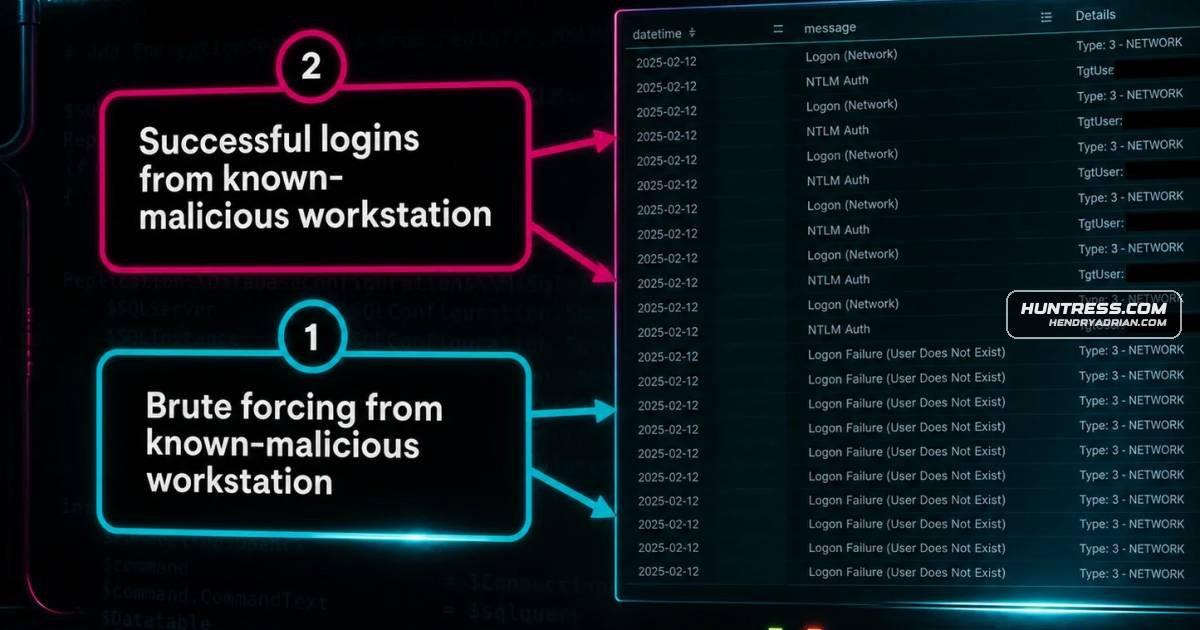
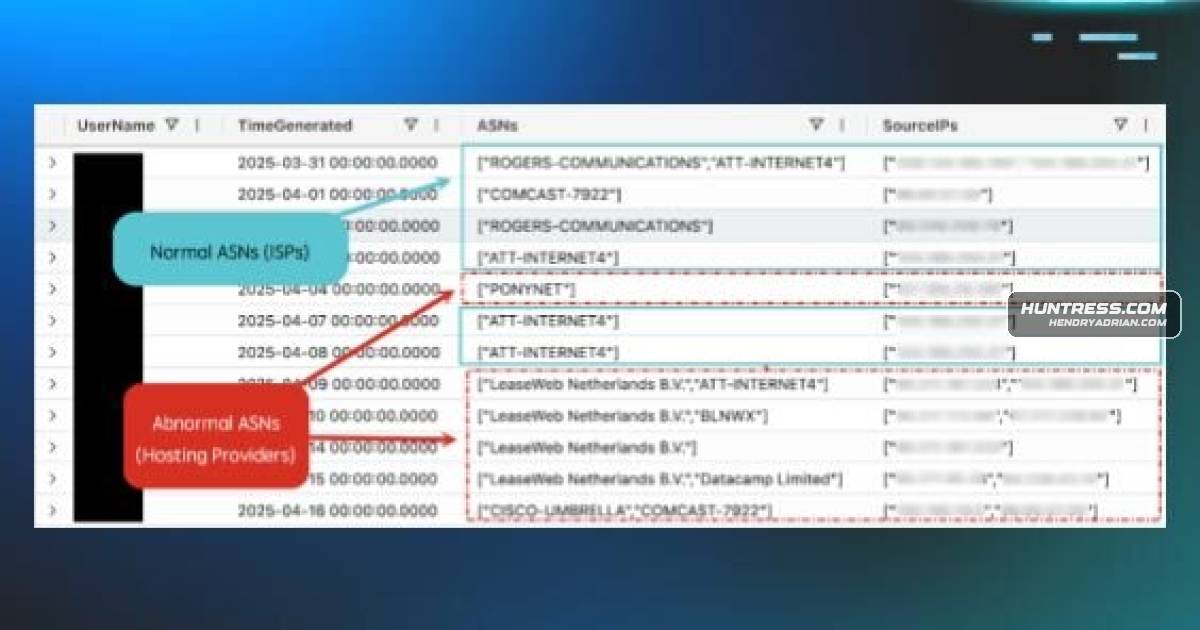
Using ASN Enrichment to Improve Threat Hunting and Incident Response

Huntress explains how analysts can enrich IP data with ASN information to investigate suspicious authentication and identify compromises across remote desktop, RADIUS, and VPN systems.

May 8, 2025
Detection & Defense · darktrace.com

How Darktrace Used Anomaly-Based Threat Hunting to Investigate a Suspected Energy-Sector Attack

Darktrace describes using experimental detection models to hunt for PerfectData-related activity, uncovering a suspected attack involving email access, deletions and downloads of operational files at an energy-sector organization.

May 8, 2025
Detection & Defense · hunt.io

How to Detect IOX, FRP, and Rakshasa Proxy Infrastructure

The article demonstrates how defenders can identify likely IOX, FRP, and Rakshasa deployments using TLS certificate fingerprints, HTTP responses, and exposed files and configurations.

May 8, 2025
Detection & Defense · trendmicro.com

Trend Micro’s Collector Scans Claude Enterprise Chats for Policy Violations

Trend Micro’s Claude Compliance Collector retrieves Claude Enterprise conversations through Anthropic’s Compliance API, scans them with AI Guard for policy violations, and sends detections to the AI Application Security dashboard.

May 5, 2025
Detection & Defense · cloudsek.com

Scan Finds Exposed APIs and Email Spoofing Risks at Digital Lending Firm

A CloudSEK scan found publicly accessible APIs that exposed internal information and misconfigured SPF records that could enable email spoofing at a digital lending firm. The article recommends securing APIs, correcting email settings, and scanning regularly.

May 2, 2025
Detection & Defense · huntress.com

Using Evidence and Context to Improve Detection Engineering

Huntress proposes applying criminal-justice concepts to detection engineering, using evidence levels and behavioral context to assess intent, classify alerts, reduce false positives, and prioritize responses.

May 1, 2025
Detection & Defense · huntress.com

Small Businesses Urged to Build a Security-First Culture to Reduce Malware Risk

The article recommends layered defenses for small businesses, including MFA, software updates, restricted admin privileges, employee training, regular security audits, and tested backups, while promoting managed security services.

Apr 24, 2025
Detection & Defense · wiz.io

Best Practices for Securing Cloud Identities and Privileged Access

The article recommends using CIEM and privileged access controls to improve cloud identity visibility, enforce least privilege, prioritize risky access, grant just-in-time privileges, and protect active sessions. It also promotes a Wiz–CyberArk integration.

Apr 16, 2025
Detection & Defense · huntress.com

Four Cyber Hygiene Failures That Let Attackers Into Networks—and How to Prevent Them

Huntress describes four intrusions involving compromised credentials, brute-forced VPN access, abandoned accounts, and credential theft, and recommends account audits, MFA, strong passwords, VPN monitoring, and logging.

Apr 4, 2025
Detection & Defense · huntress.com

Attackers Enable Windows Guest Accounts for Persistence and Remote Access

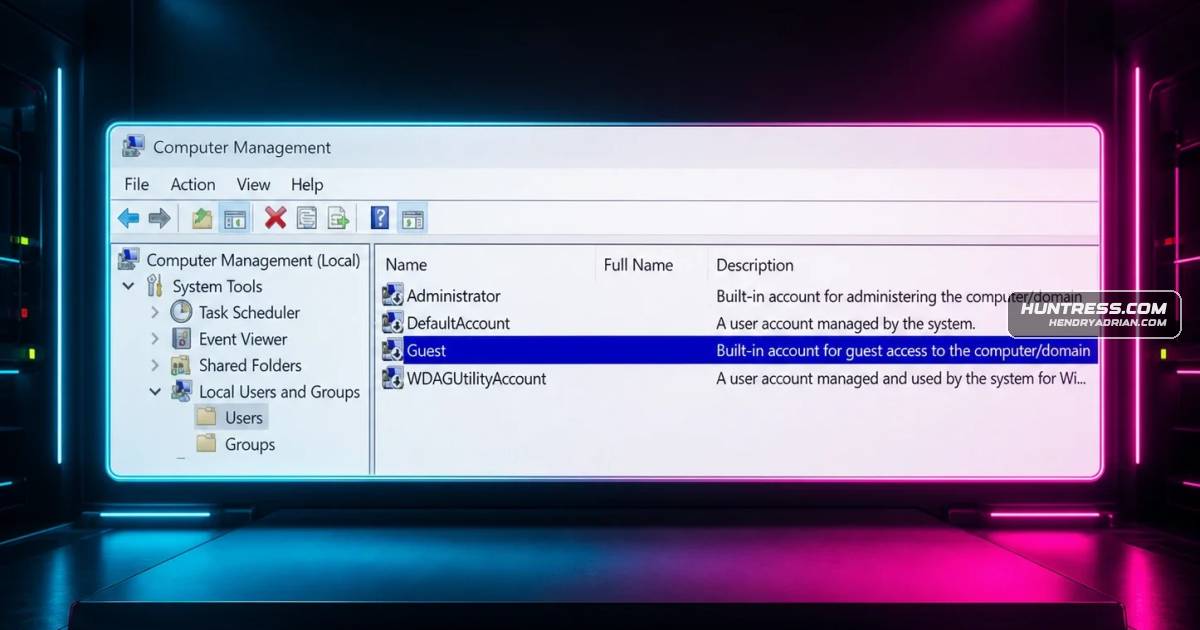
Huntress reports attackers enabling Windows’ disabled Guest account, changing its password, and adding it to privileged or remote-access groups. It recommends monitoring account changes and hunting for active Guest accounts.

Apr 2, 2025
Detection & Defense · huntress.com

Huntress Warns Small Businesses That Cybersecurity Cuts Can Raise Recovery Costs

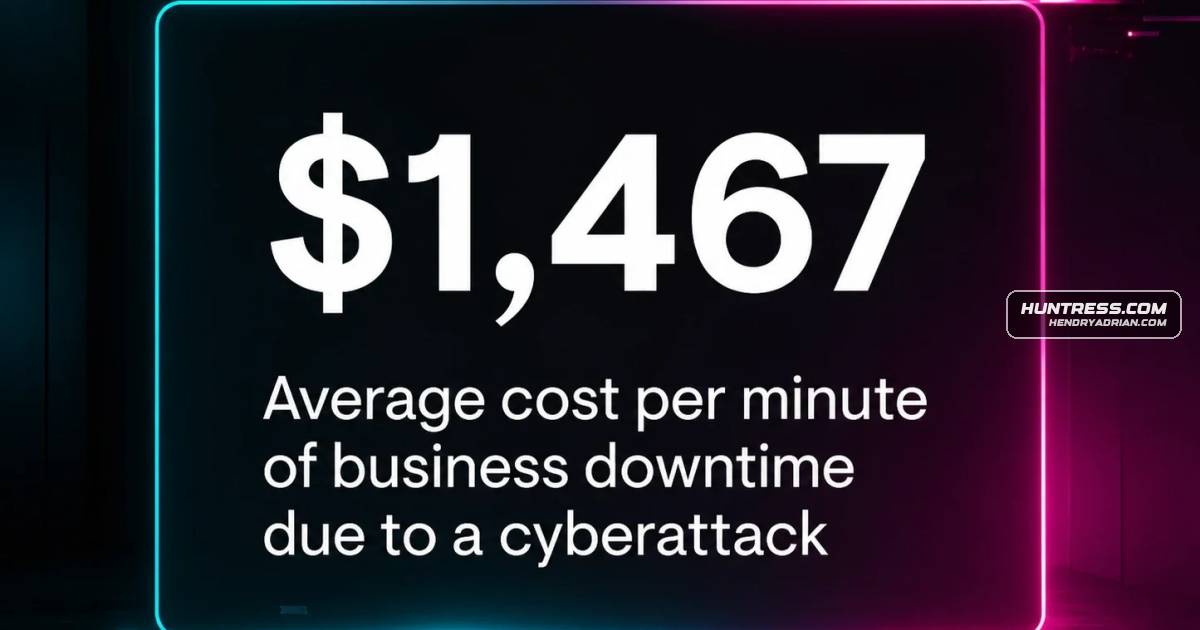
Huntress argues that underinvestment leaves businesses exposed, citing a 16-day median breach dwell time and high recovery costs. It recommends 24/7 SOC monitoring, EDR/ITDR, staff training, and incident-response planning.

Mar 31, 2025
Detection & Defense · huntress.com

How to Reduce Common Endpoint Security Risks

Huntress outlines risks from exposed RDP, phishing, abused RMM tools, and unpatched software, with steps such as MFA, access controls, monitoring, user training, and regular patching.

Mar 28, 2025
Detection & Defense · cloudsek.com

Digital Lending Platforms Face API, Authentication and Encryption Risks

The article describes security gaps in digital lending platforms, including exposed APIs, weak authentication and inadequate encryption, and recommends stronger access controls and data protection.

Mar 26, 2025
Detection & Defense · wiz.io

How to Use AWS CloudTrail Network Activity Events to Monitor VPC Endpoints

AWS CloudTrail network activity events provide visibility into supported API calls through VPC Endpoints. The article explains using them to assess endpoint policies, monitor denied requests, and help detect possible data exfiltration, while weighing coverage against 비용

Mar 20, 2025
Detection & Defense · wiz.io

ClickHouse Disables Default-User Network Access After DeepSeek Database Exposure

After Wiz Research found a publicly accessible DeepSeek ClickHouse database, ClickHouse disabled network access for the default user by default in official images and backported the change to three recent releases and two LTS versions.

Mar 18, 2025
Detection & Defense · aquasec.com

Aqua Shows Runtime Protection Against Sobolan Malware Targeting JupyterLab

Aqua researchers describe a Sobolan campaign that exploited unauthenticated JupyterLab, deployed cryptominers and persistence tools, and show how Aqua runtime policies detected and blocked activity while providing incident telemetry.

Mar 10, 2025
Detection & Defense · huntress.com

Huntress Shares Incident Examples and Tips for Detecting Persistent Malware

Huntress describes four customer incidents involving persistent malware or unauthorized access, highlighting endpoint monitoring, persistence checks, user training, and securing exposed remote desktop services.

Mar 7, 2025
Detection & Defense · wiz.io

How to Secure Code Repositories, CI/CD Pipelines, and Software Artifacts

Developer infrastructure can expose software supply chains to unauthorized access and malicious changes. The article outlines repository, pipeline, identity, and registry controls, plus monitoring for suspicious activity.

Feb 14, 2025
Detection & Defense · hunt.io

Hunt.io Adds SSL Certificate Flags to Help Hunt PupyRAT, AsyncRAT and Coyote Infrastructure

Hunt.io added SSL certificate anomaly flags to its HuntSQL tooling and demonstrates filtering certificate data to identify likely infrastructure linked to PupyRAT, AsyncRAT and Coyote.

Feb 13, 2025
Detection & Defense · hunt.io

Hunt IO Shares Network Signatures for Detecting Pyramid C2 Servers

Hunt IO describes HTTP response patterns and a query to identify Pyramid C2 servers, reporting nine matching IP addresses. Three overlapped with infrastructure previously linked to a RansomHub affiliate’s Python-based backdoor.

Feb 12, 2025
Detection & Defense · hunt.io

How SSL Certificate History Can Help Threat Hunters Map Malicious Infrastructure

Historical SSL/TLS certificate data can help threat hunters connect domains and IPs, identify reused certificates and suspicious changes, and investigate infrastructure linked to malware and threat actors.

Jan 30, 2025
Detection & Defense · wiz.io

A “Zero Noise” Approach to More Effective Cloud Detection

The article outlines a defensive method for reducing cloud alert noise: tailor detections to critical assets, review their effectiveness, and investigate every alert. A financial services organization used these steps to reduce noise and detect later attack attempts.

Jan 27, 2025
Detection & Defense · huntress.com

Using Windows PerfMon to Detect Kerberos Roasting Activity

A lab-based demonstration shows how Windows PerfMon counters and Active Directory ETW telemetry can provide context for detecting Kerberoasting, AS-REP roasting, and related attacks beyond relying only on Windows Events 4768 and 4769.

Jan 23, 2025
PreviousPage 22 of 27 Next
© 2026 cyber.hendryadrian.com